

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
583
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 eddinos2/cve-2026-64747
Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…
 amorcool/ios26.6-cve-2026-65343
CVE-2026-65343 PoC — AppleKeyStore OOB read → KASLR defeat (iOS 26.6 / 23G71)
 lame-projects/stratum-c2
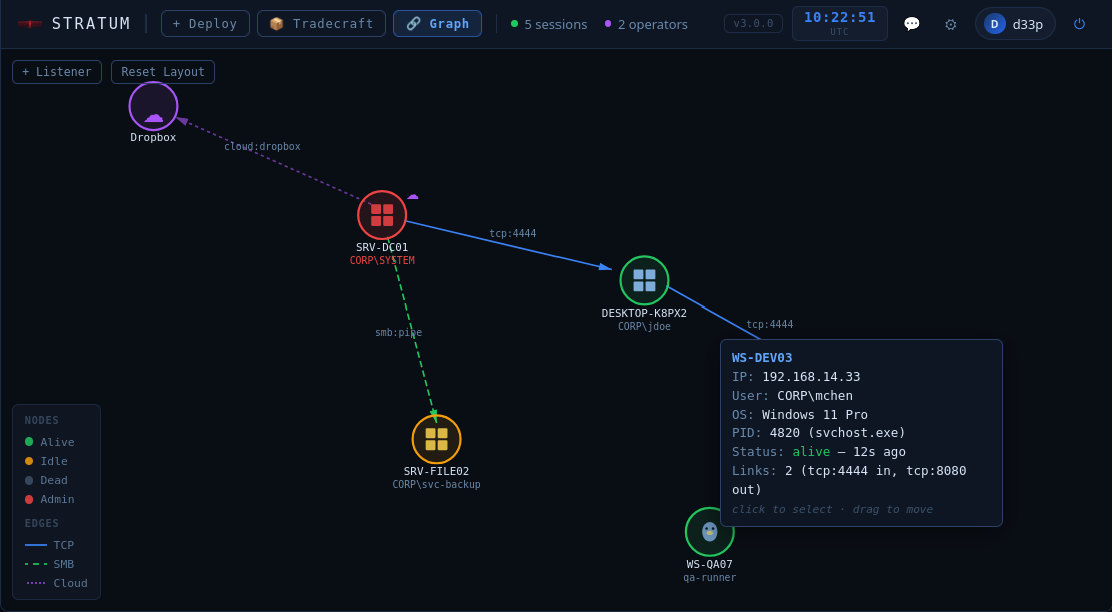
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 hyderpwn/veritas-backup
Metasploit module for exploiting Veritas Backup Exec Agent SHA-auth NDMP vulnerability to achieve remote code execution.
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 kaleth4/cve-2026-4747-
Remote kernel exploit for FreeBSD CVE-2026-4747, leveraging a stack buffer overflow in kgssapi.ko to achieve RCE with a reverse shell. Includes…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 233laoliu/mt6985-cve-2026-43499
CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)
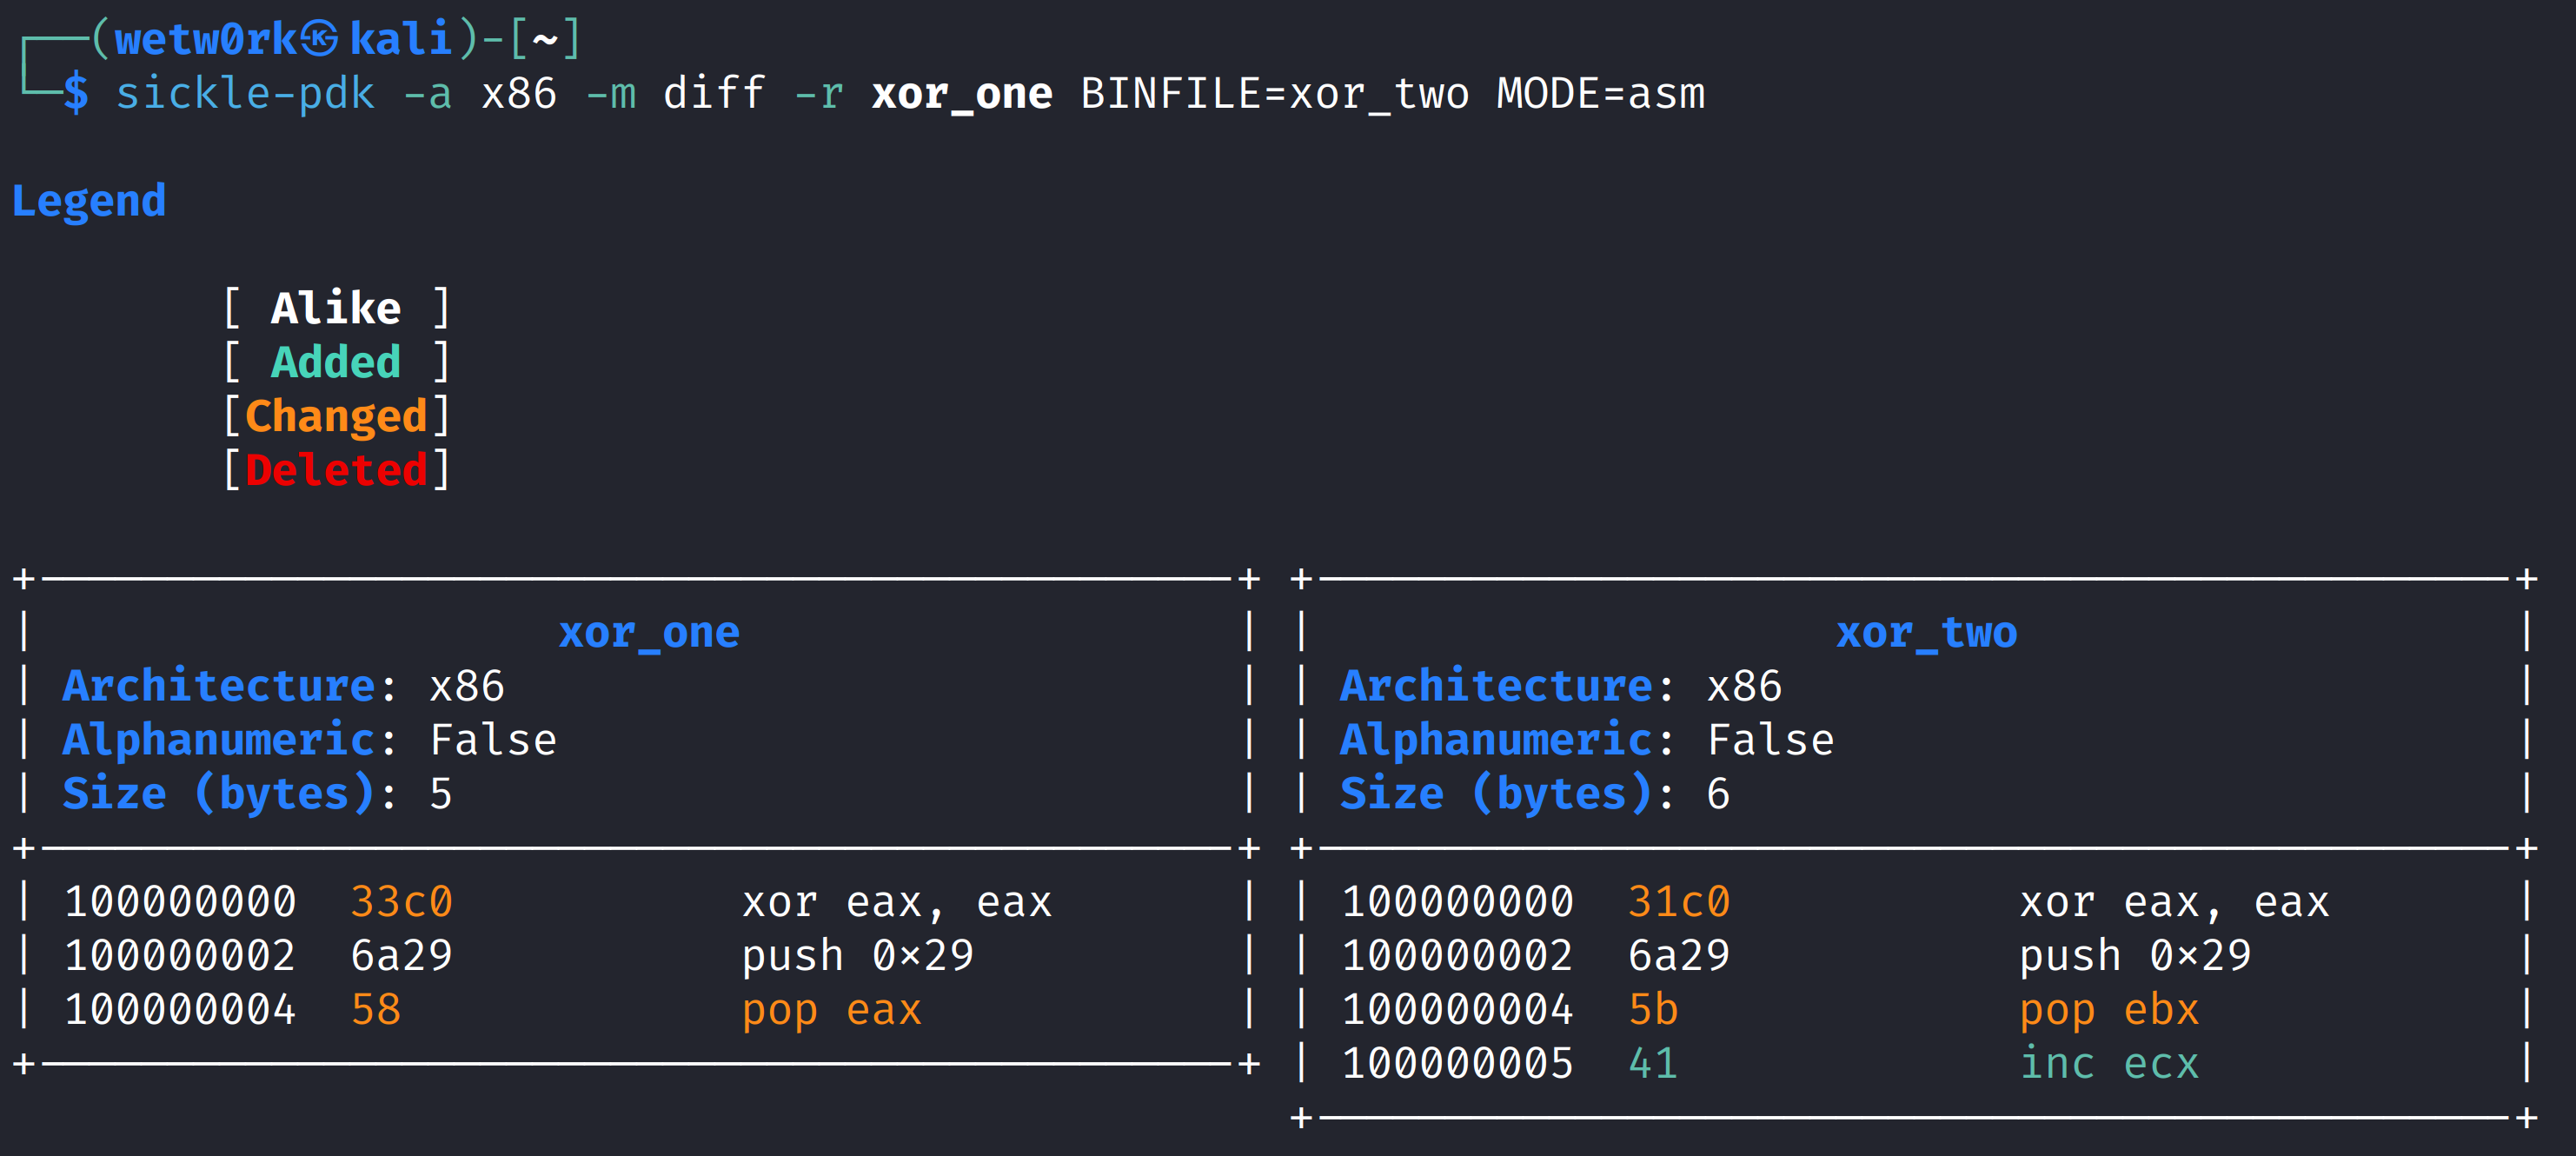 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…