
spip-exploits
 ambionics/spip-exploits
Python exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.
exploitationexploit-frameworkspapers-research+4
1
ambionics/spip-exploitsPython exploit chain for SPIP CVEs 2026-72708/72709/72710, chaining unauthenticated SQL injection to account takeover and remote code execution.
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
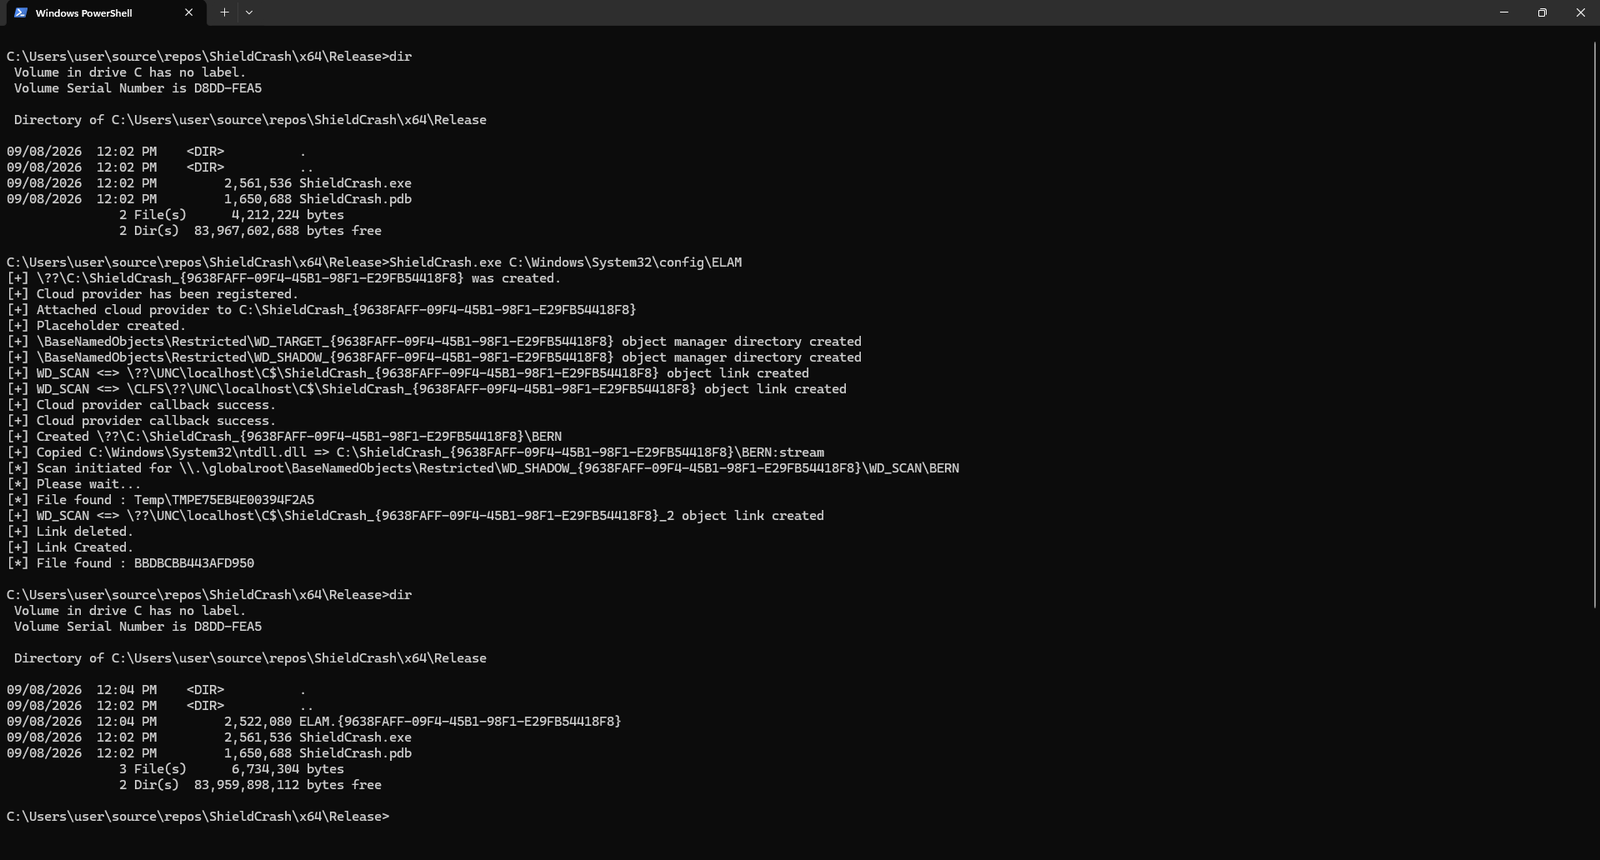 msnightmare/shieldcrash
Proof-of-concept exploit for CVE-2026-69414, a Windows Defender 0day enabling arbitrary file read as SYSTEM on all supported Windows versions.
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 cyberbalsa/ghostlock-nvidia-shield-9.2.4
Validated GhostLock CVE-2026-43499 port for NVIDIA Shield TV Pro mdarcy 9.2.4
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
 samirchapagain/metasploit-lab-report
Educational penetration testing lab report documenting exploitation of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable 2 using Metasploit,…
 ruik-tech/ghostlock-s25fe
GhostLock (CVE-2026-43499) for the Galaxy S25 FE (W.I.P)
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 sq00ky/zero-logon-exploit
Python script exploiting Zerologon (CVE-2020-1472) to perform Netlogon authentication bypass and reset domain controller password to null.
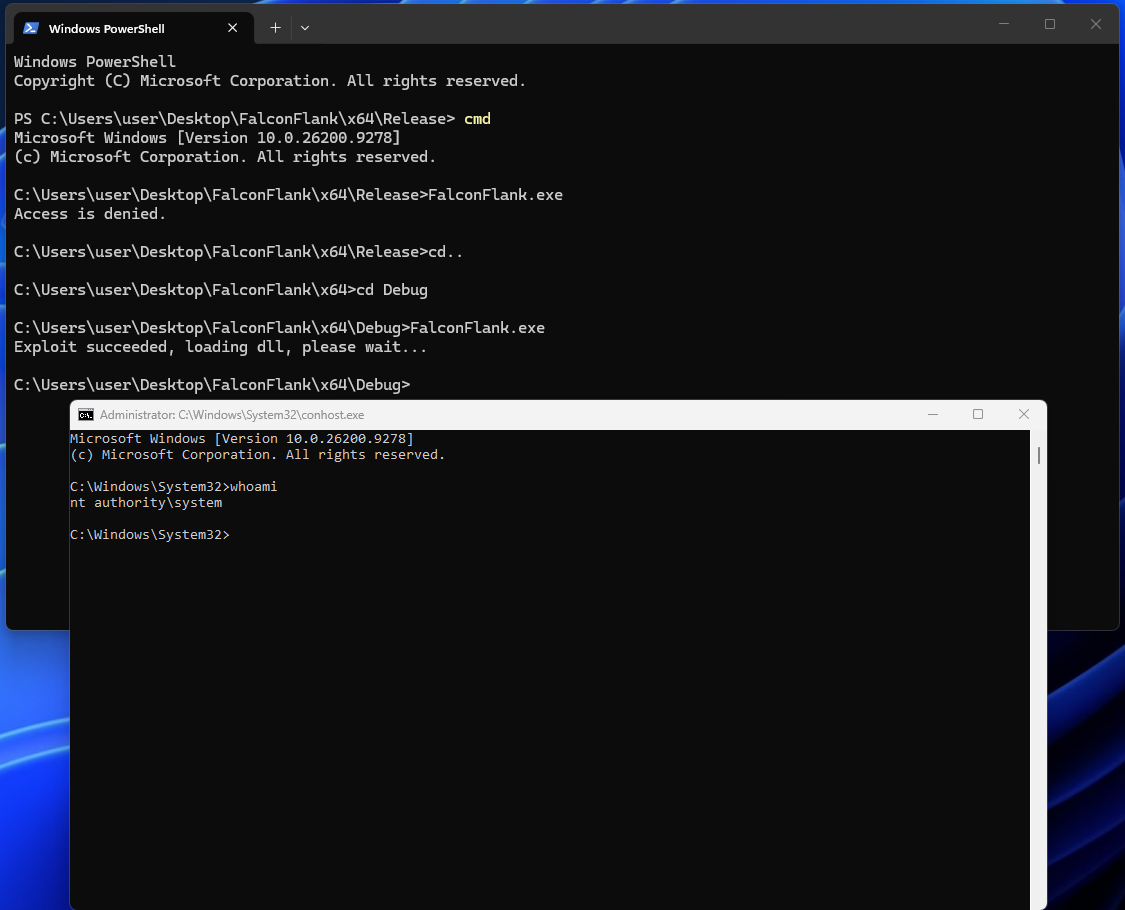 msnightmare/falconflank
Crowdstrike Falcon 0day Privilege Escalation Vulnerability
 quyicheng03-boop/xiaomi15-dada-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for Xiaomi 15 dada OS4.0.0.8
 everyoneexe/root-s24-e1s
Galaxy S24 SM-S921B S921BXXSDCZB2 RAM-only KernelSU Next + Root S24 app
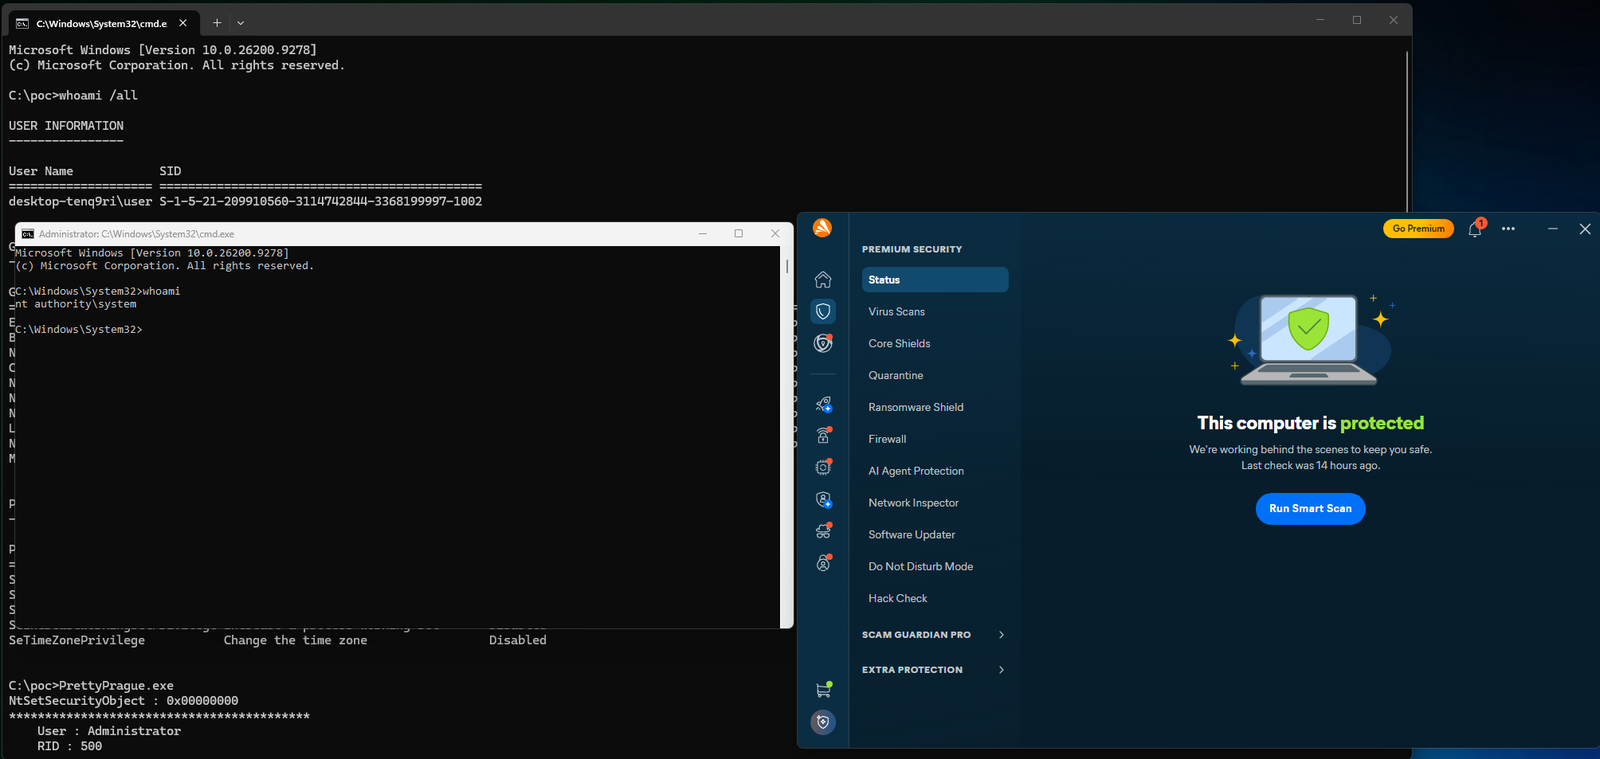 msnightmare/prettyprague
GenDigital Avast Antivirus ZeroDay Elevation of Privileges Vulnerability
 aboubacar70/lab1-metasploitable
Exploitation des vulnérabilités sur la version vsftpd 2.3.4 du service ftp (CVE-2011-2523)
 abdgalaxy36-code/rmgp-complete-handoff
Complete RMGP (CVE-2026-43499) workspace + experiment-state handoff for SM-A376B/A376BXXU1AZB7
 slapah/ghostlock-h8q
GhostLock CVE-2026-43499 port for Galaxy Z Fold 8 (h8q)