

lockjaw
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
command-and-controldns-analysisexploit-frameworks+9
26
g13net/lockjawModular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 k3ystr0k3r/metis
Modular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 n0qword/mythic_ornn
LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 exploiteoom/cve-2026-31431
Exploit for CVE-2026-31431 that escalates privileges by altering user ID, with a verification script and mitigation instructions for the algif_aead…
 estamelgg/cve-2021-4034-nogcc
Standalone exploit for CVE-2021-4034 (polkit pkexec) that runs without gcc or cmake, providing interactive shell or one-liner command execution on…
 ck00004/cve-2021-4034
Exploit for CVE-2021-4034 (pkexec) targeting CentOS 8, allowing custom command execution via modified pwnkit-dry-run.c. Includes compilation and…
 h1d3r/copy-fail_lpe_interactive
Exploit for CVE-2026-31431, a Linux kernel page cache corruption vulnerability, providing interactive root shell and non-interactive command…
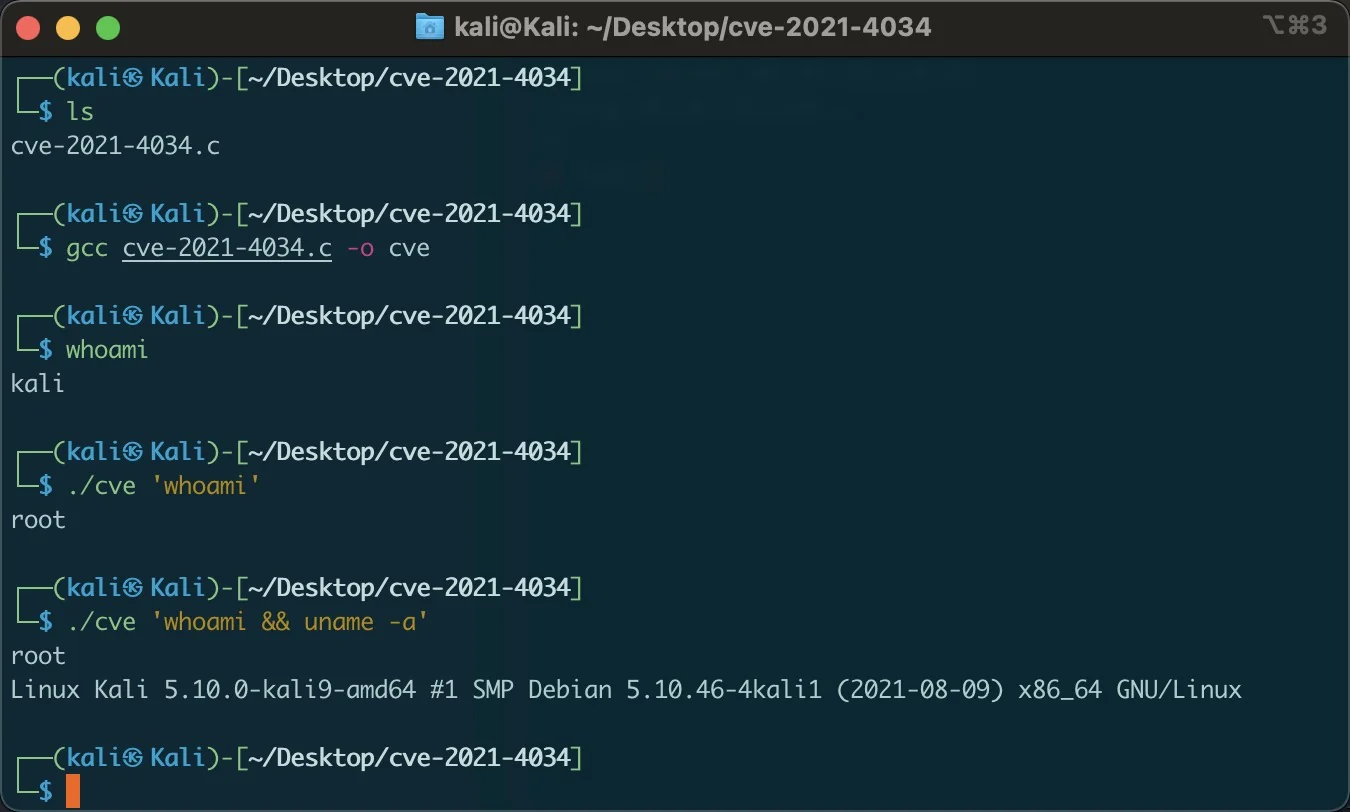 zhzyker/cve-2021-4034
polkit pkexec Local Privilege Vulnerability to Add custom commands