

METIS
 k3ystr0k3r/metis
Modular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…
command-and-controlctfeducation+9
3
k3ystr0k3r/metisModular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 diegslva/cve-2010-4221-lab
From patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented
 samirchapagain/metasploit-lab-report
Educational penetration testing lab report documenting exploitation of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable 2 using Metasploit,…
 diegslva/cve-2015-3306-lab
Reproducible Docker lab + raw-socket exploit for CVE-2015-3306 (ProFTPD mod_copy pre-auth arbitrary file copy) — a patch-diffing learning exercise
 eddinos2/cve-2026-64705
Root-cause analysis and proof-of-concept for CVE-2026-64705, a macOS HFS xattr kernel heap overflow. Includes weaponized HFS+ image, patcher, parser,…
 aramosf/cve-2026-64468
Unprivileged proof-of-concept and x86_64 local privilege escalation for a Linux kernel Binder use-after-free (CVE-2026-64468), with KASAN lab and…
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
 vp777/windows-kernel-exploitation
Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…
 smgorelik/windows-rce-exploits
The exploit samples database is a repository for **RCE** (remote code execution) exploits and Proof-of-Concepts for **WINDOWS**, the samples are…
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…
 xn0kkx/cve-2026-31431_copyfail_linuxkernel_lpe
Educational rewrite of the Copy Fail PoC (CVE-2026-31431) — Linux kernel LPE via algif_aead in-place crypto + splice() page-cache write
 astounds/copy-fail-cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG + splice page-cache overwrite. Includes PoC, BPFtrace detection script,…
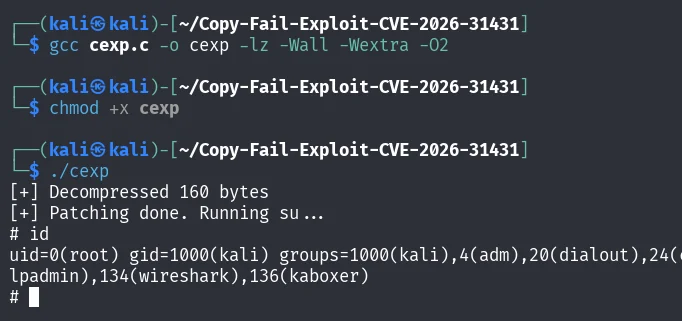 beatbeast007/linux-copyfail-c-version-cve-2026-31431
Clean C implementation of the Copy Fail Linux local privilege escalation exploit (CVE-2026-31431). Uses AF_ALG and splice to overwrite page cache of…
 abhishekhargan/cve-2026-31431
Python exploit for Linux kernel local privilege escalation (CVE-2026-31431) using AF_ALG socket state confusion and splice() to achieve arbitrary…
 themursalin/cve-2026-31431
Python exploit for CVE-2026-31431, a Linux kernel LPE via AF_ALG null pointer dereference leading to heap OOB write and credential overwrite.…
 industri4l-h3ll-xpl0it3rs/cve-2026-31431-copy-fail
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability, allowing unprivileged users to gain root access.
 erdemozgen/copy-fail-cve-2026-31431
Go port of the Copy Fail PoC for CVE-2026-31431, a Linux kernel authencesn flaw enabling a 4-byte write into page cache via AF_ALG and splice.…