
CiLocks
 tegal1337/cilocks
Crack Interface lockscreen, Metasploit and More Android/IOS Hacking
android-securityexploit-frameworksinformation-gathering+7
3.1k3 years ago
tegal1337/cilocksCrack Interface lockscreen, Metasploit and More Android/IOS Hacking
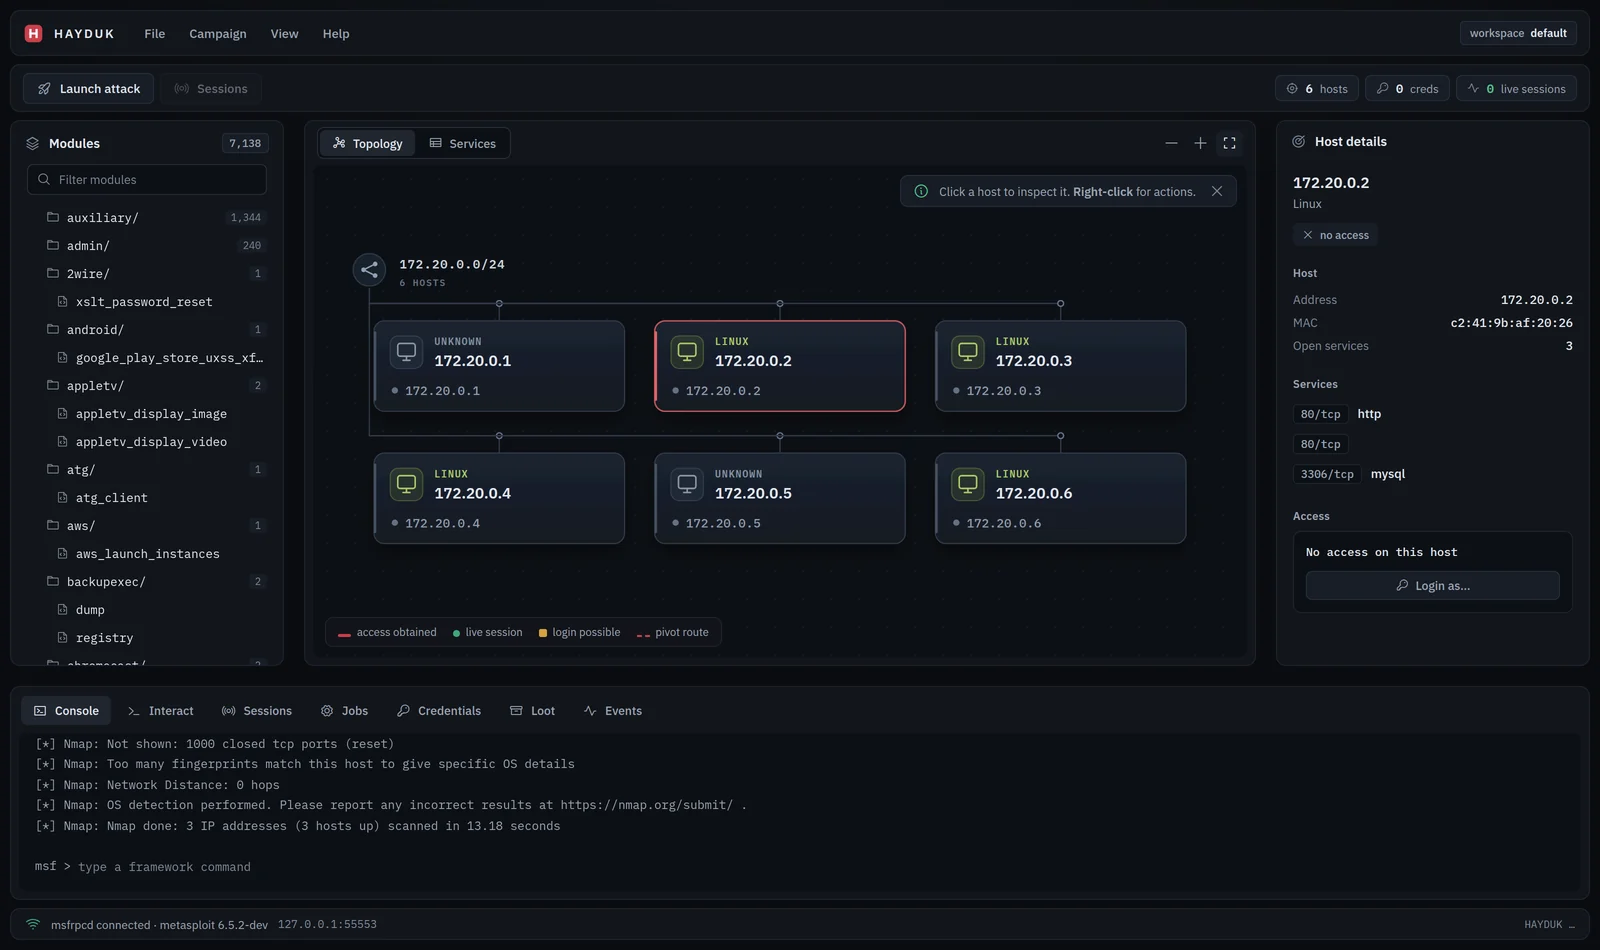 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 cream-sec/cve-2019-0708-msf--
CVE-2019-0708-Msf-验证
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
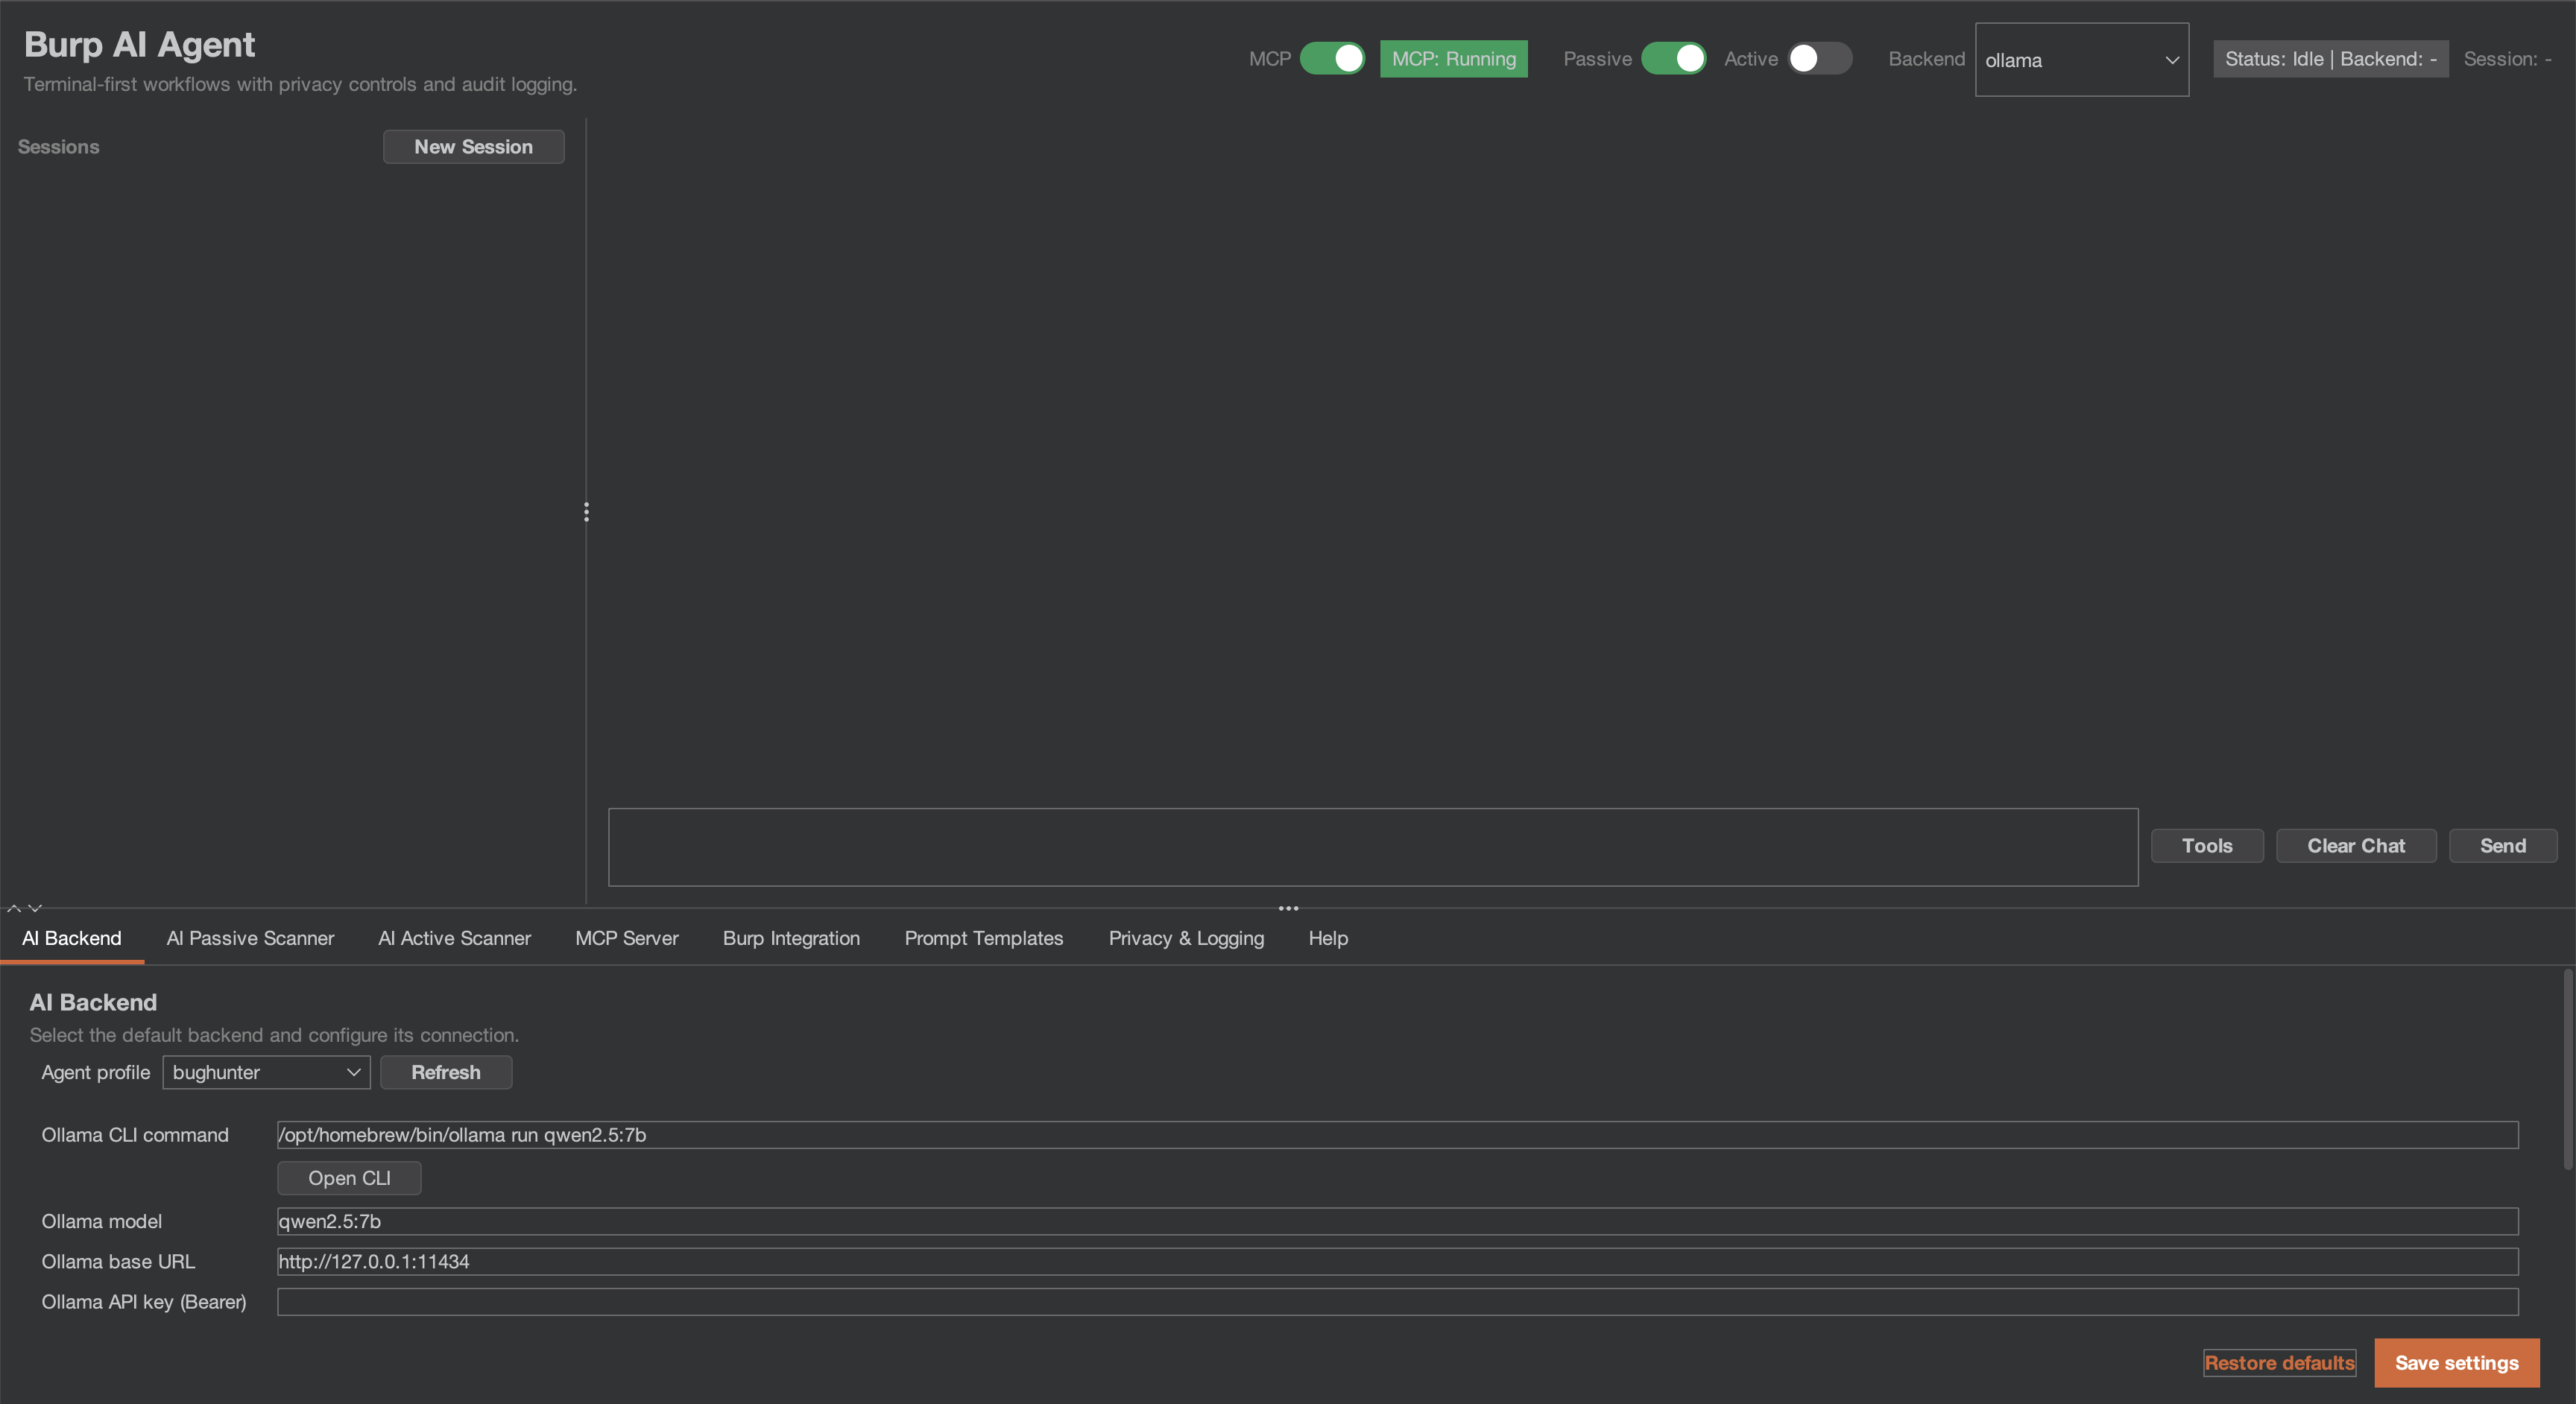 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 bounteous17/libenom
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…
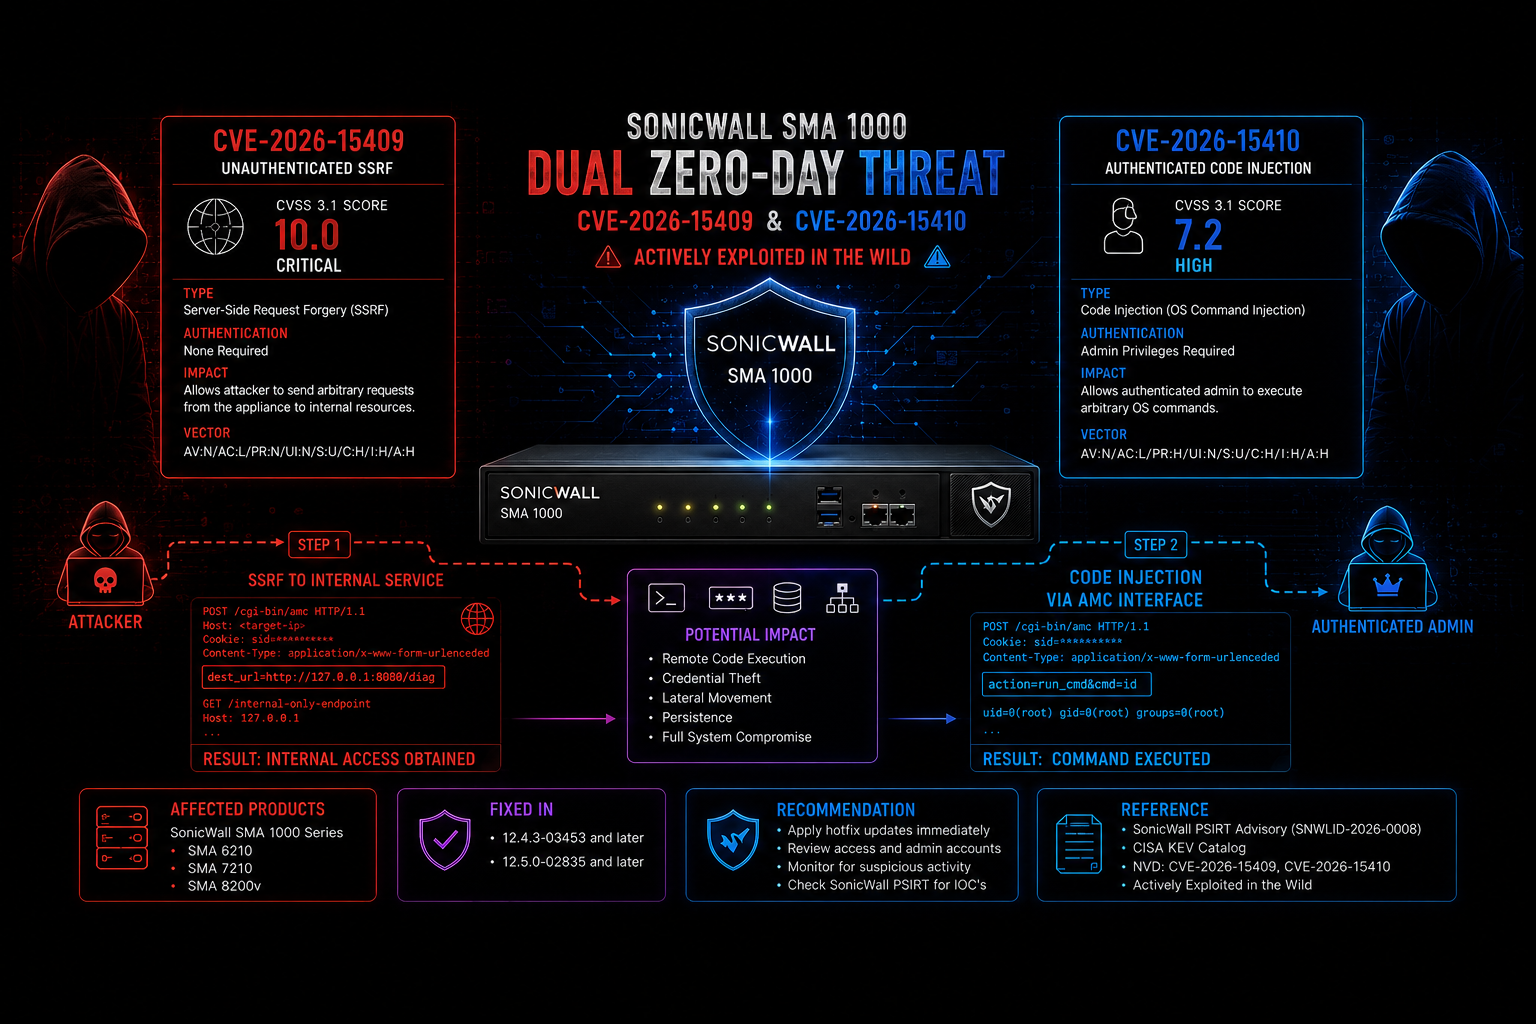 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 0xthirteen/staykit
Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…
 d4em0n/exrop
Automated ROP chain generator for x86-64 binaries using symbolic execution. Supports register/memory writes, function calls, syscalls, badchar…
 telefonica/uac-a-mola
Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…