
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 naksyn/pythonmemorymodule
pure-python implementation of MemoryModule technique to load dll and unmanaged exe entirely from memory
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3
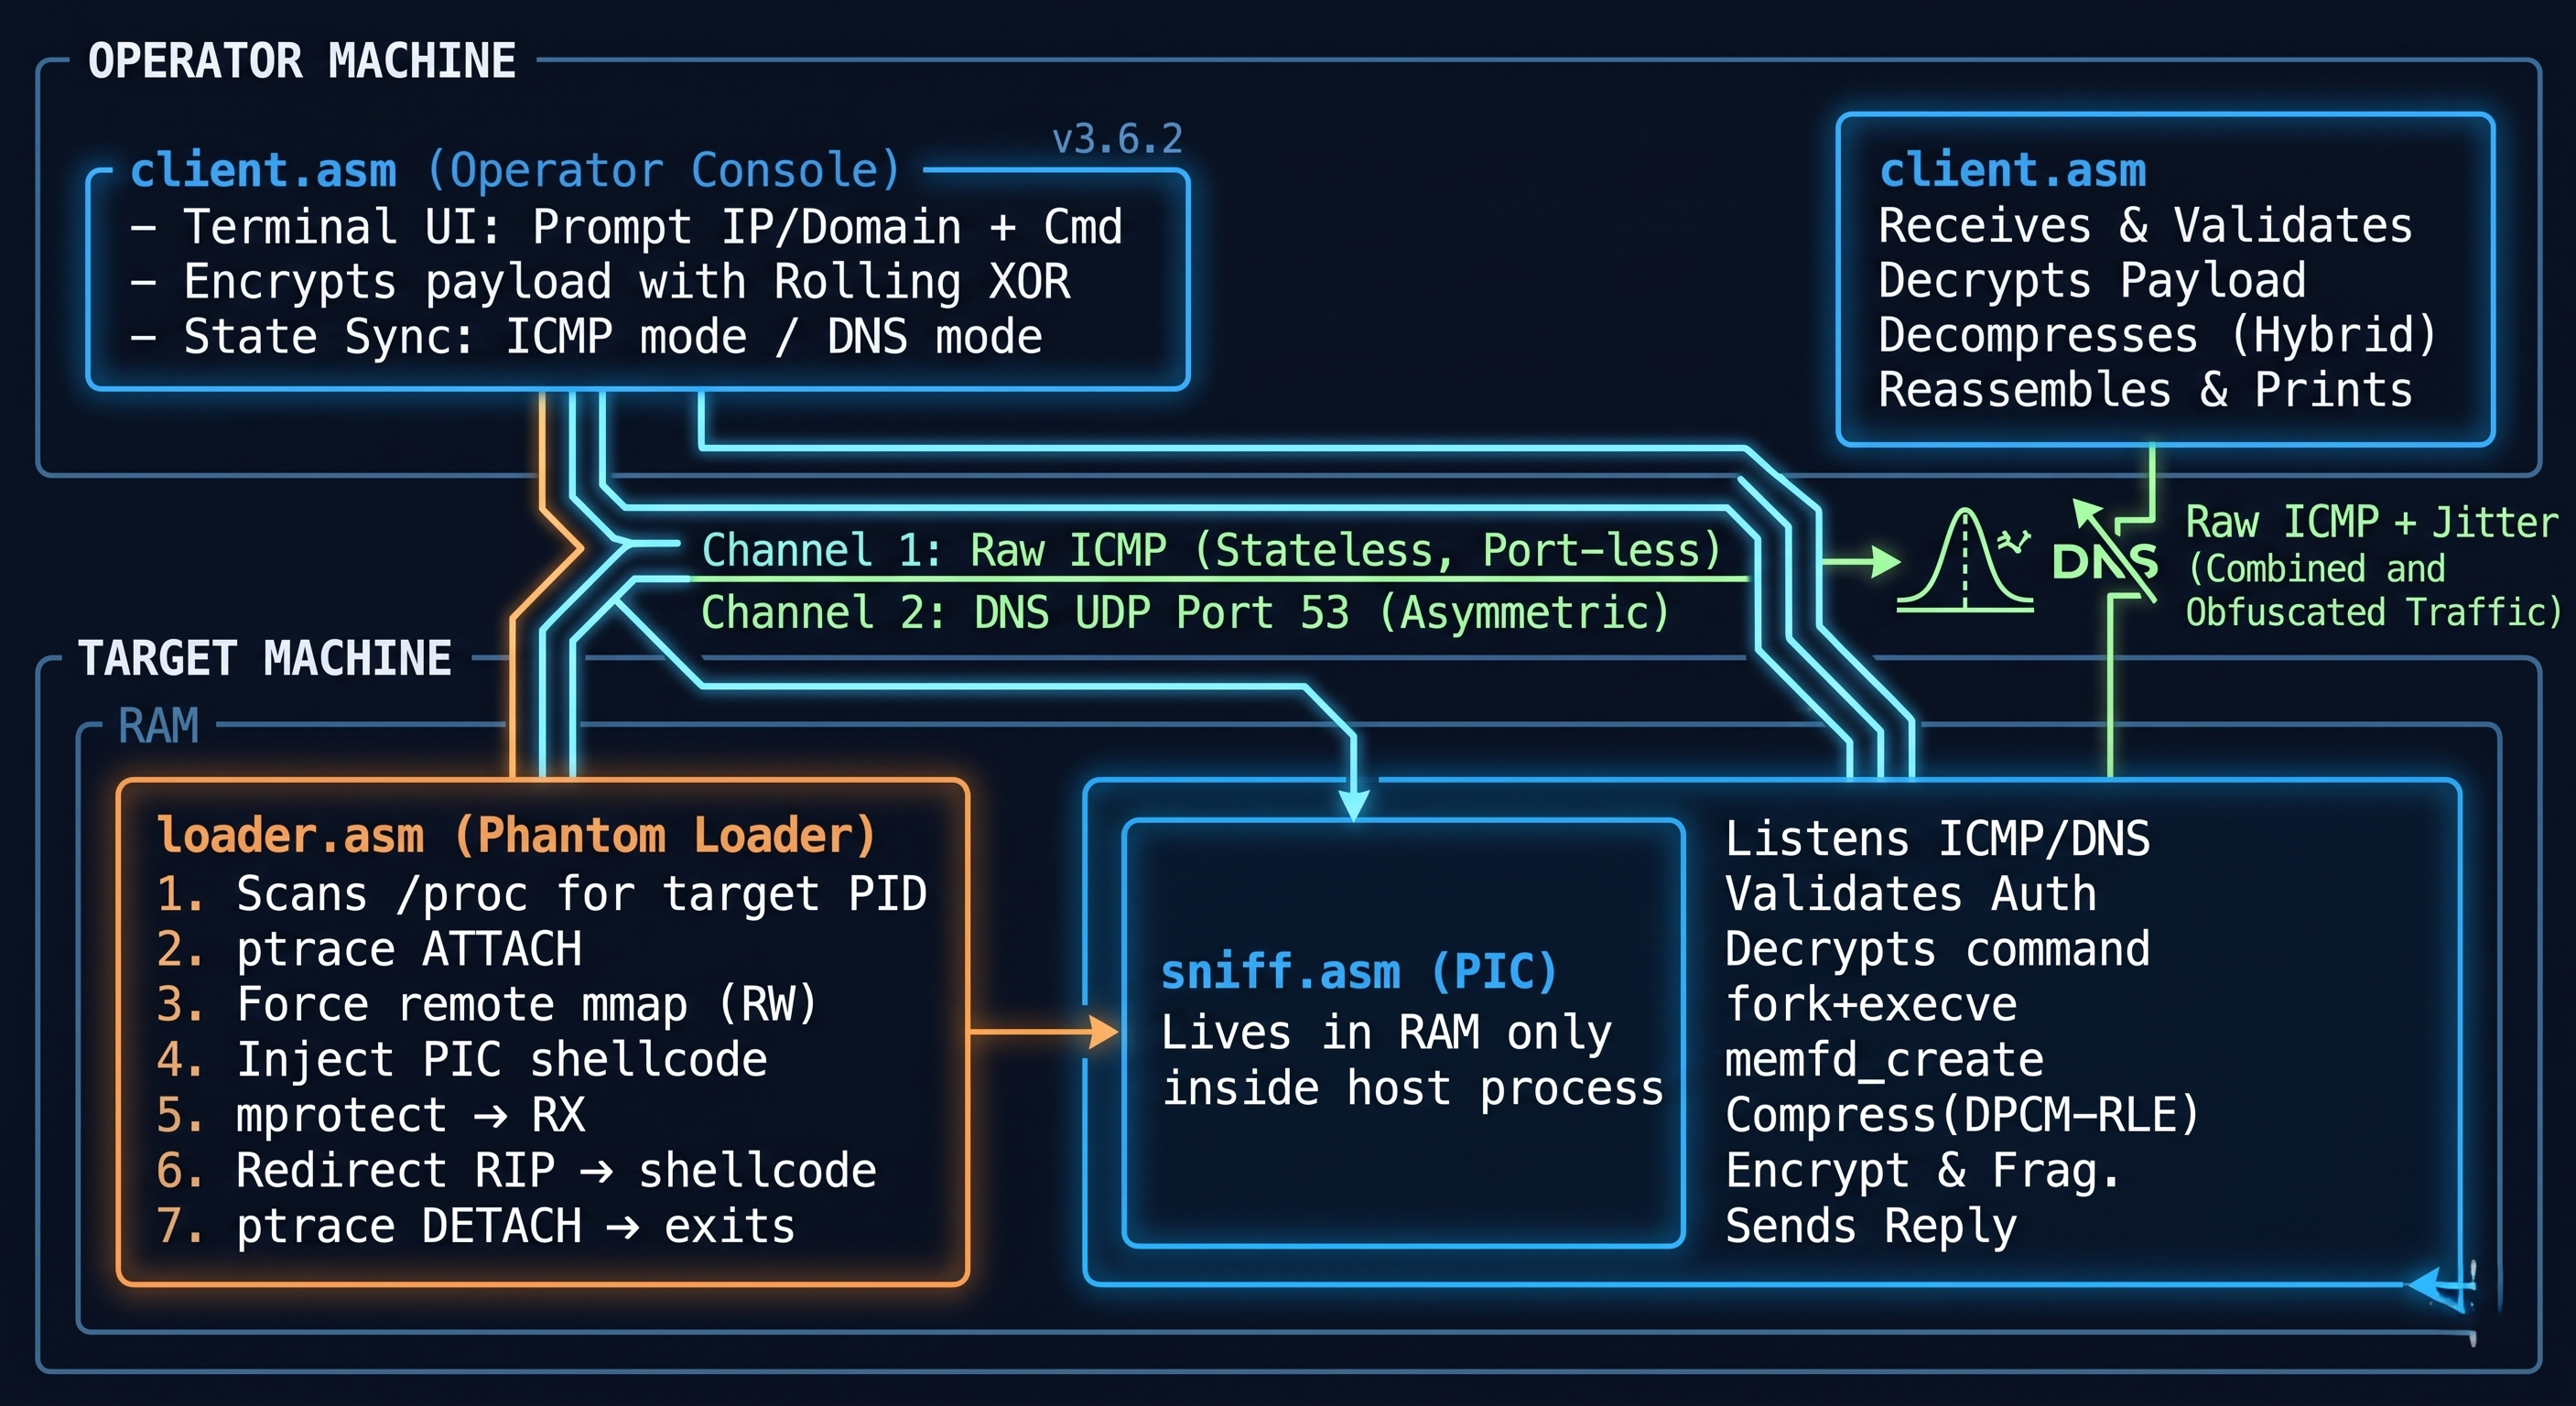 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 jarpex/cve-2023-4911-exploit-optimized
Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…
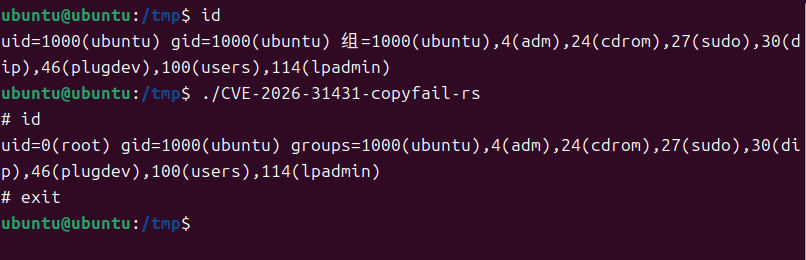 kanbaraakihito/cve-2026-31431-copyfail-rs
Pure Rust proof-of-concept for CVE-2026-31431, targeting Linux x86_64 kernels with AF_ALG AEAD support. Static musl build, no runtime dependencies,…
 oxdbxkxo/ez-pwnkit
Go implementation of the PwnKit Linux Local Privilege Escalation exploit (CVE-2021-4034)