
cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

Adversary Emulation Framework

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.

Kernel root exploit (CVE-2026-43499) for some Amazon devices

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

CVE research and exploits to help gaining roots for Pixel devices

A collaborative, multi-platform, red teaming framework

Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…

The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup

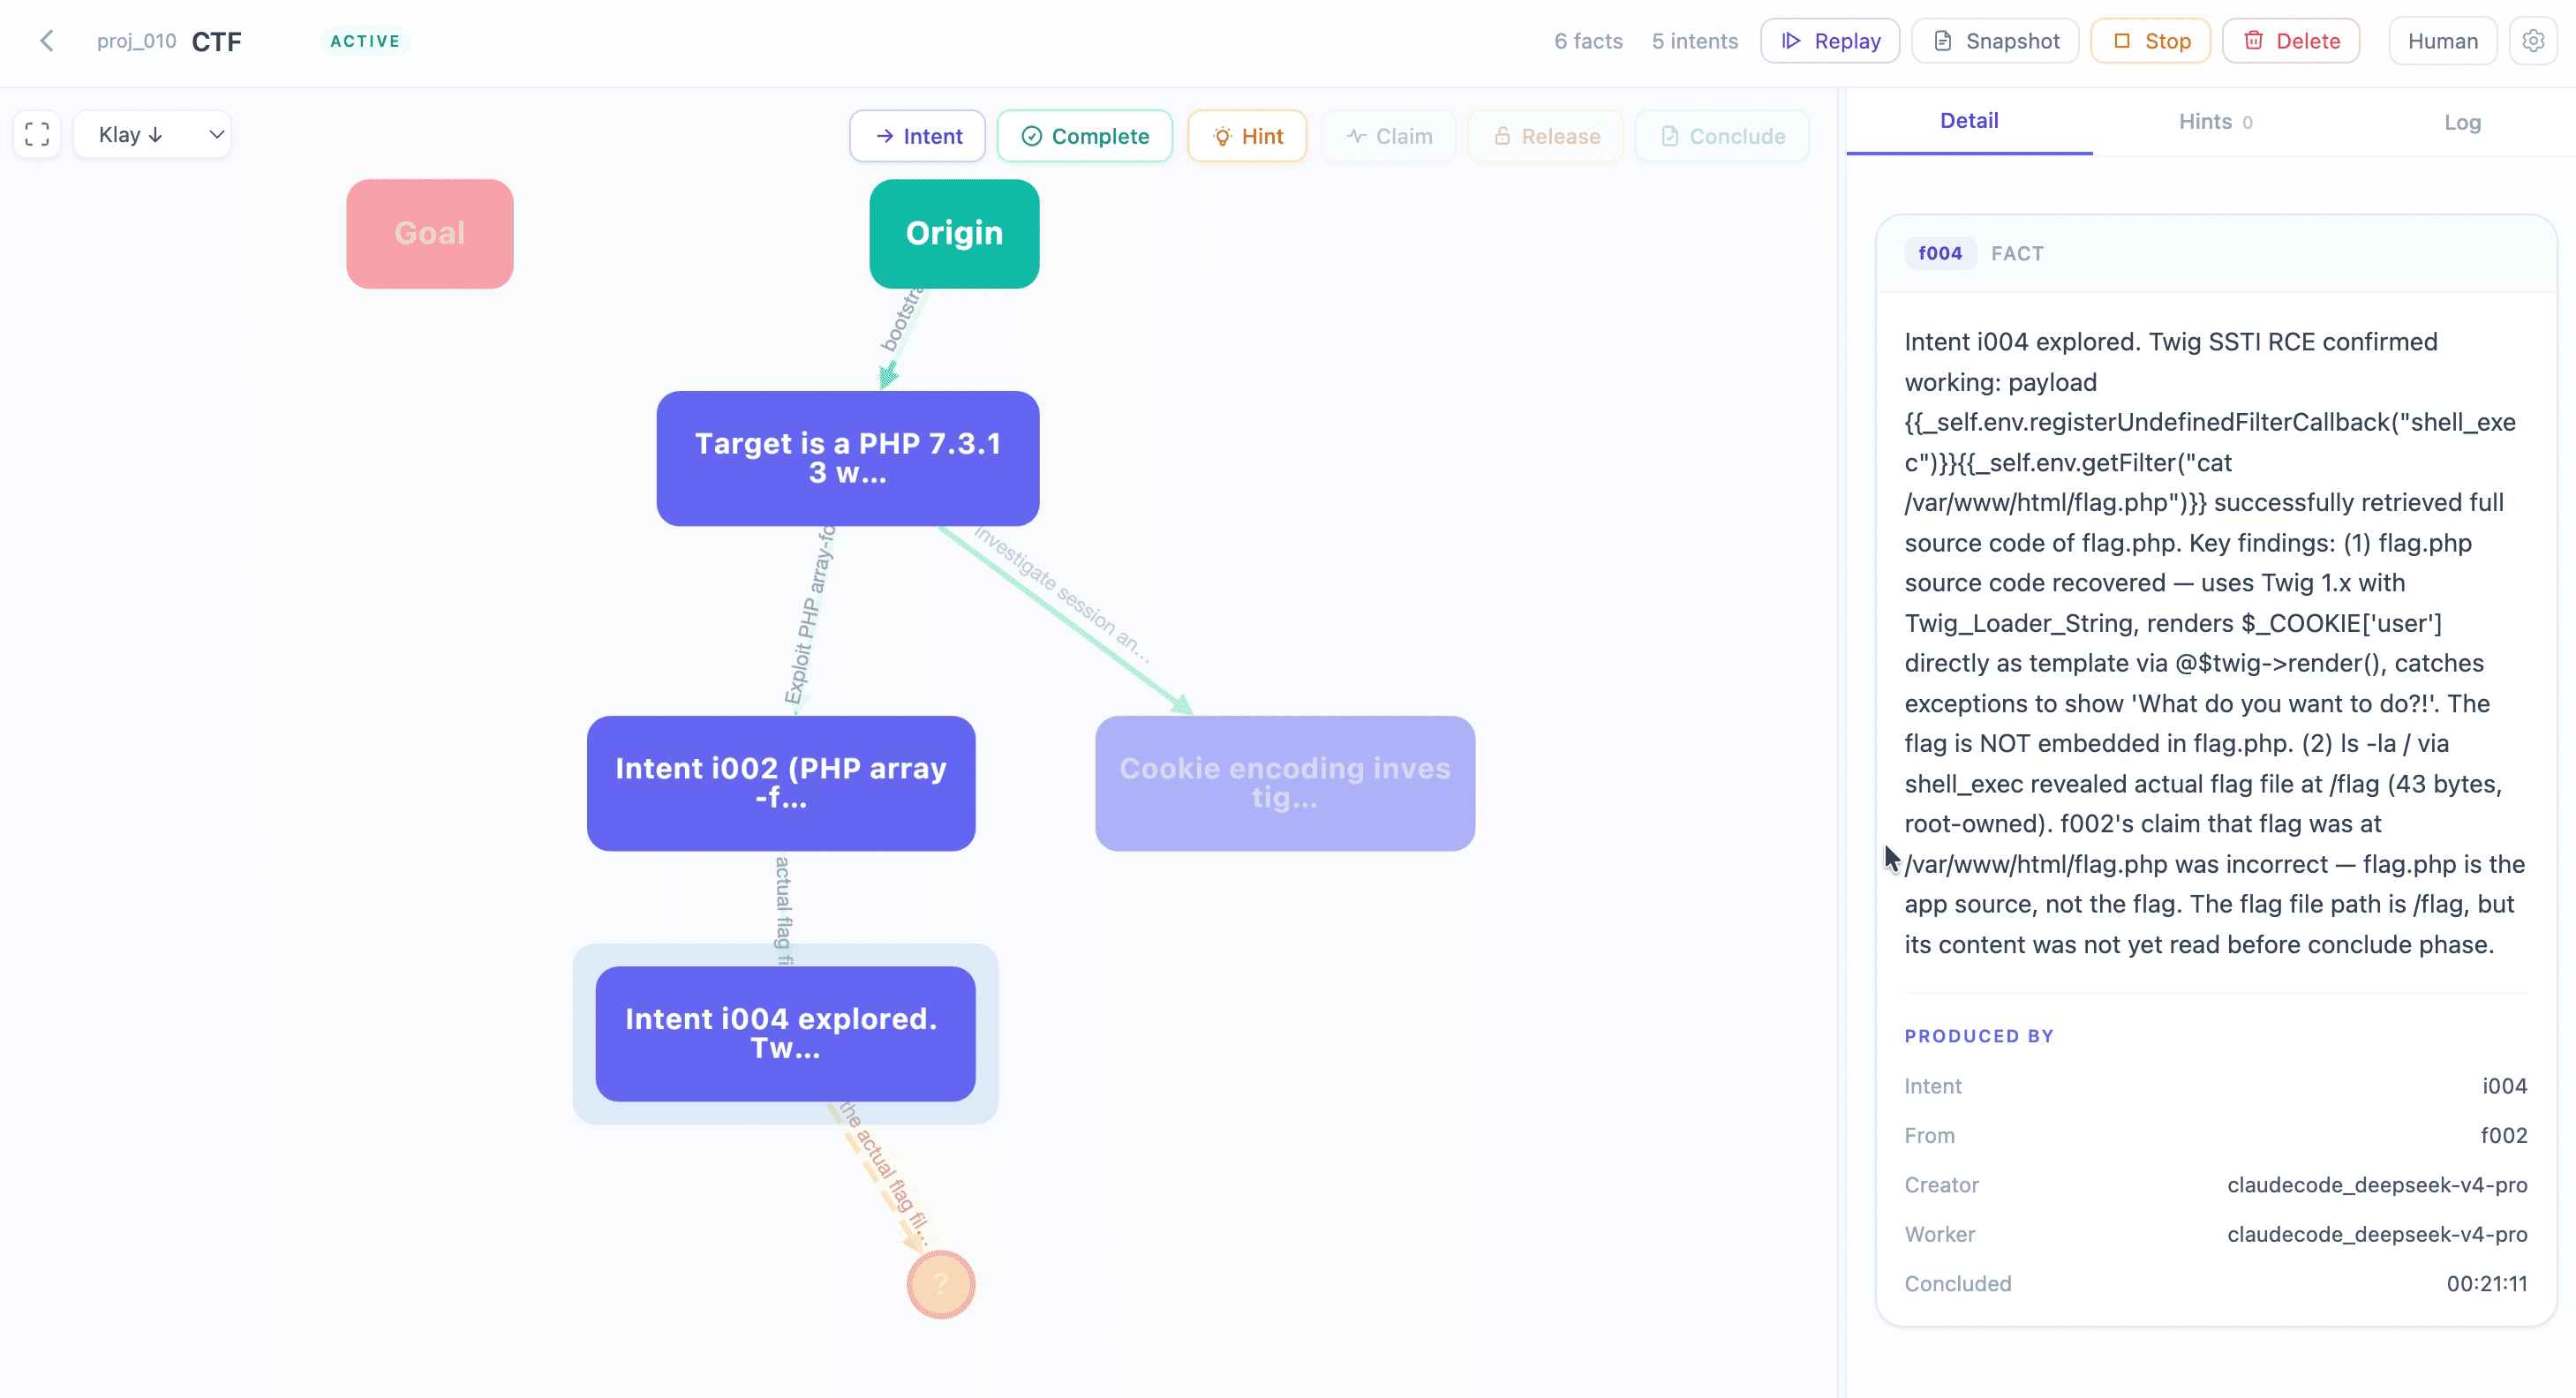
LLM-driven state-space search engine for autonomous penetration testing, CTF solving, and vulnerability research. Uses blackboard architecture with…

DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…

BOF implementations of CVE-2024-26229 for Cobalt Strike and BruteRatel

A listener profile for the Mythic C2 framework that utilizes AI vendors file API's

Search and download public exploits from the Vulners database — online, or fully offline from a local SQLite FTS5 index.