cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

Hack the World using Termux

Adversary Emulation Framework

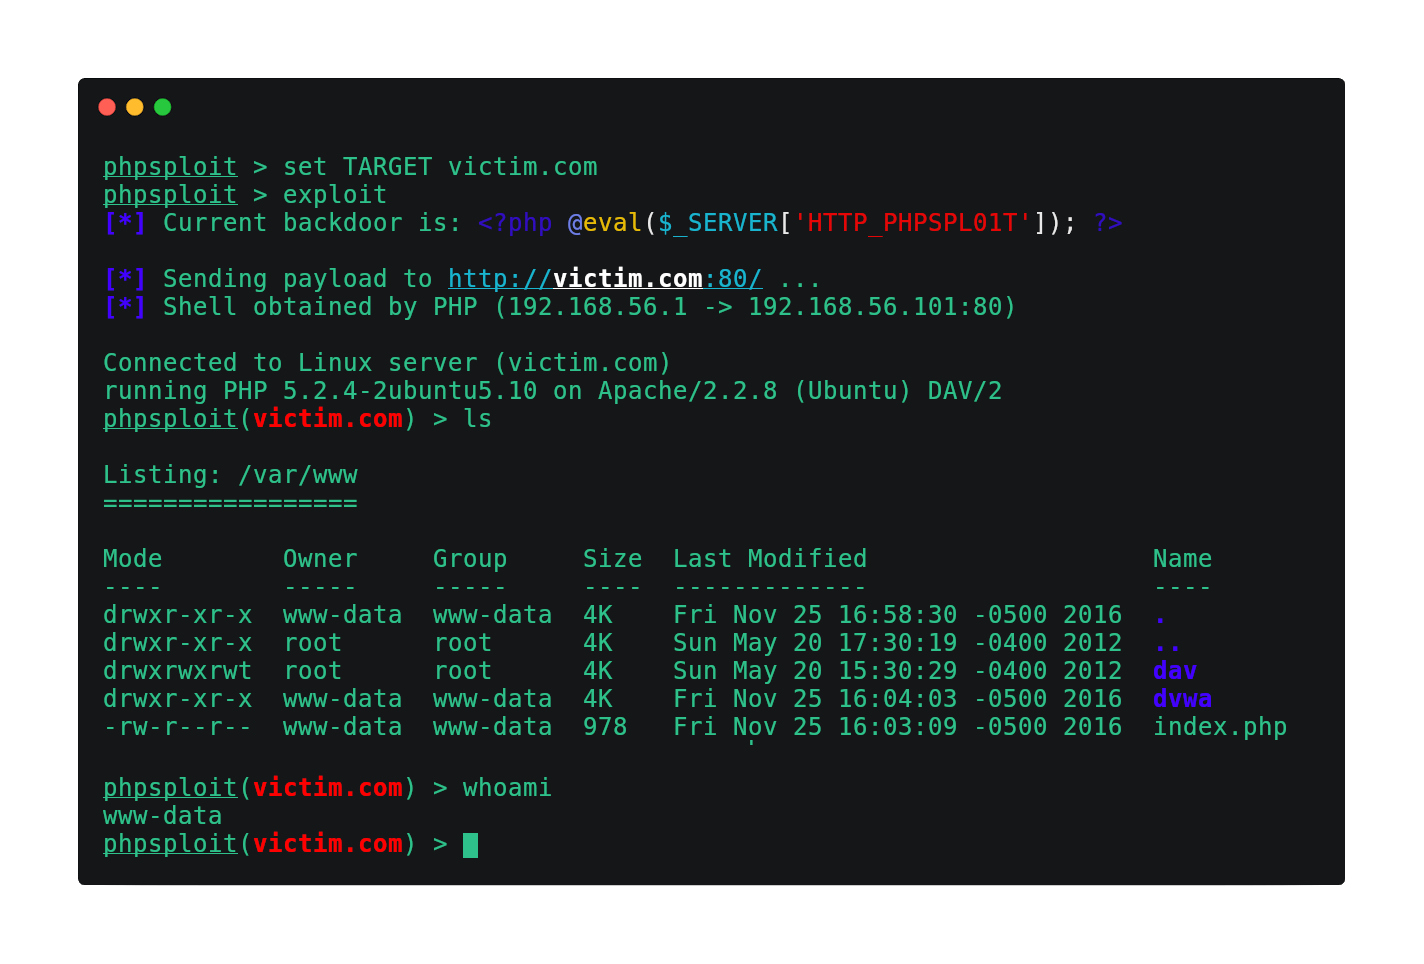
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor

Python-Based Pentesting Framework

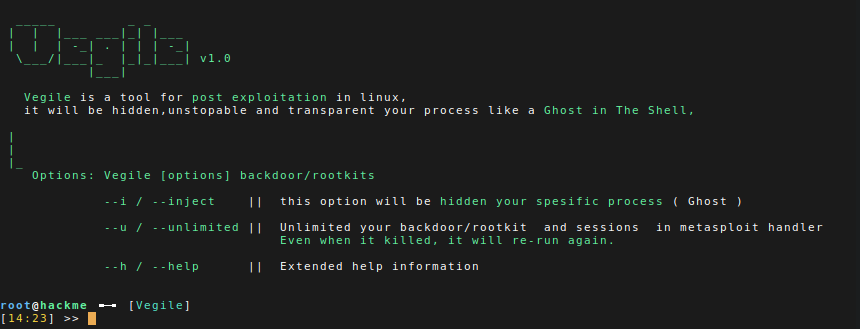
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…

Metarget is a framework providing automatic constructions of vulnerable infrastructures.

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Modular penetration testing platform that enables you to write, test, and execute exploit code.

link is a command and control framework written in rust

CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.

All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…


Automated penetration testing & attack surface management platform. Recon, scan, exploit, report — 600+ exploits, 90+ integrations, 10K+ detections.

Exploit for CVE-2021-1675 (PrintNightmare) enabling local and remote SYSTEM-level privilege escalation on Windows via the Print Spooler service.…

OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup

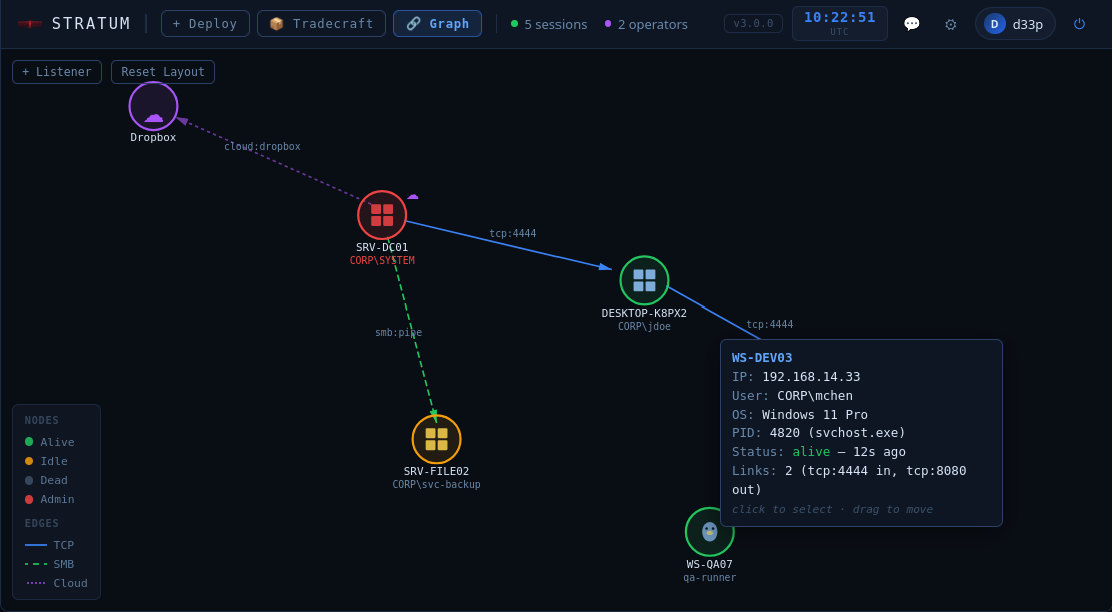
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting