

FUD-C2-Framework
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
7
x3r0day/fud-c2-frameworkA fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
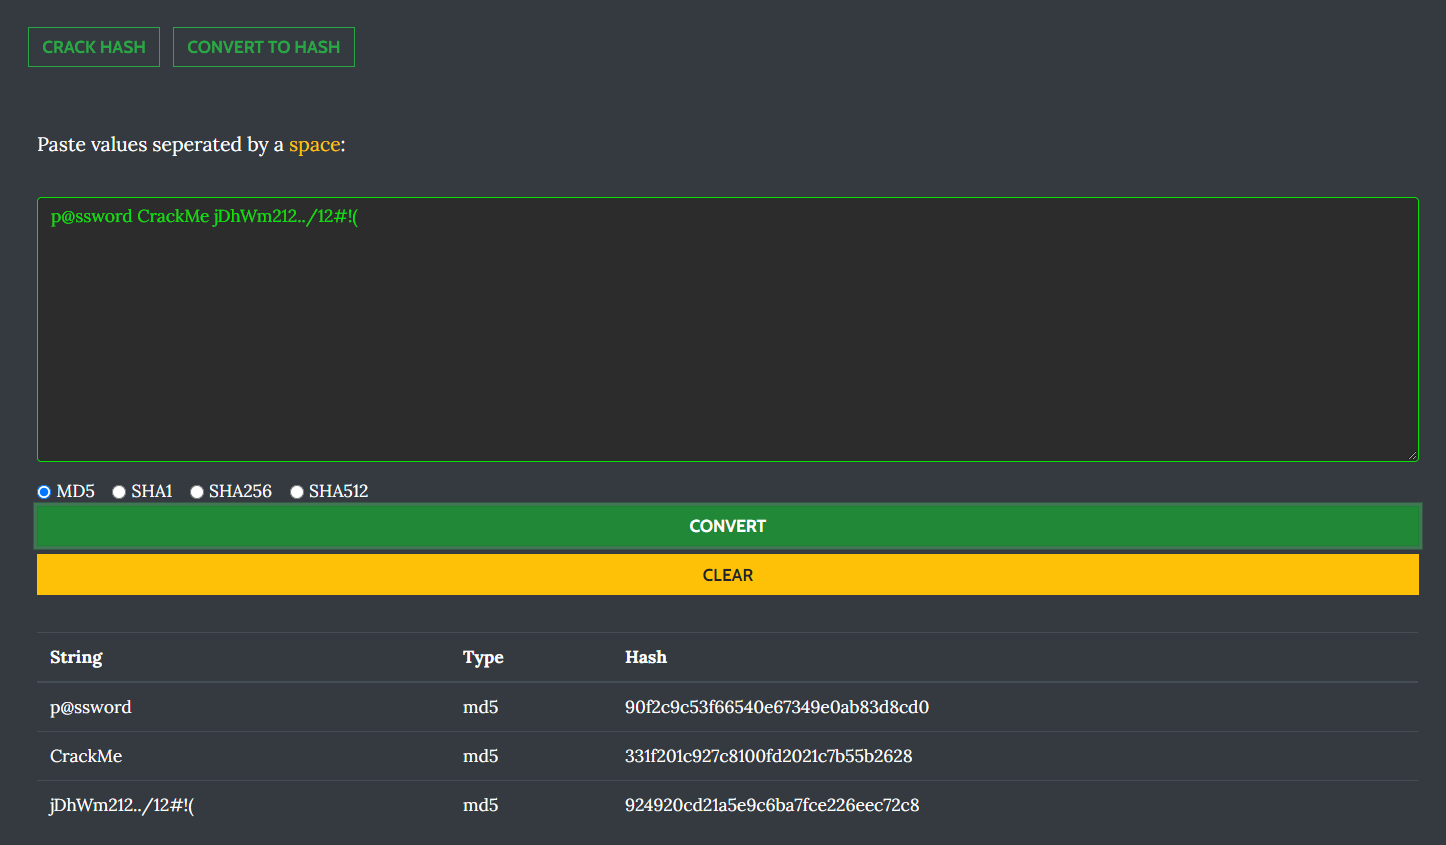 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 4n4nk3/tinkerershell
A simple python reverse shell written just for fun.
 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
 lesnuages/hershell
Multiplatform reverse shell generator
 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 hackerschoice/bincrypter
Pack/Encrypt/Obfuscate ELF + SHELL scripts