
nextdns
 nextdns/nextdns
Command-line DNS-over-HTTPS client and proxy for encrypted, tamper-resistant DNS resolution; works with any DoH provider and supports split-horizon…
encryption-decryption-toolsnetwork-securityprivacy+1
4.2k
nextdns/nextdnsCommand-line DNS-over-HTTPS client and proxy for encrypted, tamper-resistant DNS resolution; works with any DoH provider and supports split-horizon…
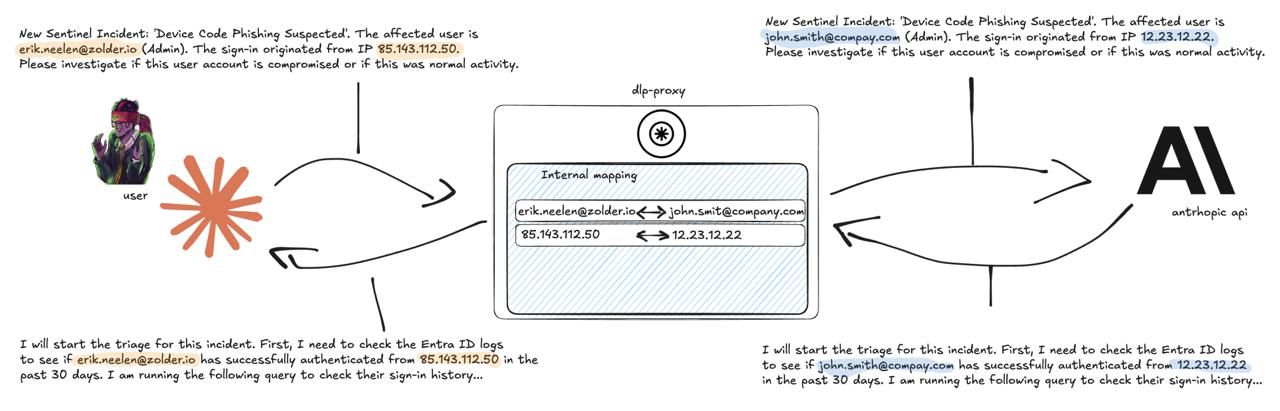 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 ph4ntonn/stowaway
Multi-hop proxy tool for pentesters enabling traffic routing through multiple nodes, SOCKS5/SSH tunneling, port forwarding, remote shell, and…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 dnscrypt/dnscrypt-proxy
Flexible DNS proxy with encrypted protocol support (DNSCrypt v2, DoH, ODoH, Anonymized DNS), caching, filtering, load balancing, and cloaking for…
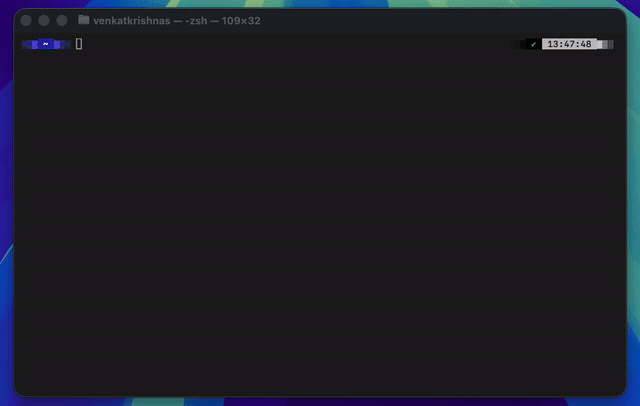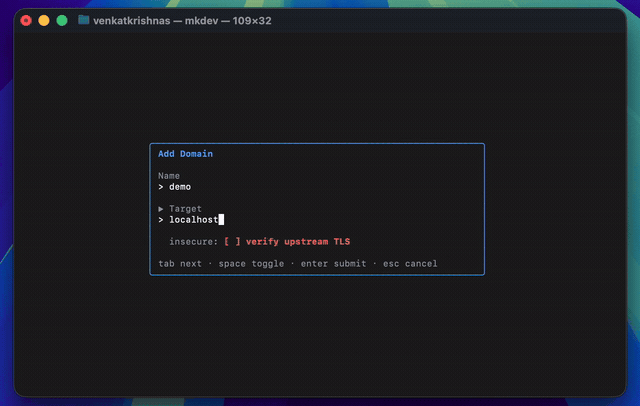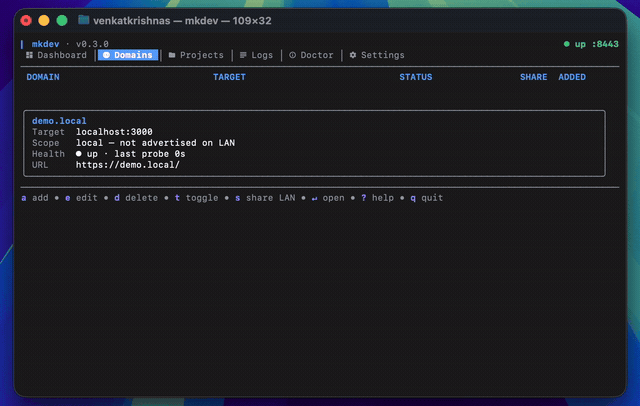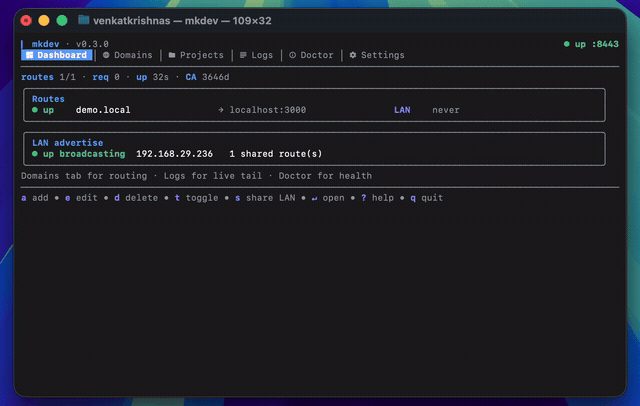 venkatkrishna07/mkdev
Trusted localhost HTTPS — local CA, /etc/hosts, mDNS LAN sharing, reverse proxy. Maps https://name.local → localhost:port
 taherio/redi
Automated script for setting up CobaltStrike redirectors (nginx reverse proxy, letsencrypt)
 droe/sslsplit
Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…
 trusttunnel/trusttunnel
Open-source VPN protocol that tunnels TCP, UDP, and ICMP traffic over HTTPS, bypassing DPI and throttling. Features split tunneling, SOCKS5 proxy,…
 cbeuw/cloak
A censorship circumvention tool to evade detection by authoritarian state adversaries
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
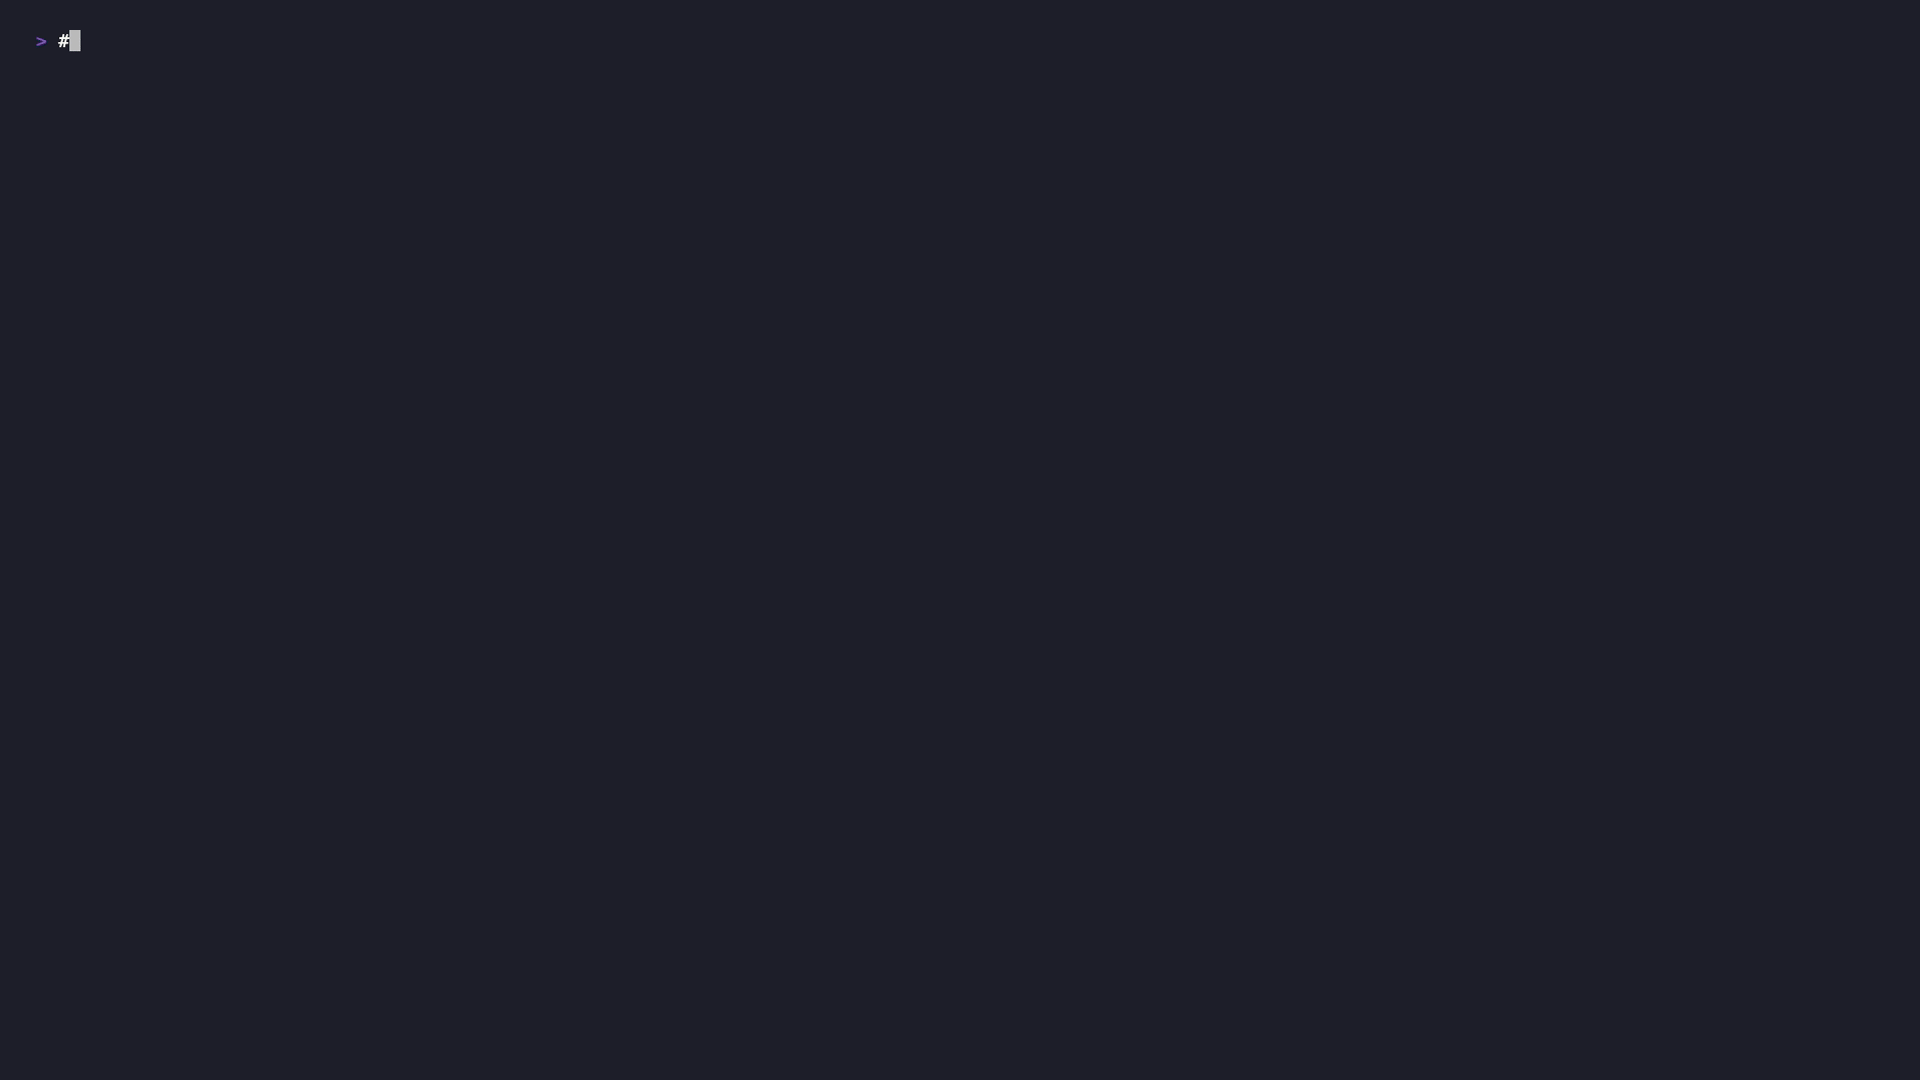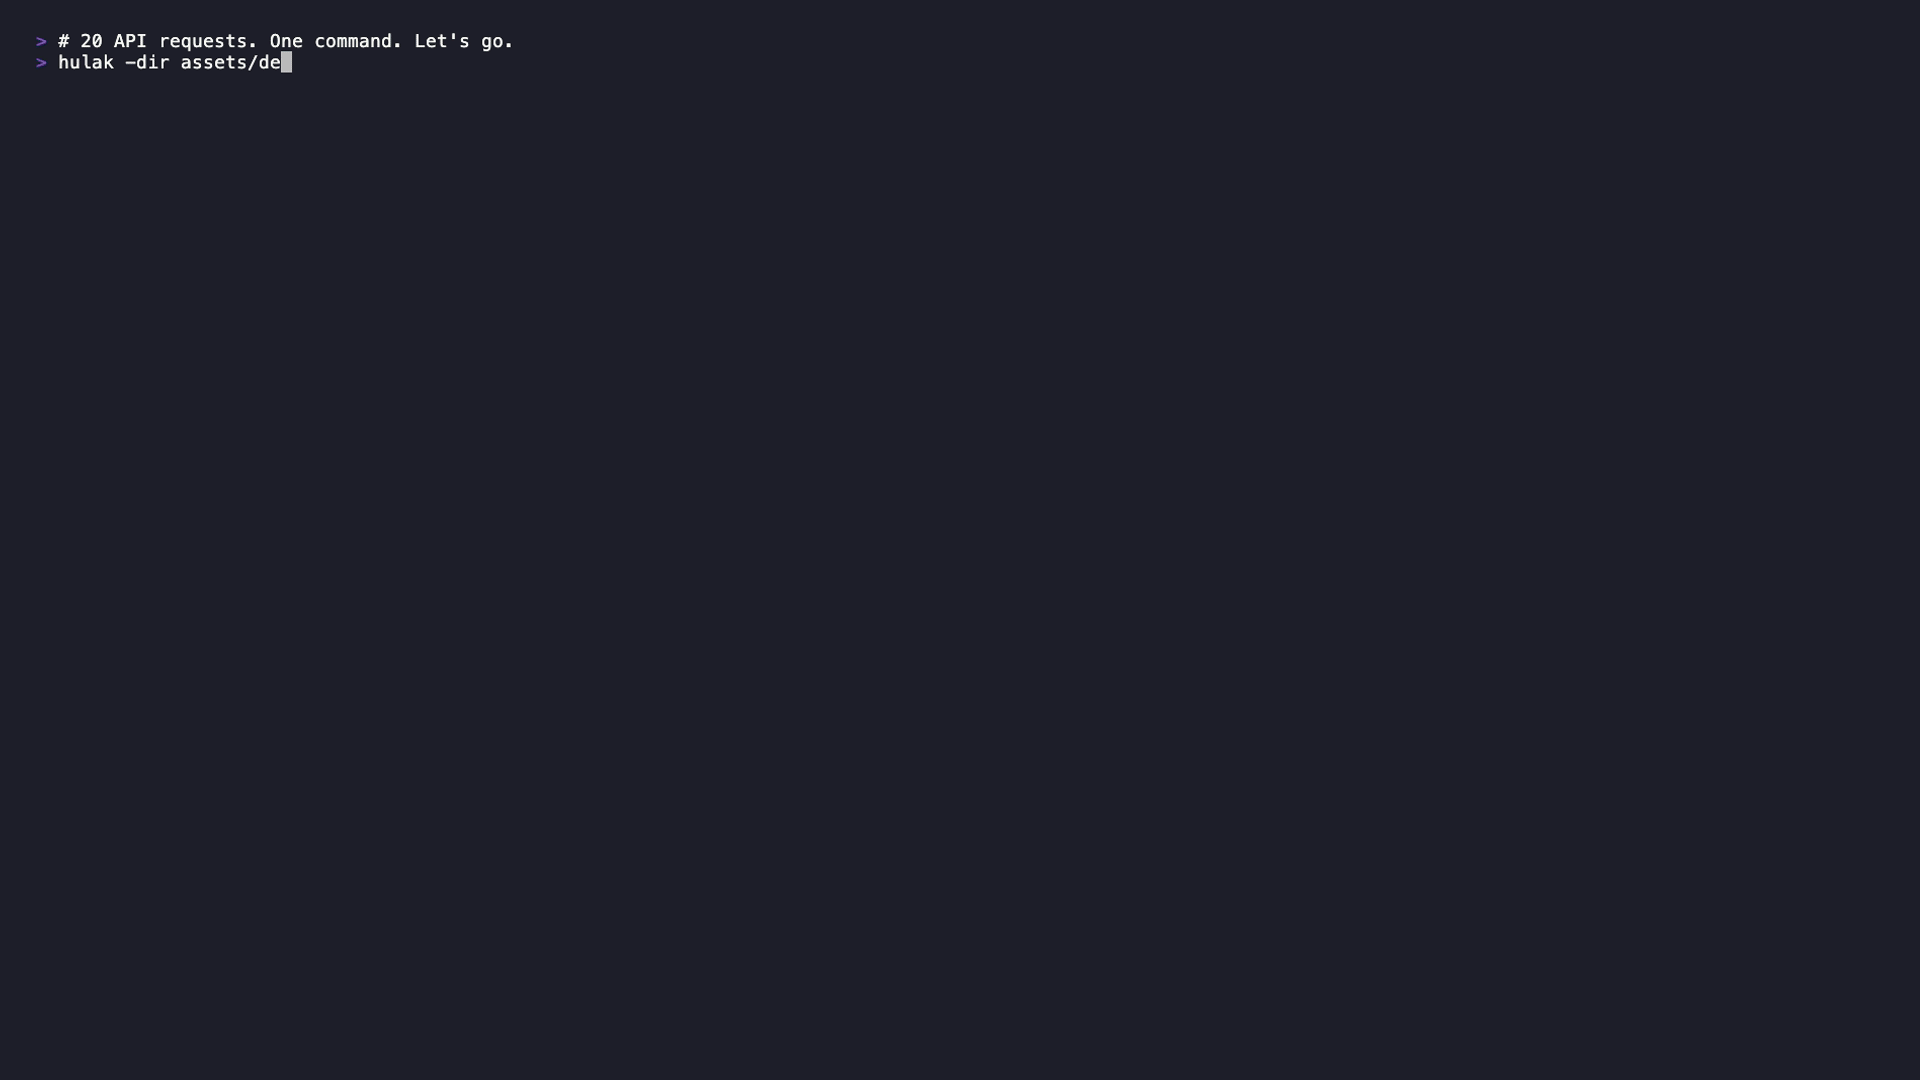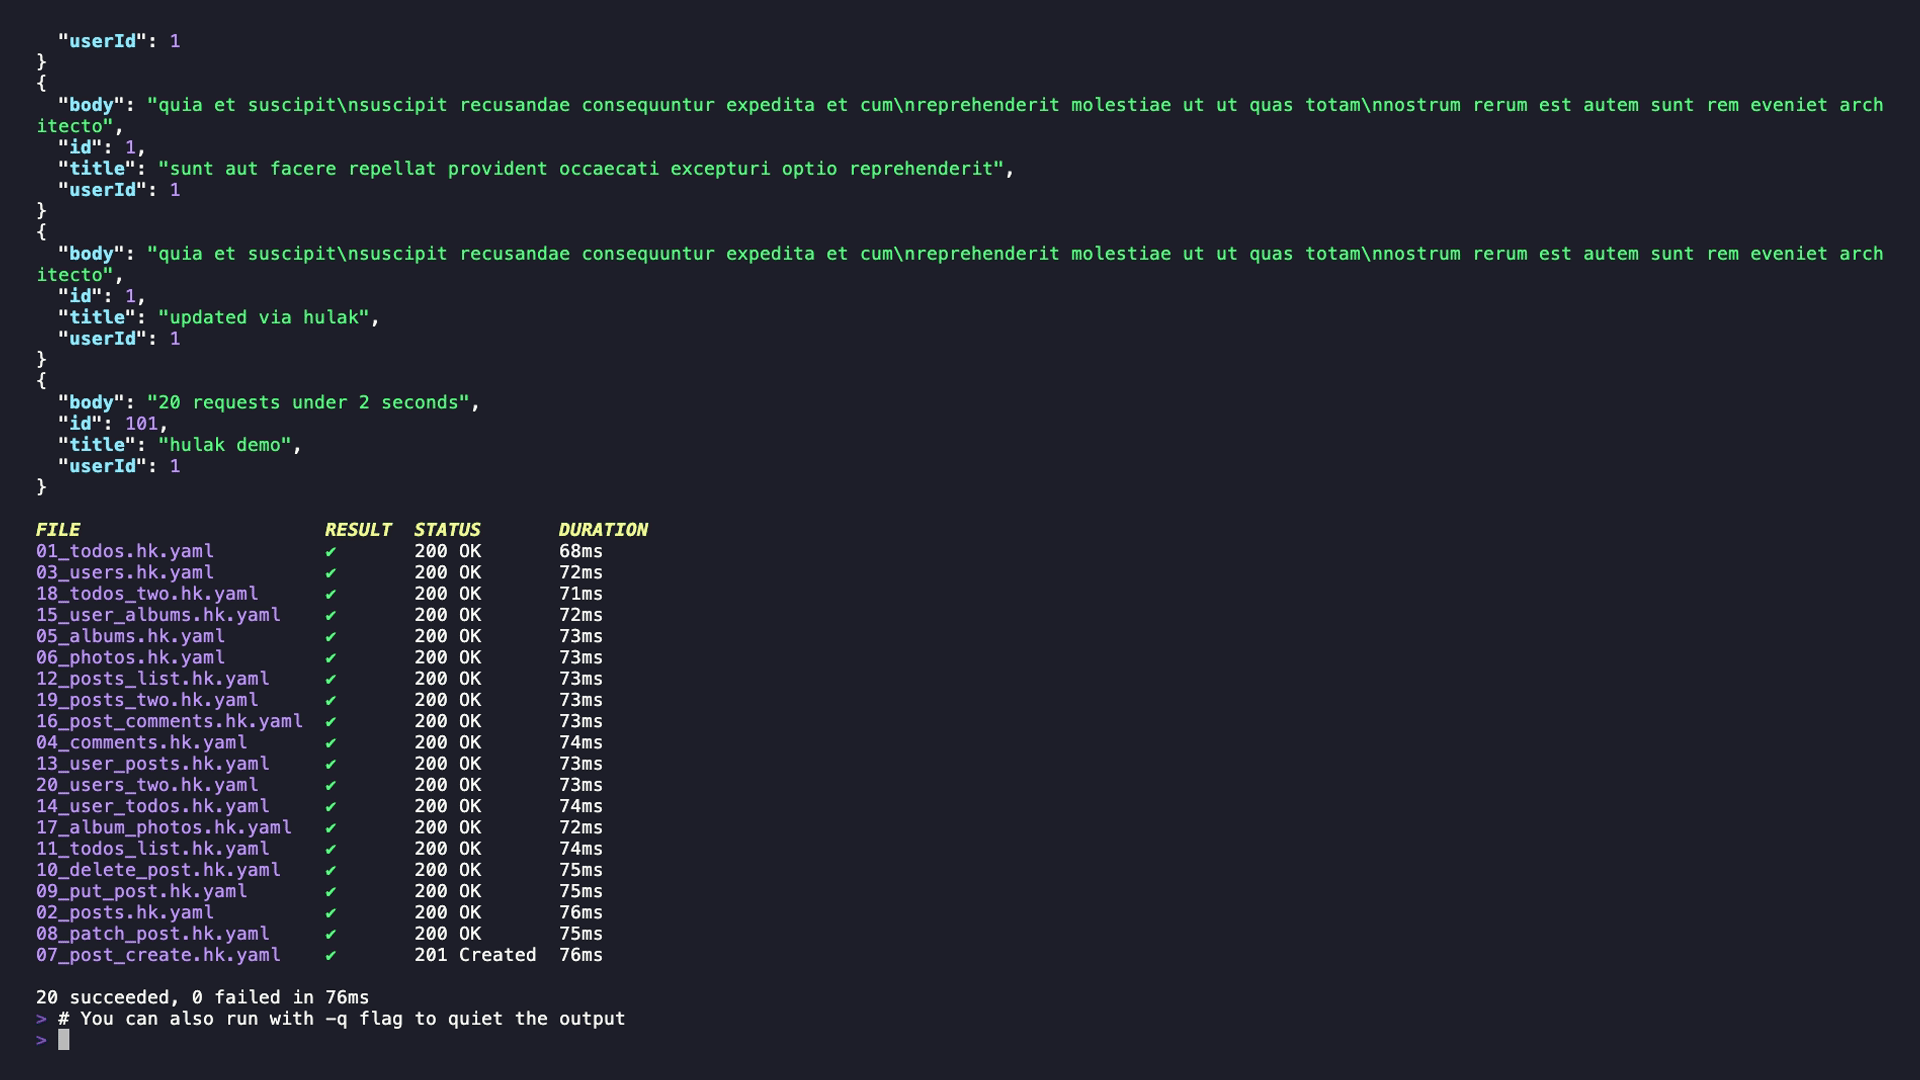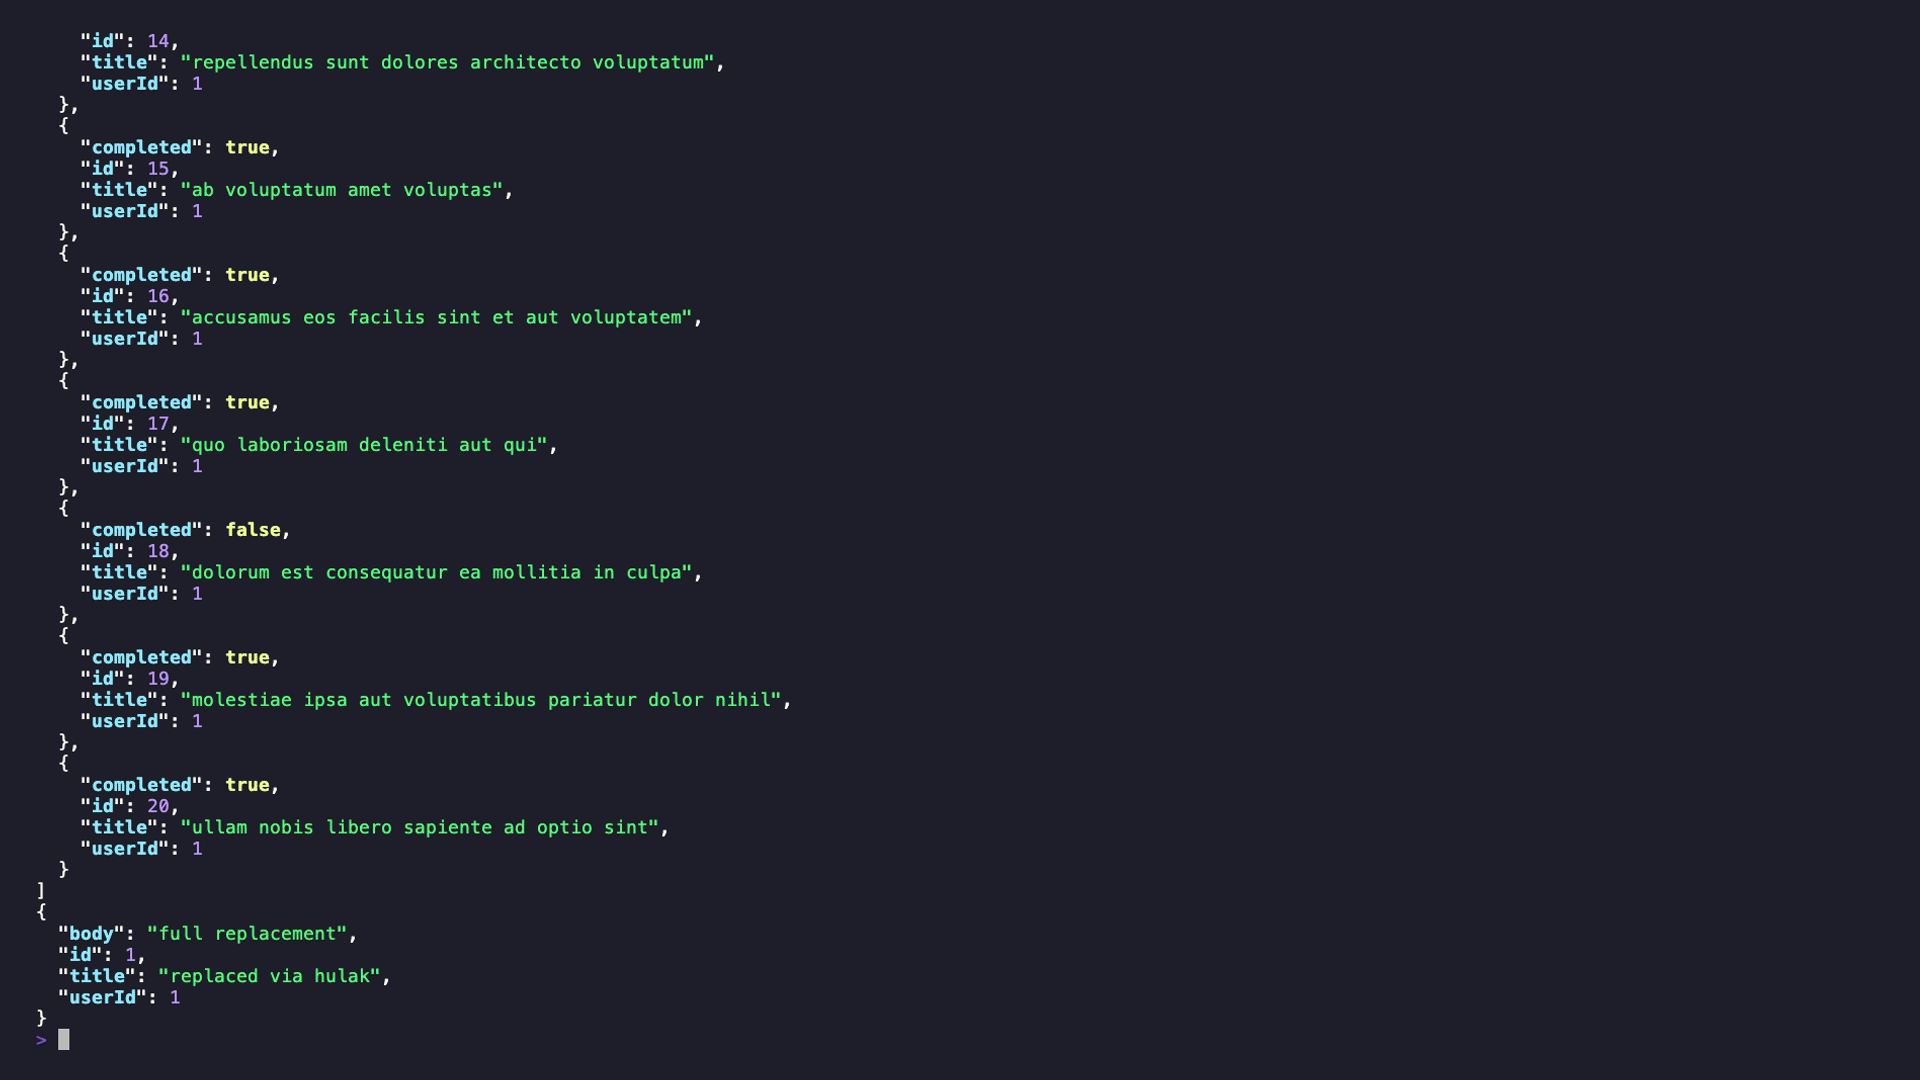 xaaha/hulak
Lightweight file-based CLI API client with age-encrypted secrets, first-class GraphQL support and MCP server for agentic workflow.
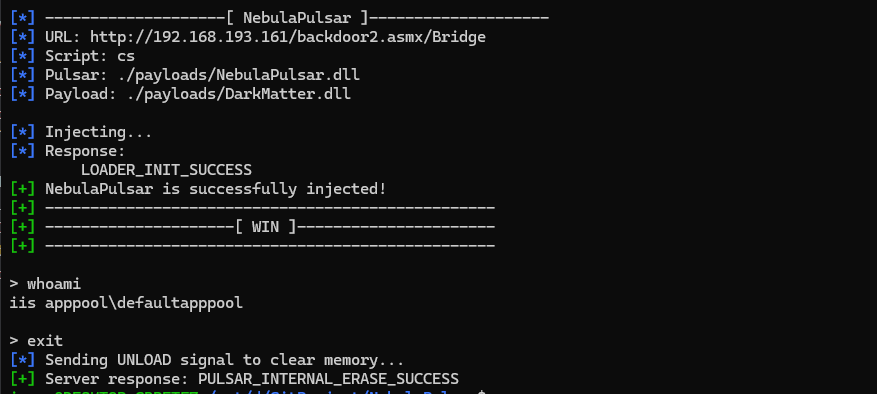 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 ipopov/starttls-mitm
A starttls-capable transparent man-in-the-middle proxy
 x011/smtp-tunnel-proxy
A high-speed covert tunnel that disguises TCP traffic as SMTP email communication to bypass Deep Packet Inspection (DPI) firewalls.
 enkomio/alanframework
A C2 post-exploitation framework
 compasssecurity/samlraider
SAML2 Burp Extension
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.