
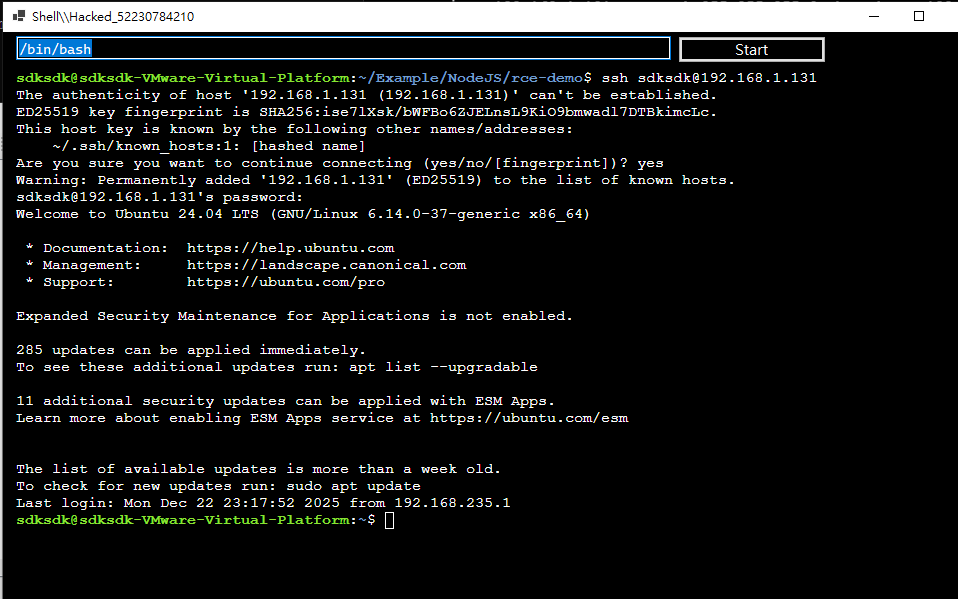
Eden-RAT
 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
command-and-controlencryption-decryption-toolsexploitation+5
33
iss4cf0ng/eden-ratAn open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 iagox86/dnscat2
Encrypted command-and-control tunnel over DNS protocol. Creates stealthy C&C channels for penetration testing, with file transfer, shell access, and…
 droe/sslsplit
Transparent man-in-the-middle proxy that terminates SSL/TLS connections, forges certificates on-the-fly, and logs decrypted traffic for network…
 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
 0x36/vpnpivot
Explore the network using VPNPivot tool
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
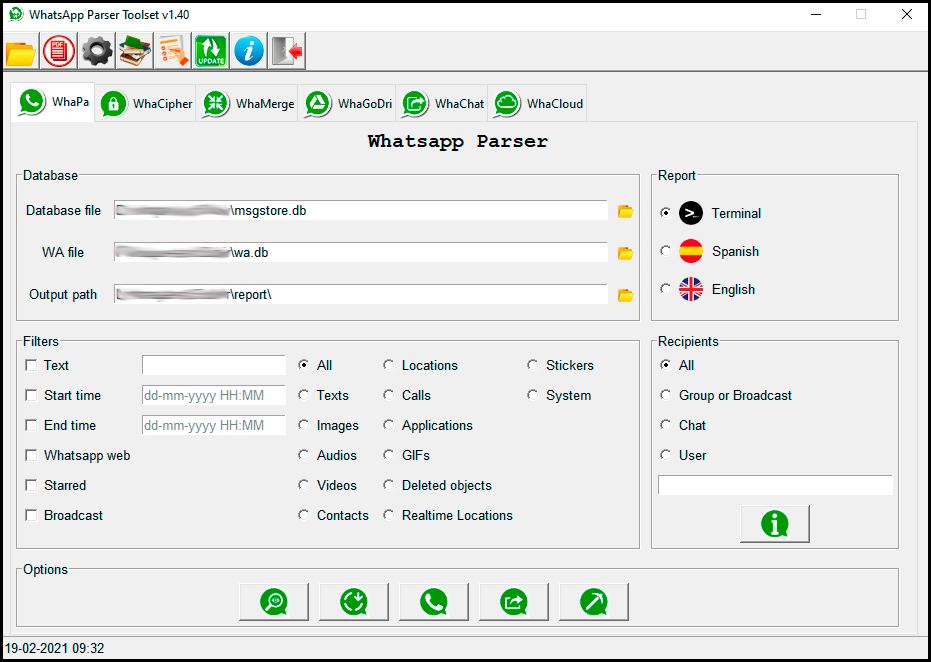 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 donctl/sandy
Release of the sandy framework.
 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 jas502n/2024informationsecurityengineer
2024年信息安全工程师、2024InformationSecurityEngineer
 syss-research/wirebug
WireBug is a toolset for Voice-over-IP penetration testing
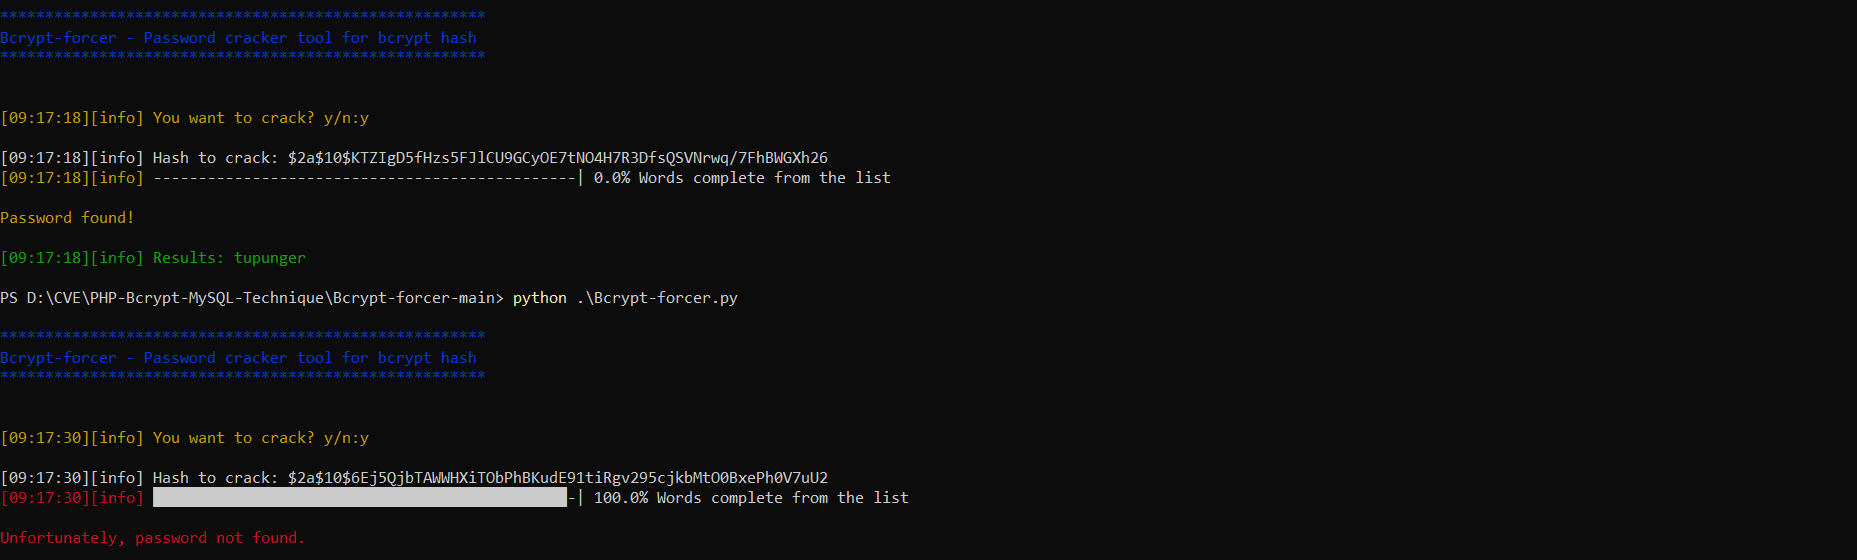 nu11secur1ty/bcrypt-forcer
Bcrypt hash cracker for penetration testing and password recovery. Decrypts Bcrypt hashes using dictionary or brute-force methods.
 adel-hx0d/cve-2025-59287
Exploitation toolkit for CVE-2025-59287 RCE in WSUS. Includes AES payload encryption and an exploitation module for authorized penetration testing.
 compasssecurity/samlraider
SAML2 Burp Extension
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…