

CVE-2025-24204
 ffri/cve-2025-24204
PoC and technical details of CVE-2025-24204
encryption-decryption-toolsexploitationmemory-forensics+2
11411 months ago
ffri/cve-2025-24204PoC and technical details of CVE-2025-24204
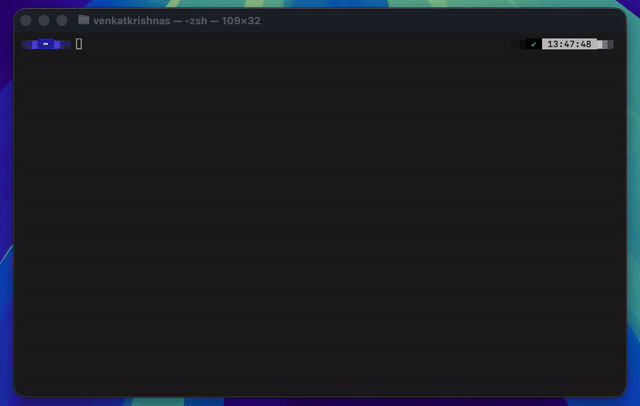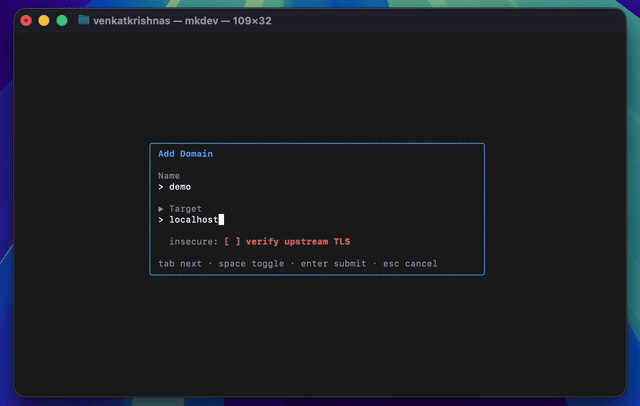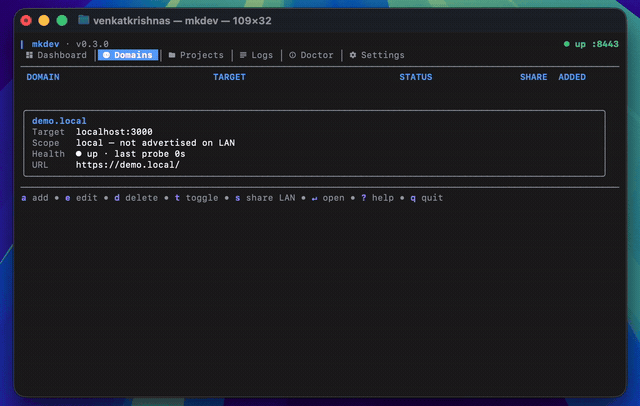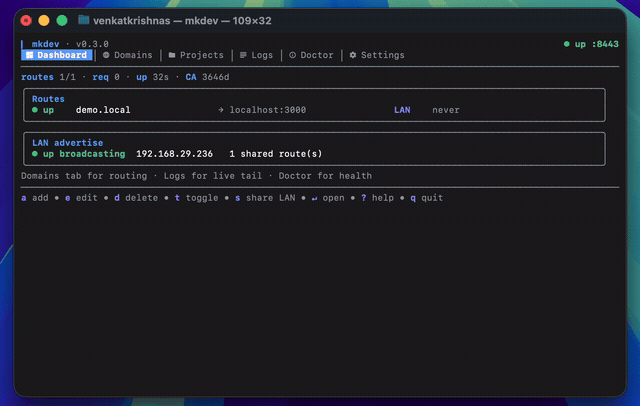 venkatkrishna07/mkdev
Trusted localhost HTTPS — local CA, /etc/hosts, mDNS LAN sharing, reverse proxy. Maps https://name.local → localhost:port
 watchfulip/tp-link-decrypt
Decrypt TP-Link Firmware
 guibacellar/nxransomware
A next generation of ransomware. Fully written using a .Net Framework + C&C System
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
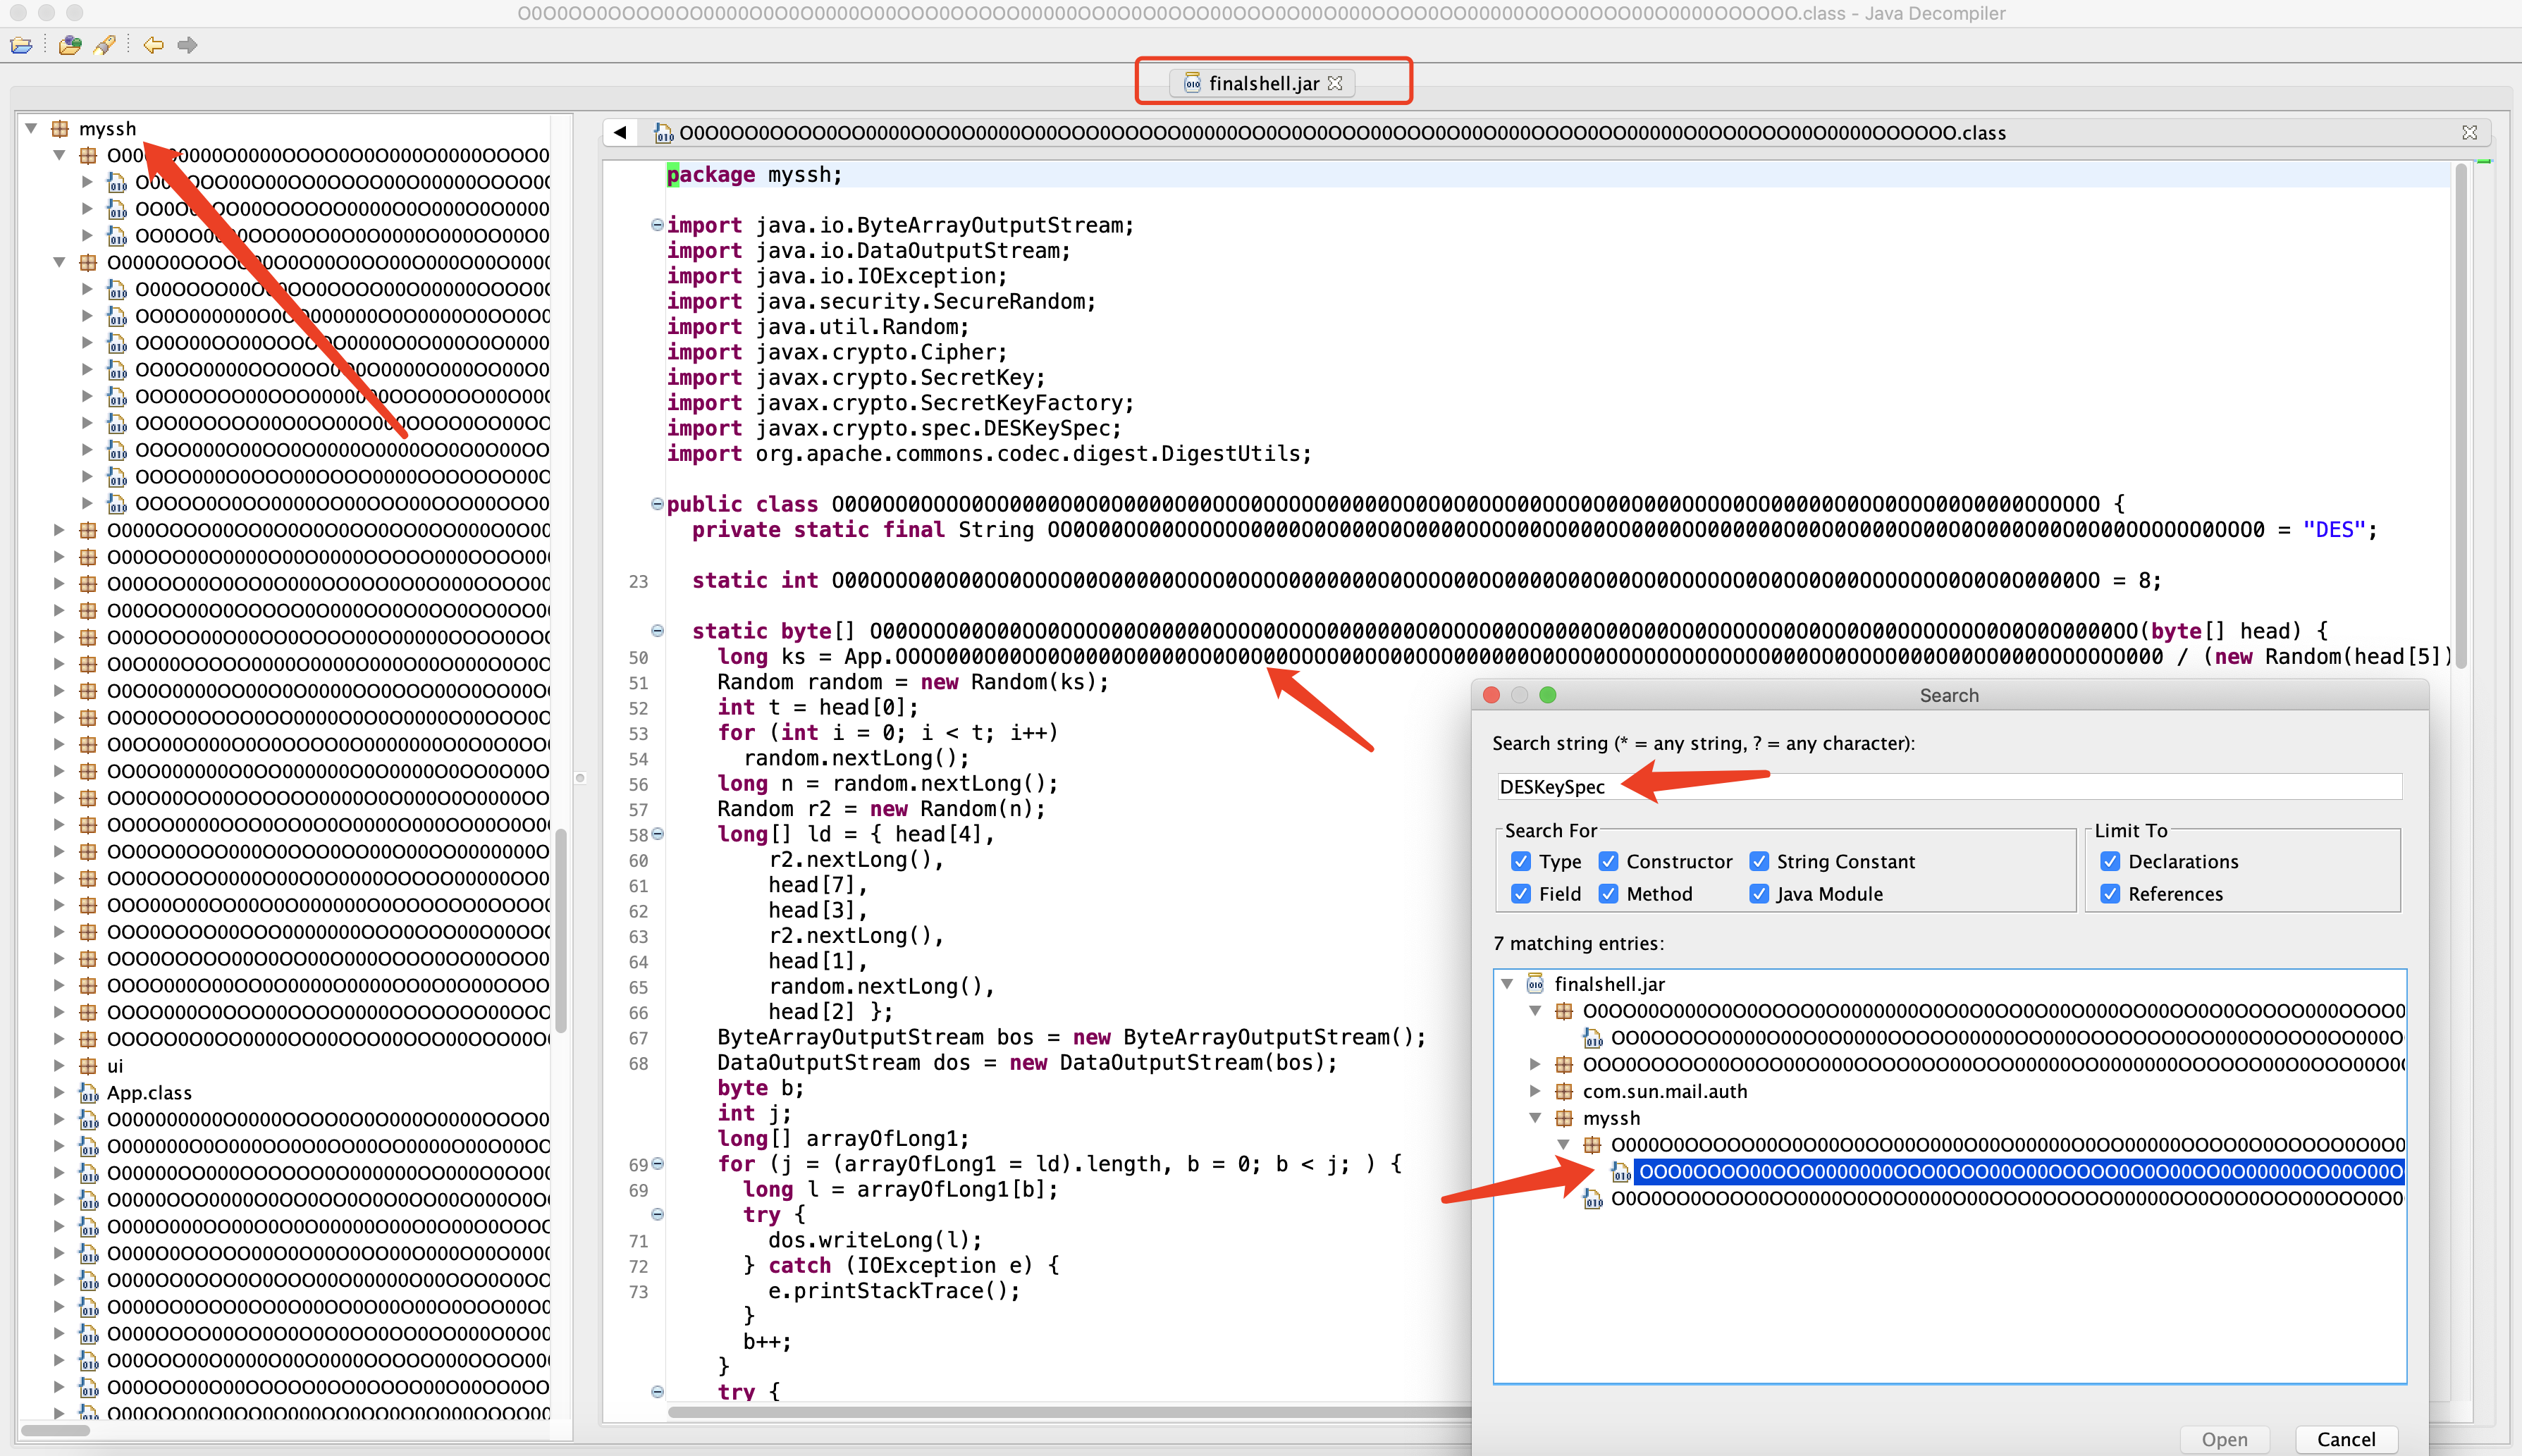 jas502n/finalshelldecodepass
FinalShellDecodePass 加密解密
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 x86byte/sbox
Compile-time AES string obfuscation for C++
 dr4k0nia/xorstringsnet
Easy XOR string encryption for NET based binaries
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
 infobyte/cve-2023-21036
Detection and sanitization for Acropalypse Now - CVE-2023-21036
 blasty/sonos
Exploit and tooling for Amlogic-based Sonos devices: dumps OTP/eFUSE via an EL3 exploit, extracts LUKS decryption keys, and fetches/decrypts OTA…
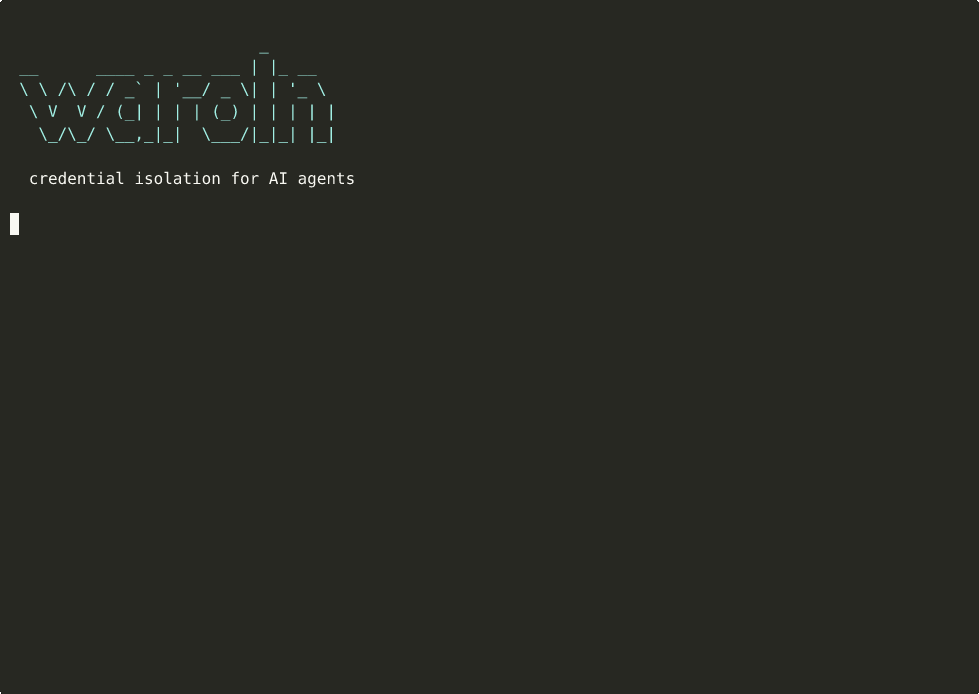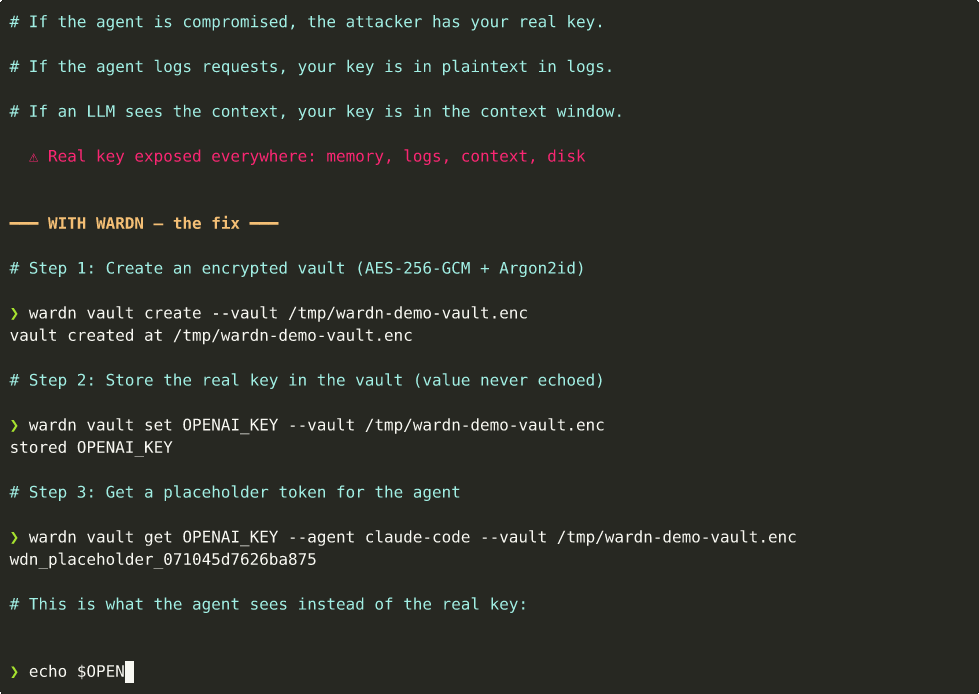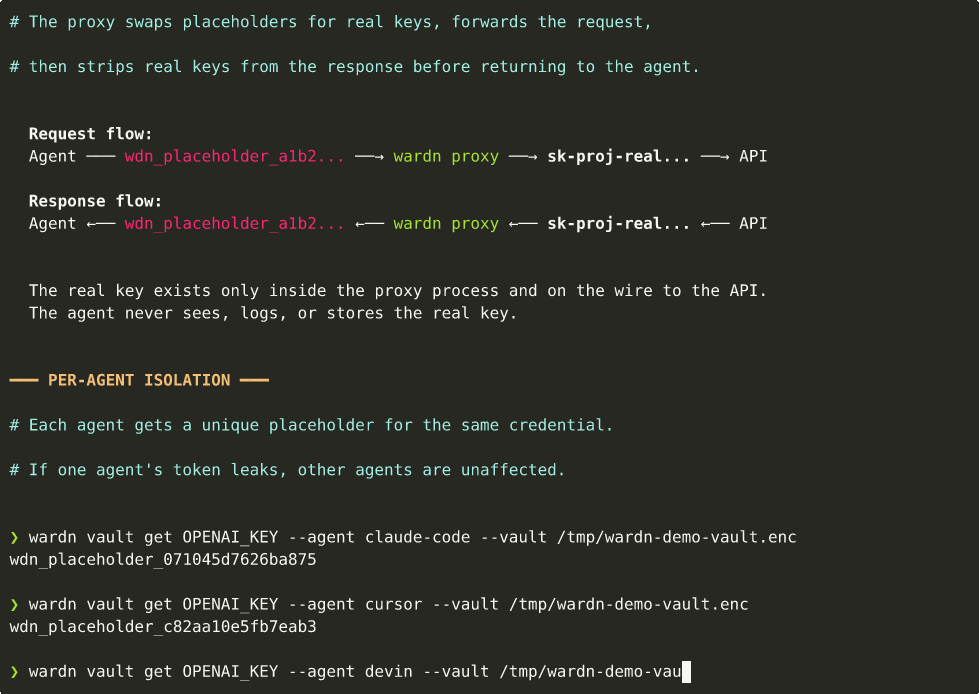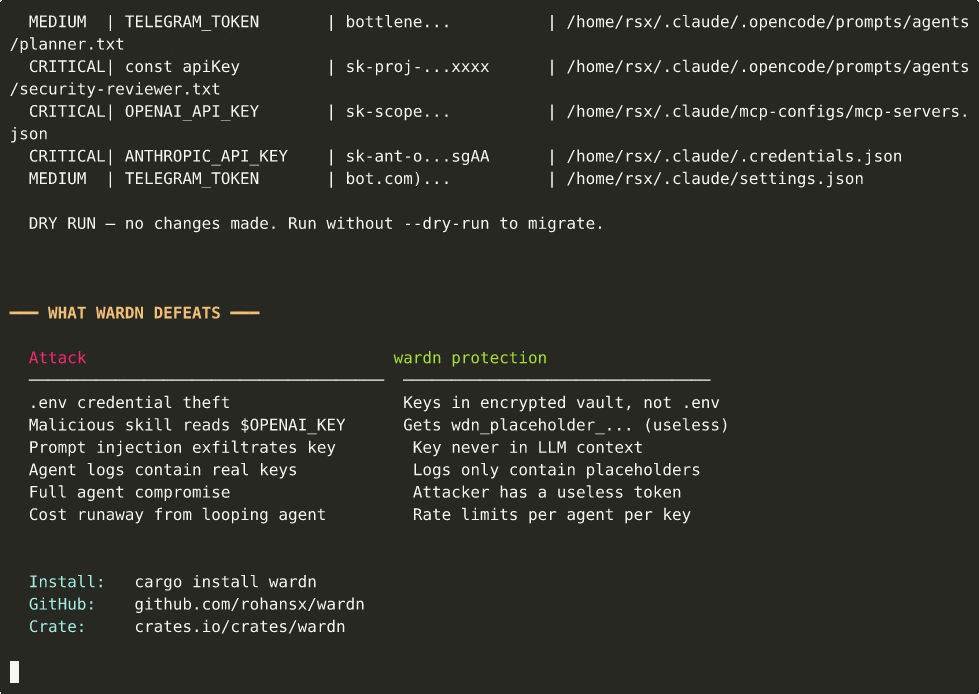 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 reecdeep/hivev5_keystream_decryptor
bad stuffs by bad guys