

laravel-crypto-killer
 synacktiv/laravel-crypto-killer
A tool designed to exploit bad implementations of decryption mechanisms in Laravel applications.
encryption-decryption-toolsexploitationpayload-generation+2
146
synacktiv/laravel-crypto-killerA tool designed to exploit bad implementations of decryption mechanisms in Laravel applications.
 paradoxis/adsyncdump-bof
The ADSyncDump BOF is a port of Dirk-Jan Mollema's adconnectdump.py / ADSyncDecrypt into a Beacon Object File (BOF) with zero dependencies.

 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 ricardojoserf/sharpcoverttube
Youtube as C2 channel - Control Windows systems uploading QR videos to Youtube
 jfmaes/gg-aesy
Hide cool stuff in images :)
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 ffri/cve-2025-24204
PoC and technical details of CVE-2025-24204
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.

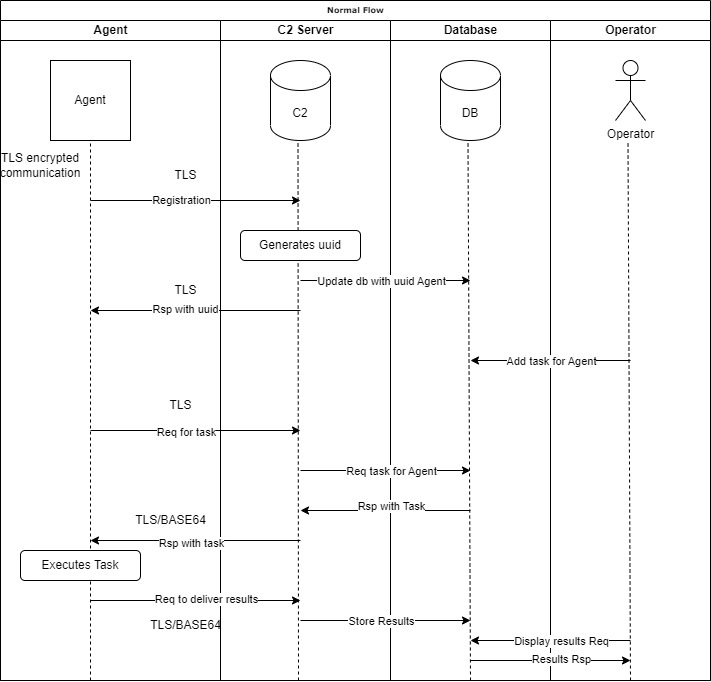 voukatas/commander
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…
 ricardojoserf/covert-control
Google Drive, OneDrive and Youtube as covert-channels - Control systems remotely by uploading files to Google Drive, OneDrive, Youtube or Telegram
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…