
Phirautee
 viralmaniar/phirautee
A proof of concept crypto virus to spread user awareness about attacks and implications of ransomwares. Phirautee is written purely using PowerShell…
command-and-controldata-exfiltrationeducation+8
124
viralmaniar/phirauteeA proof of concept crypto virus to spread user awareness about attacks and implications of ransomwares. Phirautee is written purely using PowerShell…
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 guibacellar/nxransomware
A next generation of ransomware. Fully written using a .Net Framework + C&C System
 lawndoc/mediator
An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
 ricardojoserf/covert-control
Google Drive, OneDrive and Youtube as covert-channels - Control systems remotely by uploading files to Google Drive, OneDrive, Youtube or Telegram
 cys3c/evilosx
A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.
 28zaaky/pulse-c2
HTTPS C&C Framework with encrypted beacons, web dashboard, and Windows agent.
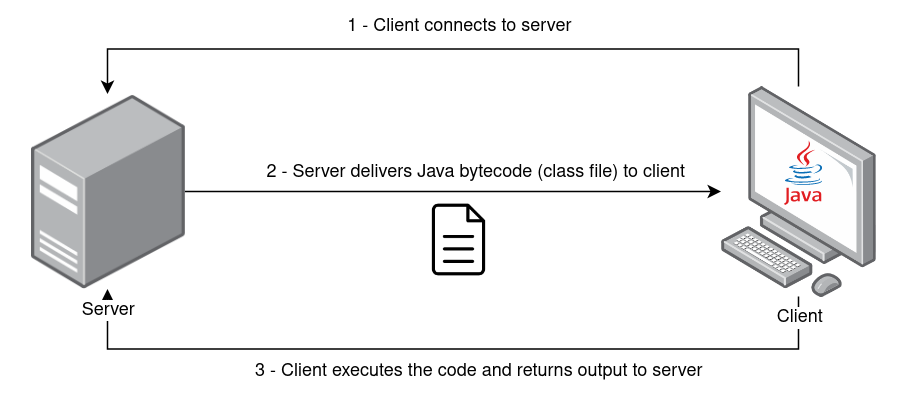 joaovarelas/java-remote-class-loader
Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…
 rek7/ddoor
DDoor - cross platform backdoor using dns txt records
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
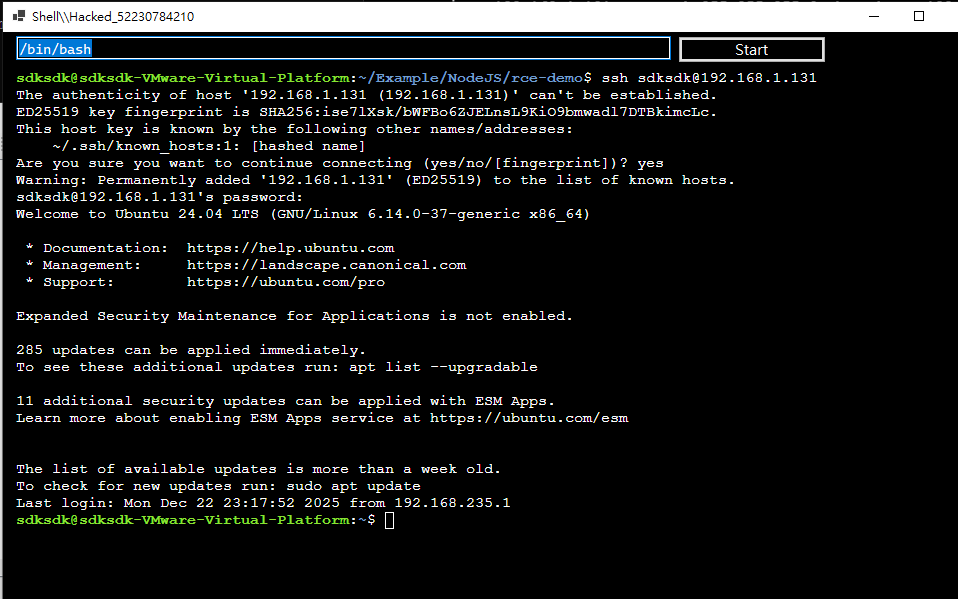 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
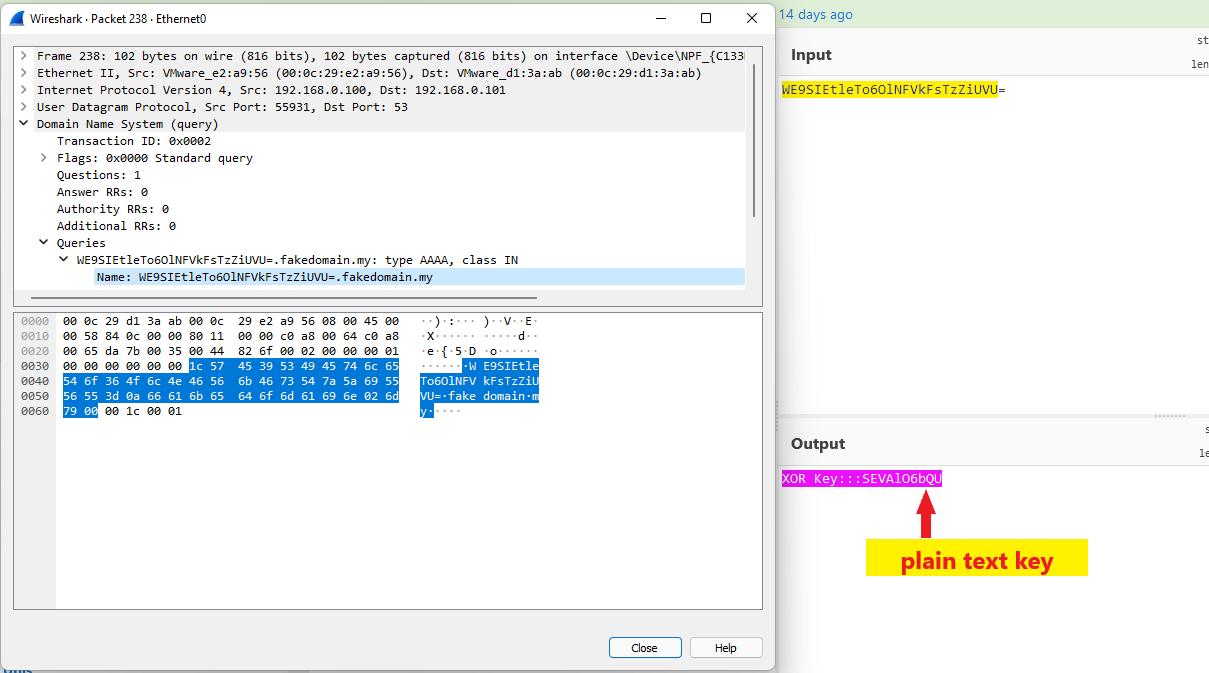 aniqfakhrul/sharpdnsexfil
C# tool for exfiltrating files over DNS using XOR and asymmetric encryption, designed for red team engagements with restricted outbound connections.