ESAPI__esapi-java-legacy_CVE-2022-24891_2-2-3-1

OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…

OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…

Java security library providing contextual encoders and sanitizers to automatically remediate vulnerabilities like XSS, path traversal, and command…

OAuth and OAuth2 support library for Spring Security, enabling secure API authentication and authorization for consumer and provider implementations…

OpenSSL 1.0.1g source code snapshot, providing SSL/TLS and general-purpose cryptography library with ciphers, digests, and X.509 certificate handling.

This little script encrypts password to gpp cpassword. It useful to create vulnerable lab AD (CVE-2014-1812).

Decrypts Huawei router and switch passwords using DES ECB mode, exploiting CVE-2012-4960 weak encryption. Python script for password recovery from…

Base64-based encryption oracle exploit for CVE-2017-9248 (Telerik UI for ASP.NET AJAX dialog handler)

CVE-2010-3332 Oracle Padding Vulnerability in Microsoft ASP.NET

Скрипт для расшифровки пароля пользователя в СЭД Detrix

Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.

Centralized configuration server for distributed systems with HTTP API, Git-backed storage, property encryption/decryption, and integration with…

Fix for ECDSA and EDDSA signature verification in Wycheproof project, addressing missing length checks that allowed zero-byte manipulation during…

OpenSSL toolkit providing TLS/SSL protocols and general-purpose cryptographic library with command-line tools for key generation, certificate…

OpenSSL toolkit providing TLS/SSL protocols and general-purpose cryptographic library with command-line tools for key generation, certificate…

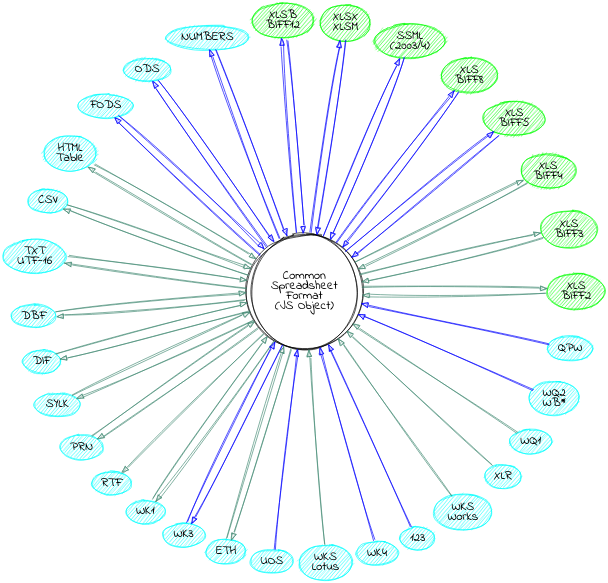
SheetJS xlsx 0.18.5 fork with CVE-2023-30533 and CVE-2024-22363 fixes

Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.

Exploit for CVE-2024-43044 enabling arbitrary file read from Jenkins controller to extract and decrypt credentials.xml using secret keys.

Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…