

CVE-2019-5420
 j4k0m/cve-2019-5420
A vulnerability can allow an attacker to guess the automatically generated development mode secret token.
encryption-decryption-toolspassword-attackspenetration-testing+2
5
j4k0m/cve-2019-5420A vulnerability can allow an attacker to guess the automatically generated development mode secret token.
 kl4v3/axiom-protocol
The goal of Axiom is to provide a completely anonymous, decentralized, and censorship-resistant social media platform. To make this possible, the…
 shoucheng3/apache__rocketmq_cve-2019-17572_4-6-0
Exploit for Apache RocketMQ CVE-2019-17572 targeting distributed messaging platforms with authentication and encryption features.
 pandora-research/cve-2018-0114-exploit
Exploit for CVE-2018-0114: re-signs JWT tokens by embedding an attacker-controlled public key in the JWS header, bypassing authentication in…
 shoucheng3/apache__rocketmq_cve-2023-37582_4-9-6
Exploit for CVE-2023-37582 targeting Apache RocketMQ, a distributed messaging platform with low latency, high throughput, and support for…
 pazhanivel07/openssl_1_0_1g_cve-2015-1788
General-purpose cryptography library implementing SSL/TLS protocols, symmetric/ asymmetric ciphers, message digests, and X.509 certificate handling…
 trinadh465/openssl-1_0_1g_cve-2015-1791
OpenSSL 1.0.1g source code with CVE-2015-1791 patch, providing SSL/TLS and cryptographic library for secure communications.
 satheesh575555/openssl_1_1_1_g
Robust toolkit implementing TLS/SSL protocols and a full-strength cryptographic library for encryption, decryption, certificate creation, and secure…
 vmware-archive/lightwave
Identity services for traditional infrastructure, applications and containers.
 dbeaver/dbeaver
Free universal database tool and SQL client
 scille/parsec-cloud
Open source Dropbox-like file sharing with full client encryption !
 ak3zaidan/trust-decision-security
Reverse Engineer of Trust Decision Chinese Security
 projectdiscovery/ldapserver
Package ldapserver implements LDAP Server
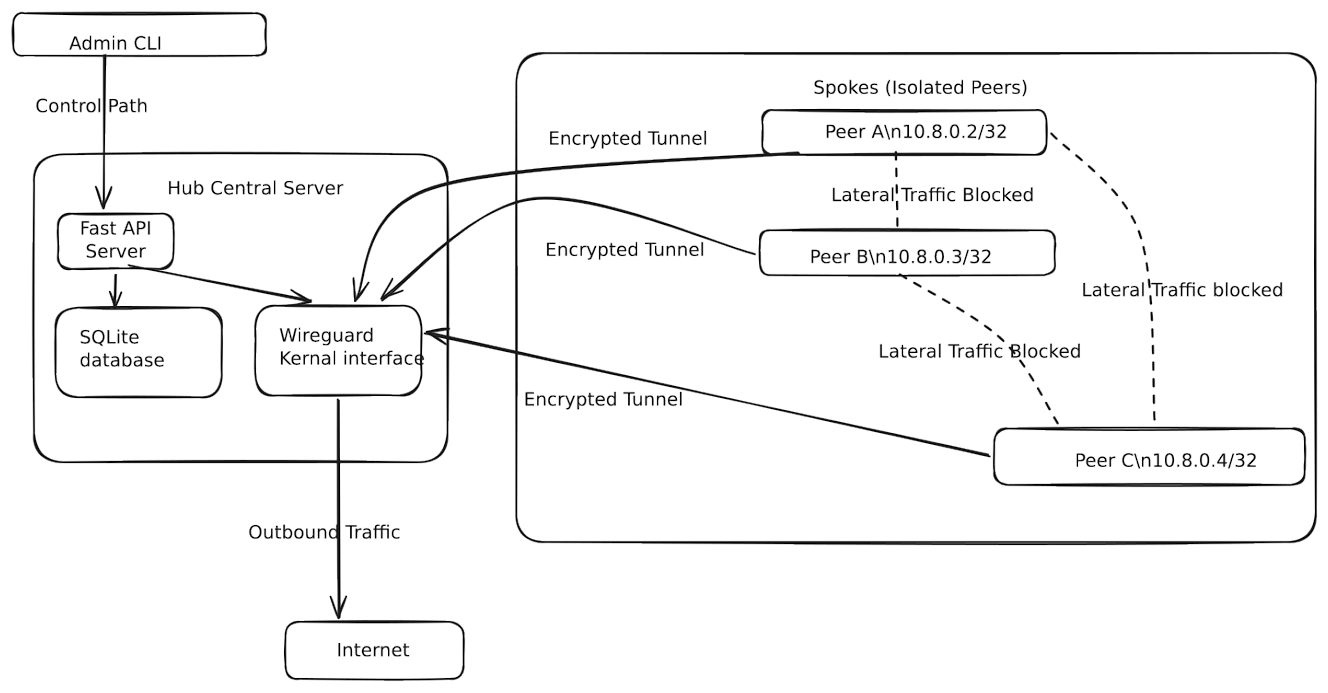 alvin-alvo/safenet-soho-security-framework
A lightweight, policy-driven framework that brings Zero-Trust micro-segmentation to SOHO networks using WireGuard.
 freerdp/freerdp
FreeRDP is a free remote desktop protocol library and clients
 strongswan/strongswan
strongSwan - IPsec-based VPN
 agwa/git-crypt
Transparent file encryption in git
 mwiede/jsch
fork of the popular jsch library