

aes-finder
 mmozeiko/aes-finder
Utility to find AES keys in running processes
binary-analysiscryptographyencryption-decryption-tools+2
1.1k
mmozeiko/aes-finderUtility to find AES keys in running processes
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
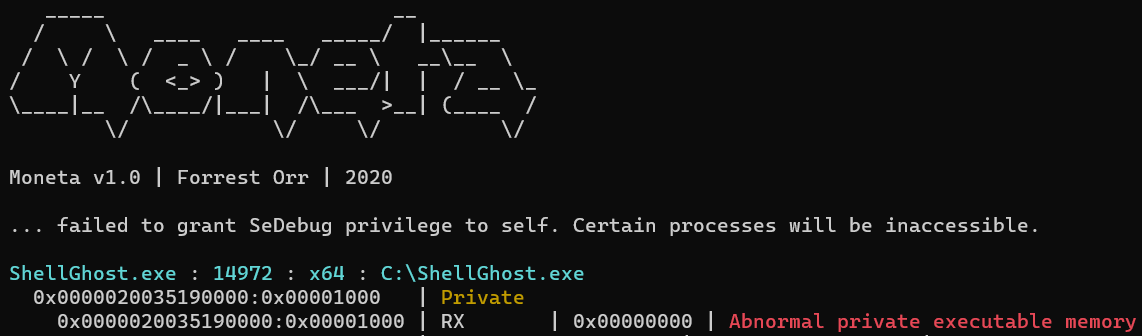 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
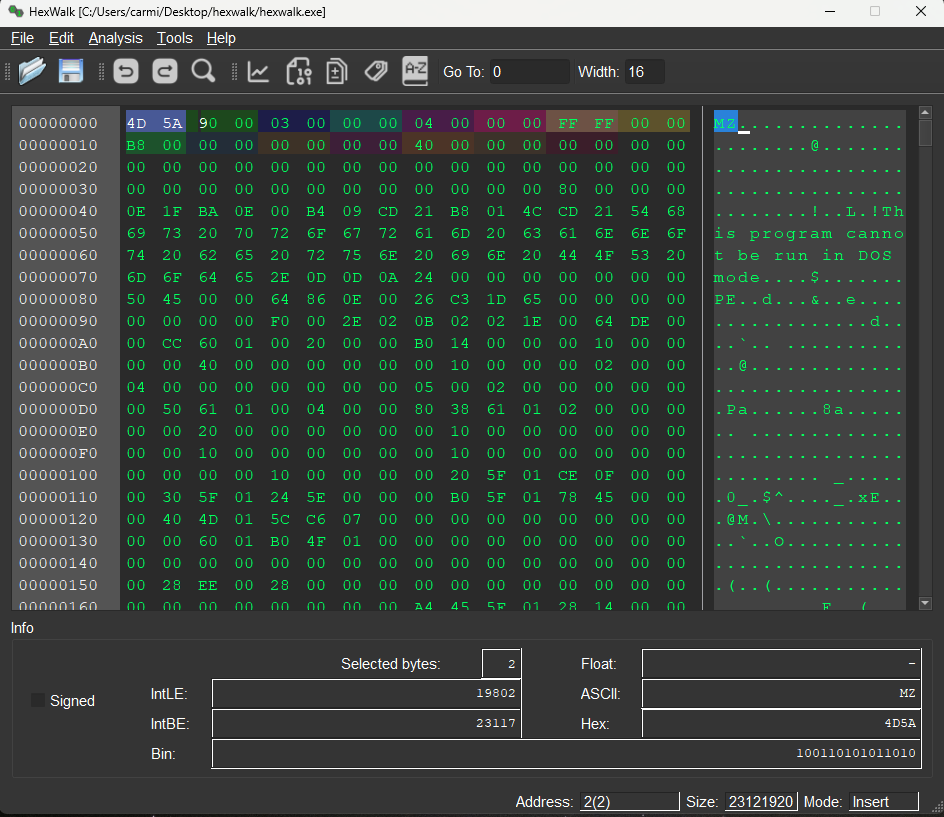 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
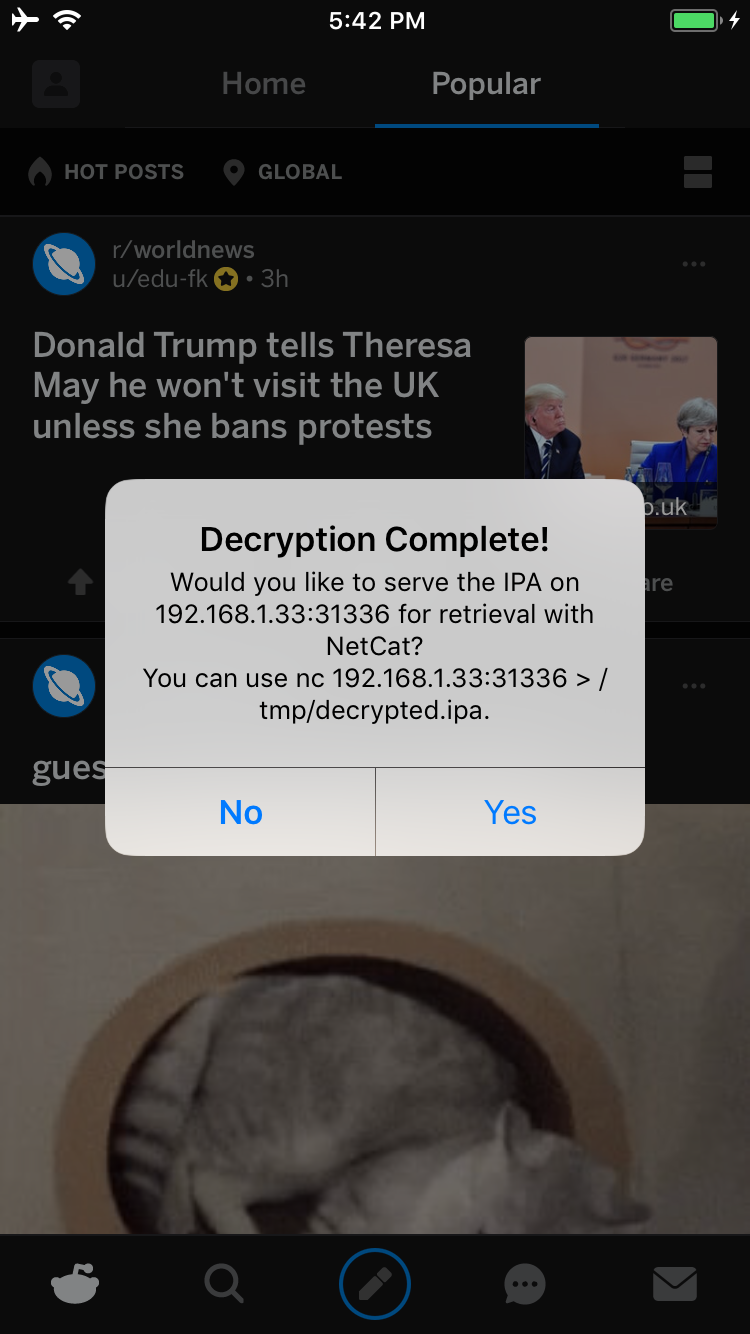 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 hfiref0x/wdextract
Extract Windows Defender database from vdm files and unpack it
 marcog3/whatsdump
Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)
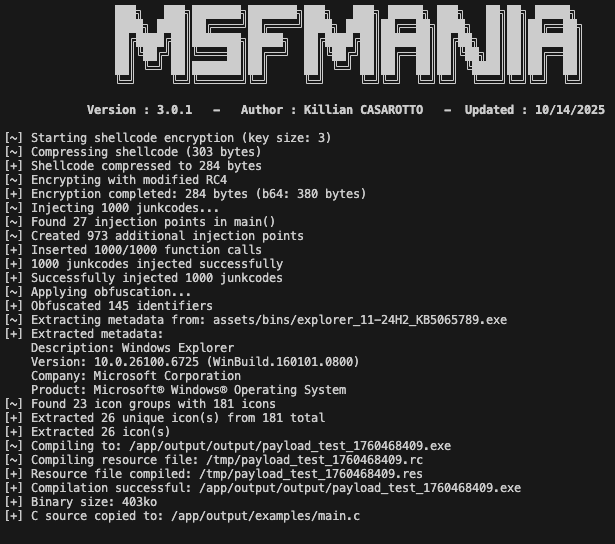 lepotekil/msfmania
Python AV Evasion Tools
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 hackerschoice/bincrypter
Pack/Encrypt/Obfuscate ELF + SHELL scripts
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 jb-selfcompany/tyr
True P2P Email on top of Yggdrasil Network for Android
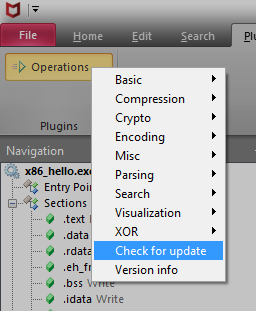 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
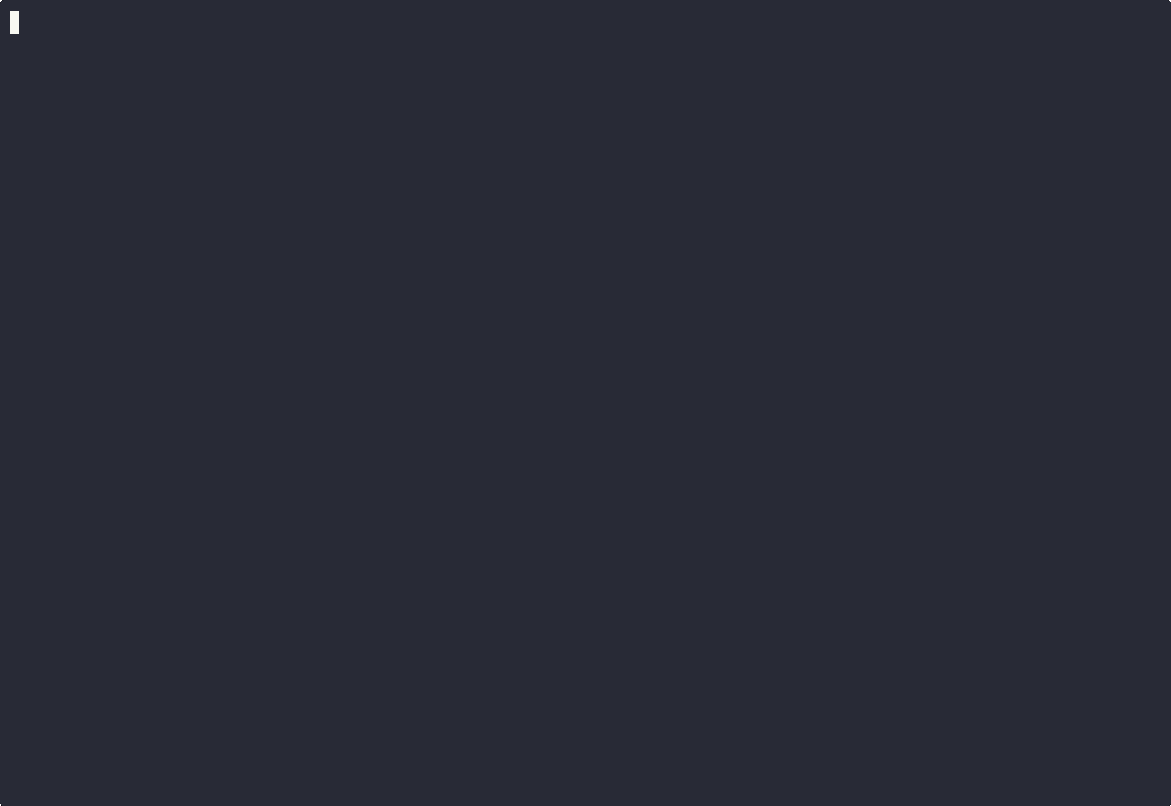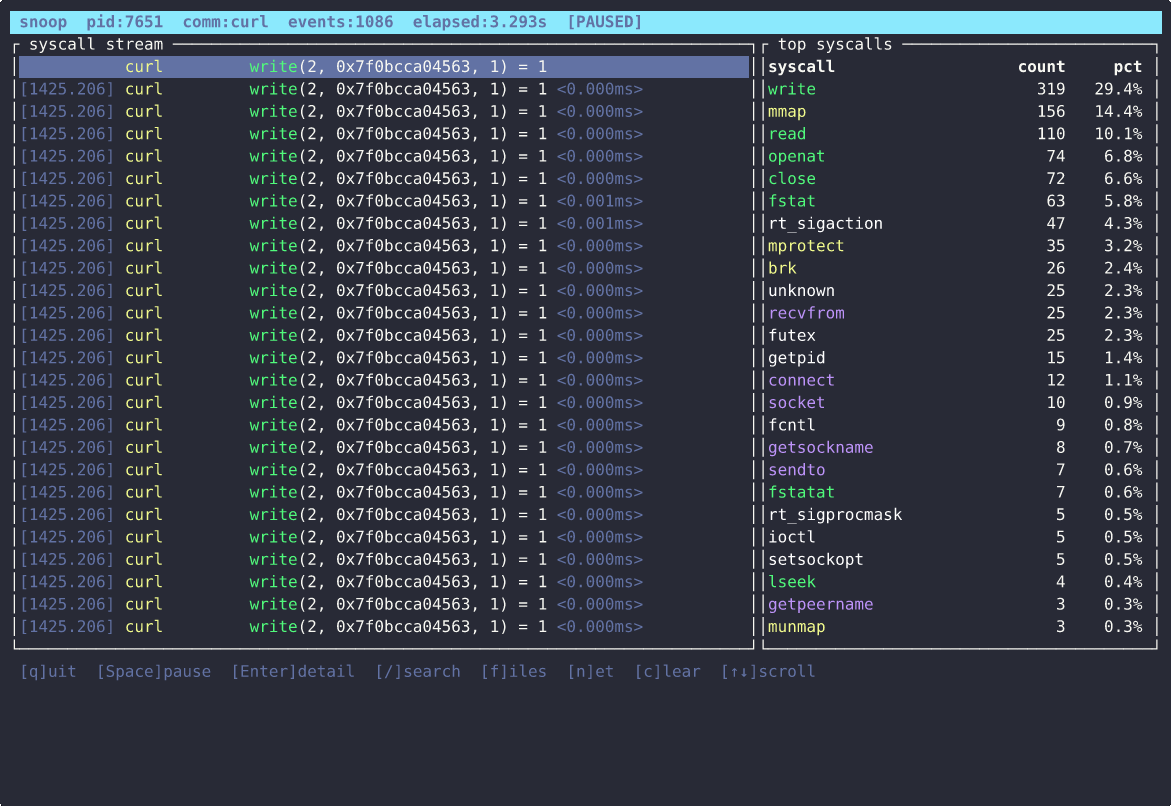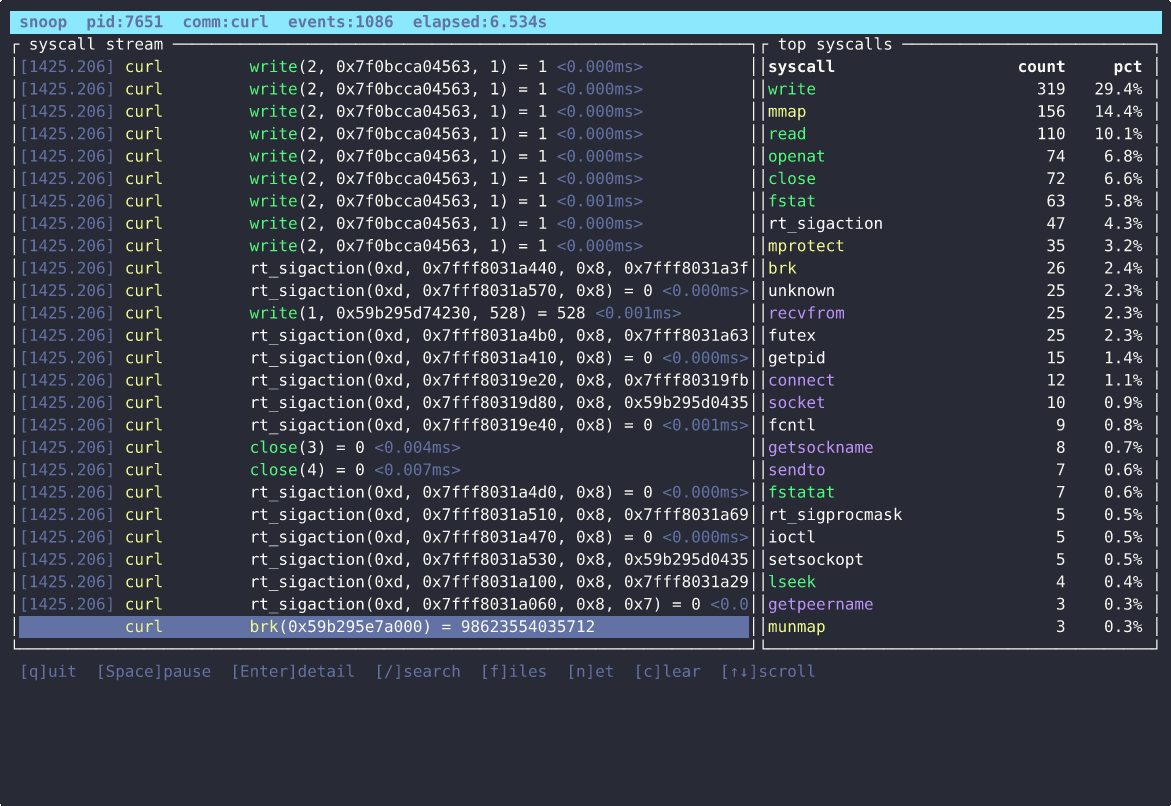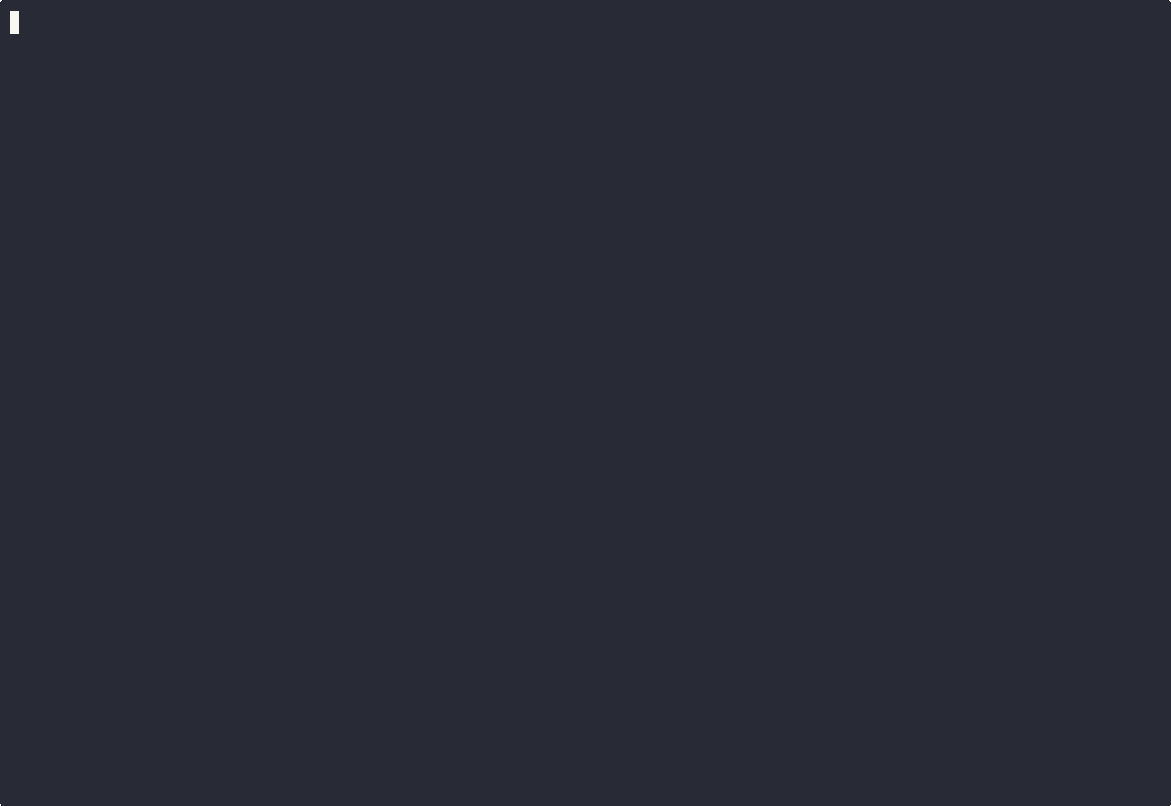 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
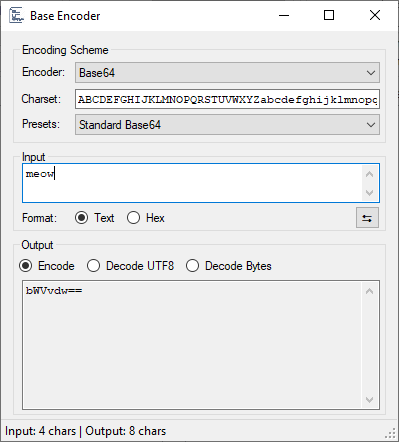 demonslay335/cryptotester
A utility for playing with cryptography, geared towards ransomware analysis.