

Decoder-Improved
 nccgroup/decoder-improved
Improved decoder for Burp Suite
cryptographyencryption-decryption-toolsweb-proxies-interception
nccgroup/decoder-improvedImproved decoder for Burp Suite
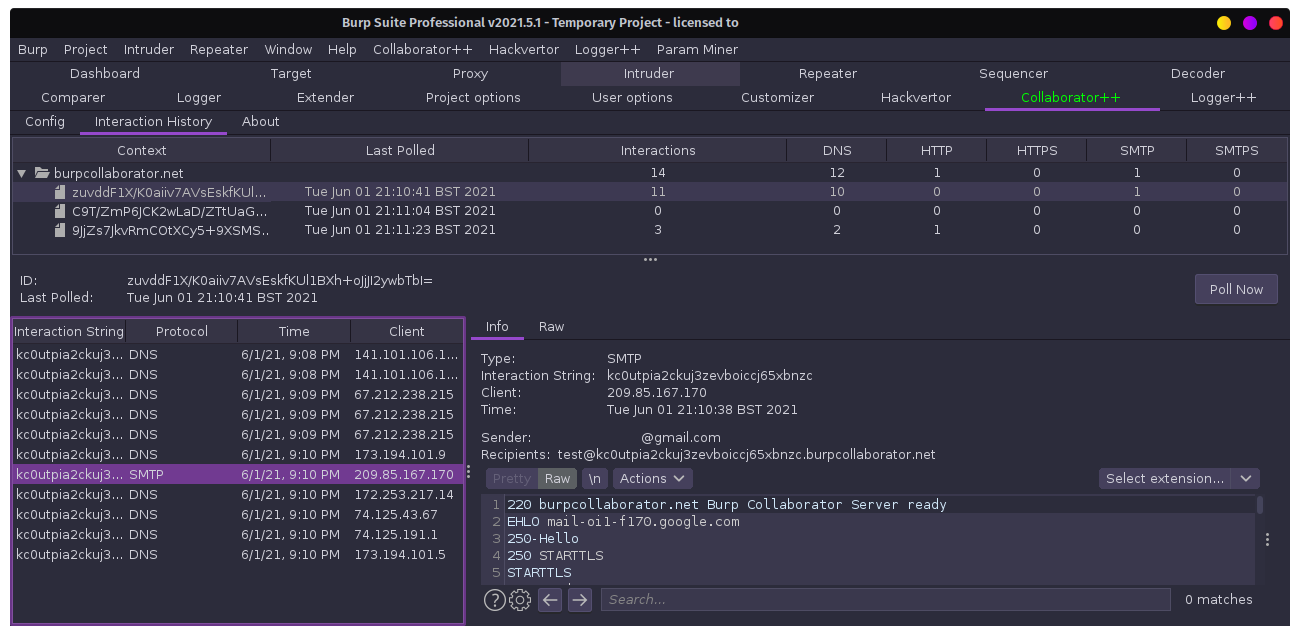 nccgroup/collaboratorplusplus
Burp Suite extension enhancing Collaborator with context capture, polling history, and optional AES-encrypted authentication for private server…
 kac89/vulnrepo
VULNRΞPO - Free vulnerability report generator and repository, end-to-end encrypted! Templates of issues, CWE,CVE,MITRE ATT&CK,PCI DSS, import…
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 kishanbagaria/padding-oracle-attacker
🔓 CLI tool and library to execute padding oracle attacks easily, with support for concurrent network requests and an elegant UI.
 bao7uo/rau_crypto
Telerik UI for ASP.NET AJAX File upload and .NET deserialisation exploit (CVE-2017-11317, CVE-2017-11357, CVE-2019-18935)
 bao7uo/dp_crypto
Base64-based encryption oracle exploit for CVE-2017-9248 (Telerik UI for ASP.NET AJAX dialog handler)
 jas502n/cve-2019-2618
Exploit script for CVE-2019-2618, a Weblogic arbitrary file upload vulnerability, with JSP webshell deployment and encrypted credential decryption.
 a-d-team/grafanaexp
A exploit tool for Grafana Unauthorized arbitrary file reading vulnerability (CVE-2021-43798), it can burst plugins / extract secret_key / decrypt…
 taherio/redi
Automated script for setting up CobaltStrike redirectors (nginx reverse proxy, letsencrypt)
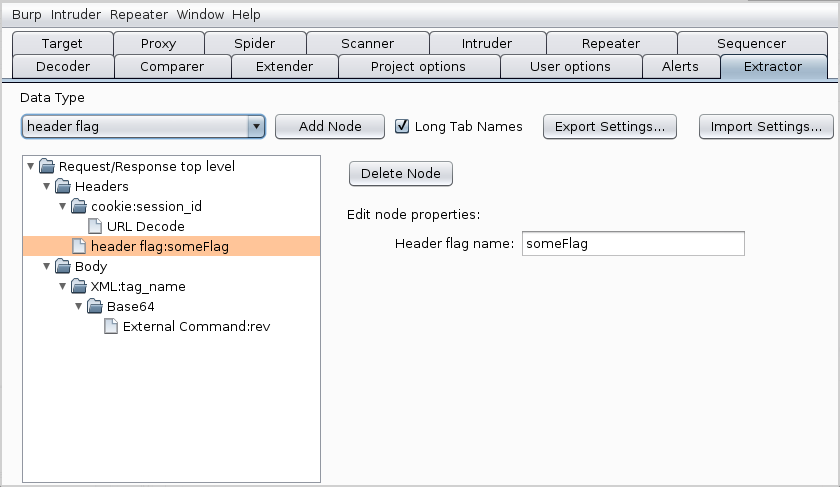 nccgroup/extractor
Extension adds a new tab in Burp Suite called Extractor
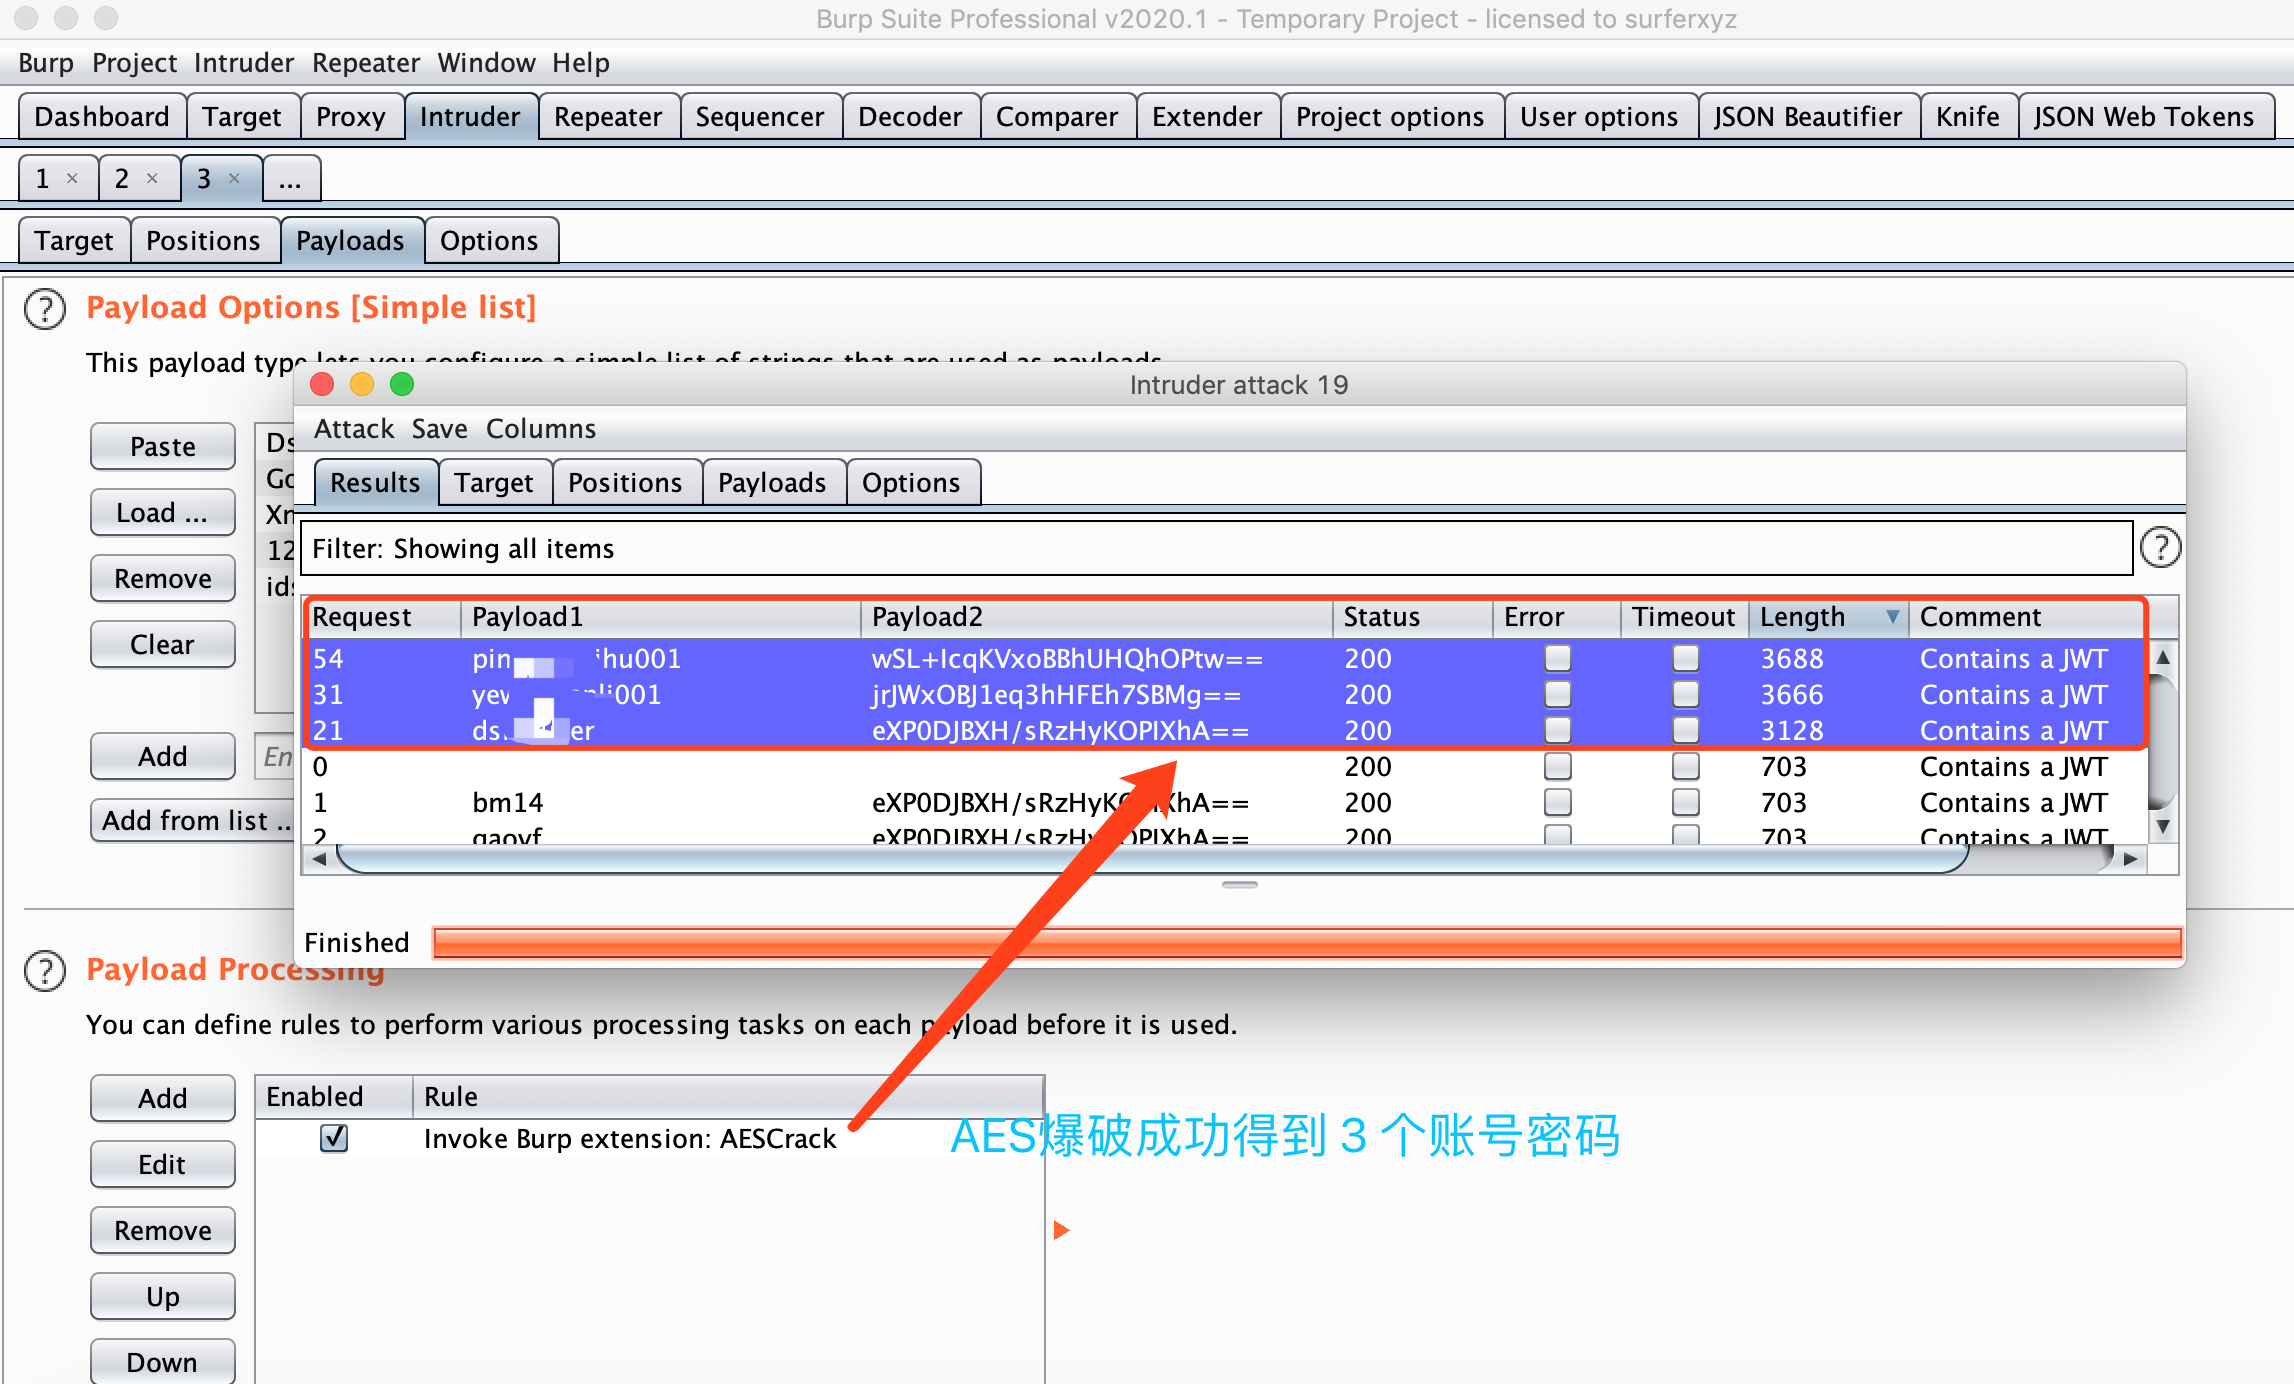 jas502n/burp_aes_plugin
Burpsuite Plugin For AES Crack
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 synacktiv/laravel_cookie_killer
Decrypt and re-encrypt Laravel session cookies to exploit insecure PHP deserialization for remote code execution.
 eremiel/cve-2018-0114
python2.7 script for JWT generation
 thanhuutuan/cve_2019_18935
This project for CVE-2019-18935
 anmolksachan/cve-2020-2733
Exploit for CVE-2020-2733 in JD Edwards EnterpriseOne Tools, demonstrating unauthenticated admin password decryption and authentication bypass to…
 pandora-research/cve-2018-0114-exploit
Exploit for CVE-2018-0114: re-signs JWT tokens by embedding an attacker-controlled public key in the JWS header, bypassing authentication in…