

ecapture
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
android-securitydatabase-securitydynamic-analysis-sandboxing+3
15.4k
gojue/ecaptureCapture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
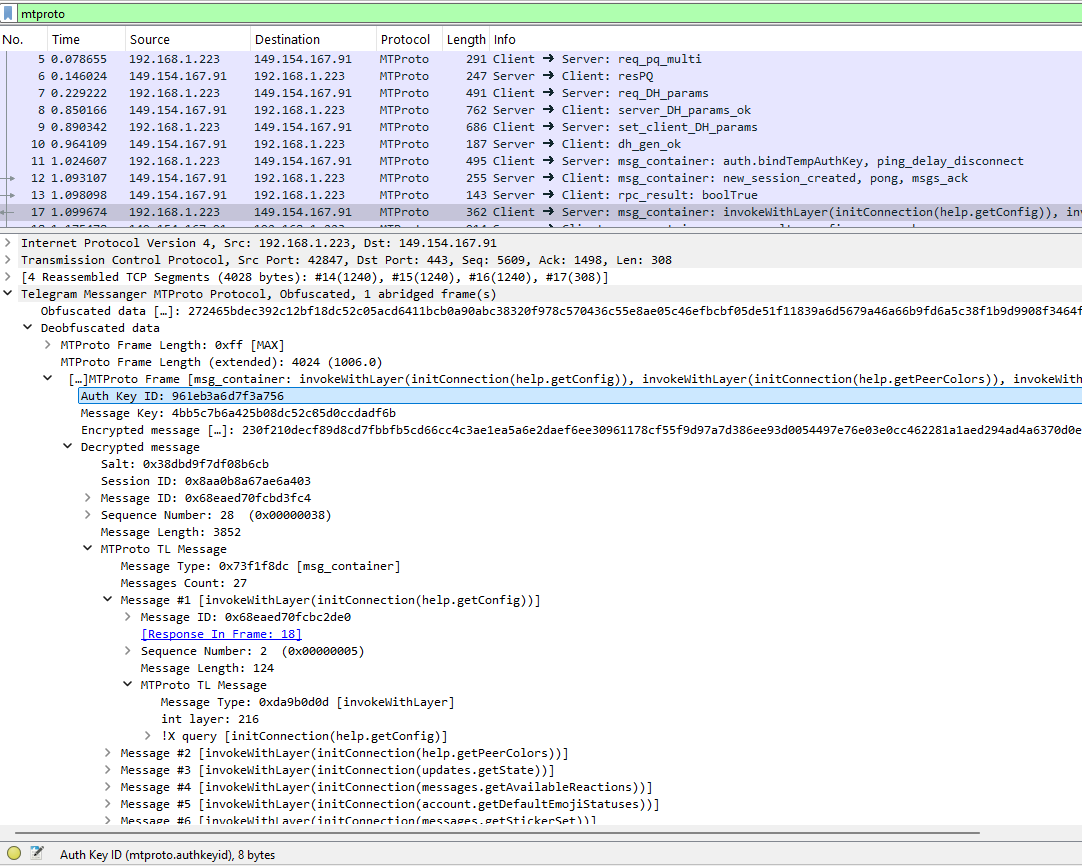 tomer8007/mtproto-dissector
Wireshark plugin for dissecting the Telegram protocol
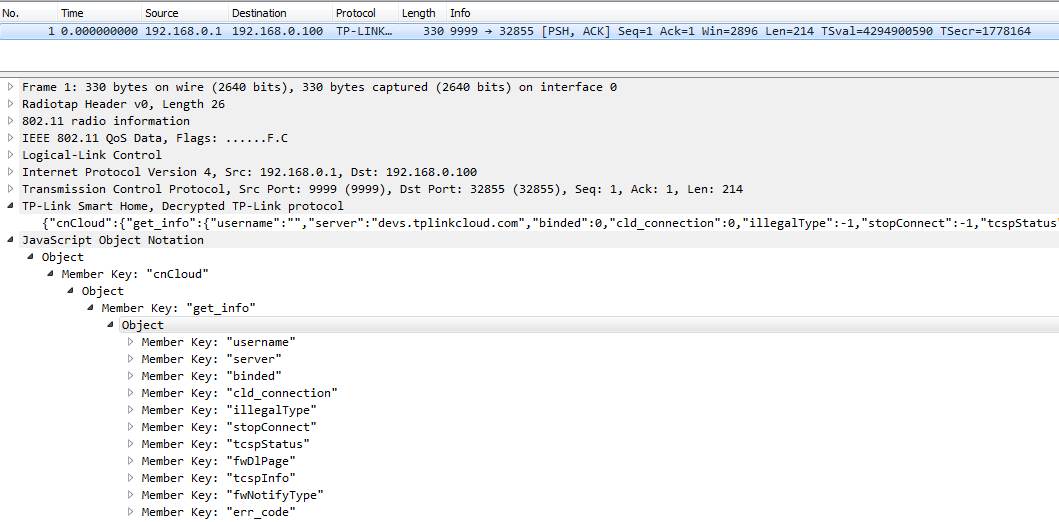 softscheck/tplink-smartplug
TP-Link WiFi SmartPlug Client and Wireshark Dissector