
frida-ios-dump
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
encryption-decryption-toolsios-securitymobile-app-pentesting+4
3.9k
alonemonkey/frida-ios-dumpExtracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…

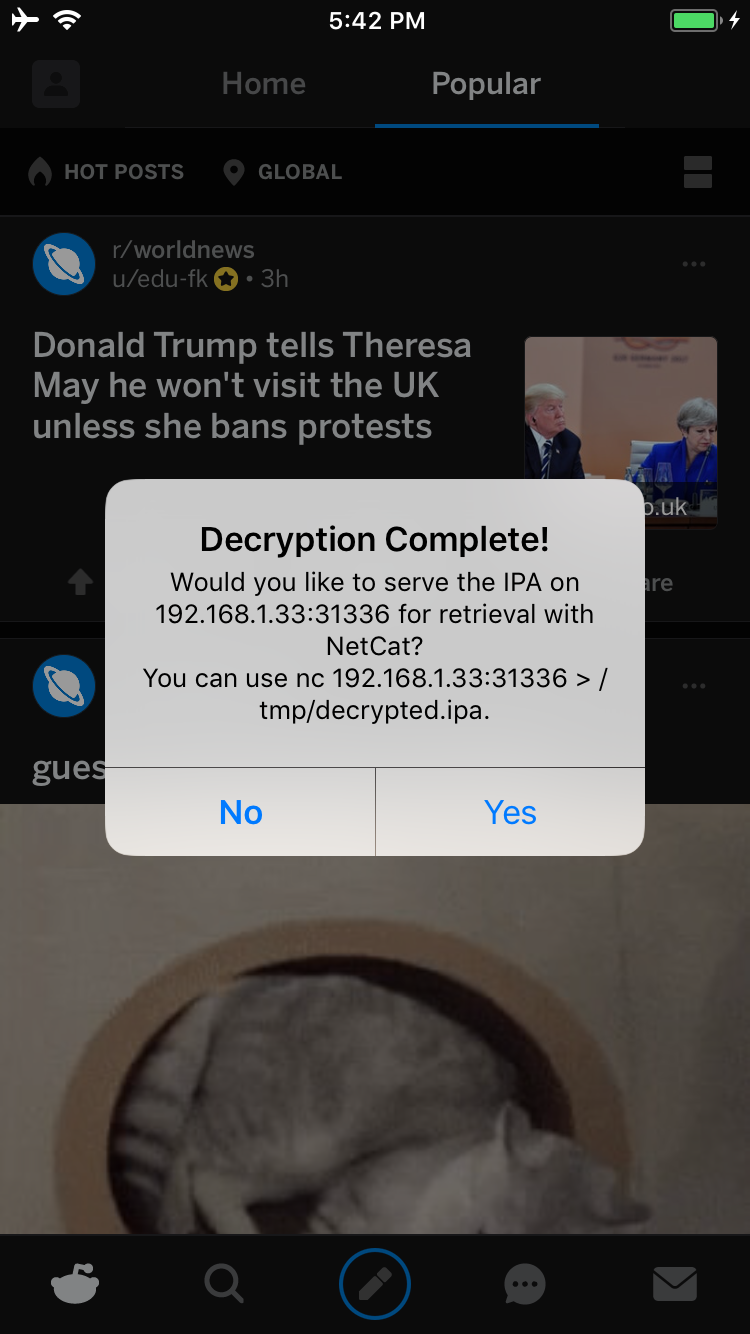 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
 jan0/isslfix
CVE-2011-0228 fix for older idevices/firmwares
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…