

whapa
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
android-securitydata-recoverydigital-forensics+5
1.5k
b16f00t/whapaGraphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 ghcohu/decrypt-passwords-for-huawei-routers-and-switches-cve-2012-4960
Decrypts Huawei router and switch passwords using DES ECB mode, exploiting CVE-2012-4960 weak encryption. Python script for password recovery from…
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 golioth/signy
Asymmetric cryptography library for generating signed URLs on embedded devices, enabling time-limited resource access using PSA Crypto API with…
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
 e-ago/bitcracker
BitCracker is the first open source password cracking tool for memory units encrypted with BitLocker
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
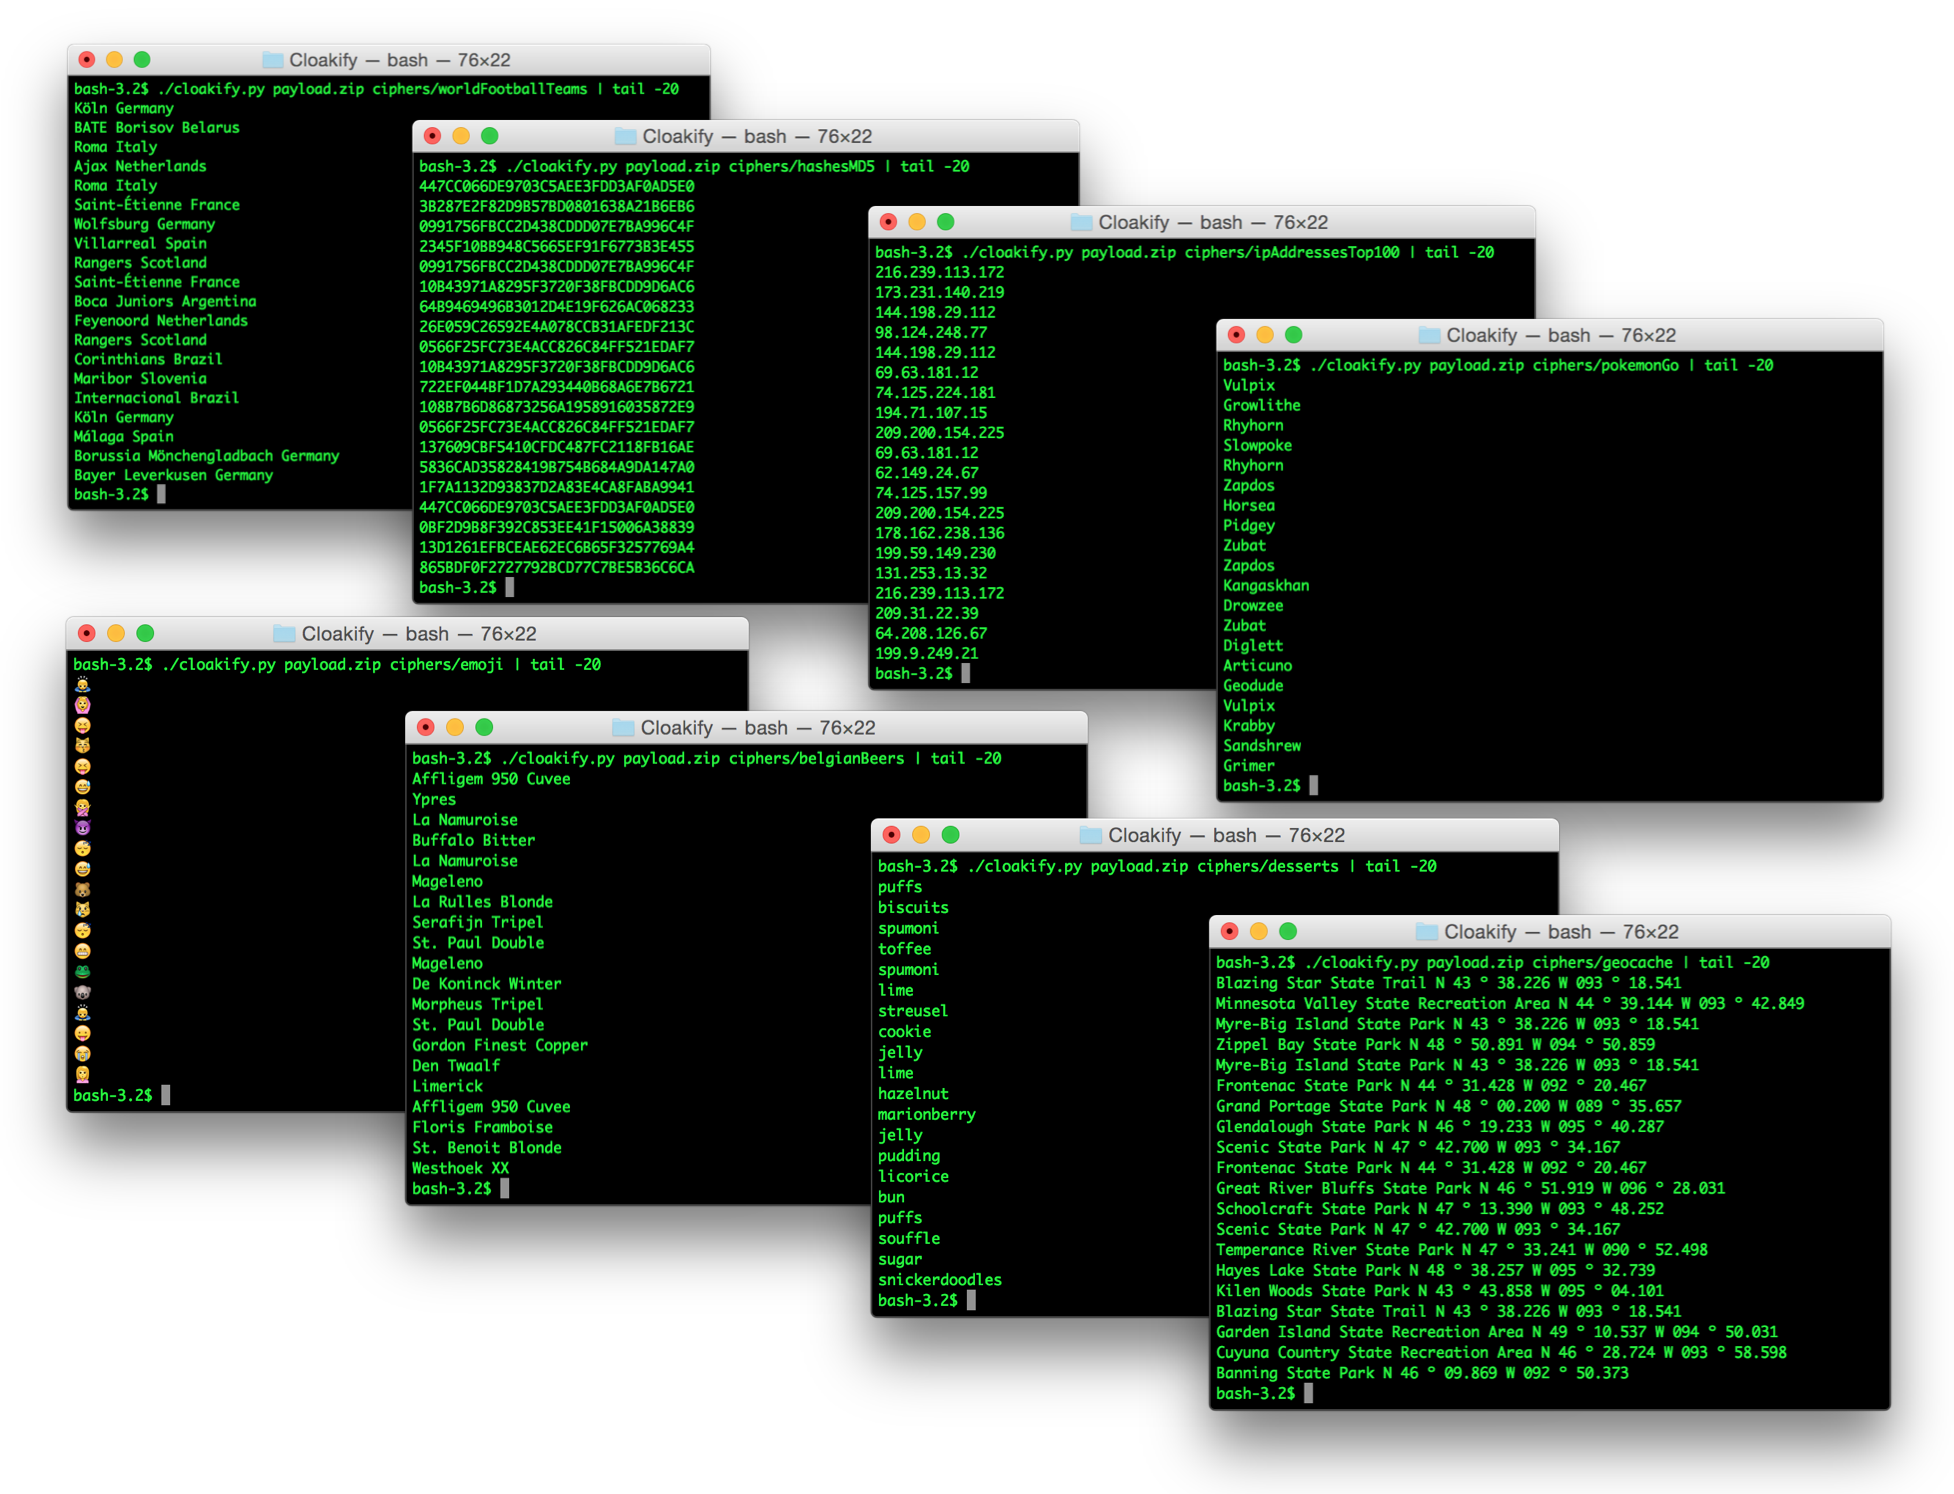 trycatchhcf/cloakify
CloakifyFactory - Data Exfiltration & Infiltration In Plain Sight; Convert any filetype into list of everyday strings, using Text-Based…
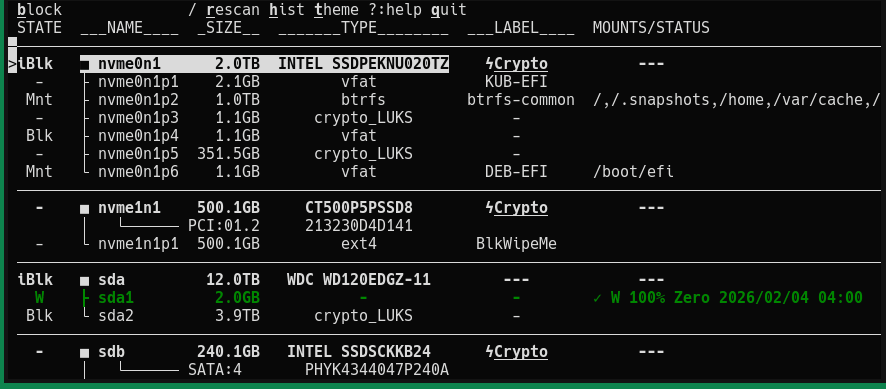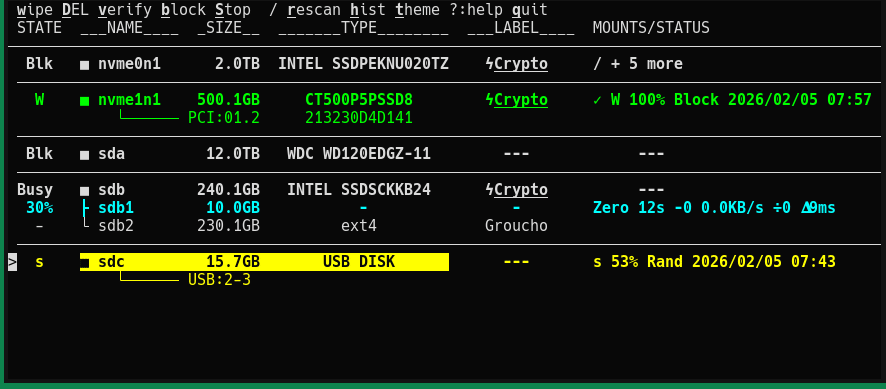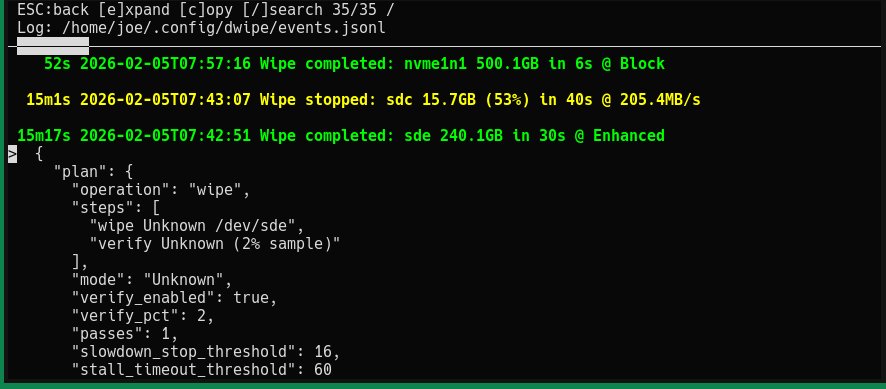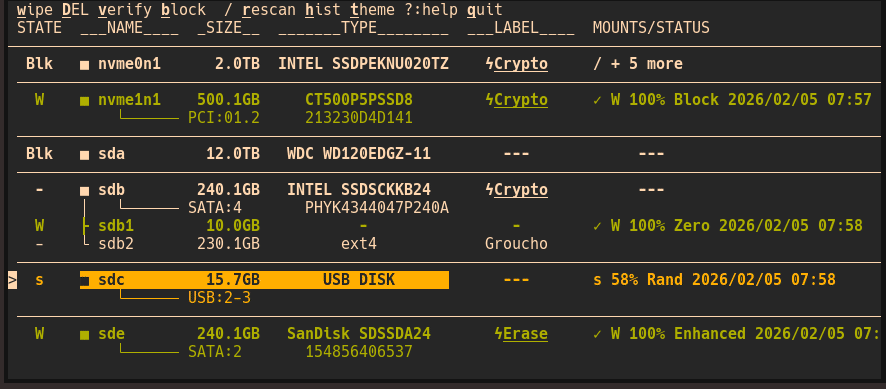 joedefen/dwipe
Tool to securely and efficiently wipe devices and partiitions for Linux
 blasty/sonos
Exploit and tooling for Amlogic-based Sonos devices: dumps OTP/eFUSE via an EL3 exploit, extracts LUKS decryption keys, and fetches/decrypts OTA…
 qcomms/cqptoolkit
Framework for controlling QKD devices and managing symmetric keys. See the [project page here](https://qcomms.gitlab.io/cqptoolkit/)
 akabe1/kr00ker
An experimental script PoC for Kr00k vulnerability (CVE-2019-15126)
 0xblackash/cve-2026-45585
CVE-2026-45585