
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
14 results
CVE-2024-48705 preview

CVE-2024-48705

GitHubl41kaa/cve-2024-48705

Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
binary-analysiscommand-and-controlembedded-systems-security+7
2
1 year ago
Starlink-FI preview

Starlink-FI

GitHubkuleuven-cosic/starlink-fi

Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
binary-analysisembedded-systems-securityexploitation+4
1.0k4 years ago
CVE-2021-4045 preview

CVE-2021-4045

GitHub234329a423853/cve-2021-4045

CVE-2021-4045 CVE-2021-4045 is a Command Injection vulnerability that allows Remote Code Execution in the TP-Link Tapo c200 IP camera. It affects all…
embedded-systems-securityexploitationfirmware-analysis+3
210 months ago
CVE-2022-20607 preview

CVE-2022-20607

GitHubsumeetit/cve-2022-20607

In the Pixel cellular firmware, there is a possible out of bounds write due to a missing bounds check. This could lead to remote code execution with…
android-securityembedded-systems-securityexploitation+3
3 years ago
R7000_httpd_BOF_CVE-2020-15416 preview

R7000_httpd_BOF_CVE-2020-15416

GitHubk3vinlusec/r7000_httpd_bof_cve-2020-15416

Walkthrough of CVE-2020-15416 buffer overflow exploit for Netgear R7000 router, including QEMU user-mode debugging environment setup and detailed…
binary-exploitationeducationembedded-systems-security+5
5 years ago
shining-mask preview

shining-mask

GitHubbishopfox/shining-mask

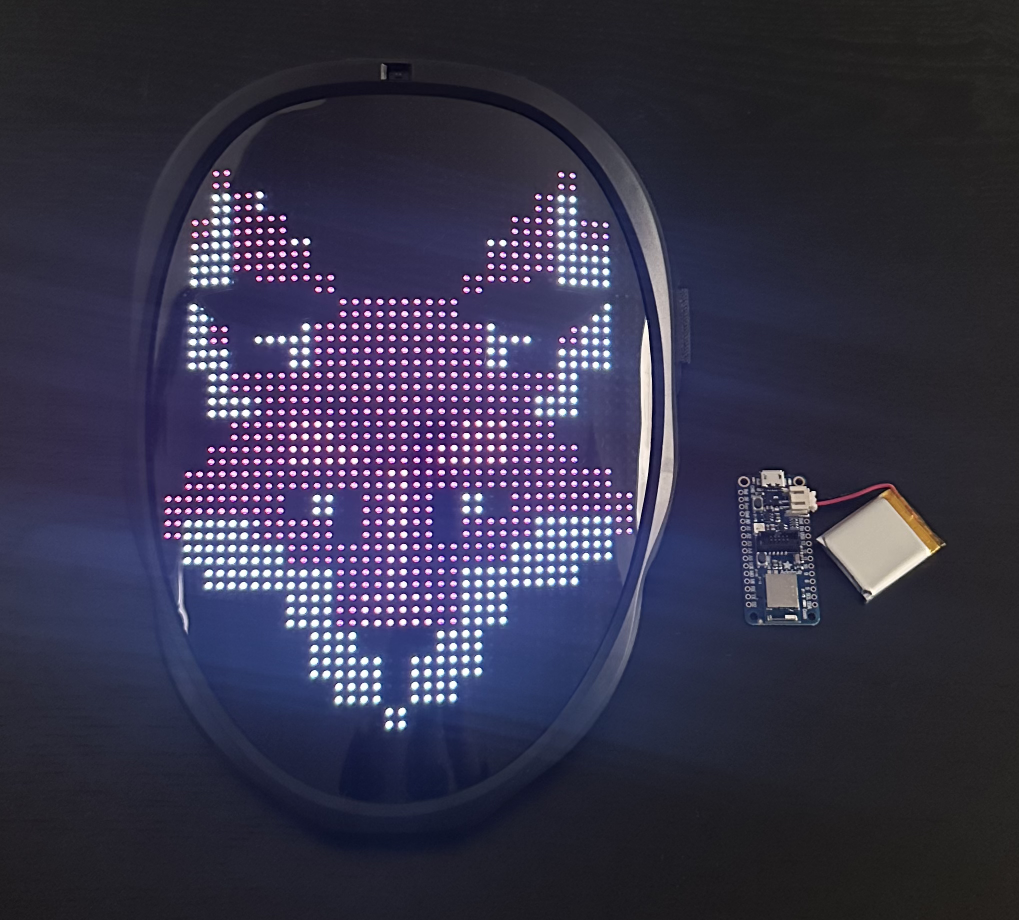
BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…
bluetooth-securityeducationembedded-systems-security+5
141 year ago
CVE-2018-18852 preview

CVE-2018-18852

GitHubandripwn/cve-2018-18852

CERIO RCE CVE-2018-18852, authenticated (vendor defaults) web-based RCE as root user.
embedded-systems-securityexploitationiot-security+4
17 years ago
CVE-2022-26269 preview

CVE-2022-26269

GitHubnsbogam/cve-2022-26269

Suzuki connect app is used to get the car information like Fuel, Ignition status, Current location, Seat buckle status etc. In Ignis, Zeta variant…
embedded-systems-securityexploitationfuzzing+2
24 years ago
CatSniffer-Firmware preview

CatSniffer-Firmware

GitHubelectroniccats/catsniffer-firmware

Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
bluetooth-securityembedded-systems-securityfirmware-analysis+5
461 month ago
CVE-2019-10999 preview

CVE-2019-10999

GitHubtacnetsol/cve-2019-10999

Full exploit for D-Link DCS-5020L, POC crash for others that are vulnerable as well.

binary-exploitationembedded-systems-securityexploitation+4
434 years ago
badbox-h713-projector preview

badbox-h713-projector

GitHubflorentineprinzessinzusachsen/badbox-h713-projector

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
android-securitydigital-forensicsembedded-systems-security+8
31 month ago
CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure preview

CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure

GitHubdylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…
embedded-systems-securityexploitationiot-security+3
32 years ago
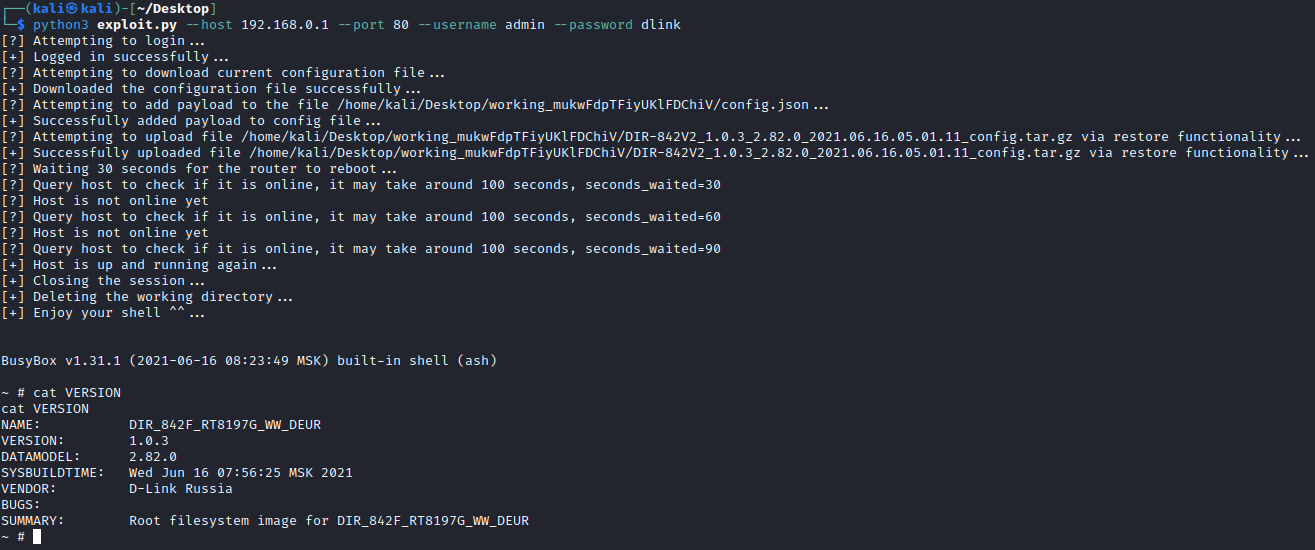
CVE-2023-33781 preview

CVE-2023-33781

GitHubs0tr/cve-2023-33781

Proof-of-concept exploit for CVE-2023-33781 enabling arbitrary binary execution on D-Link DIR-842V2 routers via telnet and backup/restore…
binary-exploitationembedded-systems-securityexploitation+3
17 months ago
CVE-2026-96515 preview

CVE-2026-96515

GitHubwhoami-012/cve-2026-96515

Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…

binary-analysisembedded-systems-securityexploitation+7
11 month ago