
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
18 results
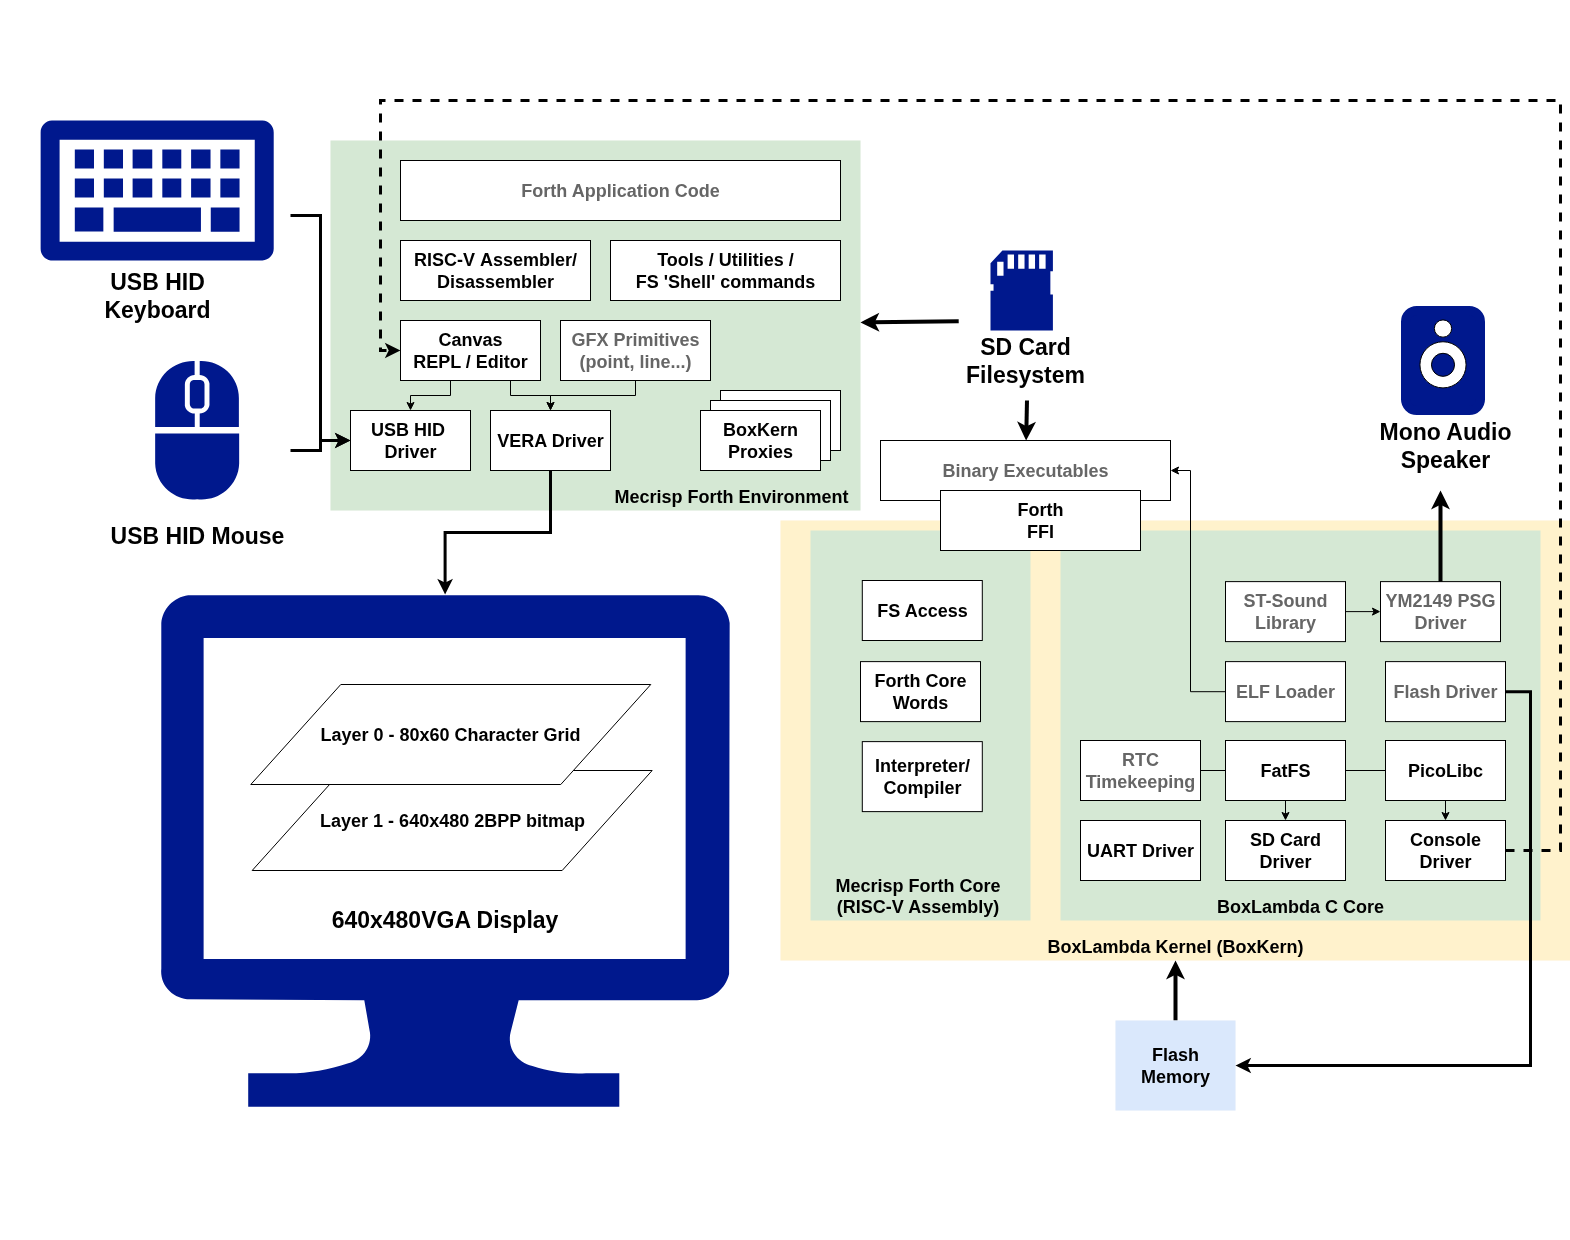
boxlambda preview

boxlambda

GitHubepsilon537/boxlambda

FPGA based microcomputer sandbox for software and RTL experimentation

debuggerseducationembedded-systems-security+5
862 days ago
firmadyne preview

firmadyne

GitHubfirmadyne/firmadyne

Platform for emulation and dynamic analysis of Linux-based firmware
dynamic-analysis-sandboxingembedded-systems-securityfirmware-analysis+2
2.1k2 years ago
rbpf preview

rbpf

GitHubqmonnet/rbpf

Rust virtual machine and JIT compiler for eBPF programs
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+4
1.1k4 months ago
USBvalve preview

USBvalve

GitHubcecio/usbvalve

Expose USB activity on the fly

dynamic-analysis-sandboxingembedded-systems-securityforensics+2
1.3k2 months ago
FirmAE preview

FirmAE

GitHubpr0v3rbs/firmae

Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis
dynamic-analysis-sandboxingembedded-systems-securityfirmware-analysis+3
9574 months ago
kAFL preview

kAFL

GitHubintellabs/kafl

A fuzzer for full VM kernel/driver targets
dynamic-analysis-sandboxingembedded-systems-securityfirmware-analysis+4
8179 months ago
ghidralligator preview

ghidralligator

GitHubairbus-cyber/ghidralligator

Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+3
3322 years ago
icicle preview

icicle

GitHubicicle-emu/icicle

Emulation-based fuzzer for MSP430 firmware that finds and analyzes memory-corruption bugs with detailed crash reports and reproducible inputs.
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+3
1942 years ago
go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset preview

go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset

GitHubhunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset

PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.
binary-exploitationdynamic-analysis-sandboxingembedded-systems-security+6
2 months ago
efi_fuzz preview
Archived

efi_fuzz

GitHubsentinel-one/efi_fuzz

Coverage-guided fuzzer for UEFI NVRAM variables using Qiling emulation and AFL++ to discover firmware vulnerabilities through automated input…

binary-analysisdynamic-analysis-sandboxingembedded-systems-security+3
1545 years ago
emba preview

emba

GitHube-m-b-a/emba

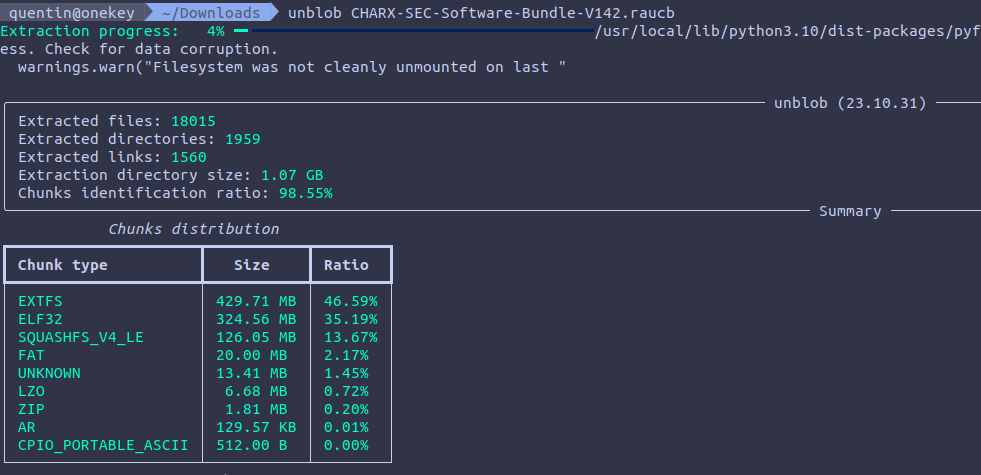
EMBA - The firmware security analyzer
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+8
3.7k1 day ago
firmware-workshop preview

firmware-workshop

GitHubonekey-sec/firmware-workshop

In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
binary-analysisdynamic-analysis-sandboxingeducation+5
673 months ago
FrisbeeLite preview

FrisbeeLite

GitHubnccgroup/frisbeelite

A GUI-based USB device fuzzer

dynamic-analysis-sandboxingembedded-systems-securityfuzzing+2
659 years ago
FACT_core preview

FACT_core

GitHubfkie-cad/fact_core

Firmware Analysis and Comparison Tool
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+9
1.5k10h 5m ago
rex preview

rex

GitHubrex-rs/rex

Rex is a safe and usable kernel extension framework that allows loading and executing Rust kernel extension programs in the place of eBPF.
dynamic-analysis-sandboxingembedded-systems-securitysecurity-virtualization
5622 months ago
umap2 preview

umap2

GitHubnccgroup/umap2

Umap2 is the second revision of NCC Group's python based USB host security assessment tool.

dynamic-analysis-sandboxingembedded-systems-securityfuzzing+4
2885 years ago
Philips-PM-5139-5138A-5136-Firmware-Project preview

Philips-PM-5139-5138A-5136-Firmware-Project

GitHubdoctormord/philips-pm-5139-5138a-5136-firmware-project

Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…

binary-analysisdynamic-analysis-sandboxingeducation+6
41 month ago
libloong preview

libloong

GitHublibriscv/libloong

The fastest LoongArch sandbox

binary-analysisembedded-systems-securityfuzzing+3
6529 days ago