
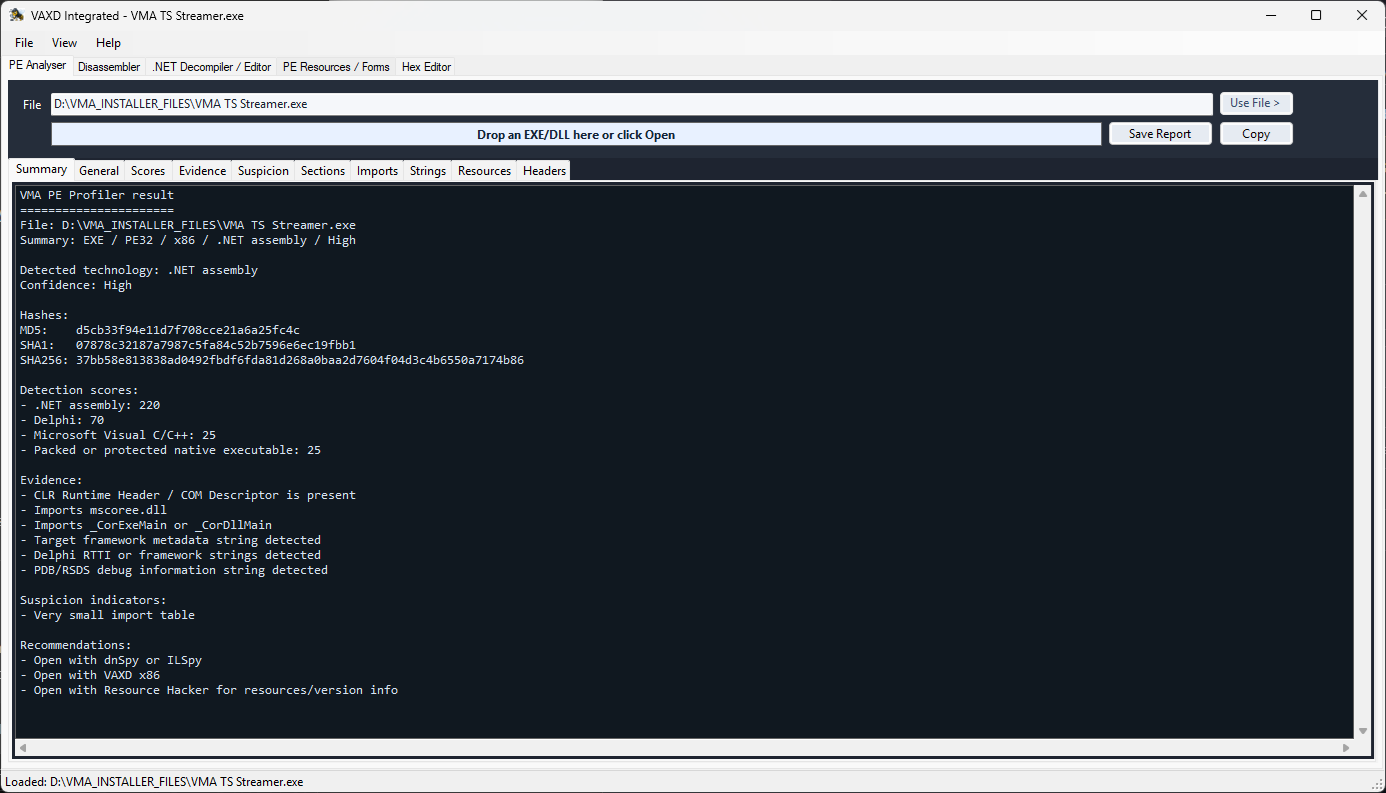
VAXD
 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
binary-analysisdebuggersdigital-forensics+7
bicurico/vaxdLightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 nccgroup/iodide
The Cisco IOS Debugger and Integrated Disassembler Environment
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
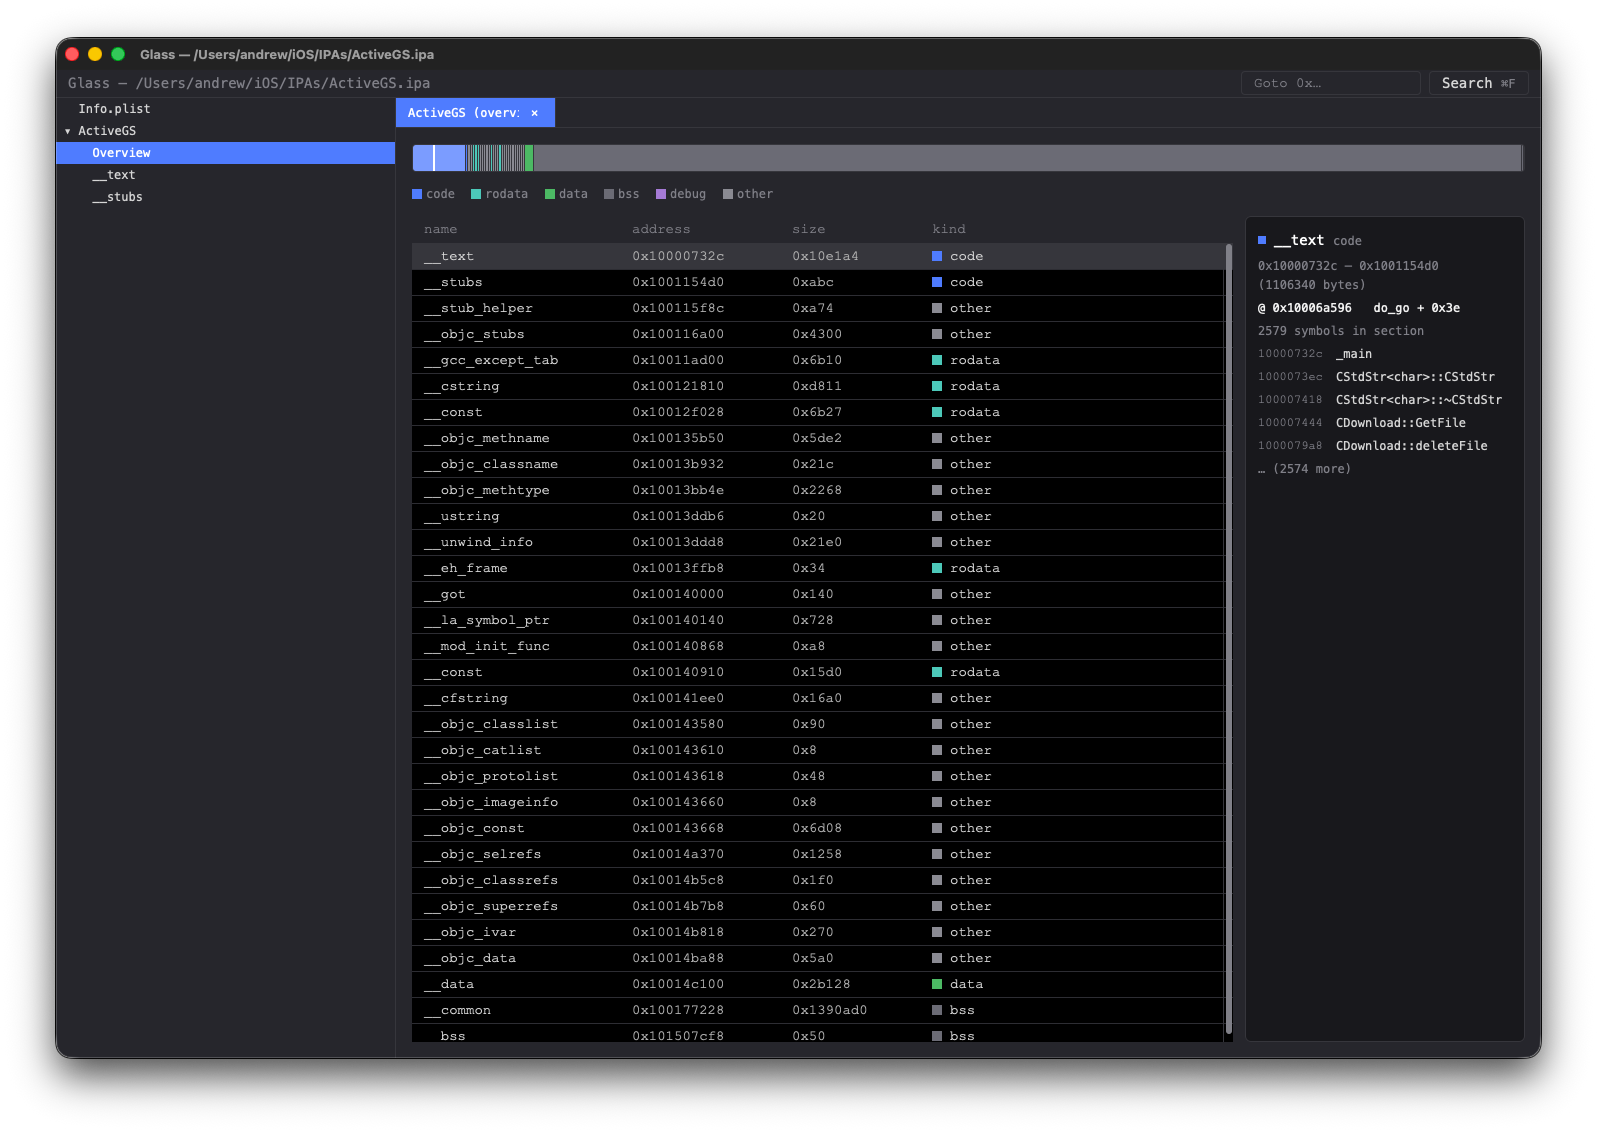 azw413/glass
Glass - a fast and free IDA Pro alternative