Tenda-F3-V4
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
embedded-systems-securityexploitationfirmware-analysis+4
3
4d000/tenda-f3-v4Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
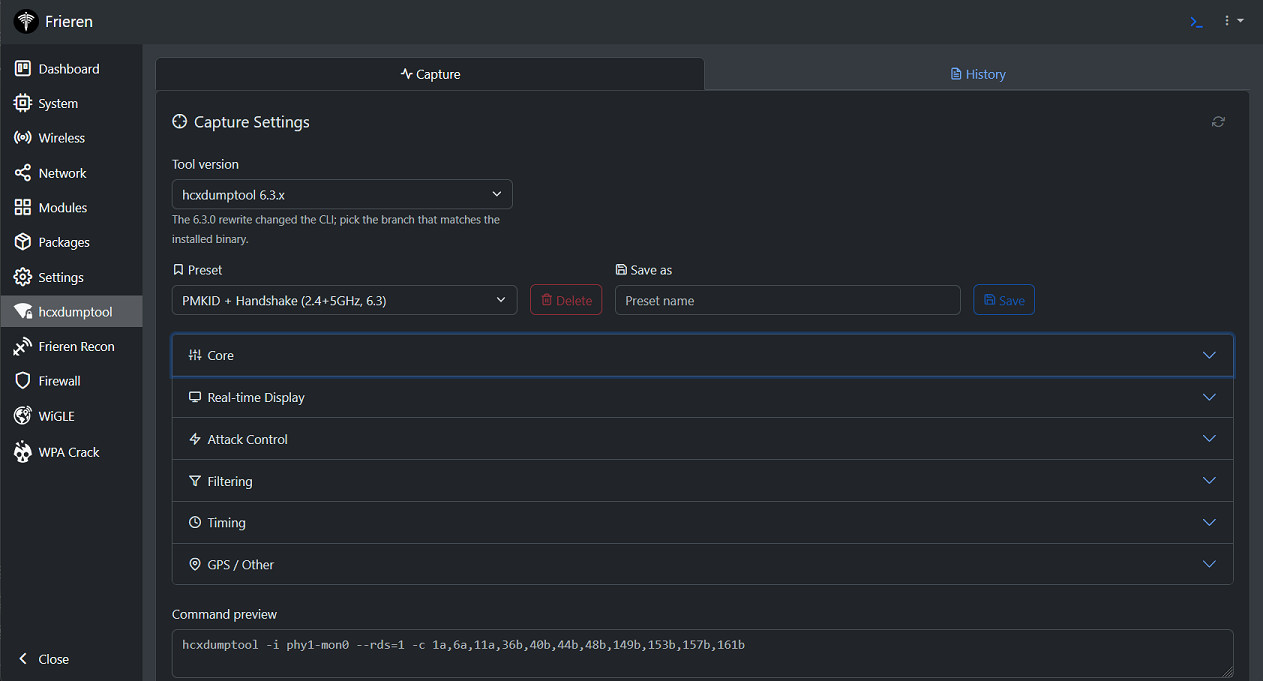 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 al3xtjames/ghidra-firmware-utils
Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…
 lixmk/concierge
Concierge Toolkit: Physical Access Control Identification and Exploitation
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 qcomms/cqptoolkit
Framework for controlling QKD devices and managing symmetric keys. See the [project page here](https://qcomms.gitlab.io/cqptoolkit/)
 jimilinuxguy/customer-assistance-buttons-sdr
This repository houses the work that ive put into reversing the various encoders and protocols used for customer service buttons in retail shops such…
 mutur4/unisocbootroms
This is a collection of Unisoc BootROMs dumped from various Unisoc chipsets via CVE-2022-38694
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 sigrokproject/libsigrok
C library providing a portable API for acquiring signals from logic analyzers, oscilloscopes, multimeters, and other test instruments, with…