samsung-exynos-sms-stack-overflow-cve-2025-54328-critical-zero-click-baseband-rce

Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…

Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…

Proof-of-concept exploit for CVE-2025-2620, a critical stack-based buffer overflow in D-Link DAP-1620 routers enabling unauthenticated remote code…

Proof-of-concept exploit for CVE-2025-45467, demonstrating remote code execution on Unitree Go1 robotic dogs via insecure MD5-based firmware…

Technical advisory and proof-of-concept for a stack-based buffer overflow (CWE-121) in the NXP moal.ko Wi-Fi kernel driver, enabling local kernel…

Technical analysis of CVE-2025-0690: integer overflow in GRUB2's read command leading to heap out-of-bounds write, arbitrary code execution, and…

Proof-of-concept exploit for CVE-2025-29384, a critical stack-based buffer overflow in Tenda AC9 routers. Includes Python and Metasploit modules for…

CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)

This repository is for Dorset_SmartLock_vulnerability. CVE-2025-25650 is suggested by MITRE which is yet to confirm.

CVE-2025-21479 proof-of-concept, I think

This is POC for IOS 0click CVE-2025-43300

Proof-of-concept for CVE-2025-48593

CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…

From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.

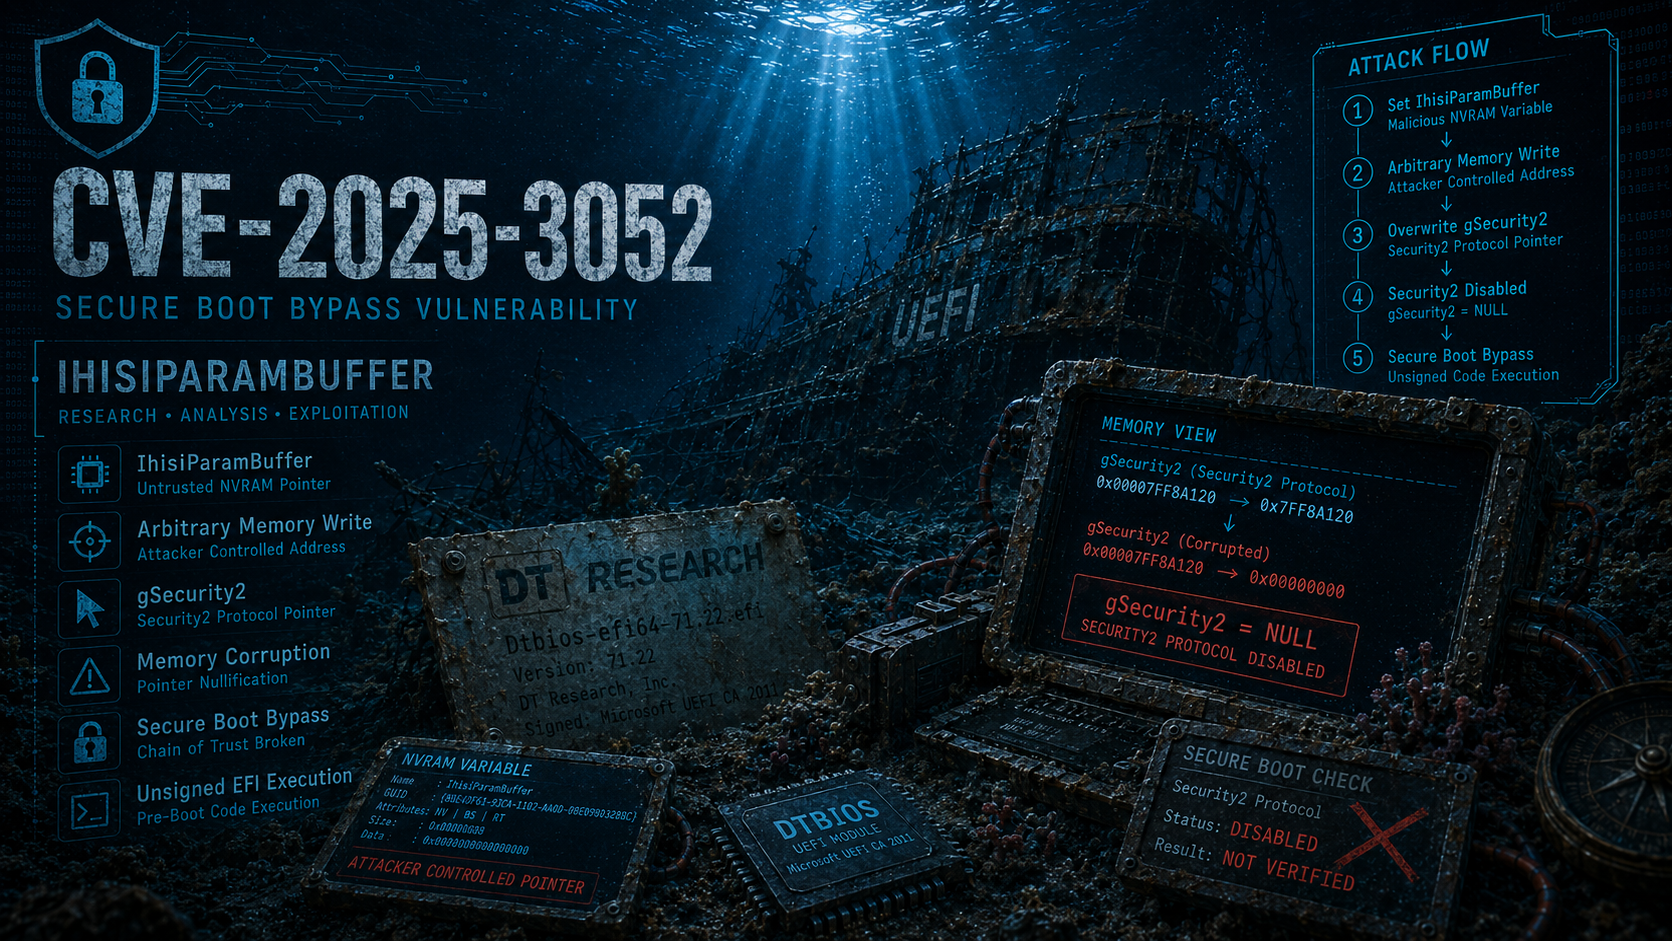
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.

Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages

Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…

POC for CVE-2025-29384

No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)