

ghidra-nanomips
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
binary-analysisembedded-systems-securityreverse-engineering+1
5611 months ago
nccgroup/ghidra-nanomipsnanoMIPS module for Ghidra
 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.
 olafdaf/cve-2022-40363
A buffer overflow in the component nfc_device_load_mifare_ul_data of Flipper Devices Inc., Flipper Zero before v0.65.2 allows attackers to cause a…
 coremaze/me2-writeup
Reconstructing a Dead USB Protocol: A Handheld's Secrets Unlocked by a Hot Knife, a multi-disciplinary journey to reviving a forgotten USB interface
 adamhrv/skylift
Wi-Fi Geolocation Spoofing with ESP8266 / ESP32
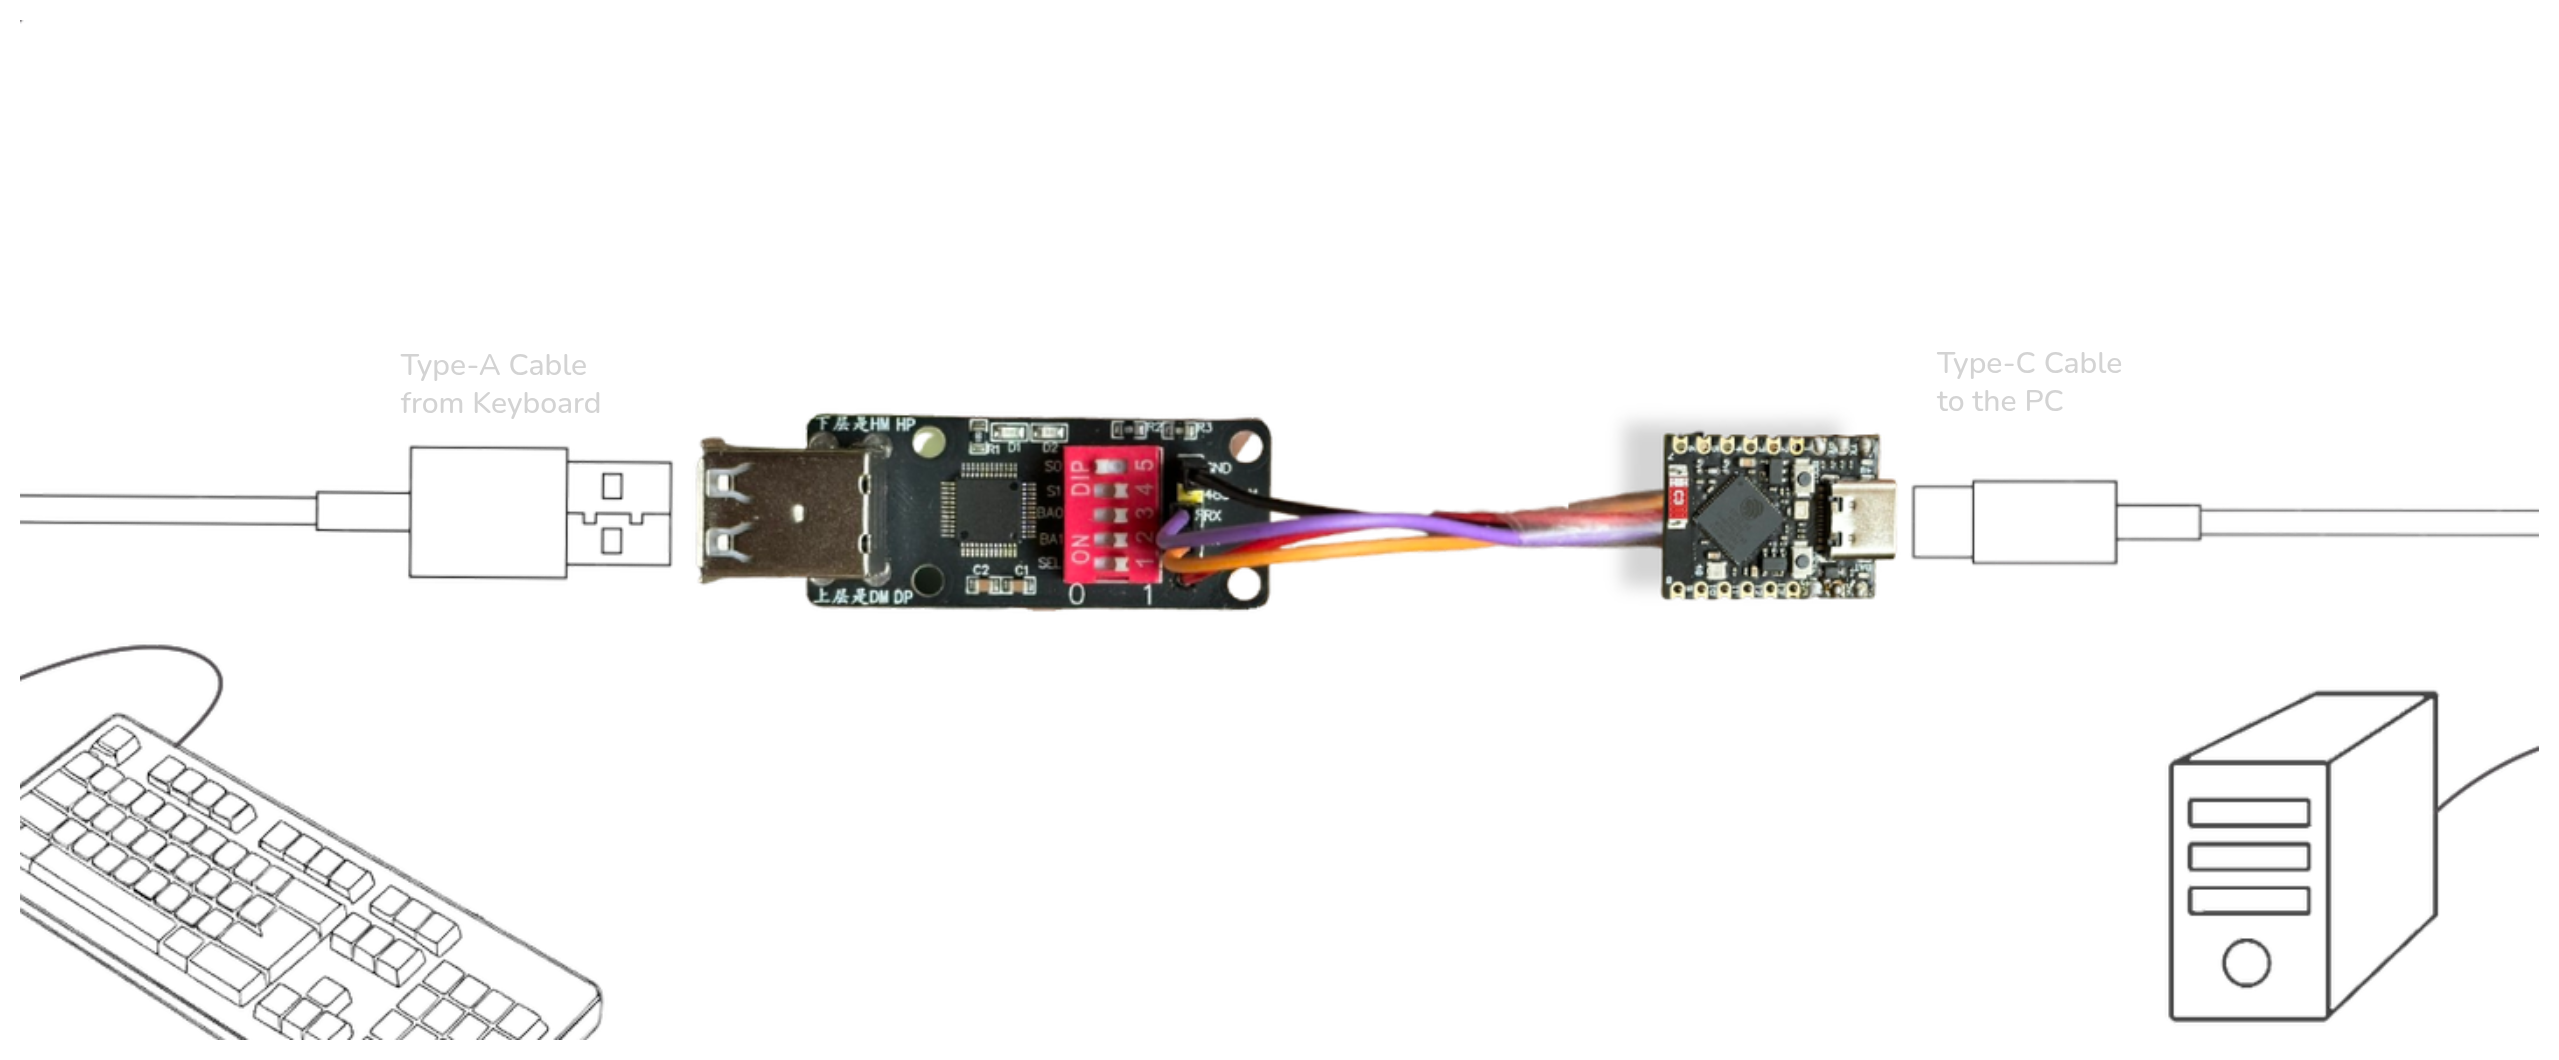 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 cyberharsh/mini_httpd-cve-2018-18778
PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.
 mateustesser/cve-2023-31716
Proof-of-concept exploit for CVE-2023-31716, a Local File Inclusion vulnerability in FUXA SCADA/HMI software versions <= 1.1.12, enabling arbitrary…
 qcomms/cqptoolkit
Framework for controlling QKD devices and managing symmetric keys. See the [project page here](https://qcomms.gitlab.io/cqptoolkit/)
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38427
CVE-2026-38427 — Integer Wraparound → Heap Buffer Overflow in Tasmota fetch_jpg() uint16_t (Tasmota <= 15.3.0.3)
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 ret5et/watchguard_webui_unpacker
Watchguard Sysa-dl file format
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)