ghostlock-oppo-watch3pro

Complete exploit research for CVE-2026-43499 (GhostLock) on OPPO Watch 3 Pro, including kernel UAF analysis, disassembly, and exploit chain…

Complete exploit research for CVE-2026-43499 (GhostLock) on OPPO Watch 3 Pro, including kernel UAF analysis, disassembly, and exploit chain…

Non-destructive PoC and technical write-up for CVE-2026-73673, an unauthenticated firmware-update flaw in Netis NC63 router, with reproduction and…

This repo contains dumped flash partitions with firmware version vulnerable to CVE-2019-17147, and some useful binaries to downgrade and debug your…

Provides a pre-compiled kernel patch for CVE-2026-31431 (Copy Fail) on RK35xx SBCs running Ubuntu 24.04, with installation instructions and build…

Suzuki connect app is used to get the car information like Fuel, Ignition status, Current location, Seat buckle status etc. In Ignis, Zeta variant…

Tools for reverse engineering and interacting with the PowerG radio protocol

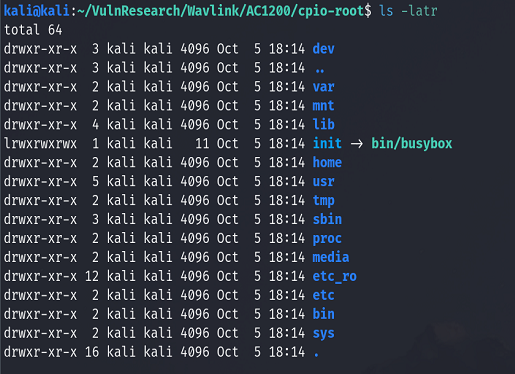
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…

Demonstrates CVE-2026-1122 Ed25519 signature bypass via low-order point injection, forging malicious IoT firmware updates with Python and C verifier…

Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…

Simulated 5G gNodeB NAS parser with stack buffer overflow PoC for CVE-2026-23002; a crafted NAS message triggers remote code execution.

Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…

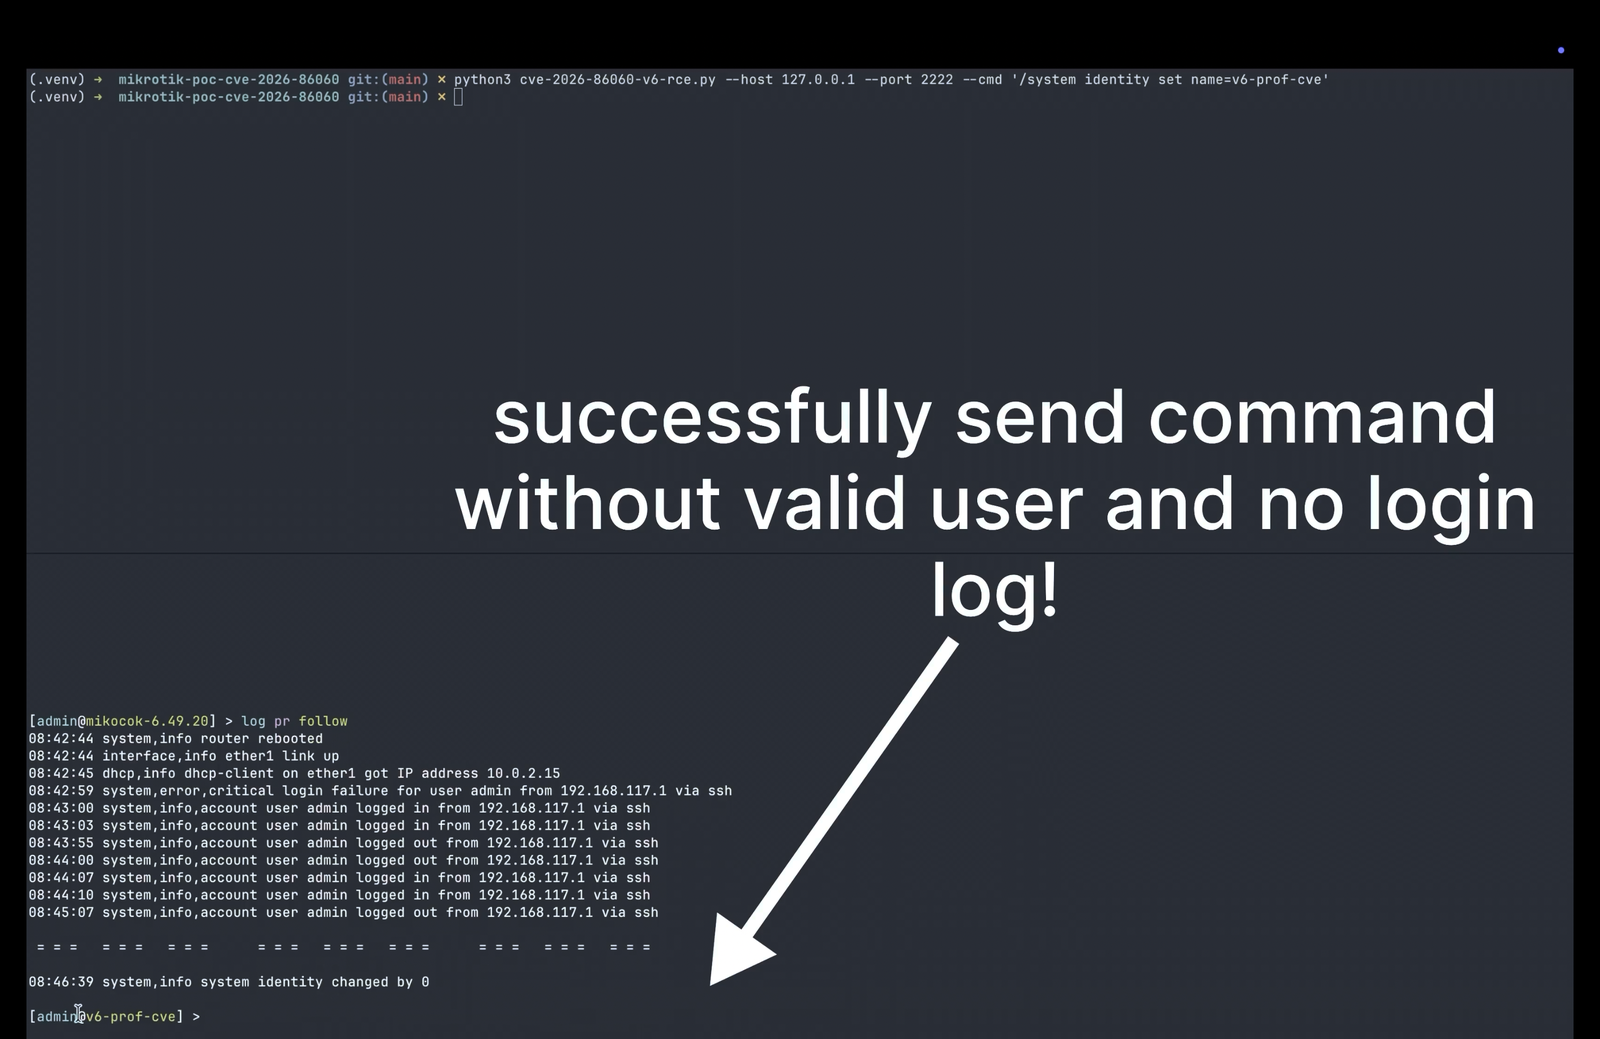
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…

Demonstrates a local access control bypass in AMI Aptio 5 NvLock module, allowing modification of NVRAM variables including administrator password,…

Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…

Stack overflow exploit for Tenda AC8 router (CVE-2023-33669) targeting firmware US_AC8V4.0si_V16.03.34.06 with emulation and RCE via TFTP.

PoC for three unauthenticated command injection vulnerabilities (CVE-2026-11450/1/2) in GL.iNet Beryl AX travel router firmware <=4.4.5, exploiting…