
 infobyte/doggie_workshop
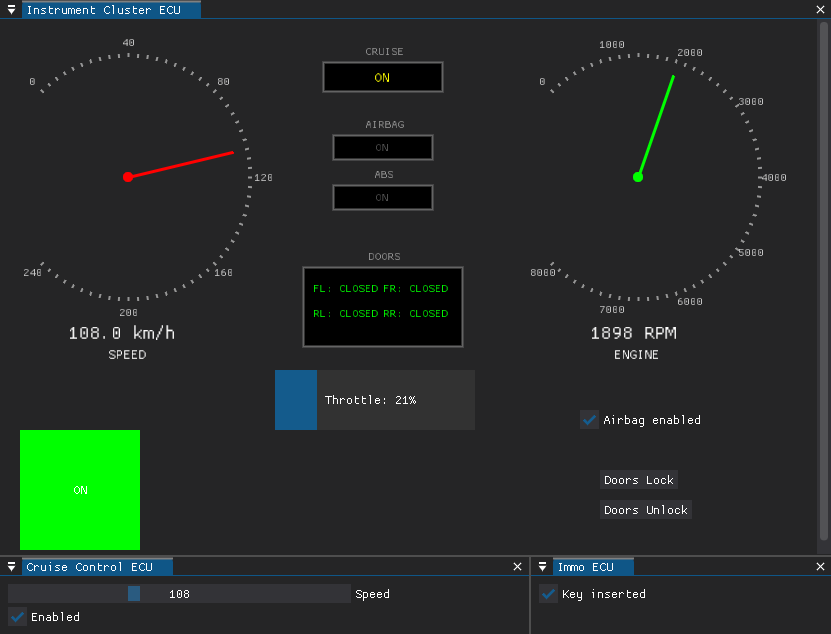
CAN Bus vehicle simulator for practicing offensive automotive security attacks. Emulates multiple ECUs to enable sniffing, injection, and…
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
 yousif-iq/cve-2026-39259
CVE-2026-39259
 0xblackash/cve-2026-12485
CVE-2026-12485
 dhammerg/cve-2023-33669
Stack overflow exploit for Tenda AC8 router (CVE-2023-33669) targeting firmware US_AC8V4.0si_V16.03.34.06 with emulation and RCE via TFTP.
 hunt-benito/glinet-beryl-ax-triple-rce-cve-2026-11450-11451-11452-unauthenticated-root-on-travel-router
PoC for three unauthenticated command injection vulnerabilities (CVE-2026-11450/1/2) in GL.iNet Beryl AX travel router firmware <=4.4.5, exploiting…
 victorique-123/cve-2023-38829-netis-wf2409e_report
对NETIS WF2409E路由器进行的一次完整硬件安全分析研究。通过对设备进行拆解分析、调试接口识别、固件提取等工作,记录了硬件分析的全过程、漏洞细节以及相应的安全建议,希望能帮助提高物联网设备的安全性。
 vidura2/cve-2024-46451
Python exploit for TOTOLINK AC1200 T8 buffer overflow vulnerability (CVE-2024-46451) with customizable payload generation and response logging for…
 nsnidie/cve-2023-40930
CVE-2023-40930 Repetition Enviroment
 fomovet/cve-2025-29384
POC for CVE-2025-29384
 mbanyamer/rtos-f-16-exploit---cve-2019-7711
Proof-of-concept exploit for CVE-2019-7711, a format string vulnerability in Green Hills INTEGRITY RTOS. Demonstrates a full attack chain with memory…
 hunt-benito/samsung-exynos-sms-stack-overflow-cve-2025-54328-critical-zero-click-baseband-rce
Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…
 kaleth4/cve-2019-7711
Technical documentation and proof-of-concept for CVE-2019-7711, a format string vulnerability in Green Hills INTEGRITY RTOS Telnet server, enabling…
 ktauchathuranga/cve-2025-70994
Passive RF signal analyzer for EV1527 fixed-code protocol, demonstrating CVE-2025-70994 replay vulnerability in Yadea T5 keyless entry systems.…
 askhatov21/best-practices-cybersecurity-otanata-project
CVE-2024-3273 — Authorized Penetration Test Report D-Link DNS-320L NAS | Client: Otonata
 kaleth4/cve-2025-0690
Technical analysis of CVE-2025-0690: integer overflow in GRUB2's read command leading to heap out-of-bounds write, arbitrary code execution, and…