
CVE-2026-19586
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
command-and-controlcryptographyembedded-systems-security+6
mattgsys/cve-2026-19586Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
 majidmc2/cve-2023-40459
PoC of CVE-2023-40459 (DoS on ACEmanager)
 0xblackash/cve-2026-11499
CVE-2026-11499
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38427
CVE-2026-38427 — Integer Wraparound → Heap Buffer Overflow in Tasmota fetch_jpg() uint16_t (Tasmota <= 15.3.0.3)
 fomovet/cve-2025-29384
POC for CVE-2025-29384
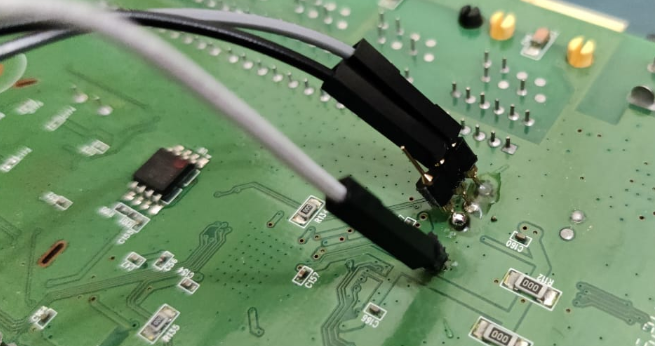 whitej3rry/cve-2025-65731
Advisory for CVE-2025-65731
 zgsnj123/cve-2025-45467
Proof-of-concept exploit for CVE-2025-45467, demonstrating remote code execution on Unitree Go1 robotic dogs via insecure MD5-based firmware…
 luismirandaacebedo/cve-2025-65855
Security advisory for CVE-2025-65855 - Multiple vulnerabilities in HelpFlash IoT OTA update mechanism
 darkspoook/cve-2025-67445
A PoC for CVE-2025-67445
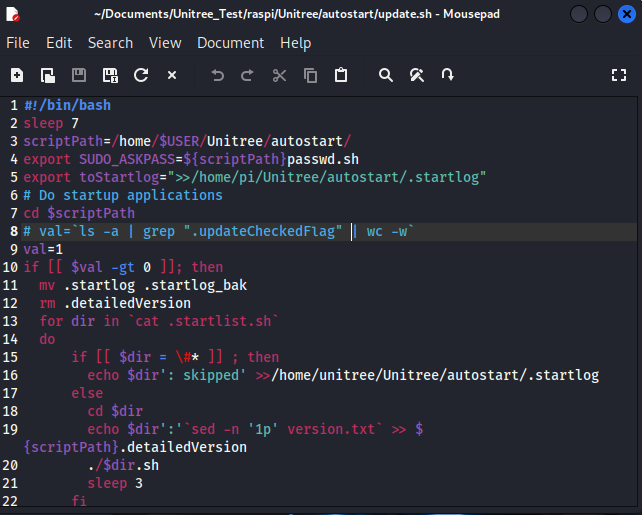 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
 cybervinner/tp-link-tl-wr820n-cve-2025-14175
Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.
 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912
 nap3xd/cve-2023-33869-rce-poc
Remote Code Execution (RCE) proof of concept on a enphase solar inverter