
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
326 results
CVE-2019-17147 preview

CVE-2019-17147

GitHubimnot-ye/cve-2019-17147

Comprehensive reverse engineering and exploitation of CVE-2019-17147, a stack buffer overflow in TP-Link TL-WR841N routers. Includes firmware…

binary-exploitationeducationembedded-systems-security+9
4
8 months ago
CVE-2022-24693 preview

CVE-2022-24693

GitHublukejenkins/cve-2022-24693

Documentation and reproduction steps for CVE-2022-24693: hardcoded credentials in Baicells Nova436Q and Neutrino 430 firmware, enabling remote SSH…
embedded-systems-securityexploitationfirmware-analysis+6
31 year ago
CVE-2022-40363 preview

CVE-2022-40363

GitHubolafdaf/cve-2022-40363

A buffer overflow in the component nfc_device_load_mifare_ul_data of Flipper Devices Inc., Flipper Zero before v0.65.2 allows attackers to cause a…
binary-analysisembedded-systems-securityexploitation+3
53 years ago
mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce preview

mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce

GitHubhunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce

Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…

binary-exploitationeducationembedded-systems-security+5
33 months ago
CVE-2025-29338 preview

CVE-2025-29338

GitHubmasjadaan/cve-2025-29338

Technical advisory and proof-of-concept for a stack-based buffer overflow (CWE-121) in the NXP moal.ko Wi-Fi kernel driver, enabling local kernel…

binary-exploitationembedded-systems-securityexploitation+2
34 months ago
CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure preview

CVE-2020-35575-TP-LINK-TL-WR841ND-password-disclosure

GitHubdylvie/cve-2020-35575-tp-link-tl-wr841nd-password-disclosure

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…
embedded-systems-securityexploitationiot-security+3
31 year ago
zephyr-lwm2m-firmware-update-oob-read-cve-2026-10672-truncated-package-uri preview

zephyr-lwm2m-firmware-update-oob-read-cve-2026-10672-truncated-package-uri

GitHubhunt-benito/zephyr-lwm2m-firmware-update-oob-read-cve-2026-10672-truncated-package-uri

Proof-of-concept exploit for CVE-2026-10672, an out-of-bounds read in Zephyr RTOS LwM2M firmware-update pull client. Includes standalone C…
binary-exploitationeducationembedded-systems-security+5
2 months ago
Poc-CVE-2024-57040 preview

Poc-CVE-2024-57040

GitHubabsholi7ly/poc-cve-2024-57040

CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…

embedded-systems-securityexploitationhardware-iot-security+3
21 year ago
CVE-2017-13672 preview

CVE-2017-13672

GitHubdavidbuchanan314/cve-2017-13672

POCs for CVE-2017-13672 (OOB read in VGA Cirrus QEMU driver, causing DoS)
binary-analysisembedded-systems-securityexploitation+3
38 years ago
CVE-2026-6789-Stack-Buffer-Overflow-in-Embedded-TLS-Certificate-Parser preview

CVE-2026-6789-Stack-Buffer-Overflow-in-Embedded-TLS-Certificate-Parser

GitHubgeorge0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser

Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…
binary-exploitationeducationembedded-systems-security+3
2 months ago
CVE-2026-75616 preview

CVE-2026-75616

GitHubtotekuh/cve-2026-75616

Proof-of-concept exploit for authenticated OS command injection in TP-Link Archer C20 v6 web management interface, executing root commands via BPA…
embedded-systems-securityexploitationiot-security+1
11 month ago
cve-2015-1187-dir820l-firmware-reverse-engineering preview

cve-2015-1187-dir820l-firmware-reverse-engineering

GitHubchristopher-leese/cve-2015-1187-dir820l-firmware-reverse-engineering

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

embedded-systems-securityexploitationfirmware-analysis+5
1 month ago
POC-CVE-2025-31931 preview

POC-CVE-2025-31931

GitHubyohanes/poc-cve-2025-31931

Proof-of-concept exploit for CVE-2025-31931 demonstrating arbitrary shared library loading in Intel ITT API on Android, affecting OpenCV 4.10.

android-securitybinary-exploitationembedded-systems-security+3
410 months ago
Ripple20 preview

Ripple20

GitHubransc0rp1on/ripple20

This comprehensive package contains everything needed to detect, analyze, and remediate Ripple20 (CVE-2020-11898) vulnerabilities in your…
embedded-systems-securityfirmware-analysisiot-security+3
2 months ago
PX4-Military-UAV-Autopilot-1.12.3-Stack-Buffer-Overflow-Exploit-CVE-2025-5640- preview

PX4-Military-UAV-Autopilot-1.12.3-Stack-Buffer-Overflow-Exploit-CVE-2025-5640-

GitHubmbanyamer/px4-military-uav-autopilot-1.12.3-stack-buffer-overflow-exploit-cve-2025-5640-

Proof-of-concept exploit for CVE-2025-5640, a stack buffer overflow in PX4 Military UAV Autopilot <=1.12.3. Sends crafted MAVLink packets to trigger…
binary-exploitationembedded-systems-securityexploitation+3
41 year ago
CVE-2026-85769 preview

CVE-2026-85769

GitHubisukasanuj/cve-2026-85769

Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
binary-analysisembedded-systems-securityexploitation+3
19 days ago
Firmware-analysis preview

Firmware-analysis

GitHubgimminse/firmware-analysis

Rediscovered CVE-2020-25279, a critical vulnerability in the Shannon baseband used in Samsung Exynos chipsets
binary-analysisembedded-systems-securityexploitation+3
1 month ago
doggie_workshop preview

doggie_workshop

GitHubinfobyte/doggie_workshop

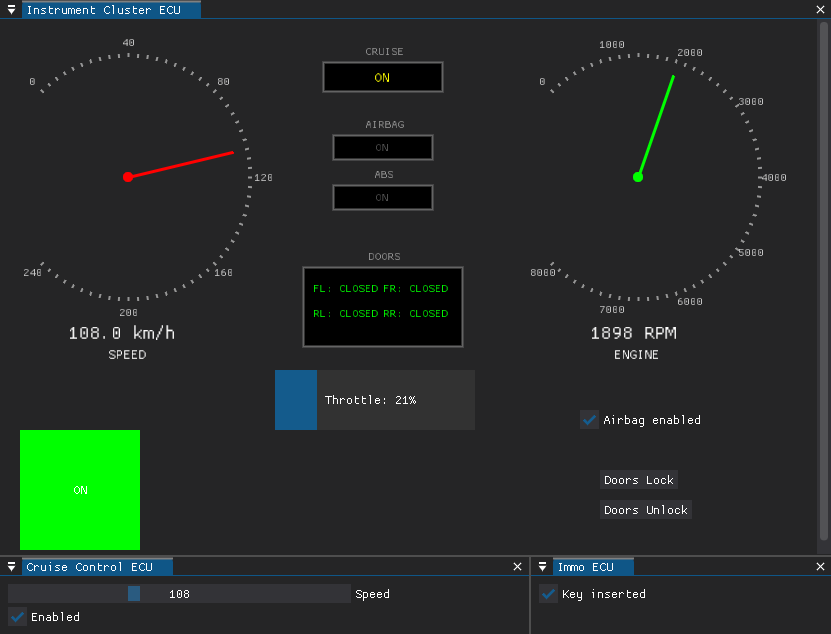
CAN Bus vehicle simulator for practicing offensive automotive security attacks. Emulates multiple ECUs to enable sniffing, injection, and…

educationembedded-systems-securityfuzzing+4
21 year ago
Previous1…456…19Next