
CVE-2025-51643
 nastycrow/cve-2025-51643
Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…
data-exfiltrationembedded-systems-securityexploitation+6
1
nastycrow/cve-2025-51643Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…
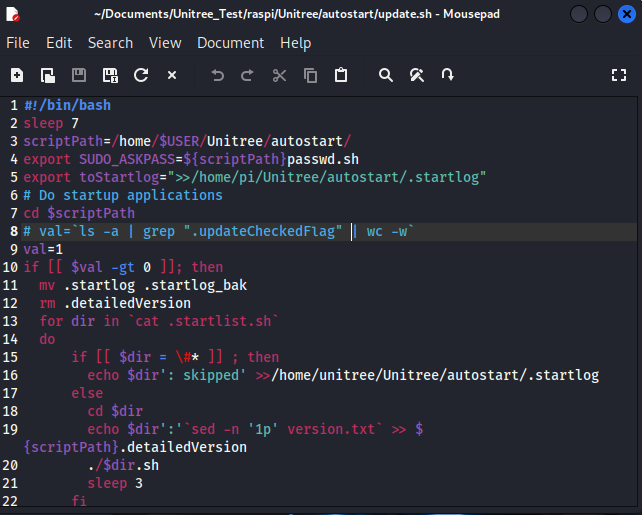 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 xernary/cve-2025-63820
Proof-of-concept of vulnerability found in Totolink A720R router
 cipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment
A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…
 likeww/cve-2021-41653
TP-Link TL-WR840N EU v5 Remote Code Execution
 ndureiss/e1000_vulnerability_exploit
Exploitation of VirtualBox vulnerability (https://nvd.nist.gov/vuln/detail/CVE-2018-3295)
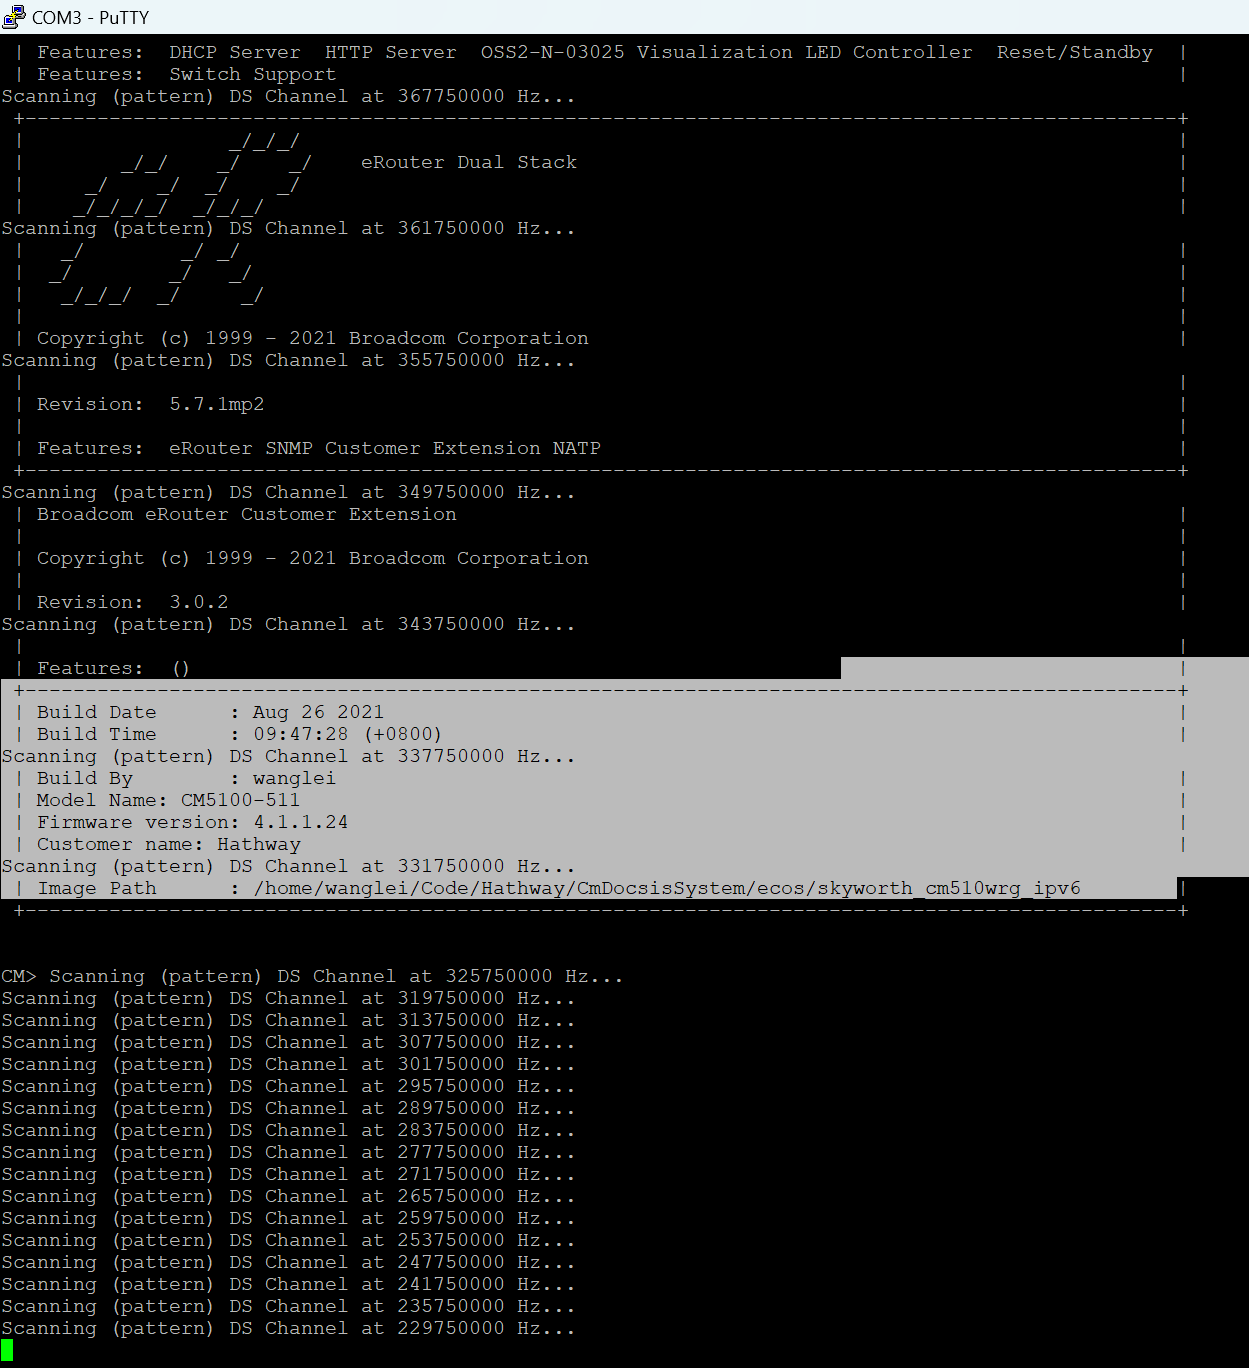 nitinronge91/extracting-user-credentials-for-web-portal-and-wifi-ap-for-hathway-router-cve-2024-44815-
CVE-2024-44815
 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 abood05972/cve-2020-3161
Cisco IP Phone 11.7 - Denial of Service (PoC)
 yanissec/cve-2018-7842
CVE-2018-7842
 yanissec/cve-2018-7844
CVE-2018-7844
 tlatkdgus1/blueborne-cve-2017-1000251
clone
 szymonh/d-os-descriptor
CVE-2022-25258 - Demo exploit targeting usb gadget's os descriptor handler
 yanissec/cve-2018-7852
CVE-2018-7852
 spiralbl0ck/bios-stuff-related-programming
Final OBJECTIVE:BIOS ROOTKIT AND RSHELL USING BIOS NETWORKING STACK