CVE-2026-22017-Firmware-Update-via-BLE-Without-Authentication

Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…

Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…

This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.

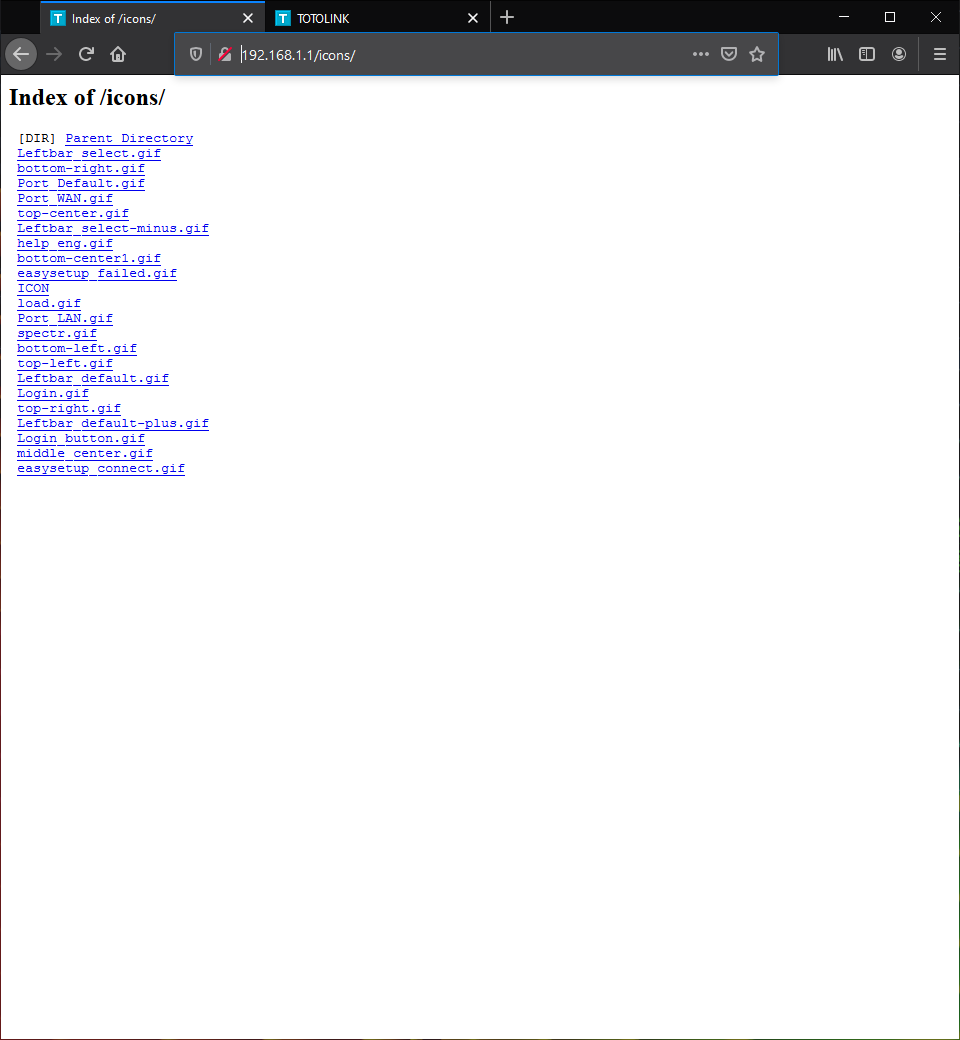
Proof-of-concept of vulnerability found in Totolink A720R router

CVE-2021-4045 CVE-2021-4045 is a Command Injection vulnerability that allows Remote Code Execution in the TP-Link Tapo c200 IP camera. It affects all…

Documentation of CVE-2026-36438: a vulnerability in Intelbras VIP 1230 B/D G4 devices allowing remote attackers to obtain administrator account…

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

Western Digital MyCloud PR4100 Link Resolution Information Disclosure Vulnerability

KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability

D-link AX1500 Vulnerability

Maxprint Maxlink 1200G v3.4.11E has an OS command injection vulnerability in the "Diagnostic tool" functionality of the device.

Documentation of CVE-2020-25748: Cleartext transmission vulnerability in Rubetek IP cameras allowing MITM interception and modification of video…

TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability

HP Deskjet 2540 series printer Firmware Version CEP1FN1418BR and Product Model Number A9U23B HTTP configuration page Cross Site Scripting (XSS)…

A collection of my public security advisories.

Epson Printer RAW Protocol Exploit Framework

CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)

Here is the CVE-2025-65817

By the Way is an exploit that enables a root shell on Mikrotik devices running RouterOS versions: