
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
326 results
CVE-2026-90847 preview

CVE-2026-90847

GitHubshlln/cve-2026-90847

Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
embedded-systems-securityexploitationiot-security+5
11 days ago
cve-2026-86547-mrubyc-op-enter preview

cve-2026-86547-mrubyc-op-enter

GitHubharshrajsinghania/cve-2026-86547-mrubyc-op-enter

Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
embedded-systems-securityexploitationfuzzing+3
25 days ago
Vulnerability-DLink-CVE-2025-14659 preview

Vulnerability-DLink-CVE-2025-14659

GitHubpeterlinccl/vulnerability-dlink-cve-2025-14659

Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…
embedded-systems-securityexploitationfirmware-analysis+6
24 days ago
CVE-2026-38577 preview

CVE-2026-38577

GitHubpoxsky/cve-2026-38577

Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
embedded-systems-securityexploitationfirmware-analysis+5
1 month ago
CVE-2026-96515 preview

CVE-2026-96515

GitHubwhoami-012/cve-2026-96515

Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…

binary-analysisembedded-systems-securityexploitation+7
12 days ago
UEFI-Security-Research-Howyar-SysReturn-NetCopy preview

UEFI-Security-Research-Howyar-SysReturn-NetCopy

GitHubthemalwareguardian/uefi-security-research-howyar-sysreturn-netcopy

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
binary-analysisembedded-systems-securityexploitation+6
225 days ago
CVE-2025-9961 preview

CVE-2025-9961

GitHubyt2w/cve-2025-9961

Exploit for TP-Link AX10/AX1500 stack buffer overflow in CWMP (TR-069) enabling remote code execution via ret2libc with ASLR bypass. Includes…

binary-exploitationembedded-systems-securityexploitation+5
69 months ago
CVE-2020-8597 preview

CVE-2020-8597

GitHublakwsh/cve-2020-8597

Exploit for CVE-2020-8597 targeting RM2100 routers, providing proof-of-concept code for remote code execution via buffer overflow in the router's web…
binary-exploitationembedded-systems-securityexploitation+3
55 years ago
DevicePairedTool preview

DevicePairedTool

GitHubelevenpaths/devicepairedtool

Tool for testing and auditing Bluetooth device pairing security, identifying vulnerabilities in wireless pairing protocols and hardware IoT…

bluetooth-securityembedded-systems-securityhardware-iot-security+3
58 years ago
CVE-2026-73673 preview

CVE-2026-73673

GitHubozcanpng/cve-2026-73673

Non-destructive PoC and technical write-up for CVE-2026-73673, an unauthenticated firmware-update flaw in Netis NC63 router, with reproduction and…
authentication-authorizationembedded-systems-securityexploitation+3
31 month ago
CVE-2025-22968 preview

CVE-2025-22968

GitHubcrunzex/cve-2025-22968

Unauthenticated access in the default configuration of the D-Link DWR-M972V
embedded-systems-securityexploitationiot-security+3
61 year ago
CVE-2026-95675 preview

CVE-2026-95675

GitHubd6fault/cve-2026-95675

Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
embedded-systems-securityexploitationfirmware-analysis+6
112 days ago
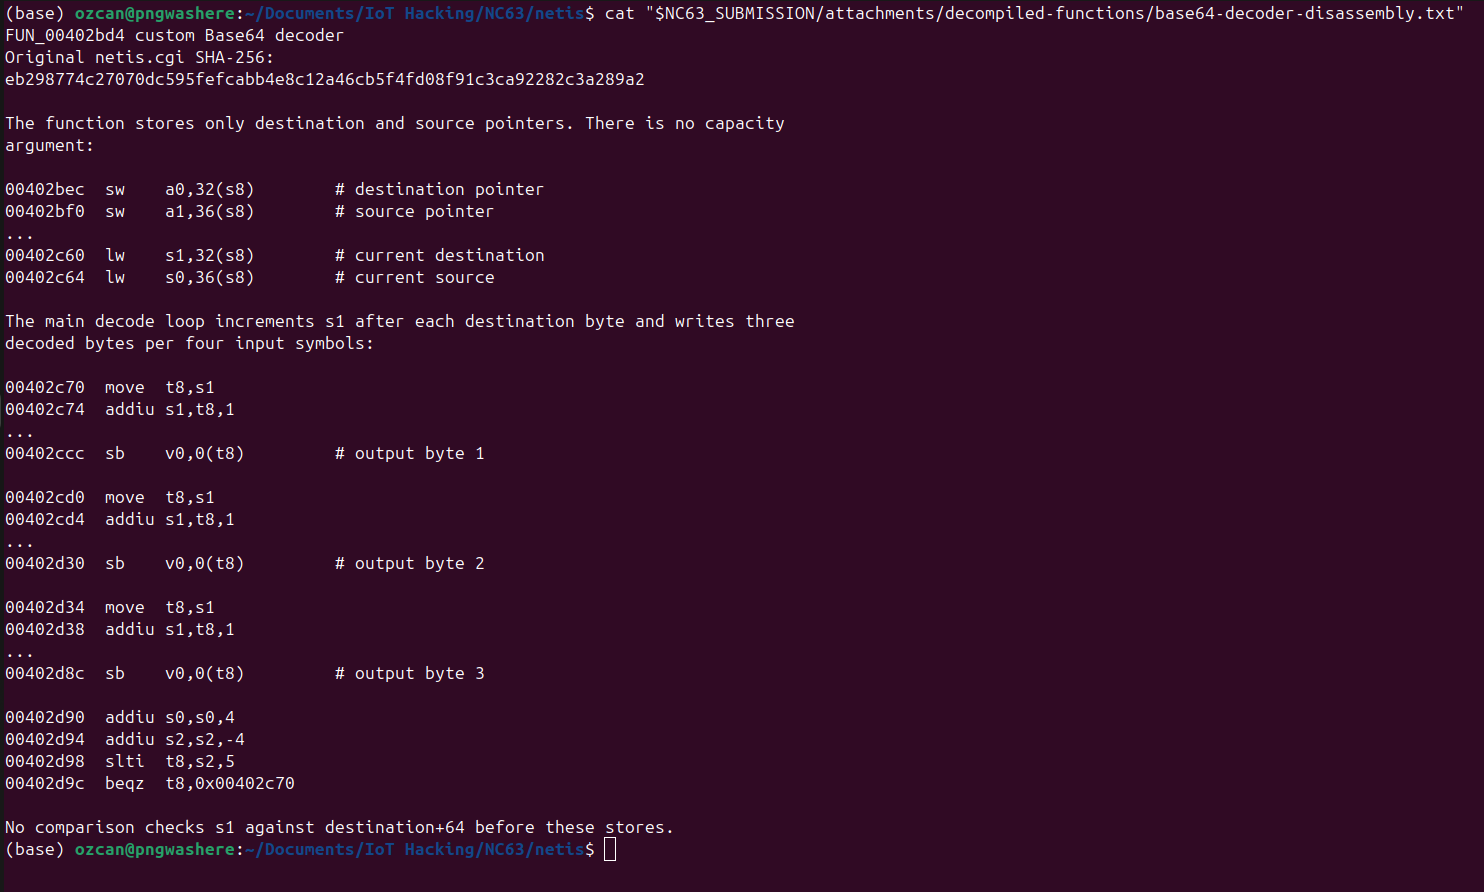
CVE-2026-76070 preview

CVE-2026-76070

GitHubozcanpng/cve-2026-76070

Original research and PoC for a pre-auth Base64-decoded password stack buffer overflow in Netis NC63 login.cgi
binary-exploitationembedded-systems-securityexploitation+4
123 days ago
CVE-2026-19586 preview

CVE-2026-19586

GitHubmattgsys/cve-2026-19586

Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
command-and-controlcryptographyembedded-systems-security+6
21 month ago
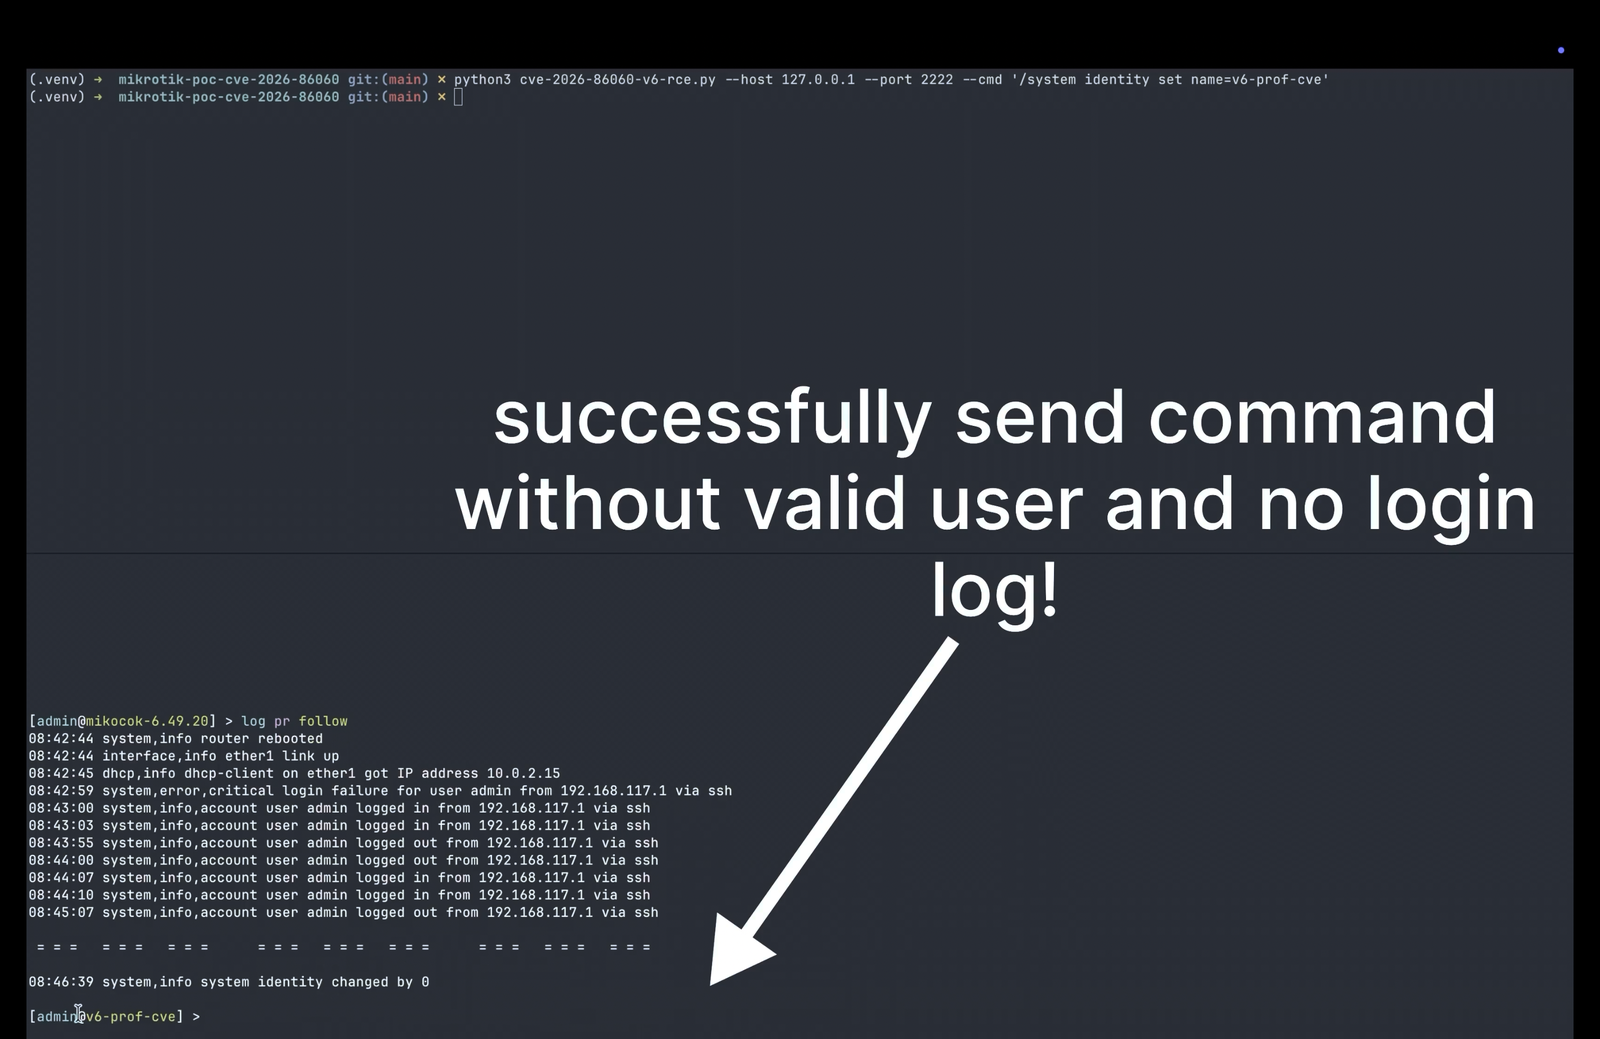
cve-2026-86060 preview

cve-2026-86060

GitHubbahirul/cve-2026-86060

Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…

defensive-toolsembedded-systems-securityexploitation+4
126 days ago
CVE-2024-24488 preview

CVE-2024-24488

GitHublegacyobj/cve-2024-24488

An issue in Shenzen Tenda Technology CP3V2.0 V11.10.00.2311090948 allows a local attacker to obtain sensitive information via the password component.
embedded-systems-securityexploitationhardware-iot-security+3
52 years ago
CVE-2026-94095 preview

CVE-2026-94095

GitHubhackspeak/cve-2026-94095

PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
embedded-systems-securityexploitationhardware-iot-security+5
115 days ago
CVE-2022-26269 preview

CVE-2022-26269

GitHubnsbogam/cve-2022-26269

Suzuki connect app is used to get the car information like Fuel, Ignition status, Current location, Seat buckle status etc. In Ignis, Zeta variant…

embedded-systems-securityexploitationfuzzing+2
24 years ago
Previous1…345…19Next