
CVE-2024-29269
 dkstar11q/cve-2024-29269
Exploit for CVE-2024-29269 enabling unauthenticated OS command execution on TLR-2005KSH routers, with ZoomEye and Leakix dork queries for target…
embedded-systems-securityexploitationinformation-gathering+5
dkstar11q/cve-2024-29269Exploit for CVE-2024-29269 enabling unauthenticated OS command execution on TLR-2005KSH routers, with ZoomEye and Leakix dork queries for target…
 fzbacon/cve-2022-34527_d-link_dsl-3782_router_command_injection
Proof-of-concept exploit for CVE-2022-34527, a command injection vulnerability in D-Link DSL-3782 routers, enabling remote code execution via crafted…
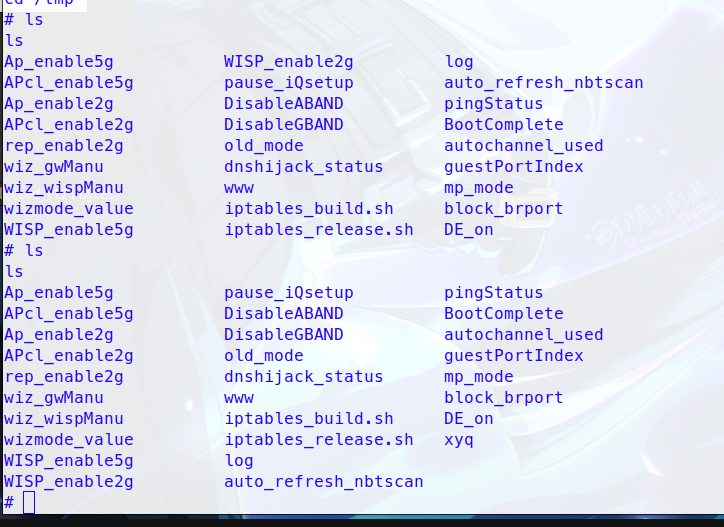 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 meshcore-dev/meshcore
A new lightweight, hybrid routing mesh protocol for packet radios
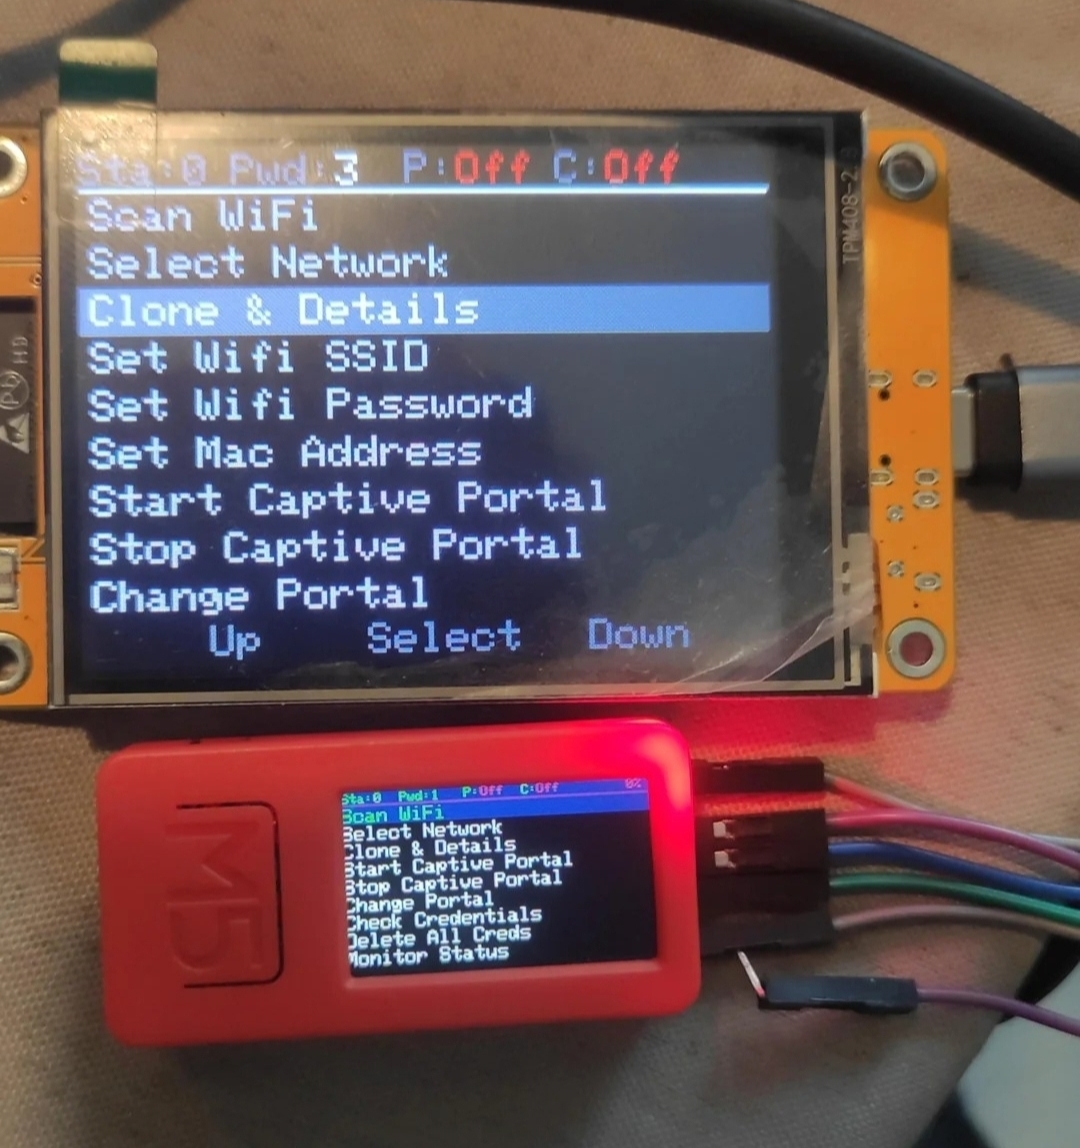 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
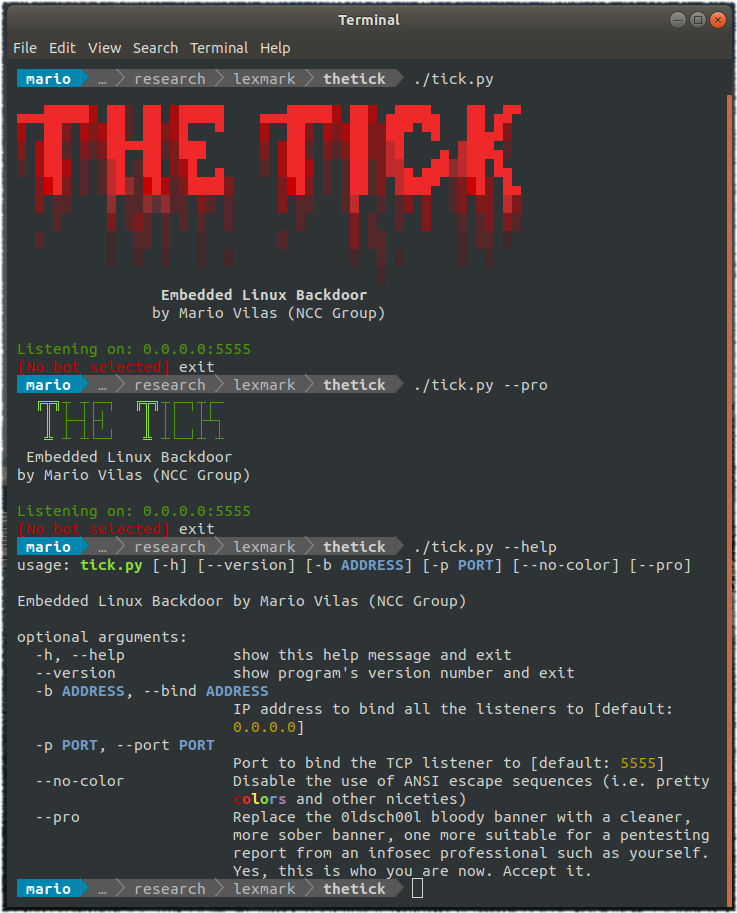 nccgroup/thetick
A simple embedded Linux backdoor.
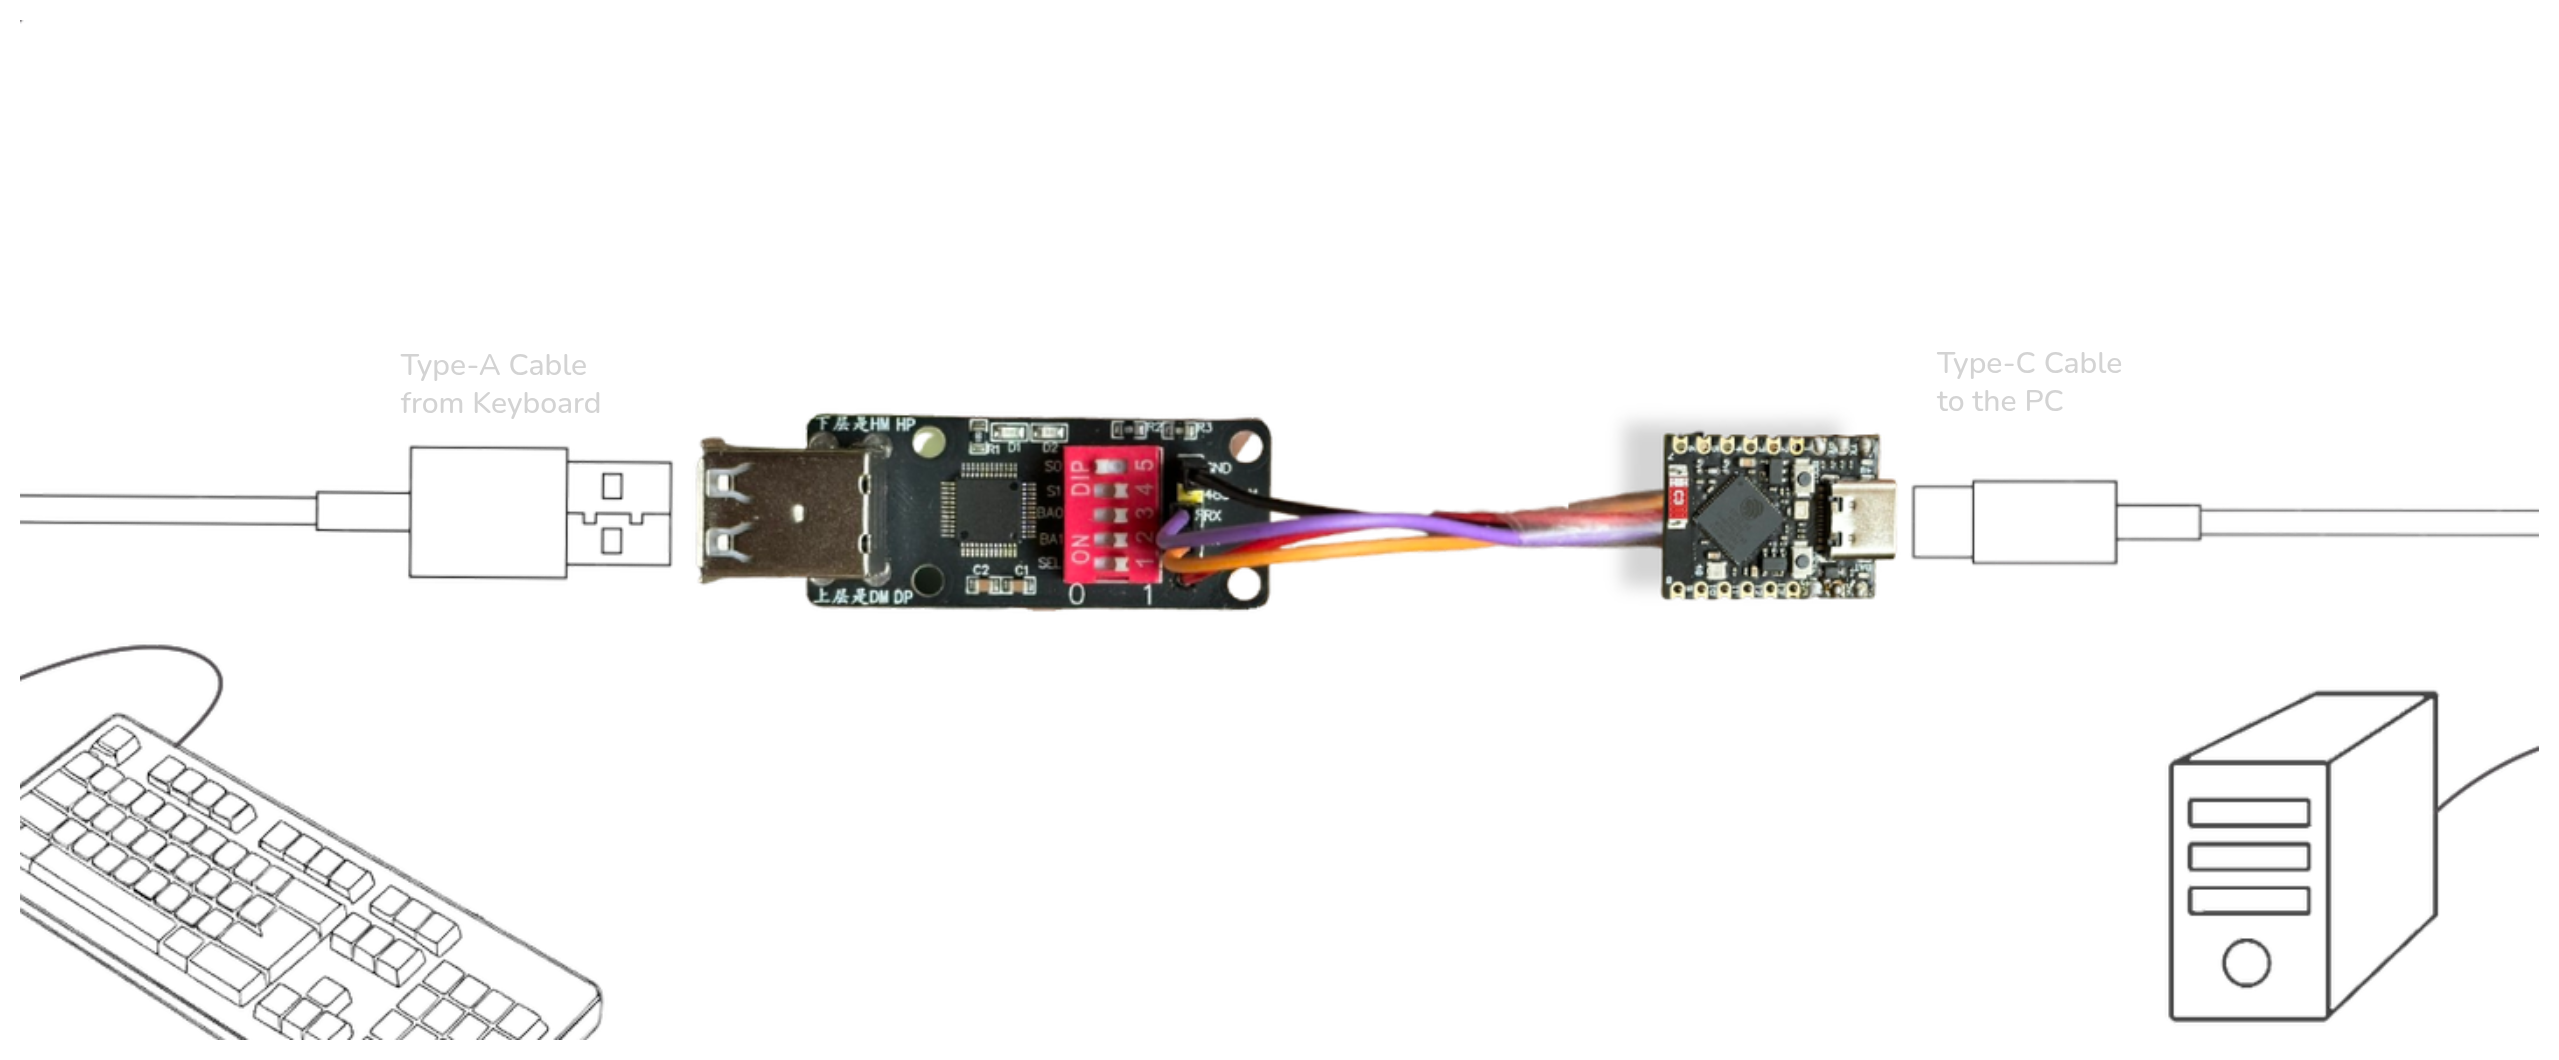 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 jackdoan/tp-link-archerc5-rce
CVE-2018-19537
 analyticeth/tesla-security-research
Vulnerability research on Tesla Model 3/Y infotainment systems. 6 vulnerabilities, 4 CVEs (CVE-2022-42005 through CVE-2022-42008). Root shell,…
 askhatov21/best-practices-cybersecurity-otanata-project
CVE-2024-3273 — Authorized Penetration Test Report D-Link DNS-320L NAS | Client: Otonata
 badboycxcc/cve-2021-43469
CVE-2021-43469
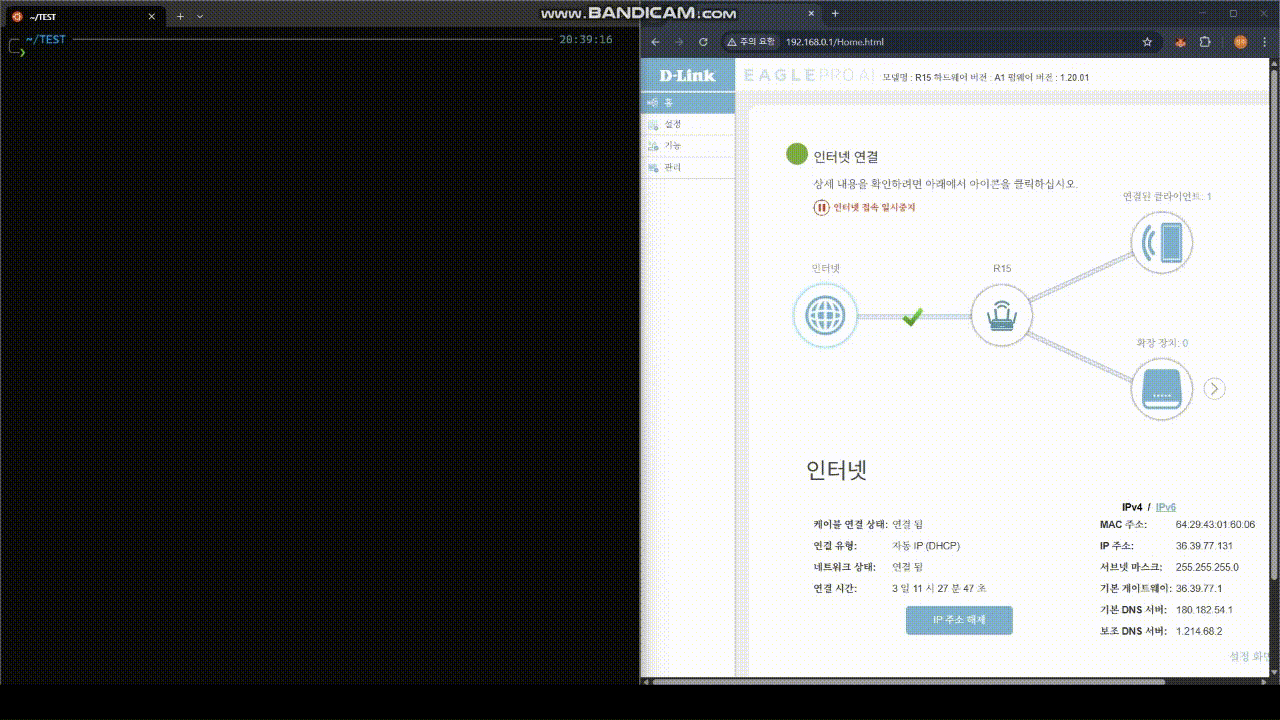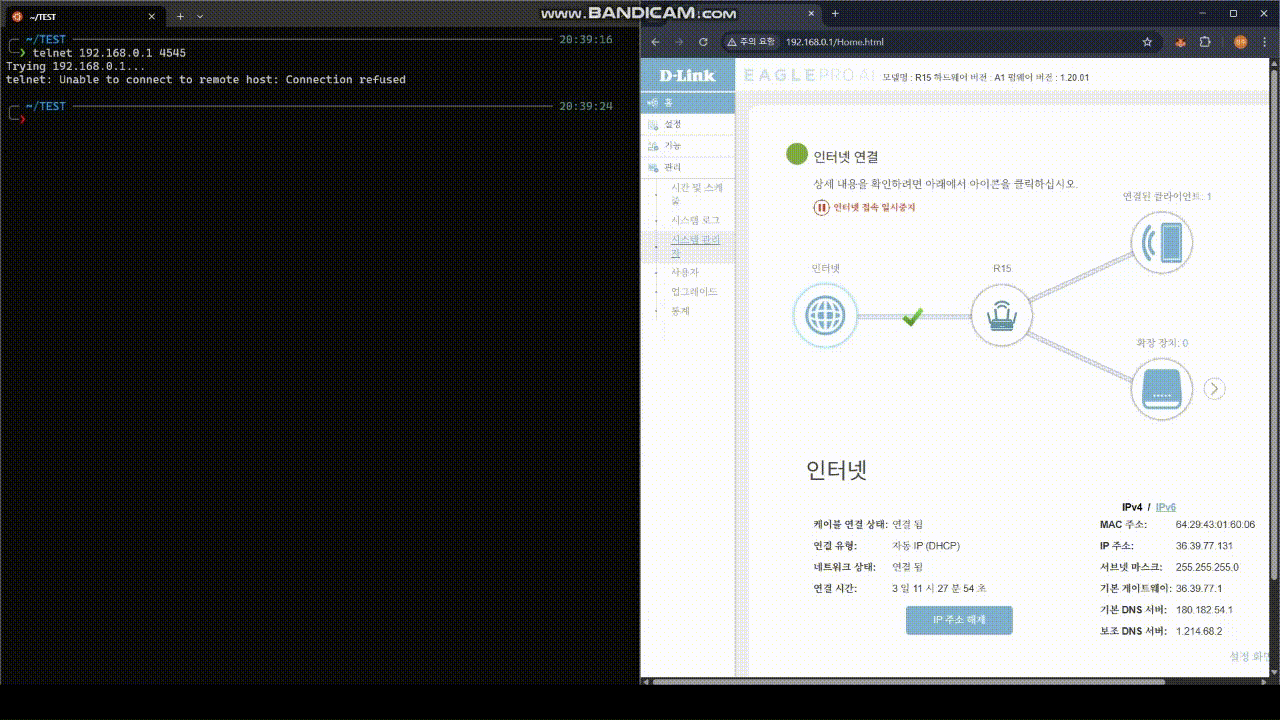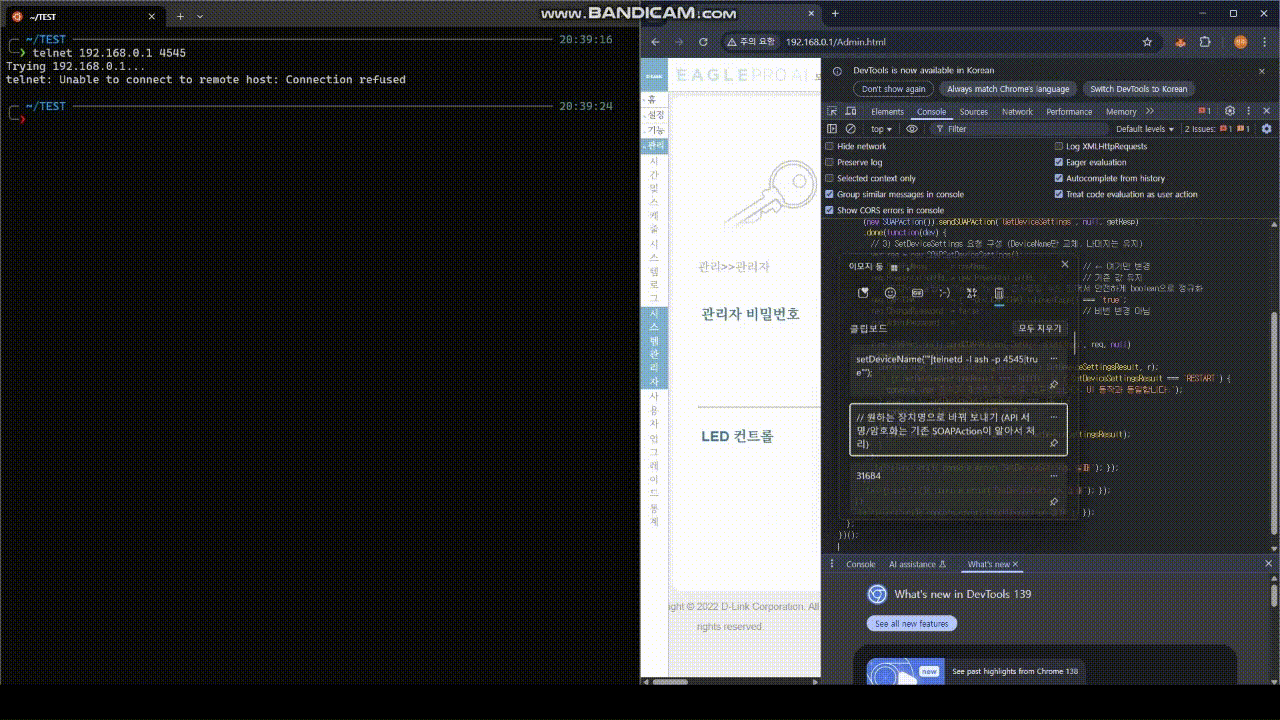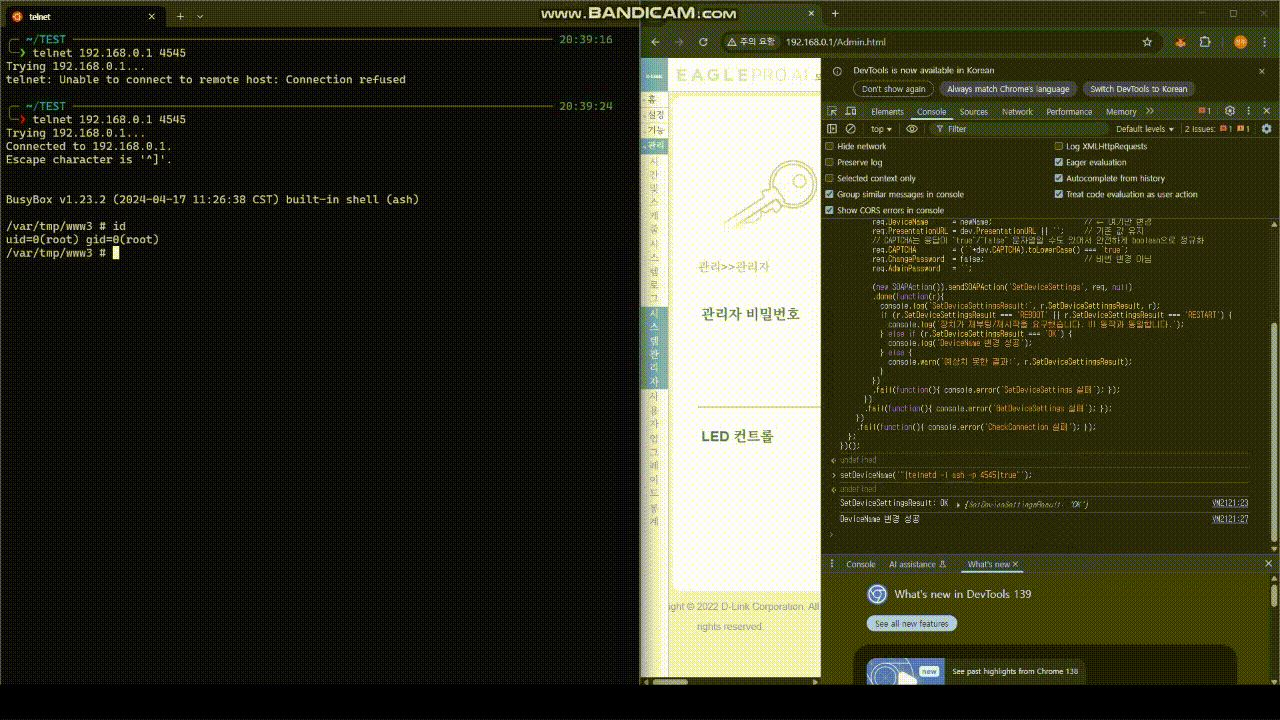 k0n9-log/cve-2025-60854
D-link AX1500 Vulnerability
 kristof-mattei/gardyn-hack
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 kiwidoggie/oni-framework
Embedded systems C2 software written in C/C#