CVE-2022-46152
 0xbbdd/cve-2022-46152
CVE-2022-46152: Improper Validation of Array Index in the `cleanup_shm_refs' function.
binary-exploitationctfeducation+5
0xbbdd/cve-2022-46152CVE-2022-46152: Improper Validation of Array Index in the `cleanup_shm_refs' function.
iot-ptv/iot-pt-v1A Virtual environment for Pentesting IoT Devices
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 bkerler/mtkclient
Mediatek Flash and Repair Utility
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 laginimaineb/extractkeymaster
Exploit that extracts Qualcomm's KeyMaster keys using CVE-2015-6639 and CVE-2016-2431
 zhuowei/cheese
CVE-2025-21479 proof-of-concept, I think
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
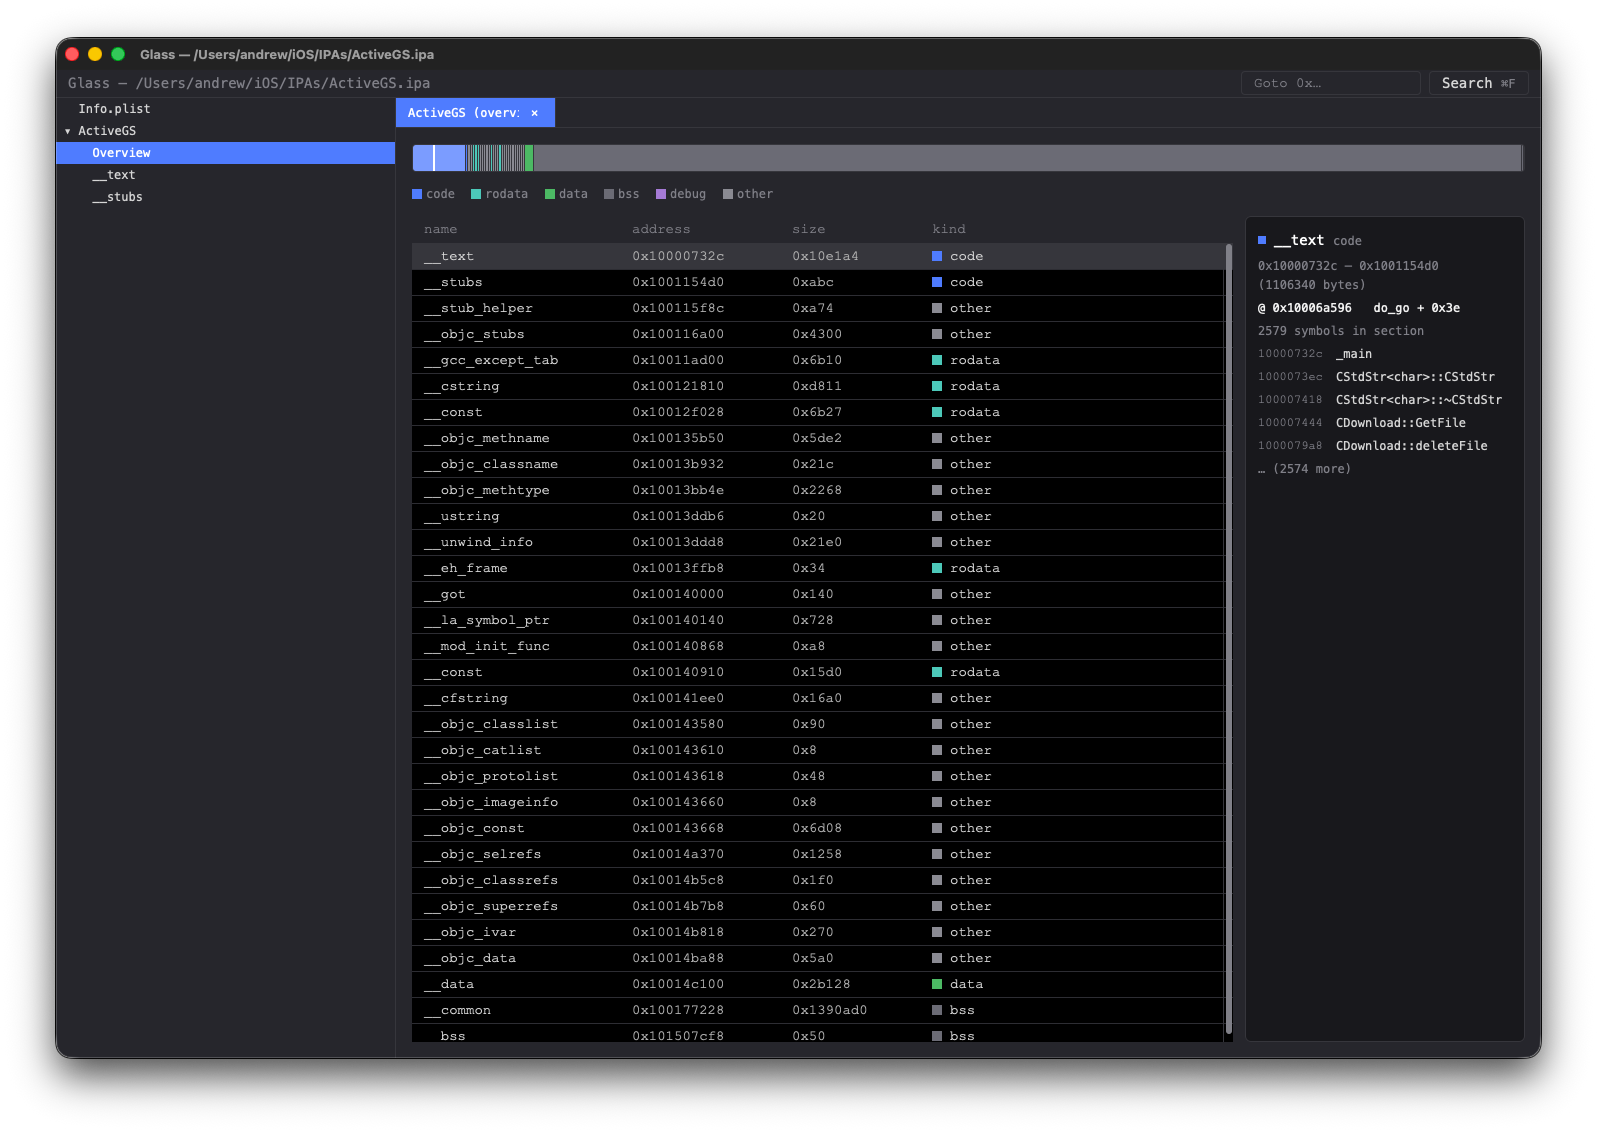 azw413/glass
Glass - a fast and free IDA Pro alternative
 mailinneberg/broadpwn
Broadpwn bug (CVE-2017-9417)
 laginimaineb/cve-2016-2431
Qualcomm TrustZone kernel privilege escalation
 oneplusoss/android_kernel_modules_and_devicetree_oneplus_sm8550
Low-level kernel modules and device tree source for the OnePlus 11 (sm8550), enabling hardware bring-up, driver analysis, and embedded system…
 kasnria001/pwnage24mtk
Cert exploit for MTK devices.There is a logic flaw in MTK cert verification process.Similar to CVE-2023-20696.
 shinyquagsire23/cve-2020-12753-poc
A proof-of-concept for CVE-2020-12753