

angr
 angr/angr
A powerful and user-friendly binary analysis platform!
ai-assisted-reversingbinary-analysisbinary-exploitation+12
angr/angrA powerful and user-friendly binary analysis platform!
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 newbe3e/pwn2own-automotive-2026-alpine-ilx-f511-0-click-rce-exploit-writeup
Writeup of a 0-click remote code execution exploit chain developed for the Alpine iLX-F511 automotive head unit at Pwn2Own Automotive 2026.
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 bkerler/mtkclient
Mediatek Flash and Repair Utility
 tangrs/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668.
 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 aomsin2526/xperia_5_bl_unlocker_poc
My take on unlocking Xperia 5 SO-01M for p42 bootloader using CVE-2021-1931
 264312431/picohaxx
A kernel exploit for Pico 4 devices based on cve-2023-33107.
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
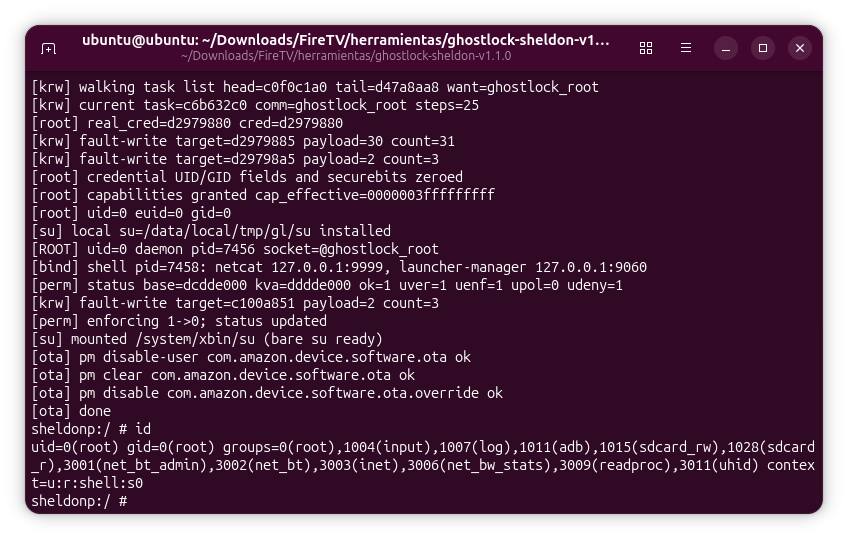 accessmodifier364/cve-2026-43499-firetv-sheldonp-writeup
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.
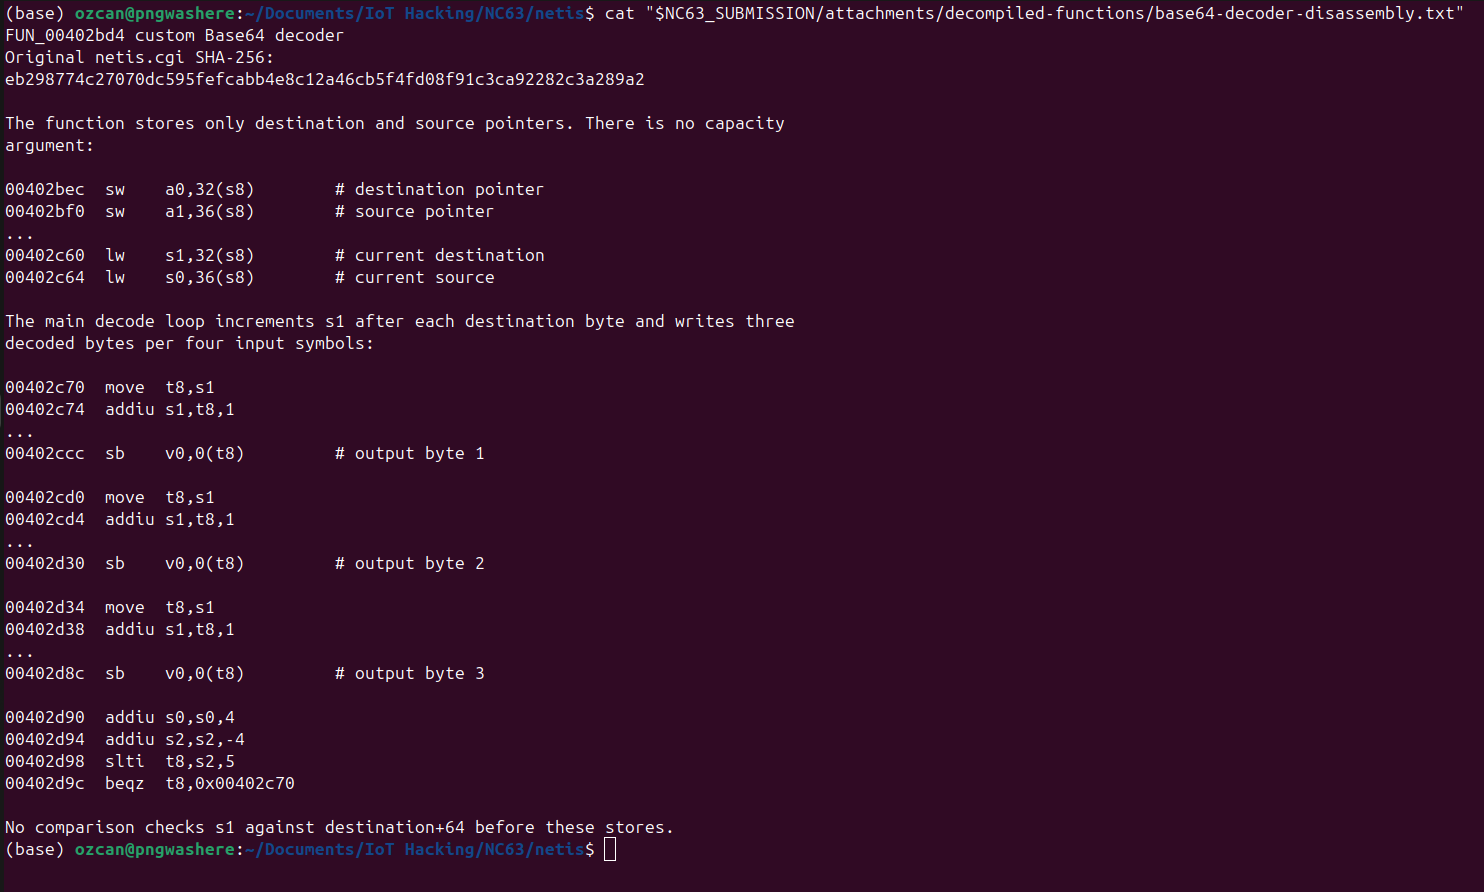 ozcanpng/cve-2026-76070
Original research and PoC for a pre-auth Base64-decoded password stack buffer overflow in Netis NC63 login.cgi
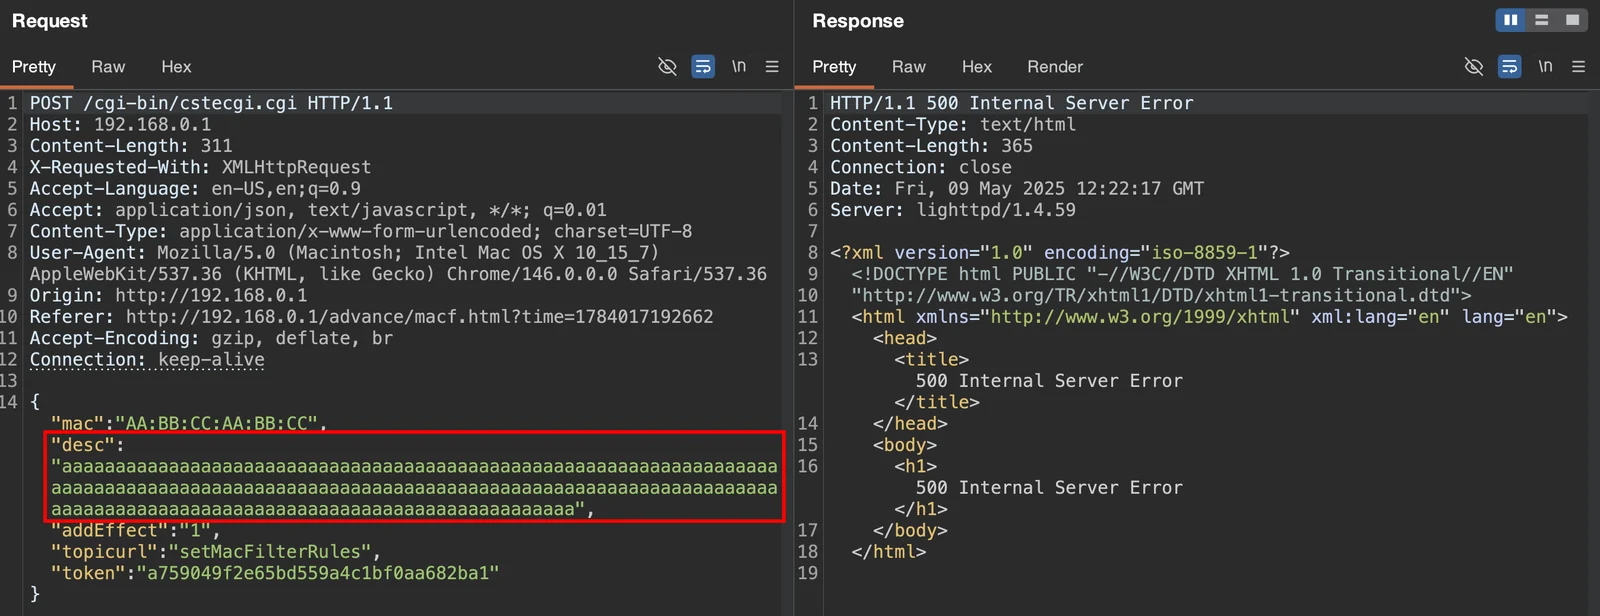 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
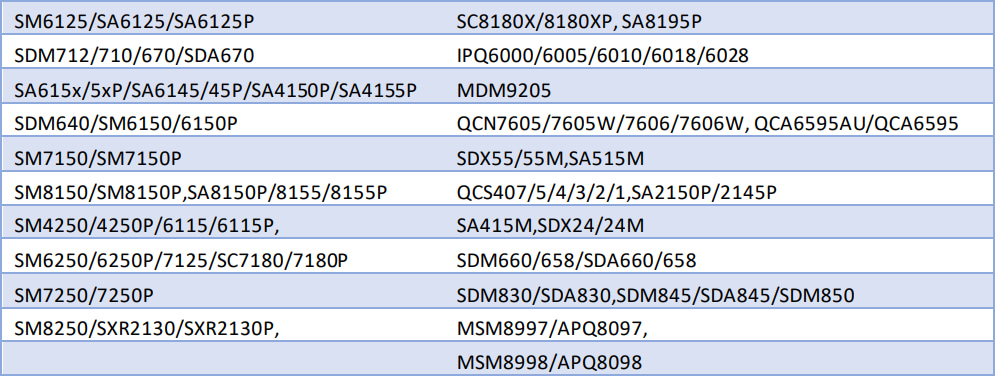 daniel224455/katana
Let's hijack our bootchain - CVE-2021-30327
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…