
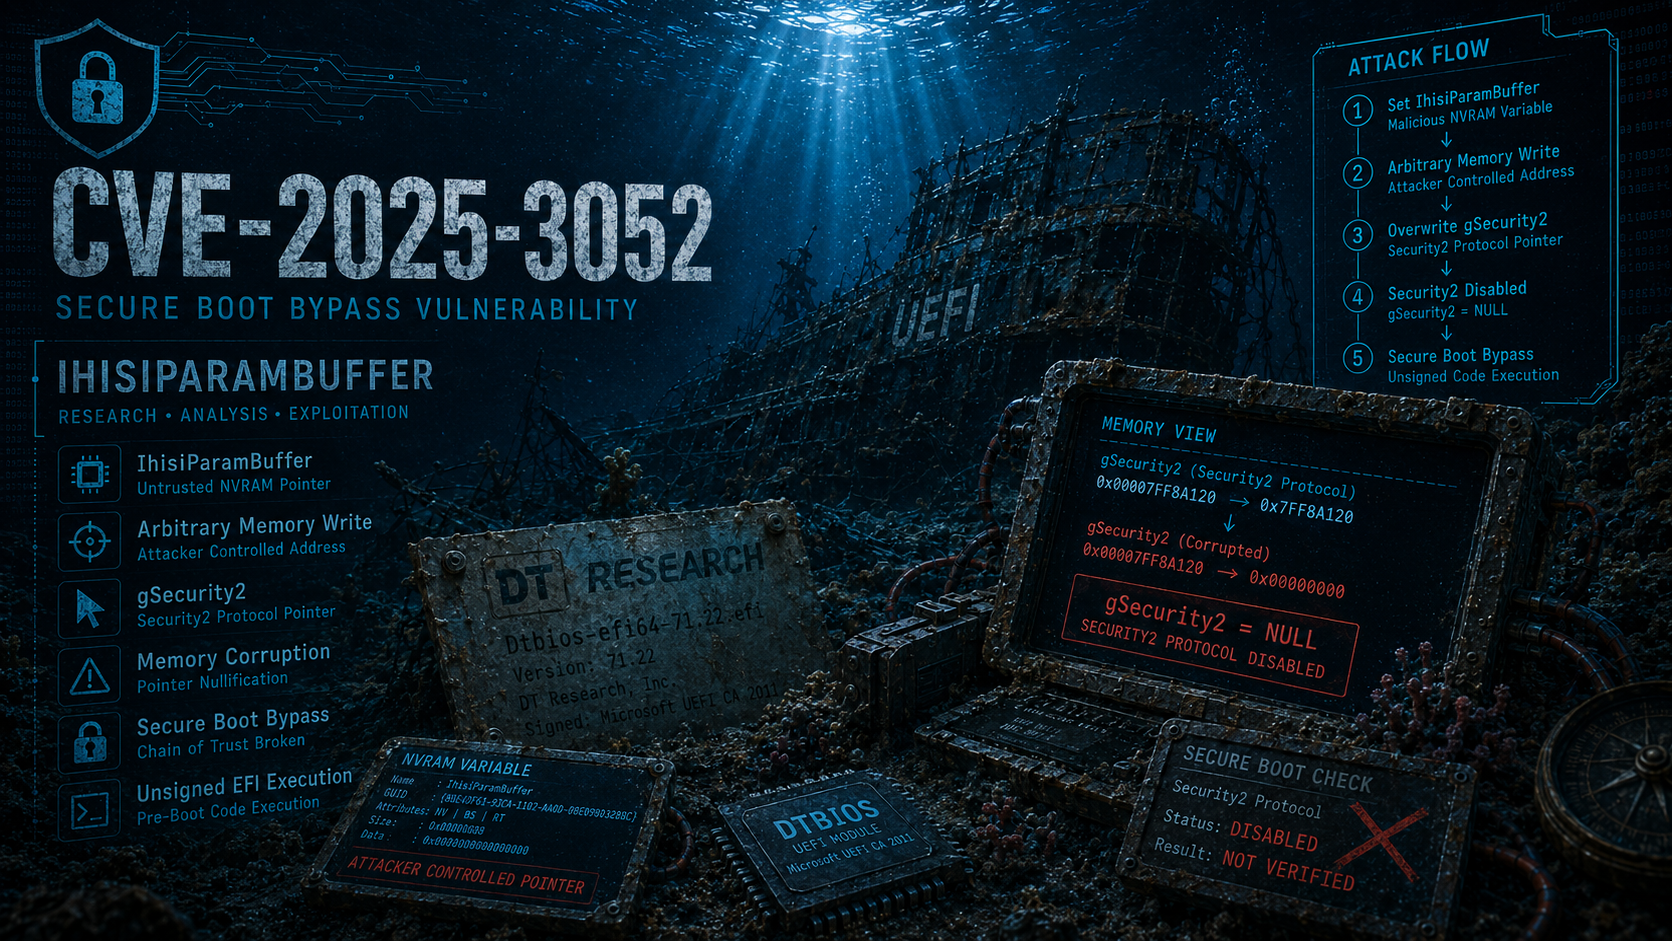
CVE-2025-3052
 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
binary-analysiseducationembedded-systems-security+5
themalwareguardian/cve-2025-3052Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
 fomovet/cve-2025-29384
POC for CVE-2025-29384
 hunt-benito/samsung-exynos-sms-stack-overflow-cve-2025-54328-critical-zero-click-baseband-rce
Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
 analyticeth/chronomaly-webos
CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…
 masjadaan/cve-2025-29338
Technical advisory and proof-of-concept for a stack-based buffer overflow (CWE-121) in the NXP moal.ko Wi-Fi kernel driver, enabling local kernel…
 kaleth4/cve-2025-0690
Technical analysis of CVE-2025-0690: integer overflow in GRUB2's read command leading to heap out-of-bounds write, arbitrary code execution, and…
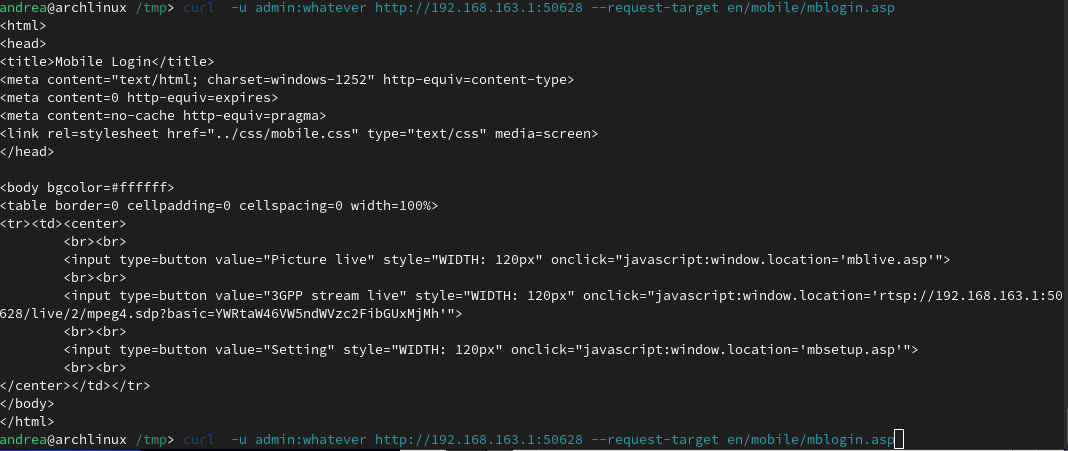 n0n4m3x41/cve-2025-1739
0day PoC for CVE-2025-1739
 5ulfur/cve-2025-57428
CVE-2025-57428
 zhuowei/blueshrimp
Proof-of-concept for CVE-2025-48593
 yohanes/poc-cve-2025-31931
Proof-of-concept exploit for CVE-2025-31931 demonstrating arbitrary shared library loading in Intel ITT API on Android, affecting OpenCV 4.10.
 jdbonfils/poc_cve-2025-48507
Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…
 yashodhanvivek/agatsa-easytouch-plus---cve-2025-56019
This report is for CVE-2025-56019 reserved for Easytouch+product for BLE authentication vulnerability assigned to Discoverer Yashodhan Vivek Mandke.…
 goldenticketlabs/cve-2025-52413
repo for CVE-2025-52413
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300