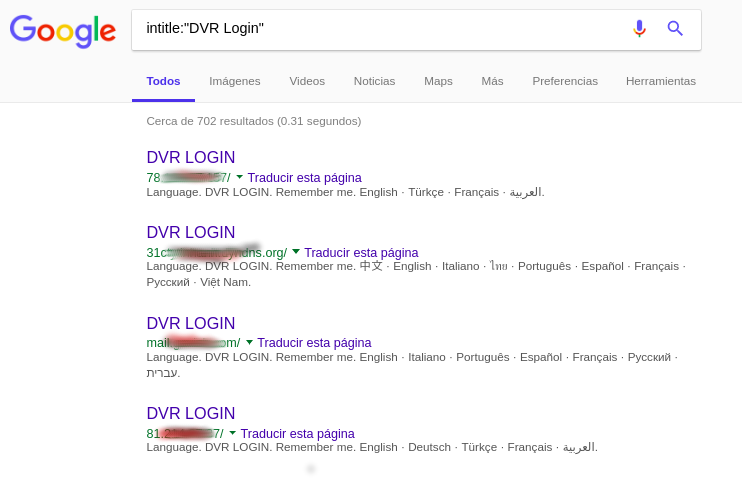
CVE-2018-9995-DVR-Credentials-Extractor

This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.

This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.

Analysis and PoC for CVE-2018-14847, MikroTik RouterOS Winbox information disclosure vulnerability allowing unauthenticated read access to the…

An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

Proof-of-concept exploit targeting ARM TrustZone secure world, demonstrating a vulnerability in OP-TEE OS for educational and research purposes.

TP-Link TL-WR1043ND - Authenticated Remote Code Execution

An implementation of a proof-of-concept for CVE-2018-5767

An implementation of a proof-of-concept for CVE-2018-5767 (https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-5767)

Implementation of CVE-2018-6242 (AKA Fusée Gelée, AKA shofel2)

This Tool Aims to Exploit the CVE-2018-13341

Rust implementation of the Fusée Gelée exploit (CVE-2018-6242) for Tegra processors.

Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices

CERIO RCE CVE-2018-18852, authenticated (vendor defaults) web-based RCE as root user.

Proof-of-concept exploit for CVE-2018-20162: sandbox escape in Digi TransPort LR54 LTE router via SIGINT handling flaw, yielding root shell access.

Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…

Collection of "modchip" designs for launching payloads via the Tegra RCM bug (CVE-2018-6242)

MikroTik RouterOS Denial of Service Vulnerability