
CVE-2026-90847
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
embedded-systems-securityexploitationiot-security+5
shlln/cve-2026-90847Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
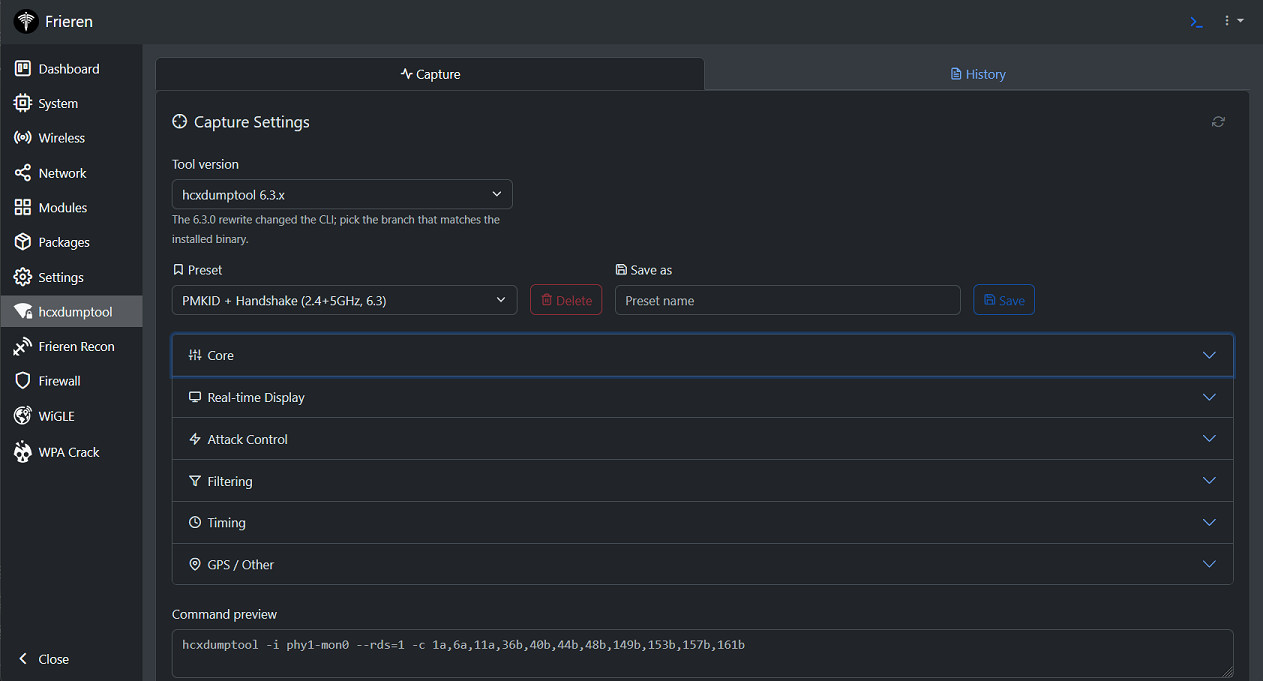 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
 d6fault/cve-2026-95675
Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 hellkkid/cve-2026-56718
AJCloud AJY IPC Firmware Path Traversal via jdbhttpd
 totekuh/cve-2026-75616
Proof-of-concept exploit for authenticated OS command injection in TP-Link Archer C20 v6 web management interface, executing root commands via BPA…
 minanagehsalalma/cve-2026-6837-zyxel-export-cgi-command-injection
Public writeup, PoC, and emulation materials for CVE-2026-6837 affecting Zyxel export-cgi PKCS#12 export handling.
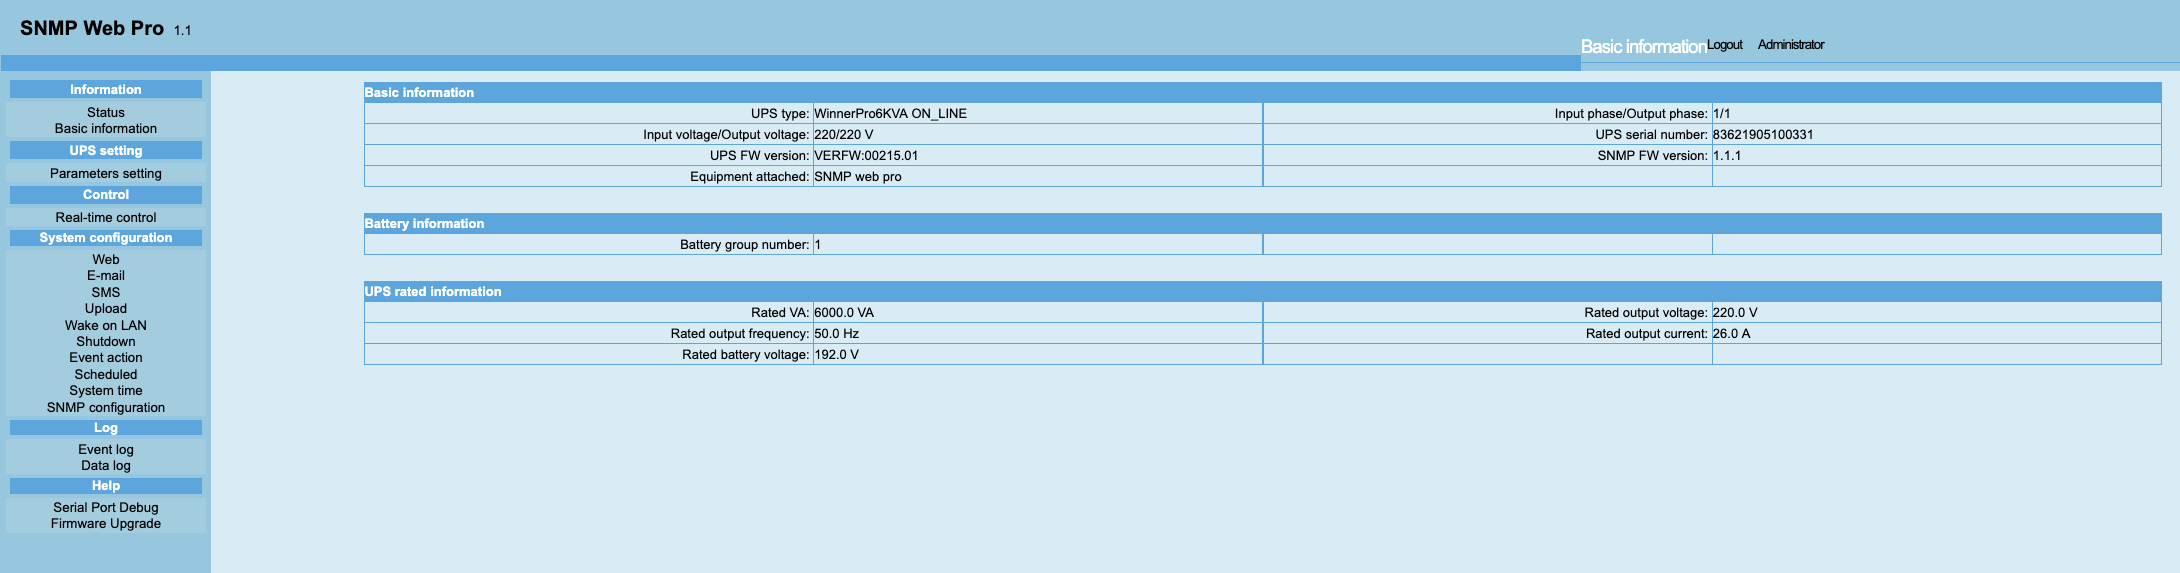 virgula0/cve-2026-44402
Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1
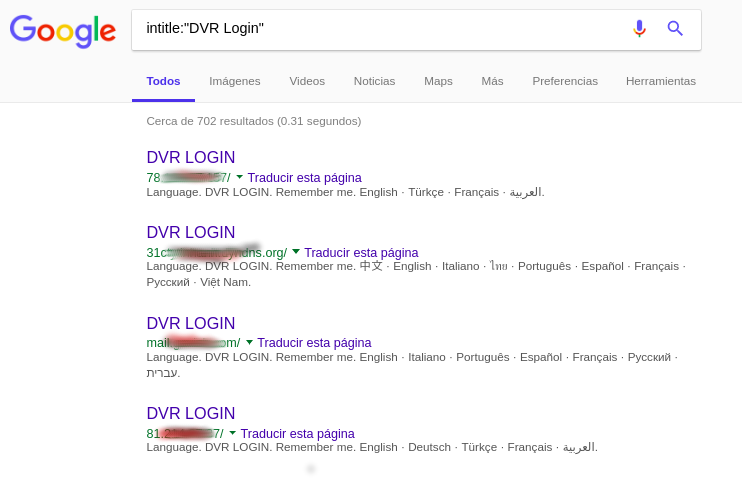 f7p-h4nn1b4l/cve-2018-9995-dvr-credentials-extractor
This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.
 ilizavr/cve-2022-30024
Tplink wr841 v10 rce exploit
 ret2c/cve-2026-8023
PoC for CVE-2026-8023: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')
 fomovet/cve-2025-29384
POC for CVE-2025-29384
 hunt-benito/glinet-beryl-ax-triple-rce-cve-2026-11450-11451-11452-unauthenticated-root-on-travel-router
PoC for three unauthenticated command injection vulnerabilities (CVE-2026-11450/1/2) in GL.iNet Beryl AX travel router firmware <=4.4.5, exploiting…