

byd-dolphin-hacking
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
android-securitybinary-analysisembedded-systems-security+7
wheregoes/byd-dolphin-hackingReverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 turretsec/u3000py
Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 flex36ty/ps5-pihost
PS5 Exploit Web Server on a Raspberry Pi Powered by the PS5's USB Port
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
 ejfkdev/reyee_decrypt
Decrypt Ruijie ReyeeOS firmware (v1/v2) and encrypted config backups; recover plaintext passwords
 nmatt0/moria
IoT firmware identification and extraction
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 khaleedbt/netis-cve-2026-36539
Python script that checks Netis routers for CVE-2026-36539, detecting vulnerable devices on a network.
 dkstar11q/cve-2024-29269
Exploit for CVE-2024-29269 enabling unauthenticated OS command execution on TLR-2005KSH routers, with ZoomEye and Leakix dork queries for target…
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
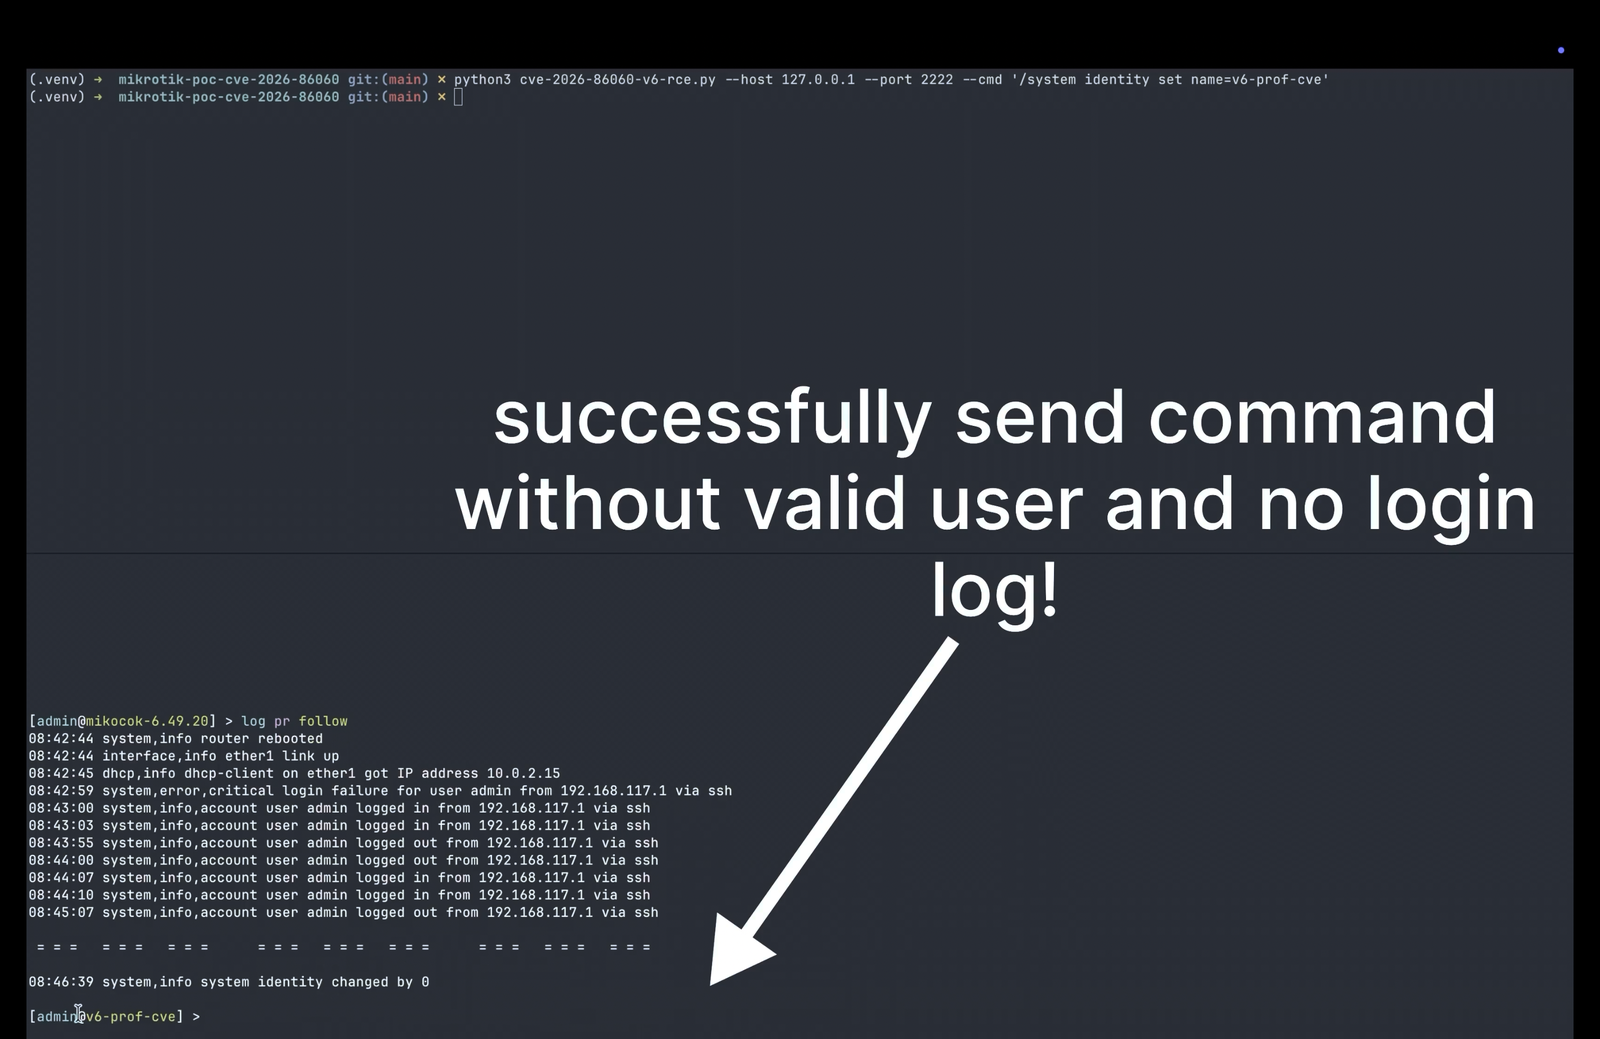 bahirul/cve-2026-86060
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 hellkkid/cve-2026-56718
AJCloud AJY IPC Firmware Path Traversal via jdbhttpd
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
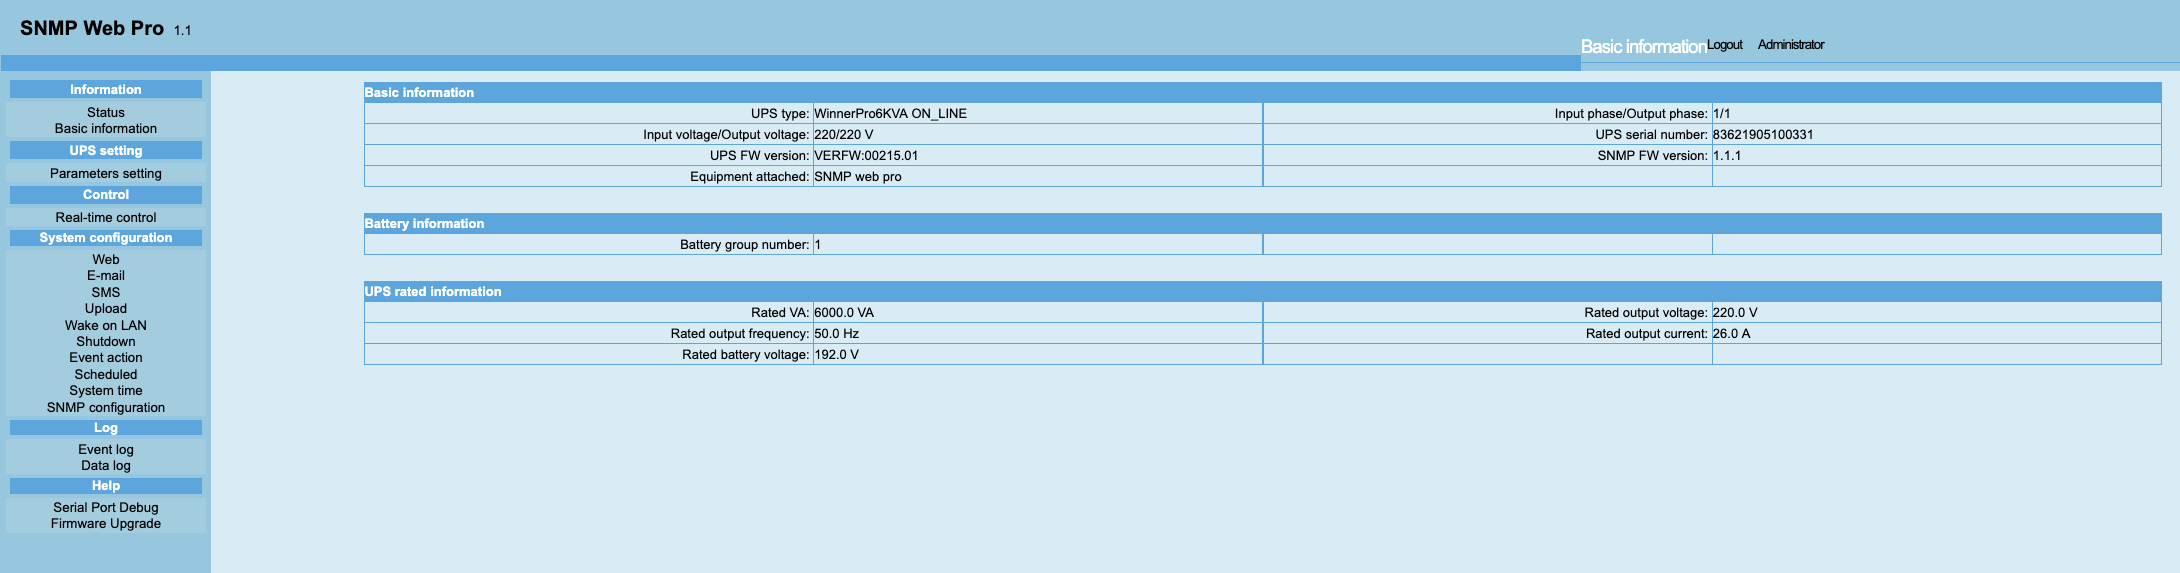 virgula0/cve-2026-44402
Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more