
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
71 results
CVE-2026-95675 preview

CVE-2026-95675

GitHubd6fault/cve-2026-95675

Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
embedded-systems-securityexploitationfirmware-analysis+6
1
4 days ago
CVE-2026-90847 preview

CVE-2026-90847

GitHubshlln/cve-2026-90847

Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
embedded-systems-securityexploitationiot-security+5
5 days ago
CVE-2026-56718 preview

CVE-2026-56718

GitHubhellkkid/cve-2026-56718

AJCloud AJY IPC Firmware Path Traversal via jdbhttpd
embedded-systems-securityexploitationiot-security+3
24 days ago
CVE-2026-32743-PX4-Autopilot-MavlinkLogHandler-Stack-Buffer-Overflow-DoS- preview

CVE-2026-32743-PX4-Autopilot-MavlinkLogHandler-Stack-Buffer-Overflow-DoS-

GitHubmbanyamer/cve-2026-32743-px4-autopilot-mavlinkloghandler-stack-buffer-overflow-dos-

A remote Denial of Service (DoS) exploit for PX4 Autopilot versions ≤1.17.0-rc2 via a stack‑based buffer overflow in the MavlinkLogHandler.
binary-exploitationembedded-systems-securityexploitation+3
4 months ago
CVE-2024-6333 preview

CVE-2024-6333

GitHub0xqrx/cve-2024-6333

Authenticated Remote Code Execution vulnerability in Xerox WorkCentre printers via the Network Troubleshooting Log feature.
embedded-systems-securityexploitationhardware-iot-security+2
7 months ago
CVE-2026-44402 preview

CVE-2026-44402

GitHubvirgula0/cve-2026-44402

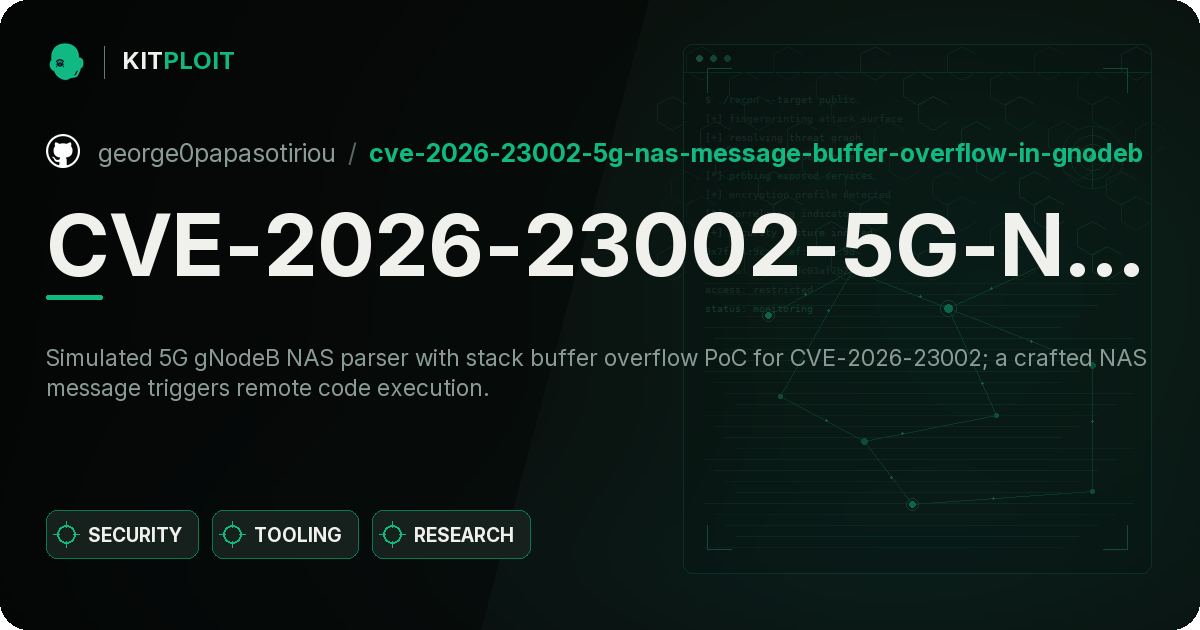
Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1

embedded-systems-securityexploitationiot-security+5
11 month ago
FOISted preview

FOISted

GitHubmarginresearch/foisted

MikroTik remote jailbreak for v6.x.x
binary-exploitationembedded-systems-securityexploitation+6
1593 years ago
CVE-2026-23002-5G-NAS-Message-Buffer-Overflow-in-gNodeB preview

CVE-2026-23002-5G-NAS-Message-Buffer-Overflow-in-gNodeB

GitHubgeorge0papasotiriou/cve-2026-23002-5g-nas-message-buffer-overflow-in-gnodeb

Simulated 5G gNodeB NAS parser with stack buffer overflow PoC for CVE-2026-23002; a crafted NAS message triggers remote code execution.
binary-exploitationembedded-systems-securityexploitation+2
1 month ago
CVE-2026-6789-Stack-Buffer-Overflow-in-Embedded-TLS-Certificate-Parser preview

CVE-2026-6789-Stack-Buffer-Overflow-in-Embedded-TLS-Certificate-Parser

GitHubgeorge0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser

Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…

binary-exploitationeducationembedded-systems-security+3
1 month ago
sagemcom-fast-3890-exploit preview

sagemcom-fast-3890-exploit

GitHublyrebirds/sagemcom-fast-3890-exploit

Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
binary-exploitationembedded-systems-securityexploitation+4
2246 years ago
watchTowr-vs-SonicWall-PreAuth-RCE-Chain preview

watchTowr-vs-SonicWall-PreAuth-RCE-Chain

GitHubwatchtowrlabs/watchtowr-vs-sonicwall-preauth-rce-chain

PoC exploit chain for pre-authentication remote code execution on SonicWall SMA 100 appliances exploiting CVE-2023-44221 and CVE-2024-38475.
embedded-systems-securityexploitationpenetration-testing+3
191 year ago
system_bt_AOSP10_r33_CVE-2021-0435 preview

system_bt_AOSP10_r33_CVE-2021-0435

GitHubnanopathi/system_bt_aosp10_r33_cve-2021-0435

Android Bluetooth stack (AOSP 10 r33) with fix for CVE-2021-0435, addressing remote code execution in Bluetooth pairing.

bluetooth-securityembedded-systems-securitymobile-security+2
4 years ago
gxv3175-remote-code-exec preview

gxv3175-remote-code-exec

GitHubdirtyfilthy/gxv3175-remote-code-exec

Remote code execution for Grandstream GXV3175 VOIP phone.
embedded-systems-securityexploit-frameworkspayload-development+2
210 years ago
Netgear_Pwn2Own2021 preview

Netgear_Pwn2Own2021

GitHubsynacktiv/netgear_pwn2own2021

Exploit used against the Netgear R6700v3 during Pwn2Own Austin 2021
binary-exploitationembedded-systems-securityexploitation+3
64 years ago
CVE-2024-35106-POC preview

CVE-2024-35106-POC

GitHublaskdjlaskdj12/cve-2024-35106-poc

Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…

binary-exploitationembedded-systems-securityexploitation+5
1 year ago
CVE-2021-41730 preview

CVE-2021-41730

GitHubyezeting/cve-2021-41730

Proof-of-concept exploit for CVE-2021-41730, demonstrating remote command execution in TENDA AC15/AC6 routers via unvalidated formSetIptv()…

command-and-controlembedded-systems-securityexploitation+5
4 years ago
CVE-2024-22853 preview

CVE-2024-22853

GitHubfallenskill1/cve-2024-22853

D-LINK Go-RT-AC750 GORTAC750_A1_FW_v101b03 has a hardcoded password for the Alphanetworks account, which allows remote attackers to obtain root…

embedded-systems-securityexploitationfirmware-analysis+5
2 years ago
TP-Link-ArcherC5-RCE preview

TP-Link-ArcherC5-RCE

GitHubjackdoan/tp-link-archerc5-rce

CVE-2018-19537

command-and-controlembedded-systems-securityexploitation+8
207 years ago
Previous1234Next