

CVE-2015-0235-workaround
 makelinux/cve-2015-0235-workaround
A shared library wrapper with additional checks for vulnerable functions gethostbyname2_r gethostbyname_r (GHOST vulnerability)
binary-analysisembedded-systems-securityexploitation+2
makelinux/cve-2015-0235-workaroundA shared library wrapper with additional checks for vulnerable functions gethostbyname2_r gethostbyname_r (GHOST vulnerability)
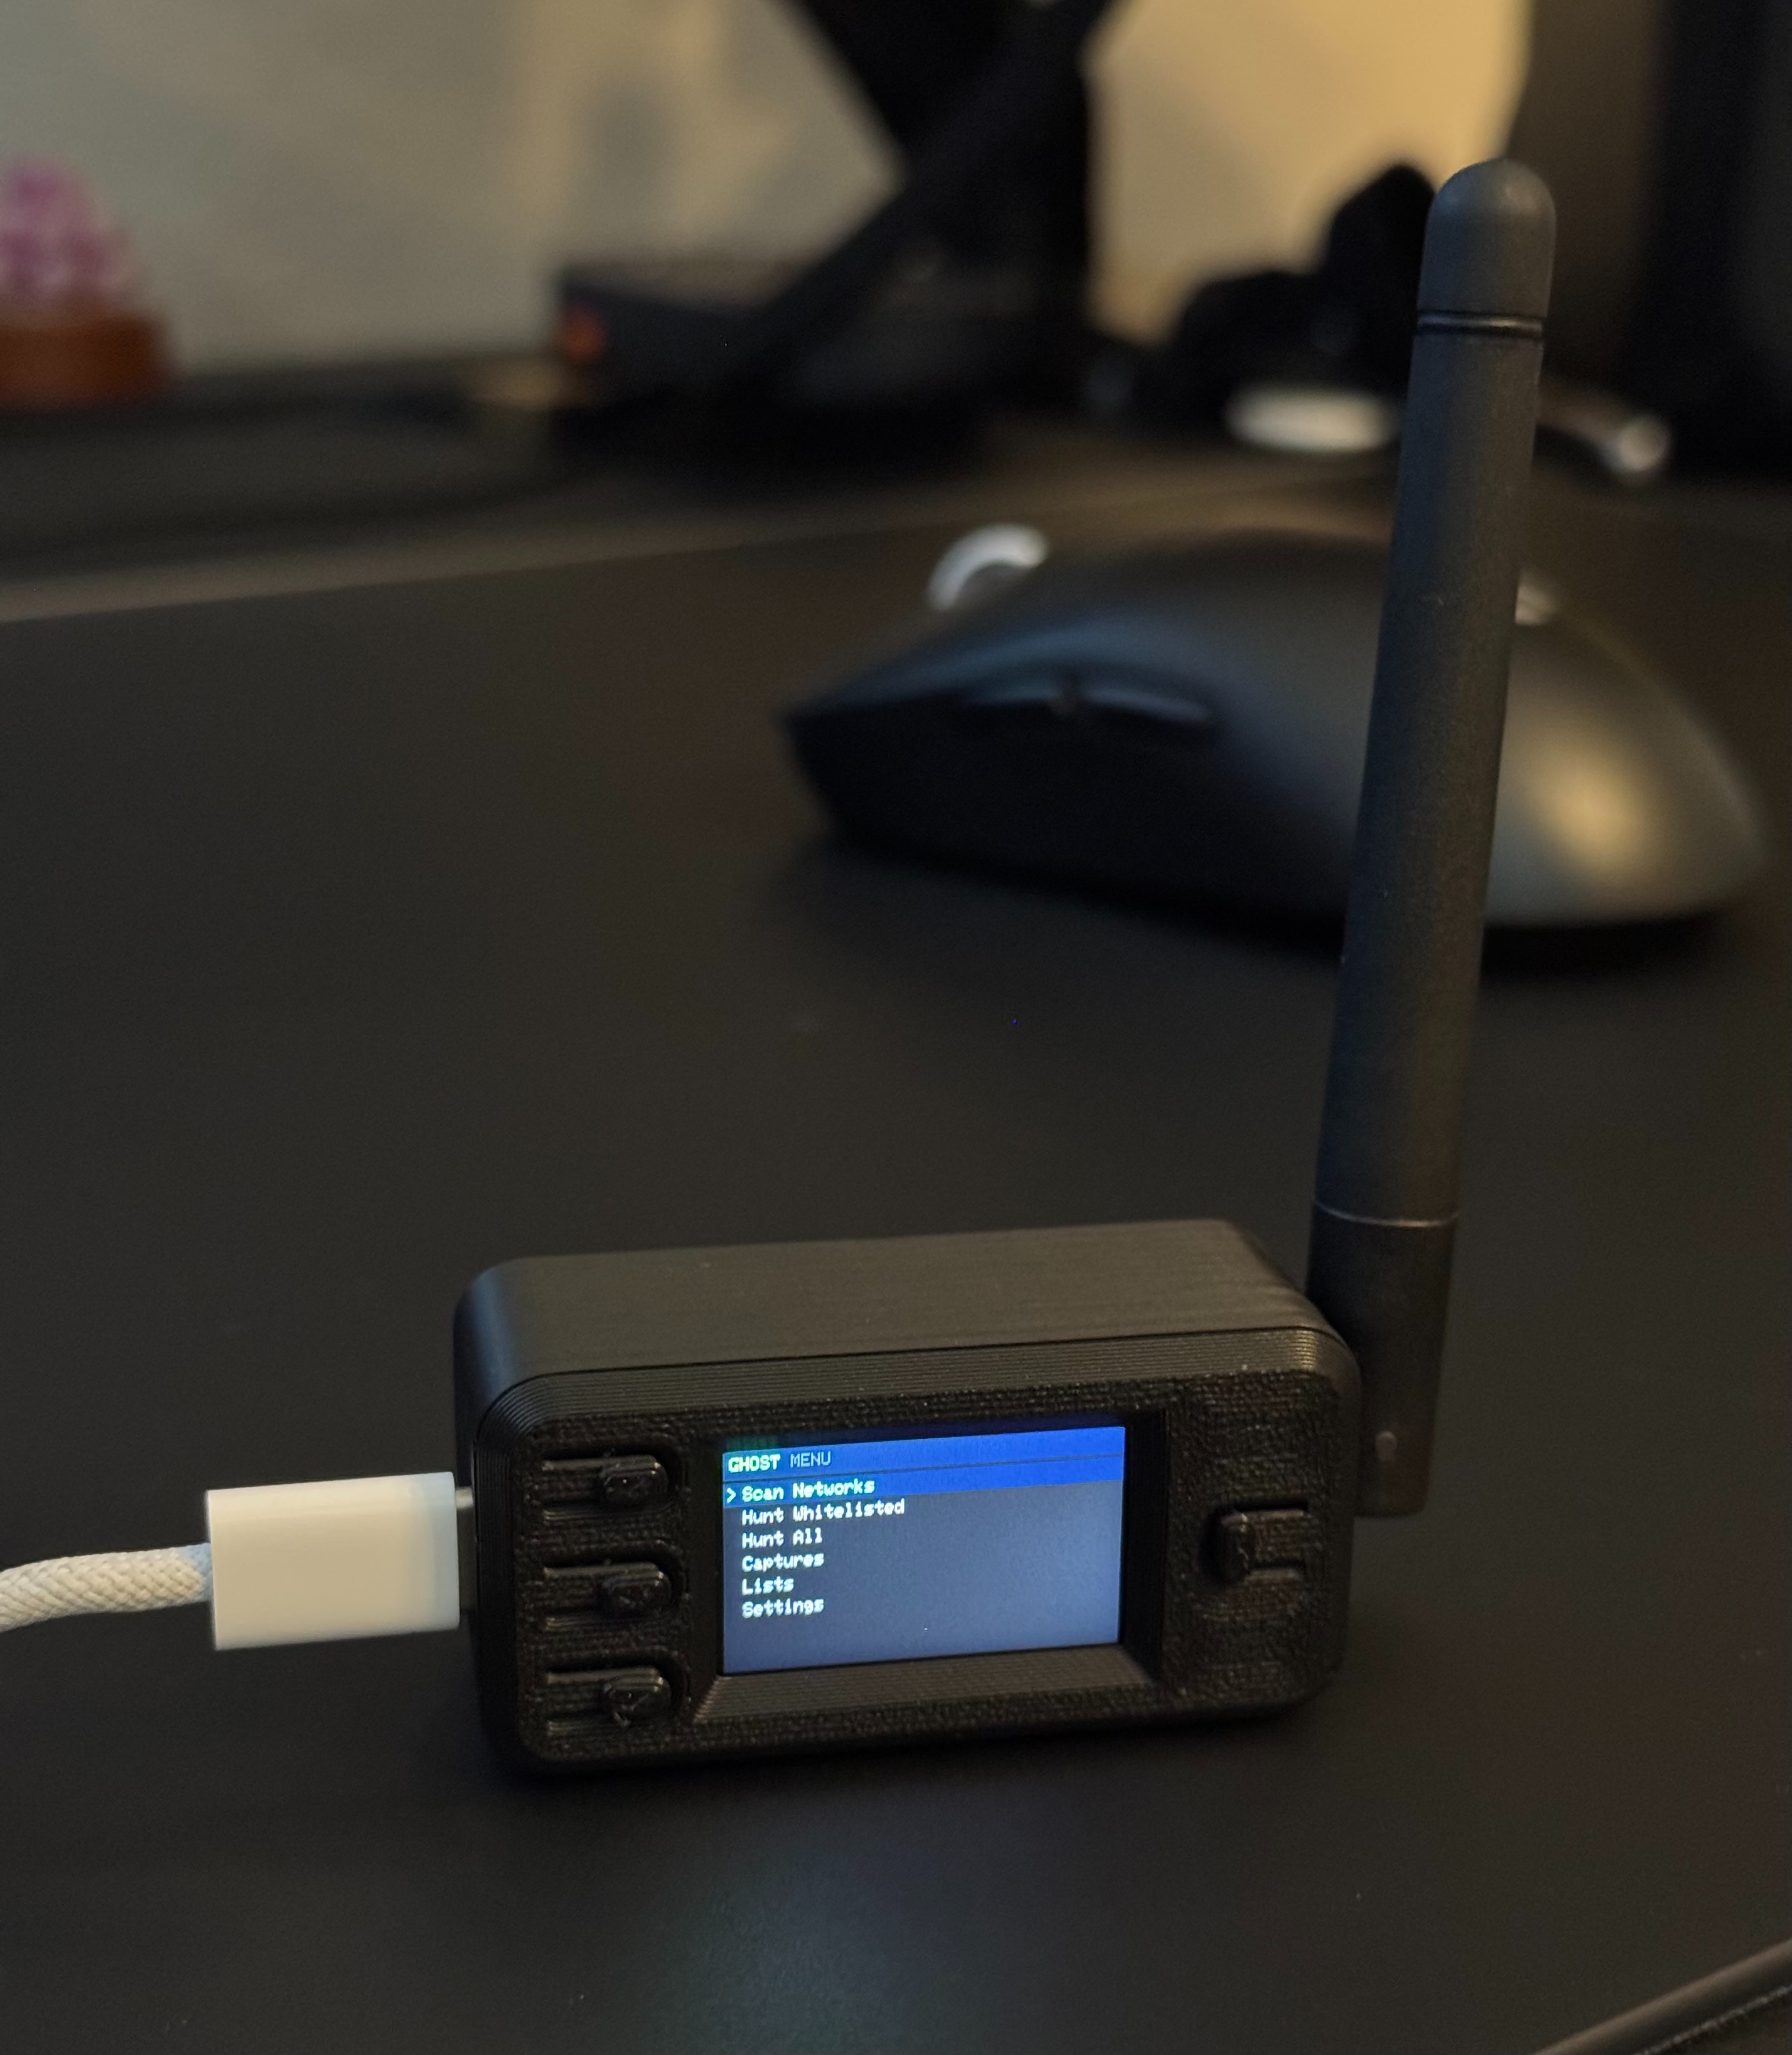 razkom/ghost
ESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.